Proof Tree for weak-lemma_3-15 (View conclusion)
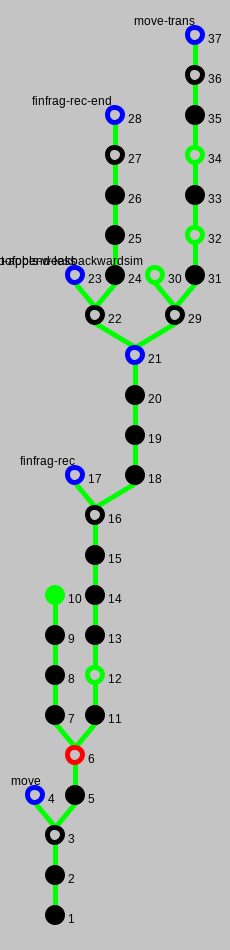
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), exec*(IOAut(cstart, cstep, cext))(csl0, cal0), csl0.last = cs, move(IOAut(cstart, cstep, cext))(cs, el, cs0), t(cs0, as0), aINV(as0) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, el, as0) ∧ t(cs, as) ∧ aINV(as) |
csl0.last = cs, aINV(as0), exec*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(cstart, cstep, cext))(cs, el, cs0), t(cs0, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, el, as0) ∧ t(cs, as) ∧ aINV(as)
| csl0.last = cs, aINV(as0), exec*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(cstart, cstep, cext))(cs, el, cs0), t(cs0, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, el, as0) ∧ t(cs, as) ∧ aINV(as) |
aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(cstart, cstep, cext))(csl0.last, el, cs0), t(cs0, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, el, as0) ∧ t(csl0.last, as) ∧ aINV(as)
Used simplifier rules: ⊦ IOAut(start, step, ext).start = start; (s) ⊦ exec*(ioa)(sl, al) ↔ frag*(ioa)(sl, al) ∧ ioa.start(sl[0]); (s)
| aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(cstart, cstep, cext))(csl0.last, el, cs0), t(cs0, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, el, as0) ∧ t(csl0.last, as) ∧ aINV(as) |
⊦ move(ioa)(s1, el, s2) ↔ (∃ al, sl. frag*(ioa)(sl, al) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ ioa.ext !(al) = el)
aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(cs0, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ∃ al, sl. frag*(IOAut(cstart, cstep, cext))(sl, al) ∧ csl0.last = sl[0] ∧ cs0 = sl.last ∧ IOAut(cstart, cstep, cext).ext !(al) = el ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, el, as0) ∧ t(csl0.last, as) ∧ aINV(as)
Used terms: IOAut(cstart, cstep, cext), csl0.last, el, cs0
| ⊦ move(ioa)(s1, el, s2) ↔ (∃ al, sl. frag*(ioa)(sl, al) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ ioa.ext !(al) = el) |
| aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(cs0, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ∃ al, sl. frag*(IOAut(cstart, cstep, cext))(sl, al) ∧ csl0.last = sl[0] ∧ cs0 = sl.last ∧ IOAut(cstart, cstep, cext).ext !(al) = el ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, el, as0) ∧ t(csl0.last, as) ∧ aINV(as) |
csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl, cal), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal), as0) ∧ t(csl[0], as) ∧ aINV(as)
Used simplifier rules: ⊦ IOAut(start, step, ext).ext = ext; (s)
| csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl, cal), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal), as0) ∧ t(csl[0], as) ∧ aINV(as) |
csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, []), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, cext !([]), as0) ∧ t(csl[0], as) ∧ aINV(as)
csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, ca + cal1), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ∀ csl0, csl, aINV, as0, cstart, cstep, cext, cal0, t, astart, astep, aext. csl0.last = csl[0] ∧ aINV(as0) ∧ cstart(csl0[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0, cal0) ∧ t(csl.last, as0) ∧ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) → (∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, cext !(ca + cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)
Used simplifier rules: List('a) freely generated by [], +;;
| csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, []), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, cext !([]), as0) ∧ t(csl[0], as) ∧ aINV(as) |
csl0.last = csl[0], csl = csl.head ', aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.head, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, [], as0) ∧ t(csl[0], as) ∧ aINV(as)
Used simplifier rules: ⊦ ext !([]) = []; (s) ⊦ x = x.head ' → x.last = x.head; (s) ⊦ frag*(IOAut(start, step, ext))(sl, []) ↔ sl = sl.head '; (s)
| csl0.last = csl[0], csl = csl.head ', aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.head, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, [], as0) ∧ t(csl[0], as) ∧ aINV(as) |
csl0.last = csl[0], csl = cs ', csl = cs + csl1, csl ≠ [], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(cs, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, [], as0) ∧ t(csl[0], as) ∧ aINV(as)
Used simplifier rules: ⊦ a ' ≠ []; (s) x ≠ [] ⊦ a = x.head ∧ y = x.tail ↔ x = a + y; (elim) Used terms: csl, cs, csl1
| csl0.last = csl[0], csl = cs ', csl = cs + csl1, csl ≠ [], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(cs, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, [], as0) ∧ t(csl[0], as) ∧ aINV(as) |
aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl0.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, [], as0) ∧ t(csl0.last, as) ∧ aINV(as)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ (a ' + x)[0] = a; (s) ⊦ a + x = a ' + x; (s) ⊦ a ' ≠ []; (s) ⊦ x + y = [] ↔ x = [] ∧ y = []; (s) ⊦ a ' = a0 ' + x ↔ a = a0 ∧ x = []; (ws)
| aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl0.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, [], as0) ∧ t(csl0.last, as) ∧ aINV(as) |
Used simplifier rules: ⊦ move(IOAut(start, step, ext))(s, [], s); (s) Used terms: as0
| csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, ca + cal1), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ∀ csl0, csl, aINV, as0, cstart, cstep, cext, cal0, t, astart, astep, aext. csl0.last = csl[0] ∧ aINV(as0) ∧ cstart(csl0[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0, cal0) ∧ t(csl.last, as0) ∧ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) → (∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, cext !(ca + cal1), as0) ∧ t(csl[0], as) ∧ aINV(as) |
csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ∀ csl0, csl, aINV, as0, cstart, cstep, cext, cal0, t, astart, astep, aext. csl0.last = csl[0] ∧ aINV(as0) ∧ cstart(csl0[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0, cal0) ∧ t(csl.last, as0) ∧ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) → (∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ ext !(a ') = (ext(a) = None ⊃ [];ext(a).get '); (s) ⊦ ext !(al + al0) = ext !(al) + ext !(al0); (s) ⊦ a + x = a ' + x; (s)
| csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ∀ csl0, csl, aINV, as0, cstart, cstep, cext, cal0, t, astart, astep, aext. csl0.last = csl[0] ∧ aINV(as0) ∧ cstart(csl0[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0, cal0) ∧ t(csl.last, as0) ∧ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) → (∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as) |
csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), (csl0 + csl.tail.head).last = csl.tail[0] ∧ aINV(as0) ∧ cstart((csl0 + csl.tail.head)[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl.tail, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl.tail.head, cal0 + ca ') ∧ t(csl.tail.last, as0) ∧ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) → (∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl.tail[0], as) ∧ aINV(as)) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)
Used terms: csl0 + csl.tail.head, csl.tail, aINV, as0, cstart, cstep, cext, cal0 + ca ', t, astart, astep, aext
| csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), (csl0 + csl.tail.head).last = csl.tail[0] ∧ aINV(as0) ∧ cstart((csl0 + csl.tail.head)[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl.tail, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl.tail.head, cal0 + ca ') ∧ t(csl.tail.last, as0) ∧ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) → (∃ as. move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl.tail[0], as) ∧ aINV(as)) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as) |
csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl.tail.head = csl.tail[0] ∧ cstart((csl0 + csl.tail.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl.tail, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl.tail.head ', cal0 + ca ') ∧ t(csl.tail.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl.tail[0], as) ∧ aINV(as) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)
Used simplifier rules: ⊦ x + a = x + a '; (s) a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ (x + a ').last = a; (s)
| csl0.last = csl[0], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl.tail.head = csl.tail[0] ∧ cstart((csl0 + csl.tail.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl.tail, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl.tail.head ', cal0 + ca ') ∧ t(csl.tail.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl.tail[0], as) ∧ aINV(as) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as) |
csl0.last = csl[0], csl = cs + csl1, csl ≠ [], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl1, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as)
Used simplifier rules: ⊦ ¬ frag*(IOAut(start, step, ext))([], al); (s) x ≠ [] ⊦ a = x.head ∧ y = x.tail ↔ x = a + y; (elim) Used terms: csl, cs, csl1
| csl0.last = csl[0], csl = cs + csl1, csl ≠ [], aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl, ca ' + cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t(csl.last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl1, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as. move(IOAut(astart, astep, aext))(as, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl[0], as) ∧ aINV(as) |
aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0.last ' + csl1, ca ' + cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl1, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ (a ' + x)[0] = a; (s) ⊦ a + x = a ' + x; (s) ⊦ a ' ≠ []; (s) ⊦ x + y = [] ↔ x = [] ∧ y = []; (s)
| aINV(as0), cstart(csl0[0]), frag*(IOAut(cstart, cstep, cext))(csl0.last ' + csl1, ca ' + cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl1, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
⊦ frag*(IOAut(start, step, ext))(s ' + sl, a ' + al) ↔ step(s, a, sl.head) ∧ frag*(IOAut(start, step, ext))(sl, al)
aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, csl1.head), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl1, cal1), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl1, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used terms: cal1, csl0.last, cext, csl1, ca, cstart, cstep
| ⊦ frag*(IOAut(start, step, ext))(s ' + sl, a ' + al) ↔ step(s, a, sl.head) ∧ frag*(IOAut(start, step, ext))(sl, al) |
| aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, csl1.head), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl1, cal1), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl1, cal1) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, csl1.head), frag*(IOAut(cstart, cstep, cext))(csl1, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
| aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, csl1.head), frag*(IOAut(cstart, cstep, cext))(csl1, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), csl1.head = csl1[0] ∧ cstart((csl0 + csl1.head ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + csl1.head ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
csl1 = cs + csl, csl1 ≠ [], aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl1, cal1), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), cs = csl1[0] ∧ cstart((csl0 + cs ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used simplifier rules: ⊦ x + [] = x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ a '.last = a; (s) ⊦ ¬ frag*(IOAut(start, step, ext))([], al); (s) x ≠ [] ⊦ a = x.head ∧ y = x.tail ↔ x = a + y; (elim) Used terms: csl1, cs, csl
| csl1 = cs + csl, csl1 ≠ [], aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(csl1, cal1), t((csl0.last ' + csl1).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), cs = csl1[0] ∧ cstart((csl0 + cs ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') ∧ t(csl1.last, as0) → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(csl1[0], as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), cstart((csl0 + cs ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(cs, as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ (a ' + x)[0] = a; (s) ⊦ a + x = a ' + x; (s) ⊦ (b ' + a ' + x).last = (a ' + x).last; (s) ⊦ a ' ≠ []; (s) ⊦ x + y = [] ↔ x = [] ∧ y = []; (s)
| aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), cstart((csl0 + cs ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') → move(IOAut(astart, astep, aext))(as, cext !(cal1), as0) ∧ t(cs, as) ∧ aINV(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1), cstart((csl0 + cs ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ')
aINV(as0), aINV(as), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t((cs ' + csl).last, as0), t(cs, as), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
| aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1), cstart((csl0 + cs ')[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') |
⊦ n < # x → (x + y)[n] = x[n]
0 < # csl0, aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1), cstart(csl0[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ')
Used simplifier rules: ⊦ 0 < m ↔ m ≠ 0; (s) ⊦ # x = 0 ↔ x = []; (s) ⊦ ¬ frag*(IOAut(start, step, ext))([], al); (s) Used terms: 0, csl0, cs '
| ⊦ n < # x → (x + y)[n] = x[n] |
| 0 < # csl0, aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1), cstart(csl0[0]) ∧ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') |
csl0 ≠ [], aINV(as0), cstart(csl0.head), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ¬ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used simplifier rules: ⊦ x ≠ [] → x[0] = x.head; (s) ⊦ # x = 0 ↔ x = []; (s) ⊦ 0 < m ↔ m ≠ 0; (s)
| csl0 ≠ [], aINV(as0), cstart(csl0.head), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ¬ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
csl0 = cs0 + csl1, csl0 ≠ [], aINV(as0), cstart(cs0), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ¬ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used simplifier rules: ⊦ x ≠ [] → (head = x.head ∧ tail = x.tail ↔ x = head + tail); (elim) Used terms: csl0, cs0, csl1
| csl0 = cs0 + csl1, csl0 ≠ [], aINV(as0), cstart(cs0), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ¬ frag*(IOAut(cstart, cstep, cext))(csl0 + cs ', cal0 + ca ') ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as0), cstart(cs0), cstep((cs0 ' + csl1).last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(cs0 ' + csl1, cal0), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ¬ frag*(IOAut(cstart, cstep, cext))((cs0 ' + csl1) + cs ', cal0 + ca ') ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t((cs0 ' + csl1).last, as1) ∧ aINV(as1)
Used simplifier rules: ⊦ a + x = a ' + x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ a ' ≠ []; (s) ⊦ x + y = [] ↔ x = [] ∧ y = []; (s)
| aINV(as0), cstart(cs0), cstep((cs0 ' + csl1).last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(cs0 ' + csl1, cal0), t((cs ' + csl).last, as0), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV), ¬ frag*(IOAut(cstart, cstep, cext))((cs0 ' + csl1) + cs ', cal0 + ca ') ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t((cs0 ' + csl1).last, as1) ∧ aINV(as1) |
⊦ frag*(IOAut(start, step, ext))(sl + s ', al + a ') ↔ step(sl.last, a, s) ∧ frag*(IOAut(start, step, ext))(sl, al)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: cal0, cs, cext, cs0 ' + csl1, ca, cstart, cstep
| ⊦ frag*(IOAut(start, step, ext))(sl + s ', al + a ') ↔ step(sl.last, a, s) ∧ frag*(IOAut(start, step, ext))(sl, al) |
| aINV(as0), aINV(as), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t((cs ' + csl).last, as0), t(cs, as), weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
⊦ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ↔ (∀ csl, cal. exec*(IOAut(cstart, cstep, cext))(csl, cal) → (∃ as. t(csl.last, as) ∧ aINV(as))) ∧ (∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as)) ∧ (∀ asl, aal. exec*(IOAut(astart, astep, aext))(asl, aal) → aINV(asl.last)) ∧ (∀ csl, cal, ca, cs0, as0. exec*(IOAut(cstart, cstep, cext))(csl, cal) ∧ cstep(csl.last, ca, cs0) ∧ t(cs0, as0) ∧ aINV(as0) → (∃ as. aINV(as) ∧ move(IOAut(astart, astep, aext))(as, cext !(ca '), as0) ∧ t(csl.last, as)))
aINV(as), aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t(cs, as), t((cs ' + csl).last, as0), ∀ csl, cal. exec*(IOAut(cstart, cstep, cext))(csl, cal) → (∃ as. t(csl.last, as) ∧ aINV(as)), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ asl, aal. exec*(IOAut(astart, astep, aext))(asl, aal) → aINV(asl.last), ∀ csl, cal, ca, cs0, as0. exec*(IOAut(cstart, cstep, cext))(csl, cal) ∧ cstep(csl.last, ca, cs0) ∧ t(cs0, as0) ∧ aINV(as0) → (∃ as. aINV(as) ∧ move(IOAut(astart, astep, aext))(as, cext !(ca '), as0) ∧ t(csl.last, as)) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used terms: cstep, cext, aext, t, astart, cstart, astep, aINV
| ⊦ weakbwsim(IOAut(cstart, cstep, cext), IOAut(astart, astep, aext), t, aINV) ↔ (∀ csl, cal. exec*(IOAut(cstart, cstep, cext))(csl, cal) → (∃ as. t(csl.last, as) ∧ aINV(as))) ∧ (∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as)) ∧ (∀ asl, aal. exec*(IOAut(astart, astep, aext))(asl, aal) → aINV(asl.last)) ∧ (∀ csl, cal, ca, cs0, as0. exec*(IOAut(cstart, cstep, cext))(csl, cal) ∧ cstep(csl.last, ca, cs0) ∧ t(cs0, as0) ∧ aINV(as0) → (∃ as. aINV(as) ∧ move(IOAut(astart, astep, aext))(as, cext !(ca '), as0) ∧ t(csl.last, as))) |
| aINV(as), aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t(cs, as), t((cs ' + csl).last, as0), ∀ csl, cal. exec*(IOAut(cstart, cstep, cext))(csl, cal) → (∃ as. t(csl.last, as) ∧ aINV(as)), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ asl, aal. exec*(IOAut(astart, astep, aext))(asl, aal) → aINV(asl.last), ∀ csl, cal, ca, cs0, as0. exec*(IOAut(cstart, cstep, cext))(csl, cal) ∧ cstep(csl.last, ca, cs0) ∧ t(cs0, as0) ∧ aINV(as0) → (∃ as. aINV(as) ∧ move(IOAut(astart, astep, aext))(as, cext !(ca '), as0) ∧ t(csl.last, as)) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as0), aINV(as), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t((cs ' + csl).last, as0), t(cs, as), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ csl1, cal, ca0, cs0, as1. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) ∧ cstep(csl1.last, ca0, cs0) ∧ t(cs0, as1) ∧ aINV(as1) → (∃ as2. aINV(as2) ∧ move(IOAut(astart, astep, aext))(as2, (cext(ca0) = None ⊃ [];cext(ca0).get '), as1) ∧ t(csl1.last, as2)), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used simplifier rules: ⊦ IOAut(start, step, ext).start = start; (s) ⊦ exec*(ioa)(sl, al) ↔ frag*(ioa)(sl, al) ∧ ioa.start(sl[0]); (s) ⊦ ext !(a ') = (ext(a) = None ⊃ [];ext(a).get '); (s)
| aINV(as0), aINV(as), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t((cs ' + csl).last, as0), t(cs, as), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ csl1, cal, ca0, cs0, as1. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) ∧ cstep(csl1.last, ca0, cs0) ∧ t(cs0, as1) ∧ aINV(as1) → (∃ as2. aINV(as2) ∧ move(IOAut(astart, astep, aext))(as2, (cext(ca0) = None ⊃ [];cext(ca0).get '), as1) ∧ t(csl1.last, as2)), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as), aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t(cs, as), t((cs ' + csl).last, as0), frag*(IOAut(cstart, cstep, cext))(csl0, cal0) ∧ cstart(csl0[0]) ∧ cstep(csl0.last, ca, cs) ∧ t(cs, as) ∧ aINV(as) → (∃ as2. aINV(as2) ∧ move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as) ∧ t(csl0.last, as2)), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
Used terms: csl0, cal0, ca, cs, as
| aINV(as), aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t(cs, as), t((cs ' + csl).last, as0), frag*(IOAut(cstart, cstep, cext))(csl0, cal0) ∧ cstart(csl0[0]) ∧ cstep(csl0.last, ca, cs) ∧ t(cs, as) ∧ aINV(as) → (∃ as2. aINV(as2) ∧ move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as) ∧ t(csl0.last, as2)), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as0), aINV(as), aINV(as2), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as), t((cs ' + csl).last, as0), t(cs, as), t(csl0.last, as2), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1)
| aINV(as0), aINV(as), aINV(as2), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as), t((cs ' + csl).last, as0), t(cs, as), t(csl0.last, as2), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)) ⊦ ∃ as1. move(IOAut(astart, astep, aext))(as1, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as1) ∧ aINV(as1) |
aINV(as2), aINV(as), aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t(csl0.last, as2), t(cs, as), t((cs ' + csl).last, as0), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as) ⊦ move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as2) ∧ aINV(as2)
Used terms: as2
| aINV(as2), aINV(as), aINV(as0), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), t(csl0.last, as2), t(cs, as), t((cs ' + csl).last, as0), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as) ⊦ move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0) ∧ t(csl0.last, as2) ∧ aINV(as2) |
aINV(as0), aINV(as), aINV(as2), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as), t((cs ' + csl).last, as0), t(cs, as), t(csl0.last, as2), ¬ move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)) ⊦
| aINV(as0), aINV(as), aINV(as2), cstart(csl0[0]), cstep(csl0.last, ca, cs), frag*(IOAut(cstart, cstep, cext))(cs ' + csl, cal1), frag*(IOAut(cstart, cstep, cext))(csl0, cal0), move(IOAut(astart, astep, aext))(as, cext !(cal1), as0), move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get '), as), t((cs ' + csl).last, as0), t(cs, as), t(csl0.last, as2), ¬ move(IOAut(astart, astep, aext))(as2, (cext(ca) = None ⊃ [];cext(ca).get ') + cext !(cal1), as0), ∀ cs, as. cstart(cs) ∧ t(cs, as) ∧ aINV(as) → astart(as), ∀ asl, aal. frag*(IOAut(astart, astep, aext))(asl, aal) ∧ astart(asl[0]) → aINV(asl.last), ∀ csl1, cal. frag*(IOAut(cstart, cstep, cext))(csl1, cal) ∧ cstart(csl1[0]) → (∃ as. t(csl1.last, as) ∧ aINV(as)) ⊦ |
⊦ move(IOAut(start, step, ext))(s, el1, s1) ∧ move(IOAut(start, step, ext))(s1, el2, s2) → move(IOAut(start, step, ext))(s, el1 + el2, s2)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: cext !(cal1), as2, aext, as0, astart, (cext(ca) = None ⊃ [];cext(ca).get '), as, astep
| ⊦ move(IOAut(start, step, ext))(s, el1, s1) ∧ move(IOAut(start, step, ext))(s1, el2, s2) → move(IOAut(start, step, ext))(s, el1 + el2, s2) |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.