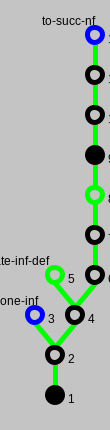
Proof Tree for replstate-inf (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ cext !(πra(step, cstep, ren, cren, ⌜pcs '⌝ + ⌜pcsf⌝ , ⌜paf⌝ )) ⊑ aext !(aα) → repls(step, cstep, cren, ren, aren, cext, aext, ⌜pcs '⌝ + ⌜pcsf⌝ , ⌜paf⌝ , aσ, aα) = lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ ) |
repls(step, cstep, cren, ren, aren, cext, aext, ⌜pcs '⌝ + ⌜pcsf⌝ , ⌜paf⌝ , aσ, aα) ≠ lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ ), cext !(πra(step, cstep, ren, cren, ⌜pcs '⌝ + ⌜pcsf⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
| repls(step, cstep, cren, ren, aren, cext, aext, ⌜pcs '⌝ + ⌜pcsf⌝ , ⌜paf⌝ , aσ, aα) ≠ lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ ), cext !(πra(step, cstep, ren, cren, ⌜pcs '⌝ + ⌜pcsf⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
⊦ ⌜a '⌝ + ⌜nf⌝ = ⌜λ n. (n = 0 ⊃ a;nf(n -1))⌝
repls(step, cstep, cren, ren, aren, cext, aext, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ , aσ, aα) ≠ lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ ), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
Used terms: pcs, pcsf
| ⊦ ⌜a '⌝ + ⌜nf⌝ = ⌜λ n. (n = 0 ⊃ a;nf(n -1))⌝ |
| repls(step, cstep, cren, ren, aren, cext, aext, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ , aσ, aα) ≠ lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ ), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
⊦ cext !(πra(step, cstep, ren, cren, ⌜pcsf⌝ , ⌜paf⌝ )) ⊑ aext !(aα) → repls(step, cstep, cren, ren, aren, cext, aext, ⌜pcsf⌝ , ⌜paf⌝ , aσ, aα) = lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcsf.take(n + 1), paf.take(n), aσ, aα)⌝ ⌝ )
lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ ⌝ ) ≠ lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ ), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
Used terms: aren, ren, paf, step, aext, cren, cstep, aα, aσ, λ n. (n = 0 ⊃ pcs;pcsf(n -1)), cext
| ⊦ cext !(πra(step, cstep, ren, cren, ⌜pcsf⌝ , ⌜paf⌝ )) ⊑ aext !(aα) → repls(step, cstep, cren, ren, aren, cext, aext, ⌜pcsf⌝ , ⌜paf⌝ , aσ, aα) = lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcsf.take(n + 1), paf.take(n), aσ, aα)⌝ ⌝ ) |
| lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ ⌝ ) ≠ lim(⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ ), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ ⌝ ≠ ⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ , cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
| ⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ ⌝ ≠ ⌜λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ⌝ , cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
(λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ ) ≠ (λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
| (λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ ) ≠ (λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ ), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
(λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ )(n) ≠ (λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ )(n), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
| (λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n -1))).take(n + 1), paf.take(n), aσ, aα)⌝ )(n) ≠ (λ n. ⌜repls(step, cstep, cren, ren, aren, cext, aext, pcs + pcsf.take(n), paf.take(n), aσ, aα)⌝ )(n), cext !(πra(step, cstep, ren, cren, ⌜λ n. (n = 0 ⊃ pcs;pcsf(n -1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n - 1))).take(n + 1), paf.take(n), aσ, aα) ≠ repls(step, cstep, cren, ren, aren, cext, aext, pcs ' + pcsf.take(n), paf.take(n), aσ, aα), cext !(πra(step, cstep, ren, cren, ⌜λ n0. (n0 = 0 ⊃ pcs;pcsf(n0 - 1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
Used simplifier rules: ⊦ n -1 = n - 1; (s) ⊦ ⌜x⌝ = ⌜x0⌝ ↔ x = x0; (s) ⊦ a + x = a ' + x; (s)
| repls(step, cstep, cren, ren, aren, cext, aext, (λ n. (n = 0 ⊃ pcs;pcsf(n - 1))).take(n + 1), paf.take(n), aσ, aα) ≠ repls(step, cstep, cren, ren, aren, cext, aext, pcs ' + pcsf.take(n), paf.take(n), aσ, aα), cext !(πra(step, cstep, ren, cren, ⌜λ n0. (n0 = 0 ⊃ pcs;pcsf(n0 - 1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
(λ n. (n = 0 ⊃ pcs;pcsf(n - 1))).take(n + 1) ≠ pcs ' + pcsf.take(n), cext !(πra(step, cstep, ren, cren, ⌜λ n0. (n0 = 0 ⊃ pcs;pcsf(n0 - 1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦
| (λ n. (n = 0 ⊃ pcs;pcsf(n - 1))).take(n + 1) ≠ pcs ' + pcsf.take(n), cext !(πra(step, cstep, ren, cren, ⌜λ n0. (n0 = 0 ⊃ pcs;pcsf(n0 - 1))⌝ , ⌜paf⌝ )) ⊑ aext !(aα) ⊦ |
⊦ nf.take(n + 1) = nf(0) + (λ n. nf(n + 1)).take(n)
Used simplifier rules: ⊦ m + 1 ≠ 0; (s) ⊦ n ≤ m → m + n0 - n = (m - n) + n0; (s) ⊦ n + 0 = n; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ a + x = a ' + x; (s) ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws) a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: λ n. (n = 0 ⊃ pcs;pcsf(n - 1)), n
| ⊦ nf.take(n + 1) = nf(0) + (λ n. nf(n + 1)).take(n) |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.