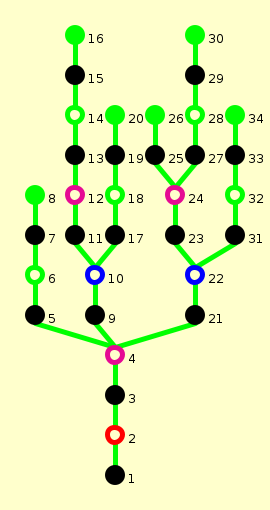
Proof Tree for FOWs-FO-split (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ bel.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 ↔ (∃ bel0, bel1. bel = bel0 + FO(l) ' + bel1 ∧ fowl0 = bel0.FOWs(t, l) ∧ fowl1 = bel1.FOWs(t, l)) |
bel.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 ⊦ ∃ bel0, bel1. bel = bel0 + FO(l) ' + bel1 ∧ fowl0 = bel0.FOWs(t, l) ∧ fowl1 = bel1.FOWs(t, l)
Used simplifier rules: FOWs-append: ⊦ (bel0 + bel1).FOWs(t, l) = bel0.FOWs(t, l) + bel1.FOWs(t, l); FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws)
| bel.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 ⊦ ∃ bel0, bel1. bel = bel0 + FO(l) ' + bel1 ∧ fowl0 = bel0.FOWs(t, l) ∧ fowl1 = bel1.FOWs(t, l) |
(be + bel0).FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: FOWs-base: ⊦ [].FOWs(t, l) = []; List('a) freely generated by [], +;; ⊦ x + y = [] ↔ x = [] ∧ y = []; (s) ⊦ a ' ≠ []; (s) a: ⊦ (x + y) + z = x + y + z; from specification list
| (be + bel0).FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: FOWs-append: ⊦ (bel0 + bel1).FOWs(t, l) = bel0.FOWs(t, l) + bel1.FOWs(t, l); ⊦ a + x = a ' + x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list
| be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, be = SF, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, be = W(l0, v), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, be = FO(l0), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: Bevent freely generated by SF, W, FO;;
| be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, be = SF, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. SF ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: FOWs-one-SF: ⊦ SF '.FOWs(t, l) = []; a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ [] + x = x; (s)
| bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. SF ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. SF ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used terms: t, l, fowl0, fowl1
| bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. SF ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
∀ t0, l0, fowl0, fowl1. bel1.FOWs(t0, l0) + (l0 = l ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l0) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l) ' + bel2 = bel + FO(l0) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l0) ∧ fowl1 = bel3.FOWs(t0, l0)) ⊦ ∃ bel, bel3. SF ' + bel1 + FO(l) ' + bel2 = bel + FO(l) ' + bel3 ∧ bel1.FOWs(t, l) = bel.FOWs(t, l) ∧ bel2.FOWs(t, l) = bel3.FOWs(t, l)
Used simplifier rules: FOWs-append: ⊦ (bel0 + bel1).FOWs(t, l) = bel0.FOWs(t, l) + bel1.FOWs(t, l); FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws)
| ∀ t0, l0, fowl0, fowl1. bel1.FOWs(t0, l0) + (l0 = l ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l0) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l) ' + bel2 = bel + FO(l0) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l0) ∧ fowl1 = bel3.FOWs(t0, l0)) ⊦ ∃ bel, bel3. SF ' + bel1 + FO(l) ' + bel2 = bel + FO(l) ' + bel3 ∧ bel1.FOWs(t, l) = bel.FOWs(t, l) ∧ bel2.FOWs(t, l) = bel3.FOWs(t, l) |
Used simplifier rules: FOWs-SF: ⊦ (SF ' + bel).FOWs(t, l) = bel.FOWs(t, l); a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: SF ' + bel1, bel2
| be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, be = W(l0, v), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
(l = l0 ⊃ W(v, t) ';[]) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: FOWs-one-W: ⊦ W(l0, v) '.FOWs(t, l) = (l = l0 ⊃ W(v, t) ';[]);
| (l = l0 ⊃ W(v, t) ';[]) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
W(v, t) ' + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l = l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
[] + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
| W(v, t) ' + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l = l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
W(v, t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, W(v, t) ∈ fowl0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ FO(tid) ≠ W(v, tid0); (s) ⊦ ¬ a ∈ y → (y + a0 ' + z = a ' + z0 ↔ y = [] ∧ a0 = a ∧ z = z0); (ws) ⊦ a ∈ a0 ' + x ↔ a = a0 ∨ a ∈ x; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) in-14: ⊦ a ' + x = y → a ∈ y; (forward) from specification list
| W(v, t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, W(v, t) ∈ fowl0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
W(v, t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, fowl0 = fow + fowl, W(v, t) ∈ fowl0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used simplifier rules: List('a) freely generated by [], +;; ⊦ [] + x = x; (s) ⊦ a ' + x = a0 ' + y ↔ a = a0 ∧ x = y; (ws) ⊦ FO(tid) ≠ W(v, tid0); (s) a: ⊦ (x + y) + z = x + y + z; from specification list
| W(v, t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, fowl0 = fow + fowl, W(v, t) ∈ fowl0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ W(v, t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used simplifier rules: ⊦ a + x = a ' + x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ a ∈ a0 ' + x ↔ a = a0 ∨ a ∈ x; (s) ⊦ a ' + x = a0 ' + y ↔ a = a0 ∧ x = y; (ws)
| bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ W(v, t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ W(v, t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used terms: t, l0, fowl, fowl1
| bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ W(v, t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
∀ t0, l, fowl0, fowl1. bel1.FOWs(t0, l) + (l = l0 ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l0) ' + bel2 = bel + FO(l) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l) ∧ fowl1 = bel3.FOWs(t0, l)) ⊦ ∃ bel, bel3. W(l0, v) ' + bel1 + FO(l0) ' + bel2 = bel + FO(l0) ' + bel3 ∧ W(v, t) ' + bel1.FOWs(t, l0) = bel.FOWs(t, l0) ∧ bel2.FOWs(t, l0) = bel3.FOWs(t, l0)
Used simplifier rules: FOWs-append: ⊦ (bel0 + bel1).FOWs(t, l) = bel0.FOWs(t, l) + bel1.FOWs(t, l); FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws)
| ∀ t0, l, fowl0, fowl1. bel1.FOWs(t0, l) + (l = l0 ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l0) ' + bel2 = bel + FO(l) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l) ∧ fowl1 = bel3.FOWs(t0, l)) ⊦ ∃ bel, bel3. W(l0, v) ' + bel1 + FO(l0) ' + bel2 = bel + FO(l0) ' + bel3 ∧ W(v, t) ' + bel1.FOWs(t, l0) = bel.FOWs(t, l0) ∧ bel2.FOWs(t, l0) = bel3.FOWs(t, l0) |
Used simplifier rules: FOWs-W: ⊦ (W(l0, v) ' + bel).FOWs(t, l) = (l = l0 ⊃ W(v, t) ';[]) + bel.FOWs(t, l); ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws) a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: W(l0, v) ' + bel1, bel2
| [] + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ [] + x = x; (s)
| bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used terms: t, l, fowl0, fowl1
| bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. W(l0, v) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
l ≠ l0, ∀ t0, l1, fowl0, fowl1. bel1.FOWs(t0, l1) + (l1 = l ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l1) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l) ' + bel2 = bel + FO(l1) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l1) ∧ fowl1 = bel3.FOWs(t0, l1)) ⊦ ∃ bel, bel3. W(l0, v) ' + bel1 + FO(l) ' + bel2 = bel + FO(l) ' + bel3 ∧ bel1.FOWs(t, l) = bel.FOWs(t, l) ∧ bel2.FOWs(t, l) = bel3.FOWs(t, l)
Used simplifier rules: FOWs-append: ⊦ (bel0 + bel1).FOWs(t, l) = bel0.FOWs(t, l) + bel1.FOWs(t, l); FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws)
| l ≠ l0, ∀ t0, l1, fowl0, fowl1. bel1.FOWs(t0, l1) + (l1 = l ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l1) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l) ' + bel2 = bel + FO(l1) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l1) ∧ fowl1 = bel3.FOWs(t0, l1)) ⊦ ∃ bel, bel3. W(l0, v) ' + bel1 + FO(l) ' + bel2 = bel + FO(l) ' + bel3 ∧ bel1.FOWs(t, l) = bel.FOWs(t, l) ∧ bel2.FOWs(t, l) = bel3.FOWs(t, l) |
Used simplifier rules: FOWs-W: ⊦ (W(l0, v) ' + bel).FOWs(t, l) = (l = l0 ⊃ W(v, t) ';[]) + bel.FOWs(t, l); ⊦ [] + x = x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: W(l0, v) ' + bel1, bel2
| be '.FOWs(t, l) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, be = FO(l0), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. be ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
(l = l0 ⊃ FO(t) ';[]) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: FOWs-one-FO: ⊦ FO(l0) '.FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]);
| (l = l0 ⊃ FO(t) ';[]) + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
FO(t) ' + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l = l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
[] + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
| FO(t) ' + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l = l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
FO(t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ a ∈ a0 ' + x ↔ a = a0 ∨ a ∈ x; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) in-14: ⊦ a ' + x = y → a ∈ y; (forward) from specification list
| FO(t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
FO(t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, fowl0 = [], ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
FO(t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, fowl0 = fow + fowl, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used simplifier rules: List('a) freely generated by [], +;;
| FO(t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, fowl0 = [], ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ [] = bel1.FOWs(t, l0) ∧ bel0.FOWs(t, l0) = bel2.FOWs(t, l0)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws) ⊦ [] + x = x; (s)
| ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ [] = bel1.FOWs(t, l0) ∧ bel0.FOWs(t, l0) = bel2.FOWs(t, l0) |
Used simplifier rules: FOWs-base: ⊦ [].FOWs(t, l) = []; ⊦ [] + x = x; (s) ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws) a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: [], bel0
| FO(t) ' + bel0.FOWs(t, l0) = fowl0 + FO(t) ' + fowl1, fowl0 = fow + fowl, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ FO(t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used simplifier rules: ⊦ a + x = a ' + x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ a ' + x = a0 ' + y ↔ a = a0 ∧ x = y; (ws)
| bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ FO(t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ FO(t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)
Used terms: t, l0, fowl, fowl1
| bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1, bel0.FOWs(t, l0) = fowl + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l0) ' + bel2 ∧ fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l0) ' + bel2 ∧ FO(t) ' + fowl = bel1.FOWs(t, l0) ∧ fowl1 = bel2.FOWs(t, l0) |
∀ t0, l, fowl0, fowl1. bel1.FOWs(t0, l) + (l = l0 ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l0) ' + bel2 = bel + FO(l) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l) ∧ fowl1 = bel3.FOWs(t0, l)) ⊦ ∃ bel, bel3. FO(l0) ' + bel1 + FO(l0) ' + bel2 = bel + FO(l0) ' + bel3 ∧ FO(t) ' + bel1.FOWs(t, l0) = bel.FOWs(t, l0) ∧ bel2.FOWs(t, l0) = bel3.FOWs(t, l0)
Used simplifier rules: FOWs-append: ⊦ (bel0 + bel1).FOWs(t, l) = bel0.FOWs(t, l) + bel1.FOWs(t, l); FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws)
| ∀ t0, l, fowl0, fowl1. bel1.FOWs(t0, l) + (l = l0 ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l0) ' + bel2 = bel + FO(l) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l) ∧ fowl1 = bel3.FOWs(t0, l)) ⊦ ∃ bel, bel3. FO(l0) ' + bel1 + FO(l0) ' + bel2 = bel + FO(l0) ' + bel3 ∧ FO(t) ' + bel1.FOWs(t, l0) = bel.FOWs(t, l0) ∧ bel2.FOWs(t, l0) = bel3.FOWs(t, l0) |
Used simplifier rules: FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws) a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: FO(l0) ' + bel1, bel2
| [] + bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ [] + x = x; (s)
| bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)
Used terms: t, l, fowl0, fowl1
| bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1, l ≠ l0, bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)), ∀ t, l, fowl0, fowl1. bel0.FOWs(t, l) = fowl0 + FO(t) ' + fowl1 → (∃ bel1, bel2. bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l)) ⊦ ∃ bel1, bel2. FO(l0) ' + bel0 = bel1 + FO(l) ' + bel2 ∧ fowl0 = bel1.FOWs(t, l) ∧ fowl1 = bel2.FOWs(t, l) |
l ≠ l0, ∀ t0, l1, fowl0, fowl1. bel1.FOWs(t0, l1) + (l1 = l ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l1) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l) ' + bel2 = bel + FO(l1) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l1) ∧ fowl1 = bel3.FOWs(t0, l1)) ⊦ ∃ bel, bel3. FO(l0) ' + bel1 + FO(l) ' + bel2 = bel + FO(l) ' + bel3 ∧ bel1.FOWs(t, l) = bel.FOWs(t, l) ∧ bel2.FOWs(t, l) = bel3.FOWs(t, l)
Used simplifier rules: FOWs-append: ⊦ (bel0 + bel1).FOWs(t, l) = bel0.FOWs(t, l) + bel1.FOWs(t, l); FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws)
| l ≠ l0, ∀ t0, l1, fowl0, fowl1. bel1.FOWs(t0, l1) + (l1 = l ⊃ FO(t0) ';[]) + bel2.FOWs(t0, l1) = fowl0 + FO(t0) ' + fowl1 → (∃ bel, bel3. bel1 + FO(l) ' + bel2 = bel + FO(l1) ' + bel3 ∧ fowl0 = bel.FOWs(t0, l1) ∧ fowl1 = bel3.FOWs(t0, l1)) ⊦ ∃ bel, bel3. FO(l0) ' + bel1 + FO(l) ' + bel2 = bel + FO(l) ' + bel3 ∧ bel1.FOWs(t, l) = bel.FOWs(t, l) ∧ bel2.FOWs(t, l) = bel3.FOWs(t, l) |
Used simplifier rules: FOWs-FO: ⊦ (FO(l0) ' + bel).FOWs(t, l) = (l = l0 ⊃ FO(t) ';[]) + bel.FOWs(t, l); ⊦ [] + x = x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: FO(l0) ' + bel1, bel2
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.