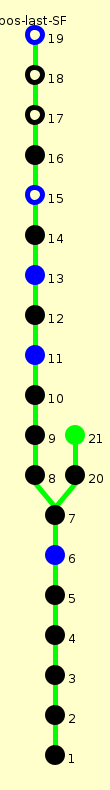
Proof Tree for rely-PROP_FO (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ ( ctrok(gs.fctr, gs.fwriters) ∧ writersOk(gs.bq, gs.pq, gs.fwriters) ∧ pendingOk(gs.bq, gs.pq) ∧ SFTrailing(gs.bq) ∧ readFOsOk(gs.rfo, gs.fwriters)) ∧ (∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid))) ∧ ⟨fwriters := gs.fwriters, pq := gs.pq, bq := gs.bq, rfo := gs.rfo; PROP_FO(tid, l, fwriters; pq, bq, rfo); gs := ((gs.pq:= pq).bq:= bq).rfo:= rfo⟩ (gs0 = gs) → (∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0))) |
⟨fwriters := gs.fwriters, pq := gs.pq, bq := gs.bq, rfo := gs.rfo; PROP_FO(tid, l, fwriters; pq, bq, rfo); gs := ((gs.pq:= pq).bq:= bq).rfo:= rfo⟩ (gs0 = gs), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0))
| ⟨fwriters := gs.fwriters, pq := gs.pq, bq := gs.bq, rfo := gs.rfo; PROP_FO(tid, l, fwriters; pq, bq, rfo); gs := ((gs.pq:= pq).bq:= bq).rfo:= rfo⟩ (gs0 = gs), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0)) |
⟨PROP_FO(tid, l, fwriters; pq, bq, rfo); gs := ((gs.pq:= pq).bq:= bq).rfo:= rfo⟩ (gs0 = gs), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0))
| ⟨PROP_FO(tid, l, fwriters; pq, bq, rfo); gs := ((gs.pq:= pq).bq:= bq).rfo:= rfo⟩ (gs0 = gs), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0)) |
⟨gs := ((gs.pq:= pq0).bq:= bq0).rfo:= rfo0⟩ (gs0 = gs), ⟨PROP_FO(tid, l, fwriters; pq, bq, rfo)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0))
| ⟨gs := ((gs.pq:= pq0).bq:= bq0).rfo:= rfo0⟩ (gs0 = gs), ⟨PROP_FO(tid, l, fwriters; pq, bq, rfo)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0)) |
⟨PROP_FO(tid, l, fwriters; pq, bq, rfo)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, gs0 = ((gs.pq:= pq0).bq:= bq0).rfo:= rfo0, pq = gs.pq, rfo = gs.rfo, SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0))
| ⟨PROP_FO(tid, l, fwriters; pq, bq, rfo)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, gs0 = ((gs.pq:= pq0).bq:= bq0).rfo:= rfo0, pq = gs.pq, rfo = gs.rfo, SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∃ n. n < # gs.bq(tid) ∧ isPropFO(n, l, gs.bq(tid)) ⊦ ∀ t0. relyws(t0, gs.freaders, gs0.freaders) ∧ relyws(t0, gs.fwriters, gs0.fwriters) ∧ rely(t0, gs.pq, gs.bq, gs0.pq, gs0.bq) ∧ gs.bq(t0) ⊒w gs0.bq(t0) ∧ (gs.rfo(t0) = [] → gs0.rfo(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs0.rfo(t0) = gs0.bq(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → gs0.rfo(t0) + SF ' = gs0.bq(t0) ∨ gs0.rfo(t0) = gs0.bq(t0)) |
⟨PROP_FO(tid, l, gs.fwriters; pq, bq, rfo)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0))
Used simplifier rules: ⊦ # x = 0 ↔ x = []; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ (gs.bq:= bq).bq = bq; (s) ⊦ (gs.rfo:= bq0).bq = gs.bq; (s) ⊦ (gs.rfo:= bq0).rfo = bq0; (s) ⊦ (gs.pq:= pq).pq = pq; (s) ⊦ (gs.bq:= bq).pq = gs.pq; (s) ⊦ (gs.rfo:= bq0).pq = gs.pq; (s) ⊦ relyws(t, tsf, tsf); (s) ⊦ (gs.pq:= pq).fwriters = gs.fwriters; (s) ⊦ (gs.bq:= bq).fwriters = gs.fwriters; (s) ⊦ (gs.rfo:= bq0).fwriters = gs.fwriters; (s) ⊦ (gs.pq:= pq).freaders = gs.freaders; (s) ⊦ (gs.bq:= bq).freaders = gs.freaders; (s) ⊦ (gs.rfo:= bq0).freaders = gs.freaders; (s)
| ⟨PROP_FO(tid, l, gs.fwriters; pq, bq, rfo)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0)) |
⟨choose n with n < # bq(tid) ∧ isPropFO(n, l, bq(tid)) in pq(l) := pq(l) + FO(tid), bq(tid) := bq(tid) -p n, rfo(tid) := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n) ifnone skip⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0))
Used simplifier rules: decl: PROP_FO(tid, l, fwriters; pq, bq, rfo) {choose n with n < # bq(tid) ∧ isPropFO(n, l, bq(tid)) in pq(l) := pq(l) + FO(tid), bq(tid) := bq(tid) -p n, rfo(tid) := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n) ifnone skip };
| ⟨choose n with n < # bq(tid) ∧ isPropFO(n, l, bq(tid)) in pq(l) := pq(l) + FO(tid), bq(tid) := bq(tid) -p n, rfo(tid) := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n) ifnone skip⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0)) |
⟨pq(l) := pq(l) + FO(tid), bq(tid) := bq(tid) -p n, rfo(tid) := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n0 < # gs.bq(tid), n < # bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(tid)), isPropFO(n, l, bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0))
⟨skip⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∀ n. ¬(n < # bq(tid) ∧ isPropFO(n, l, bq(tid))) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0))
| ⟨pq(l) := pq(l) + FO(tid), bq(tid) := bq(tid) -p n, rfo(tid) := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n0 < # gs.bq(tid), n < # bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(tid)), isPropFO(n, l, bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0)) |
⟨pq(l) := pq(l) + FO(tid) ', bq(tid) := bq(tid) -p n, rfo(tid) := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), n0 < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), isPropFO(n0, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0))
Used simplifier rules: ⊦ x + a = x + a '; (s)
| ⟨pq(l) := pq(l) + FO(tid) ', bq(tid) := bq(tid) -p n, rfo(tid) := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n)⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), n0 < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), isPropFO(n0, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0)) |
pq(l := pq(l) + FO(tid) ') = pq0, bq(tid := bq(tid) -p n) = bq0, rfo(tid := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n)) = rfo0, bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n0 < # gs.bq(tid), n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(tid)), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0))
| pq(l := pq(l) + FO(tid) ') = pq0, bq(tid := bq(tid) -p n) = bq0, rfo(tid := (tid ∈ fwriters(l) ⊃ rfo(tid);rfo(tid) -p n)) = rfo0, bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n0 < # gs.bq(tid), n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(tid)), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0)) |
gs.bq(tid) ≠ [], n < # gs.bq(tid), n0 < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), isPropFO(n0, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ gs.bq(t0) ⊒w (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∧ (gs.rfo(t0) = [] → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0))) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) + SF ' = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∨ (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)))
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ isPropFO(n, l, bq(t0)) → rely(t, pq, bq, pq(l := pq(l) + FO(t0) '), bq(t0 := bq(t0) -p n)); (ss)
| gs.bq(tid) ≠ [], n < # gs.bq(tid), n0 < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), isPropFO(n0, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ gs.bq(t0) ⊒w (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∧ (gs.rfo(t0) = [] → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0))) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) + SF ' = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∨ (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0))) |
tid = t0, gs.bq(tid) ≠ [], n0 < # gs.bq(tid), n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(tid)), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ gs.bq(t0) ⊒w (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∧ (gs.rfo(t0) = [] → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0))) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) + SF ' = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∨ (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)))
Used simplifier rules: ⊦ bel ⊒w bel; (s) Used formulas: tid = t0
| tid = t0, gs.bq(tid) ≠ [], n0 < # gs.bq(tid), n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(tid)), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ gs.bq(t0) ⊒w (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∧ (gs.rfo(t0) = [] → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0))) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) + SF ' = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0)) ∨ (tid = t0 ⊃ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n);gs.rfo(t0)) = (tid = t0 ⊃ gs.bq(t0) -p n;gs.bq(t0))) |
gs.bq(t0) ≠ [], n0 < # gs.bq(t0), n < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(t0)), isPropFO(n, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ (gs.rfo(t0) = [] → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) + SF ' = gs.bq(t0) -p n ∨ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n)
Used simplifier rules: ⊦ # x = 0 ↔ x = []; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ isPropFO(n, l, bel) → bel ⊒w bel -p n; (ss)
| gs.bq(t0) ≠ [], n0 < # gs.bq(t0), n < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(t0)), isPropFO(n, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters) ⊦ (gs.rfo(t0) = [] → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) + SF ' = gs.bq(t0) -p n ∨ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n) |
gs.bq(t0) ≠ [], n < # gs.bq(t0), n0 < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(t0)), isPropFO(n0, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ¬ t0 ∈ gs.fwriters(l) ⊦ (gs.rfo(t0) = [] → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) + SF ' = gs.bq(t0) -p n ∨ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n)
Used simplifier rules: readFOsOk-empty-rfo-while-writing: ⊦ readFOsOk(rfo, writers) ∧ t ∈ writers(l) → rfo(t) = []; (forward) from specification FLIT-preds ne-01: ⊦ a ∈ s → s ≠ ∅; (forward) from specification set-basic size-zero-01: ⊦ s ≠ ∅ → # s ≠ 0; (forward) from specification set-basic ⊦ ctrok(ctr, writers) → # writers(l) = ctr(l); (s) ⊦ [] + x = x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ # a ' = 0 +1; (s) ⊦ m < 1 ↔ m = 0; (s) ⊦ a ' ≠ []; (s) ⊦ a ' -p 0 = []; (s) Used formulas: t0 ∈ gs.fwriters(l)
| gs.bq(t0) ≠ [], n < # gs.bq(t0), n0 < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(t0)), isPropFO(n0, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ¬ t0 ∈ gs.fwriters(l) ⊦ (gs.rfo(t0) = [] → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n) ∧ ( gs.rfo(t0) + SF ' = gs.bq(t0) → (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) + SF ' = gs.bq(t0) -p n ∨ (t0 ∈ gs.fwriters(l) ⊃ gs.rfo(t0);gs.rfo(t0) -p n) = gs.bq(t0) -p n) |
gs.bq(t0) ≠ [], n0 < # gs.bq(t0), n < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(t0)), isPropFO(n, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ¬ t0 ∈ gs.fwriters(l) ⊦ (gs.rfo(t0) = [] → gs.rfo(t0) -p n = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs.rfo(t0) -p n = gs.bq(t0) -p n) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → (gs.rfo(t0) -p n) + SF ' = gs.bq(t0) -p n ∨ gs.rfo(t0) -p n = gs.bq(t0) -p n)
| gs.bq(t0) ≠ [], n0 < # gs.bq(t0), n < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(t0)), isPropFO(n, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ¬ t0 ∈ gs.fwriters(l) ⊦ (gs.rfo(t0) = [] → gs.rfo(t0) -p n = []) ∧ (gs.rfo(t0) = gs.bq(t0) → gs.rfo(t0) -p n = gs.bq(t0) -p n) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → (gs.rfo(t0) -p n) + SF ' = gs.bq(t0) -p n ∨ gs.rfo(t0) -p n = gs.bq(t0) -p n) |
gs.rfo(t0) + SF ' = gs.bq(t0), (gs.rfo(t0) -p n) + SF ' ≠ gs.bq(t0) -p n, gs.rfo(t0) -p n ≠ gs.bq(t0) -p n, gs.bq(t0) ≠ [], n < # gs.bq(t0), n0 < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(t0)), isPropFO(n0, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ¬ t0 ∈ gs.fwriters(l) ⊦
Used simplifier rules: ⊦ [] -p n = []; (s)
| gs.rfo(t0) + SF ' = gs.bq(t0), (gs.rfo(t0) -p n) + SF ' ≠ gs.bq(t0) -p n, gs.rfo(t0) -p n ≠ gs.bq(t0) -p n, gs.bq(t0) ≠ [], n < # gs.bq(t0), n0 < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(t0)), isPropFO(n0, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ¬ t0 ∈ gs.fwriters(l) ⊦ |
gs.rfo(t0) + SF ' = gs.bq(t0), (gs.rfo(t0) -p n) + SF ' ≠ gs.bq(t0) -p n, gs.rfo(t0) -p n ≠ gs.bq(t0) -p n, gs.bq(t0) ≠ [], n0 < # gs.bq(t0), n < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(t0)), isPropFO(n, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), SF ∈ gs.bq(t0), ¬ t0 ∈ gs.fwriters(l) ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list in-15: ⊦ x + a ' = y → a ∈ y; (forward) from specification list
| gs.rfo(t0) + SF ' = gs.bq(t0), (gs.rfo(t0) -p n) + SF ' ≠ gs.bq(t0) -p n, gs.rfo(t0) -p n ≠ gs.bq(t0) -p n, gs.bq(t0) ≠ [], n0 < # gs.bq(t0), n < # gs.bq(t0), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n0, l, gs.bq(t0)), isPropFO(n, l, gs.bq(t0)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), SF ∈ gs.bq(t0), ¬ t0 ∈ gs.fwriters(l) ⊦ |
gs.rfo(t0) + SF ' = gs.bq(t0), (gs.rfo(t0) -p n) + SF ' ≠ (gs.rfo(t0) + SF ') -p n, gs.rfo(t0) + SF ' ≠ [], gs.rfo(t0) -p n ≠ (gs.rfo(t0) + SF ') -p n, n < #(gs.rfo(t0) + SF '), n0 < #(gs.rfo(t0) + SF '), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.rfo(t0) + SF '), isPropFO(n0, l, gs.rfo(t0) + SF '), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), SF ∈ gs.rfo(t0) + SF ', ¬ t0 ∈ gs.fwriters(l) ⊦
| gs.rfo(t0) + SF ' = gs.bq(t0), (gs.rfo(t0) -p n) + SF ' ≠ (gs.rfo(t0) + SF ') -p n, gs.rfo(t0) + SF ' ≠ [], gs.rfo(t0) -p n ≠ (gs.rfo(t0) + SF ') -p n, n < #(gs.rfo(t0) + SF '), n0 < #(gs.rfo(t0) + SF '), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.rfo(t0) + SF '), isPropFO(n0, l, gs.rfo(t0) + SF '), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), SF ∈ gs.rfo(t0) + SF ', ¬ t0 ∈ gs.fwriters(l) ⊦ |
⊦ isPropFO(n, l, bel + SF ') → (bel + SF ') -p n = (bel -p n) + SF '
Used terms: l, n, gs.rfo(t0)
| ⊦ isPropFO(n, l, bel + SF ') → (bel + SF ') -p n = (bel -p n) + SF ' |
| ⟨skip⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, fwriters = gs.fwriters, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∀ n. ¬(n < # bq(tid) ∧ isPropFO(n, l, bq(tid))) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0)) |
⟨skip⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∀ n0. ¬ n0 < # gs.bq(tid) ∨ ¬ isPropFO(n0, l, gs.bq(tid)) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0))
| ⟨skip⟩ (pq = pq0 ∧ bq = bq0 ∧ rfo = rfo0), bq = gs.bq, pq = gs.pq, rfo = gs.rfo, gs.bq(tid) ≠ [], n < # gs.bq(tid), SFTrailing(gs.bq), ctrok(gs.fctr, gs.fwriters), isPropFO(n, l, gs.bq(tid)), pendingOk(gs.bq, gs.pq), readFOsOk(gs.rfo, gs.fwriters), writersOk(gs.bq, gs.pq, gs.fwriters), ∀ n0. ¬ n0 < # gs.bq(tid) ∨ ¬ isPropFO(n0, l, gs.bq(tid)) ⊦ rely(t0, gs.pq, gs.bq, pq0, bq0) ∧ gs.bq(t0) ⊒w bq0(t0) ∧ (gs.rfo(t0) = [] → rfo0(t0) = []) ∧ (gs.rfo(t0) = gs.bq(t0) → rfo0(t0) = bq0(t0)) ∧ (gs.rfo(t0) + SF ' = gs.bq(t0) → rfo0(t0) + SF ' = bq0(t0) ∨ rfo0(t0) = bq0(t0)) |
Used terms: n
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.