Proof Tree for plibStep-lem (View conclusion)
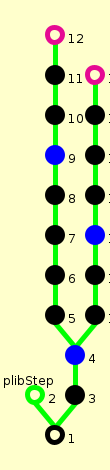
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ plibStep(mkstate(gs, lsf, pcf), a, mkstate(gs0, lsf0, pcf0)) ↔ (∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), a, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)) ∨ a = globalACrash ∧ gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) ∨ (∃ l. a = globalAPersist(l) ∧ firstVolWrite(l, gs.h) < # gs.h ∧ gs0 = (gs.pm:= gs.pm(l := gs.h[firstVolWrite(l, gs.h)]._1.v)) .h:= ( gs.h.take(firstVolWrite(l, gs.h)) + ((gs.h[firstVolWrite(l, gs.h)]._1, true) + persistDependentReads(l, gs.h.drop(firstVolWrite(l, gs.h) + 1)))) ∧ lsf0 = lsf ∧ pcf0 = pcf) |
⊦ plibStep(mkstate(gs, lsf, pcf), a, mkstate(gs0, lsf0, pcf0)) ↔ (∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), a, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)) ∨ a = globalACrash ∧ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ∨ (∃ l. a = globalAPersist(l) ∧ firstVolWrite(l, gs.h) < # gs.h ∧ gs0 = (gs.pm:= gs.pm(l := gs.h[firstVolWrite(l, gs.h)]._1.v)) .h:= ( gs.h.take(firstVolWrite(l, gs.h)) + ((gs.h[firstVolWrite(l, gs.h)]._1, true) + persistDependentReads(l, gs.h.drop(firstVolWrite(l, gs.h) + 1)))) ∧ lsf0 = lsf ∧ pcf0 = pcf)
⊦ (∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), a, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)) ∨ a = globalACrash ∧ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ∨ (∃ l. a = globalAPersist(l) ∧ firstVolWrite(l, gs.h) < # gs.h ∧ gs0 = (gs.pm:= gs.pm(l := gs.h[firstVolWrite(l, gs.h)]._1.v)) .h:= ( gs.h.take(firstVolWrite(l, gs.h)) + ((gs.h[firstVolWrite(l, gs.h)]._1, true) + persistDependentReads(l, gs.h.drop(firstVolWrite(l, gs.h) + 1)))) ∧ lsf0 = lsf ∧ pcf0 = pcf) ↔ (∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), a, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)) ∨ a = globalACrash ∧ gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) ∨ (∃ l. a = globalAPersist(l) ∧ firstVolWrite(l, gs.h) < # gs.h ∧ gs0 = (gs.pm:= gs.pm(l := gs.h[firstVolWrite(l, gs.h)]._1.v)) .h:= ( gs.h.take(firstVolWrite(l, gs.h)) + ((gs.h[firstVolWrite(l, gs.h)]._1, true) + persistDependentReads(l, gs.h.drop(firstVolWrite(l, gs.h) + 1)))) ∧ lsf0 = lsf ∧ pcf0 = pcf)
Used terms: pcf0, gs0, lsf0, pcf, lsf, gs, a
| ⊦ plibStep(mkstate(gs, lsf, pcf), a, mkstate(gs0, lsf0, pcf0)) ↔ (∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), a, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)) ∨ a = globalACrash ∧ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ∨ (∃ l. a = globalAPersist(l) ∧ firstVolWrite(l, gs.h) < # gs.h ∧ gs0 = (gs.pm:= gs.pm(l := gs.h[firstVolWrite(l, gs.h)]._1.v)) .h:= ( gs.h.take(firstVolWrite(l, gs.h)) + ((gs.h[firstVolWrite(l, gs.h)]._1, true) + persistDependentReads(l, gs.h.drop(firstVolWrite(l, gs.h) + 1)))) ∧ lsf0 = lsf ∧ pcf0 = pcf) |
| ⊦ (∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), a, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)) ∨ a = globalACrash ∧ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ∨ (∃ l. a = globalAPersist(l) ∧ firstVolWrite(l, gs.h) < # gs.h ∧ gs0 = (gs.pm:= gs.pm(l := gs.h[firstVolWrite(l, gs.h)]._1.v)) .h:= ( gs.h.take(firstVolWrite(l, gs.h)) + ((gs.h[firstVolWrite(l, gs.h)]._1, true) + persistDependentReads(l, gs.h.drop(firstVolWrite(l, gs.h) + 1)))) ∧ lsf0 = lsf ∧ pcf0 = pcf) ↔ (∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), a, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)) ∨ a = globalACrash ∧ gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) ∨ (∃ l. a = globalAPersist(l) ∧ firstVolWrite(l, gs.h) < # gs.h ∧ gs0 = (gs.pm:= gs.pm(l := gs.h[firstVolWrite(l, gs.h)]._1.v)) .h:= ( gs.h.take(firstVolWrite(l, gs.h)) + ((gs.h[firstVolWrite(l, gs.h)]._1, true) + persistDependentReads(l, gs.h.drop(firstVolWrite(l, gs.h) + 1)))) ∧ lsf0 = lsf ∧ pcf0 = pcf) |
⊦ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ↔ gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)
Used simplifier rules: disj-globalACrash-globalAPersist: ⊦ globalACrash ≠ globalAPersist(l); a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ a + x = a ' + x; (s) ⊦ firstVolWrite(l, h) < # h ↔ (h |W | l) | false ≠ []; (s)
| ⊦ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ↔ gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc) |
⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed))
gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf0 = lsf, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) ⊦ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf), ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)
| ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf) ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) |
⟨ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf), h = gs.h, pm = gs.pm, vm = gs.vm ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed))
| ⟨ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf), h = gs.h, pm = gs.pm, vm = gs.vm ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) |
⟨gs := (gs.vm:= vm0).h:= h0⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf1), ⟨ACrash(pm; vm, h, pcf)⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), h = gs.h, pm = gs.pm, vm = gs.vm ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed))
| ⟨gs := (gs.vm:= vm0).h:= h0⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf1), ⟨ACrash(pm; vm, h, pcf)⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), h = gs.h, pm = gs.pm, vm = gs.vm ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) |
⟨ACrash(pm; vm, h, pcf)⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), gs0 = (gs.vm:= vm0).h:= h0, h = gs.h, lsf0 = lsf, pcf0 = pcf1, pm = gs.pm, vm = gs.vm ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed))
| ⟨ACrash(pm; vm, h, pcf)⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), gs0 = (gs.vm:= vm0).h:= h0, h = gs.h, lsf0 = lsf, pcf0 = pcf1, pm = gs.pm, vm = gs.vm ⊦ ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc), gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ lsf0 = lsf ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) |
⟨ACrash(gs.pm; vm, h, pcf)⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), h = gs.h, vm = gs.vm ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= vm0).h:= h0, lsf(t0), pc) ∧ pcf1 = pcf(t0 := pc), (gs.vm:= vm0).h:= h0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ pcf1(t) = (pcf(t) = idle ⊃ idle;crashed)
| ⟨ACrash(gs.pm; vm, h, pcf)⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), h = gs.h, vm = gs.vm ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= vm0).h:= h0, lsf(t0), pc) ∧ pcf1 = pcf(t0 := pc), (gs.vm:= vm0).h:= h0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ pcf1(t) = (pcf(t) = idle ⊃ idle;crashed) |
⟨pcf := λ t. (pcf(t) = idle ⊃ idle;crashed), vm := pm, h := h | true⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), h = gs.h, pm = gs.pm, vm = gs.vm ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= vm0).h:= h0, lsf(t0), pc) ∧ pcf1 = pcf(t0 := pc), (gs.vm:= vm0).h:= h0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ pcf1(t) = (pcf(t) = idle ⊃ idle;crashed)
Used simplifier rules: ACrash: ⊦ ;
| ⟨pcf := λ t. (pcf(t) = idle ⊃ idle;crashed), vm := pm, h := h | true⟩ (vm = vm0 ∧ h = h0 ∧ pcf = pcf1), h = gs.h, pm = gs.pm, vm = gs.vm ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= vm0).h:= h0, lsf(t0), pc) ∧ pcf1 = pcf(t0 := pc), (gs.vm:= vm0).h:= h0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ pcf1(t) = (pcf(t) = idle ⊃ idle;crashed) |
(λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf1, h = gs.h, pm = gs.pm, pm = vm0, vm = gs.vm, h | true = h0 ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= vm0).h:= h0, lsf(t0), pc) ∧ pcf1 = pcf(t0 := pc), (gs.vm:= vm0).h:= h0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ pcf1(t) = (pcf(t) = idle ⊃ idle;crashed)
| (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf1, h = gs.h, pm = gs.pm, pm = vm0, vm = gs.vm, h | true = h0 ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= vm0).h:= h0, lsf(t0), pc) ∧ pcf1 = pcf(t0 := pc), (gs.vm:= vm0).h:= h0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true) ∧ pcf1(t) = (pcf(t) = idle ⊃ idle;crashed) |
(gs.vm:= gs.pm).h:= (gs.h | true) ≠ mkPLIBgs(gs.pm, gs.pm, gs.h | true) ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= gs.pm).h:= (gs.h | true), lsf(t0), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t0 := pc)
| (gs.vm:= gs.pm).h:= (gs.h | true) ≠ mkPLIBgs(gs.pm, gs.pm, gs.h | true) ⊦ ∃ t0, pc. lstep(gs, lsf(t0), pcf(t0), globalACrash, (gs.vm:= gs.pm).h:= (gs.h | true), lsf(t0), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t0 := pc) |
Used simplifier rules: gen-PLIBGState: ⊦ ; upd-mkPLIBgs-dotvm: ⊦ mkPLIBgs(vm, vm0, h).vm:= vm1 = mkPLIBgs(vm1, vm0, h); upd-mkPLIBgs-doth: ⊦ mkPLIBgs(vm, vm0, h).h:= h0 = mkPLIBgs(vm, vm0, h0); sel-mkPLIBgs-dotpm: ⊦ mkPLIBgs(vm, vm0, h).pm = vm0; sel-mkPLIBgs-doth: ⊦ mkPLIBgs(vm, vm0, h).h = h; inj-mkPLIBgs: ⊦ mkPLIBgs(vm, vm0, h) = mkPLIBgs(vm1, vm2, h0) ↔ vm = vm1 ∧ vm0 = vm2 ∧ h = h0;
| gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf0 = lsf, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) ⊦ ⟨pm := gs.pm, vm := gs.vm, h := gs.h; ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf), ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc) |
gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, lsf0 = lsf, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ⟨ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf), ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc)
| gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, lsf0 = lsf, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ⟨ACrash(pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ lsf0 = lsf ∧ pcf0 = pcf), ∃ t, ls, pc. lstep(gs, lsf(t), pcf(t), globalACrash, gs0, ls, pc) ∧ lsf0 = lsf(t := ls) ∧ pcf0 = pcf(t := pc) |
gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), vm = gs.vm ⊦ ⟨ACrash(gs.pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ pcf0 = pcf), ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc)
| gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), vm = gs.vm ⊦ ⟨ACrash(gs.pm; vm, h, pcf); gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ pcf0 = pcf), ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc) |
gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ⟨pcf := λ t. (pcf(t) = idle ⊃ idle;crashed), vm := pm, h := h | true; gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ pcf0 = pcf), ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc)
Used simplifier rules: ACrash: ⊦ ;
| gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ⟨pcf := λ t. (pcf(t) = idle ⊃ idle;crashed), vm := pm, h := h | true; gs := (gs.vm:= vm).h:= h⟩ (gs0 = gs ∧ pcf0 = pcf), ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc) |
gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ⟨gs := (gs.vm:= pm).h:= (h | true)⟩ (gs0 = gs ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed))), ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc)
| gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ⟨gs := (gs.vm:= pm).h:= (h | true)⟩ (gs0 = gs ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed))), ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc) |
gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc), gs0 = (gs.vm:= pm).h:= (h | true) ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed))
| gs0 = mkPLIBgs(gs.pm, gs.pm, gs.h | true), h = gs.h, pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)), pm = gs.pm, vm = gs.vm ⊦ ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc), gs0 = (gs.vm:= pm).h:= (h | true) ∧ pcf0 = (λ t. (pcf(t) = idle ⊃ idle;crashed)) |
mkPLIBgs(gs.pm, gs.pm, gs.h | true) ≠ (gs.vm:= gs.pm).h:= (gs.h | true) ⊦ ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc)
| mkPLIBgs(gs.pm, gs.pm, gs.h | true) ≠ (gs.vm:= gs.pm).h:= (gs.h | true) ⊦ ∃ t, pc. lstep(gs, lsf(t), pcf(t), globalACrash, mkPLIBgs(gs.pm, gs.pm, gs.h | true), lsf(t), pc) ∧ (λ t. (pcf(t) = idle ⊃ idle;crashed)) = pcf(t := pc) |
Used simplifier rules: gen-PLIBGState: ⊦ ; sel-mkPLIBgs-dotpm: ⊦ mkPLIBgs(vm, vm0, h).pm = vm0; upd-mkPLIBgs-dotvm: ⊦ mkPLIBgs(vm, vm0, h).vm:= vm1 = mkPLIBgs(vm1, vm0, h); sel-mkPLIBgs-doth: ⊦ mkPLIBgs(vm, vm0, h).h = h; upd-mkPLIBgs-doth: ⊦ mkPLIBgs(vm, vm0, h).h:= h0 = mkPLIBgs(vm, vm0, h0); inj-mkPLIBgs: ⊦ mkPLIBgs(vm, vm0, h) = mkPLIBgs(vm1, vm2, h0) ↔ vm = vm1 ∧ vm0 = vm2 ∧ h = h0;
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.