Proof Tree for abs-addWriteFO (View conclusion)
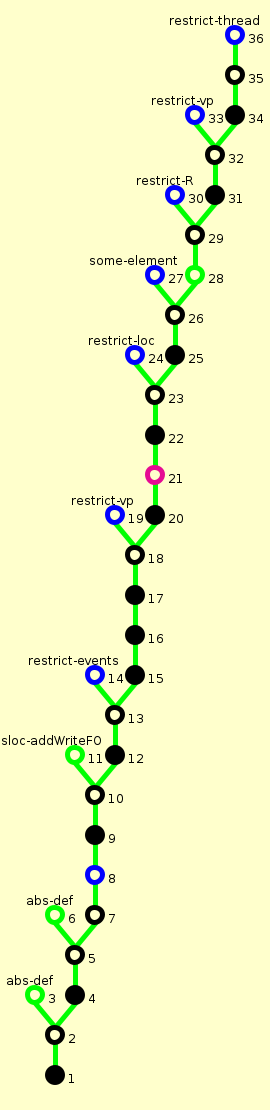
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ ((h | t) | false)|R = [] → (abs(h, rs, p(l := p(l) + FO(t) ')) ↔ abs(h, rs, p)) |
((h | t) | false)|R = [], ¬(abs(h, rs, p(l := p(l) + FO(t) ')) ↔ abs(h, rs, p)) ⊦
| ((h | t) | false)|R = [], ¬(abs(h, rs, p(l := p(l) + FO(t) ')) ↔ abs(h, rs, p)) ⊦ |
⊦ abs(h, rs, p) ↔ (∀ l. absloc(events((h | l) | false), rs(l), p(l)))
((h | t) | false)|R = [] ⊦ (∀ l0. absloc(events((h | l0) | false), rs(l0), p(l := p(l) + FO(t) ')(l0))) ↔ abs(h, rs, p)
Used terms: h, rs, p(l := p(l) + FO(t) ')
| ⊦ abs(h, rs, p) ↔ (∀ l. absloc(events((h | l) | false), rs(l), p(l))) |
| ((h | t) | false)|R = [] ⊦ (∀ l0. absloc(events((h | l0) | false), rs(l0), p(l := p(l) + FO(t) ')(l0))) ↔ abs(h, rs, p) |
((h | t) | false)|R = [] ⊦ (∀ l0. absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0)))) ↔ abs(h, rs, p)
| ((h | t) | false)|R = [] ⊦ (∀ l0. absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0)))) ↔ abs(h, rs, p) |
⊦ abs(h, rs, p) ↔ (∀ l. absloc(events((h | l) | false), rs(l), p(l)))
((h | t) | false)|R = [] ⊦ (∀ l0. absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0)))) ↔ (∀ l. absloc(events((h | l) | false), rs(l), p(l)))
Used terms: h, rs, p
| ⊦ abs(h, rs, p) ↔ (∀ l. absloc(events((h | l) | false), rs(l), p(l))) |
| ((h | t) | false)|R = [] ⊦ (∀ l0. absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0)))) ↔ (∀ l. absloc(events((h | l) | false), rs(l), p(l))) |
((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0))) ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦
| ((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0))) ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦ |
l = l0, ((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0))) ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦
Used formulas: l = l0
| l = l0, ((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), (l = l0 ⊃ p(l0) + FO(t) ';p(l0))) ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦ |
((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), p(l0) + FO(t) ') ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦
| ((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), p(l0) + FO(t) ') ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦ |
⊦ (∀ e. e ∈ el ∧ e.R? → e.t ≠ t) → (absloc(el, rset, fowl + FO(t) ') ↔ absloc(el, rset, fowl))
((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), p(l0) + FO(t) ') ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦ ∀ e. e ∈ events((h | l0) | false) ∧ e.R? → e.t ≠ t
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list Used terms: events((h | l0) | false), t, rs(l0), p(l0)
| ⊦ (∀ e. e ∈ el ∧ e.R? → e.t ≠ t) → (absloc(el, rset, fowl + FO(t) ') ↔ absloc(el, rset, fowl)) |
| ((h | t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), p(l0) + FO(t) ') ↔ absloc(events((h | l0) | false), rs(l0), p(l0))) ⊦ ∀ e. e ∈ events((h | l0) | false) ∧ e.R? → e.t ≠ t |
((h | e.t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(events((h | l0) | false), rs(l0), p(l0))), e.R?, e ∈ events((h | l0) | false) ⊦
| ((h | e.t) | false)|R = [], ¬(absloc(events((h | l0) | false), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(events((h | l0) | false), rs(l0), p(l0))), e.R?, e ∈ events((h | l0) | false) ⊦ |
⊦ events(h) = h.map(λ vpe. vpe._1)
((h | e.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(λ vpe. vpe._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(((h | l0) | false).map(λ vpe. vpe._1), rs(l0), p(l0))), e.R?, e ∈ ((h | l0) | false).map(λ vpe. vpe._1) ⊦
Used terms: (h | l0) | false
| ⊦ events(h) = h.map(λ vpe. vpe._1) |
| ((h | e.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(λ vpe. vpe._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(((h | l0) | false).map(λ vpe. vpe._1), rs(l0), p(l0))), e.R?, e ∈ ((h | l0) | false).map(λ vpe. vpe._1) ⊦ |
((h | vpe._1.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(._1), rs(l0), p(l0) + FO(vpe._1.t) ') ↔ absloc(((h | l0) | false).map(._1), rs(l0), p(l0))), vpe._1.R?, vpe ∈ (h | l0) | false ⊦
Used simplifier rules: ⊦ b ∈ x.map(f) ↔ (∃ a. b = f(a) ∧ a ∈ x); (as)
| ((h | vpe._1.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(._1), rs(l0), p(l0) + FO(vpe._1.t) ') ↔ absloc(((h | l0) | false).map(._1), rs(l0), p(l0))), vpe._1.R?, vpe ∈ (h | l0) | false ⊦ |
vpe = (e, boolvar), ((h | e.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(((h | l0) | false).map(._1), rs(l0), p(l0))), e.R?, vpe ∈ (h | l0) | false ⊦
Used terms: e, boolvar
| vpe = (e, boolvar), ((h | e.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(((h | l0) | false).map(._1), rs(l0), p(l0))), e.R?, vpe ∈ (h | l0) | false ⊦ |
((h | e.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(((h | l0) | false).map(._1), rs(l0), p(l0))), e.R?, (e, boolvar) ∈ (h | l0) | false ⊦
| ((h | e.t) | false)|R = [], ¬(absloc(((h | l0) | false).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc(((h | l0) | false).map(._1), rs(l0), p(l0))), e.R?, (e, boolvar) ∈ (h | l0) | false ⊦ |
⊦ h | b = h.filter(λ vpe. vpe._2 ↔ b)
((h | e.t) | false)|R = [], ¬ ( absloc((h | l0).filter(λ vpe. vpe._2 ↔ false).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc((h | l0).filter(λ vpe. vpe._2 ↔ false).map(._1), rs(l0), p(l0))), e.R?, (e, boolvar) ∈ (h | l0).filter(λ vpe. vpe._2 ↔ false) ⊦
Used terms: h | l0, false
| ⊦ h | b = h.filter(λ vpe. vpe._2 ↔ b) |
| ((h | e.t) | false)|R = [], ¬ ( absloc((h | l0).filter(λ vpe. vpe._2 ↔ false).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc((h | l0).filter(λ vpe. vpe._2 ↔ false).map(._1), rs(l0), p(l0))), e.R?, (e, boolvar) ∈ (h | l0).filter(λ vpe. vpe._2 ↔ false) ⊦ |
((h | e.t) | false)|R = [], ¬(absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), e.R?, (e, false) ∈ h | l0 ⊦
Used simplifier rules: ⊦ a ∈ x.filter(p) ↔ a ∈ x ∧ p(a); (s)
| ((h | e.t) | false)|R = [], ¬(absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), e.R?, (e, false) ∈ h | l0 ⊦ |
e = R(t, l, v), ((h | e.t) | false)|R = [], ¬(absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), e.R?, (e, false) ∈ h | l0 ⊦
Used simplifier rules: RWevent freely generated by R, W;; ⊦ W(t, l, v).t = t; (s) ⊦ ¬ W(t, l, v).R?; (s)
| e = R(t, l, v), ((h | e.t) | false)|R = [], ¬(absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(e.t) ') ↔ absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), e.R?, (e, false) ∈ h | l0 ⊦ |
((h | t) | false)|R = [], ¬(absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l, v), false) ∈ h | l0 ⊦
Used simplifier rules: ⊦ R(t, l, v).R?; (s) ⊦ R(t, l, v).t = t; (s)
| ((h | t) | false)|R = [], ¬(absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc((h | l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l, v), false) ∈ h | l0 ⊦ |
⊦ h | l = h.filter(λ vpe. vpe._1.l = l)
((h | t) | false)|R = [], ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l, v), false) ∈ h.filter(λ vpe. vpe._1.l = l0) ⊦
Used terms: h, l0
| ⊦ h | l = h.filter(λ vpe. vpe._1.l = l) |
| ((h | t) | false)|R = [], ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l, v), false) ∈ h.filter(λ vpe. vpe._1.l = l0) ⊦ |
((h | t) | false)|R = [], ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h ⊦
Used simplifier rules: ⊦ R(t, l, v).l = l; (s) ⊦ a ∈ x.filter(p) ↔ a ∈ x ∧ p(a); (s)
| ((h | t) | false)|R = [], ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h ⊦ |
⊦ x = [] ↔ ¬(∃ a. a ∈ x)
¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ∀ a. ¬ a ∈ ((h | t) | false)|R ⊦
Used terms: ((h | t) | false)|R
| ⊦ x = [] ↔ ¬(∃ a. a ∈ x) |
| ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ∀ a. ¬ a ∈ ((h | t) | false)|R ⊦ |
¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ ((h | t) | false)|R ⊦
Used terms: (R(t, l0, v), false)
| ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ ((h | t) | false)|R ⊦ |
⊦ h |R = h.filter(λ vpe. vpe._1.R?)
¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ ((h | t) | false).filter(λ vpe. vpe._1.R?) ⊦
Used terms: (h | t) | false
| ⊦ h |R = h.filter(λ vpe. vpe._1.R?) |
| ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ ((h | t) | false).filter(λ vpe. vpe._1.R?) ⊦ |
¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ (h | t) | false ⊦
Used simplifier rules: ⊦ R(t, l, v).R?; (s) ⊦ a ∈ x.filter(p) ↔ a ∈ x ∧ p(a); (s)
| ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ (h | t) | false ⊦ |
⊦ h | b = h.filter(λ vpe. vpe._2 ↔ b)
¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ (h | t).filter(λ vpe. vpe._2 ↔ false) ⊦
Used terms: h | t, false
| ⊦ h | b = h.filter(λ vpe. vpe._2 ↔ b) |
| ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ (h | t).filter(λ vpe. vpe._2 ↔ false) ⊦ |
¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ h | t ⊦
Used simplifier rules: ⊦ a ∈ x.filter(p) ↔ a ∈ x ∧ p(a); (s)
| ¬ ( absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0) + FO(t) ') ↔ absloc(h.filter(λ vpe. vpe._1.l = l0).filter(λ vpe. ¬ vpe._2).map(._1), rs(l0), p(l0))), (R(t, l0, v), false) ∈ h, ¬ (R(t, l0, v), false) ∈ h | t ⊦ |
⊦ h | t = h.filter(λ vpe. vpe._1.t = t)
Used simplifier rules: ⊦ a ∈ x.filter(p) ↔ a ∈ x ∧ p(a); (s) ⊦ R(t, l, v).t = t; (s) Used terms: h, t
| ⊦ h | t = h.filter(λ vpe. vpe._1.t = t) |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.