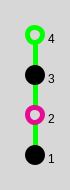
Proof Tree for dlls-null (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ dlls(null, r0, r1, x) = (emp ∧ ⌜r1 = null⌝ ∧ ⌜x = []⌝ ) |
dlls(null, r0, r1, x) ≠ (emp ∧ ⌜r1 = null⌝ ∧ ⌜x = []⌝ ) ⊦
| dlls(null, r0, r1, x) ≠ (emp ∧ ⌜r1 = null⌝ ∧ ⌜x = []⌝ ) ⊦ |
x = a + x0, dlls(null, r0, r1, x) ≠ (emp ∧ ⌜r1 = null⌝ ∧ ⌜x = []⌝ ) ⊦
Used simplifier rules: dlls-base: ⊦ dlls(r, r0, r1, []) = (emp ∧ ⌜r = r1⌝ ); List[A] freely generated by [], +; ⊦ ⌜true⌝ = true; (s) ⊦ (true ∧ hP) = hP; (s) ⊦ hP0 = hP1 → ((hP ∧ hP0) = (hP ∧ hP1) ↔ true); (ss) and-ass: ⊦ ((hP0 ∧ hP1) ∧ hP2) = (hP0 ∧ hP1 ∧ hP2); from specification map-sep and-com: ⊦ (hP0 ∧ hP1) = (hP1 ∧ hP0); from specification map-sep
| x = a + x0, dlls(null, r0, r1, x) ≠ (emp ∧ ⌜r1 = null⌝ ∧ ⌜x = []⌝ ) ⊦ |
_∃(λ r2. false) ≠ false ⊦
Used simplifier rules: dlls-rec: ⊦ dlls(r, r0, r1, a ' + x) = _∃(λ r2. r => mknode(r0, a, r2) * dlls(r2, r, r1, x)); and-ass: ⊦ ((hP0 ∧ hP1) ∧ hP2) = (hP0 ∧ hP1 ∧ hP2); from specification map-sep and-com: ⊦ (hP0 ∧ hP1) = (hP1 ∧ hP0); from specification map-sep ⊦ (false ∧ hP) = false; (s) ⊦ ⌜false⌝ = false; (s) a: ⊦ (x + y) + z = x + y + z; from specification list ⊦ a ' ≠ []; (s) ⊦ x + y = [] ↔ x = [] ∧ y = []; (s) ⊦ a + x = a ' + x; (s) sep-com: ⊦ hP0 * hP1 = hP1 * hP0; from specification map-sep sep-ass: ⊦ (hP0 * hP1) * hP2 = hP0 * hP1 * hP2; from specification map-sep ⊦ false * hP = false; (s) ⊦ null => o = ⌜false⌝ ; (s)
| _∃(λ r2. false) ≠ false ⊦ |
Used simplifier rules: ⊦ (_∃ bP)(h) ↔ (∃ b. bP(b)(h)); (s) ⊦ ¬ false(h); (s)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.