Proof Tree for rely-D14-D15 (View conclusion)
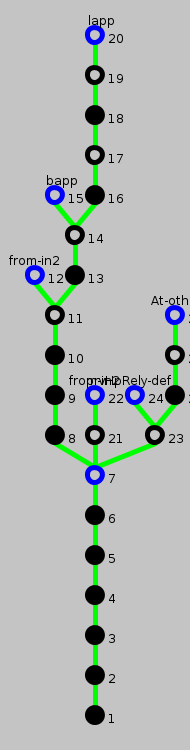
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ ls.tid ≠ tid0 ∧ ( (ls.lst ∈ gs.orl + gs.qrl ∧ gs.vrvHp[ls.rvref] = Empty ∧ ls.nxt = null) ∧ ( listp(gs.orl + gs.qrl, gs.vs, gs.ps, gs.owns) ∧ ¬ dups(gs.orl + gs.qrl) ∧ markedp(gs.orl, gs.ps) ∧ markedp(gs.orl, gs.vs) ∧ unmarkedp(gs.qrl, gs.ps) ∧ gs.orl ≠ [] ∧ gs.phead ∈ gs.orl ∧ rvownerok(gs.vretRefs, gs.vrvHp, gs.rvowns) ∧ allocrv(gs.vretRefs, gs.vrvHp) ∧ nonullRetRefs(gs.orl + gs.qrl, gs.vs, gs.vretRefs, gs.pretRefs) ∧ rvownerok(gs.pretRefs, gs.prvHp, gs.rvowns) ∧ allocrv(gs.pretRefs, gs.prvHp) ∧ dom gs.vrvHp = dom gs.prvHp ∧ ( gs.vs[gs.vhead].next ≠ null ∧ gs.vs[gs.vs[gs.vhead].next].deqID ≠ None → gs.rvowns(gs.vretRefs(gs.vs[gs.vs[gs.vhead].next].deqID.tid)) = Claimed(gs.vs[gs.vs[gs.vhead].next].deqID.tid, gs.vs[gs.vs[gs.vhead].next].val)) ∧ ( gs.orl.last = gs.vhead ∧ (gs.qrl ≠ [] → unmarkedp(gs.qrl.tail, gs.vs)) ∨ gs.orl.butlast ≠ [] ∧ gs.orl.butlast.last = gs.vhead ∧ gs.phead ≠ gs.orl.last ∧ unmarkedp(gs.qrl, gs.vs)) ∧ ( gs.vtail = (gs.orl + gs.qrl).last ∨ gs.qrl ≠ [] ∧ gs.vtail = (gs.orl + gs.qrl.butlast).last ∧ gs.vs[gs.qrl.last].deqID = None ∧ gs.vs[(gs.orl + gs.qrl).last].next = null)) ∧ (¬ ls.success ∧ gs.rvowns(gs.vretRefs(ls.tid)) = Pending(ls.tid)) ∧ (ls.first ∈ gs.orl ∧ gs.vhead ∈ gs.orl from ls.first) ∧ (gs.vretRefs(ls.tid) = ls.rvref ∧ gs.pretRefs(ls.tid) = ls.rvref ∧ ls.rvref ∈ gs.vrvHp ∧ ls.rvref ≠ null) ∧ nextnottid(ls.tid, gs.vhead, gs.vs) ∧ noid(ls.tid, gs.orl + gs.qrl, ls.first, gs.vs) ∧ noowns(ls.tid, gs.owns)) ∧ pre(gs, ls, D14, a) ∧ pcstepf(gs, ls, D14, a) = D15 → (∃ rl. gs.orl + gs.qrl + rl = gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl) ∧ (∃ rl0. gs.orl + rl0 = gstepf(gs, ls, D14, a).orl) ∧ gstepf(gs, ls, D14, a).vtail ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.vtail ∧ gstepf(gs, ls, D14, a).phead ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.phead ∧ gstepf(gs, ls, D14, a).vhead ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.vhead ∧ equalrl(gs.orl + gs.qrl, gs.vs, gs.ps, gstepf(gs, ls, D14, a).vs, gstepf(gs, ls, D14, a).ps) ∧ equalowns(gs.vs, gs.ps, gs.owns, tid0, gstepf(gs, ls, D14, a).vs, gstepf(gs, ls, D14, a).ps, gstepf(gs, ls, D14, a).owns) ∧ gs.vretRefs(tid0) = gstepf(gs, ls, D14, a).vretRefs(tid0) ∧ (gs.pretRefs(tid0) = gstepf(gs, ls, D14, a).pretRefs(tid0) ∨ gs.vretRefs(tid0) = gstepf(gs, ls, D14, a).pretRefs(tid0)) ∧ rvownsrely(tid0, gs.rvowns, gstepf(gs, ls, D14, a).rvowns, gs.vrvHp) ∧ rvrely(tid0, gs.rvowns, gs.vretRefs, gs.vrvHp, gstepf(gs, ls, D14, a).vretRefs, gstepf(gs, ls, D14, a).vrvHp) ∧ dom gs.vrvHp ⊆ dom gstepf(gs, ls, D14, a).vrvHp ∧ prvHpRely(gs.vrvHp, gs.prvHp, gstepf(gs, ls, D14, a).prvHp) ∧ noidRely(tid0, gs.orl + gs.qrl, gs.vs, gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl, gstepf(gs, ls, D14, a).vs) ∧ nextnottidRely(tid0, gs.vhead, gs.vs, gstepf(gs, ls, D14, a).vhead, gstepf(gs, ls, D14, a).vs) ∧ ownsRely(tid0, gs.owns, gstepf(gs, ls, D14, a).owns) |
ls.nxt = null, gs.pretRefs(ls.tid) = ls.rvref, gs.rvowns(gs.vretRefs(ls.tid)) = Pending(ls.tid), gs.vretRefs(ls.tid) = ls.rvref, gs.vrvHp[ls.rvref] = Empty, dom gs.vrvHp = dom gs.prvHp, pcstepf(gs, ls, D14, a) = D15, gs.orl ≠ [], ls.rvref ≠ null, ls.tid ≠ tid0, allocrv(gs.vretRefs, gs.vrvHp), allocrv(gs.pretRefs, gs.prvHp), listp(gs.orl + gs.qrl, gs.vs, gs.ps, gs.owns), markedp(gs.orl, gs.ps), markedp(gs.orl, gs.vs), nextnottid(ls.tid, gs.vhead, gs.vs), noid(ls.tid, gs.orl + gs.qrl, ls.first, gs.vs), nonullRetRefs(gs.orl + gs.qrl, gs.vs, gs.vretRefs, gs.pretRefs), noowns(ls.tid, gs.owns), pre(gs, ls, D14, a), rvownerok(gs.vretRefs, gs.vrvHp, gs.rvowns), rvownerok(gs.pretRefs, gs.prvHp, gs.rvowns), unmarkedp(gs.qrl, gs.ps), ls.lst ∈ gs.orl + gs.qrl, gs.phead ∈ gs.orl, ls.first ∈ gs.orl, gs.vhead ∈ gs.orl from ls.first, ls.rvref ∈ gs.vrvHp, ¬ ls.success, ¬ dups(gs.orl + gs.qrl), gs.vs[gs.vhead].next ≠ null ∧ gs.vs[gs.vs[gs.vhead].next].deqID ≠ None → gs.rvowns(gs.vretRefs(gs.vs[gs.vs[gs.vhead].next].deqID.tid)) = Claimed(gs.vs[gs.vs[gs.vhead].next].deqID.tid, gs.vs[gs.vs[gs.vhead].next].val), gs.orl.last = gs.vhead ∧ (gs.qrl ≠ [] → unmarkedp(gs.qrl.tail, gs.vs)) ∨ gs.orl.butlast ≠ [] ∧ gs.orl.butlast.last = gs.vhead ∧ gs.phead ≠ gs.orl.last ∧ unmarkedp(gs.qrl, gs.vs), gs.vtail = (gs.orl + gs.qrl).last ∨ gs.qrl ≠ [] ∧ gs.vtail = (gs.orl + gs.qrl.butlast).last ∧ gs.vs[gs.qrl.last].deqID = None ∧ gs.vs[(gs.orl + gs.qrl).last].next = null ⊦ (∃ rl. gs.orl + gs.qrl + rl = gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl) ∧ (∃ rl0. gs.orl + rl0 = gstepf(gs, ls, D14, a).orl) ∧ gstepf(gs, ls, D14, a).vtail ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.vtail ∧ gstepf(gs, ls, D14, a).phead ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.phead ∧ gstepf(gs, ls, D14, a).vhead ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.vhead ∧ equalrl(gs.orl + gs.qrl, gs.vs, gs.ps, gstepf(gs, ls, D14, a).vs, gstepf(gs, ls, D14, a).ps) ∧ equalowns(gs.vs, gs.ps, gs.owns, tid0, gstepf(gs, ls, D14, a).vs, gstepf(gs, ls, D14, a).ps, gstepf(gs, ls, D14, a).owns) ∧ gs.vretRefs(tid0) = gstepf(gs, ls, D14, a).vretRefs(tid0) ∧ (gs.pretRefs(tid0) = gstepf(gs, ls, D14, a).pretRefs(tid0) ∨ gs.vretRefs(tid0) = gstepf(gs, ls, D14, a).pretRefs(tid0)) ∧ rvownsrely(tid0, gs.rvowns, gstepf(gs, ls, D14, a).rvowns, gs.vrvHp) ∧ rvrely(tid0, gs.rvowns, gs.vretRefs, gs.vrvHp, gstepf(gs, ls, D14, a).vretRefs, gstepf(gs, ls, D14, a).vrvHp) ∧ dom gs.vrvHp ⊆ dom gstepf(gs, ls, D14, a).vrvHp ∧ prvHpRely(gs.vrvHp, gs.prvHp, gstepf(gs, ls, D14, a).prvHp) ∧ noidRely(tid0, gs.orl + gs.qrl, gs.vs, gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl, gstepf(gs, ls, D14, a).vs) ∧ nextnottidRely(tid0, gs.vhead, gs.vs, gstepf(gs, ls, D14, a).vhead, gstepf(gs, ls, D14, a).vs) ∧ ownsRely(tid0, gs.owns, gstepf(gs, ls, D14, a).owns)
| ls.nxt = null, gs.pretRefs(ls.tid) = ls.rvref, gs.rvowns(gs.vretRefs(ls.tid)) = Pending(ls.tid), gs.vretRefs(ls.tid) = ls.rvref, gs.vrvHp[ls.rvref] = Empty, dom gs.vrvHp = dom gs.prvHp, pcstepf(gs, ls, D14, a) = D15, gs.orl ≠ [], ls.rvref ≠ null, ls.tid ≠ tid0, allocrv(gs.vretRefs, gs.vrvHp), allocrv(gs.pretRefs, gs.prvHp), listp(gs.orl + gs.qrl, gs.vs, gs.ps, gs.owns), markedp(gs.orl, gs.ps), markedp(gs.orl, gs.vs), nextnottid(ls.tid, gs.vhead, gs.vs), noid(ls.tid, gs.orl + gs.qrl, ls.first, gs.vs), nonullRetRefs(gs.orl + gs.qrl, gs.vs, gs.vretRefs, gs.pretRefs), noowns(ls.tid, gs.owns), pre(gs, ls, D14, a), rvownerok(gs.vretRefs, gs.vrvHp, gs.rvowns), rvownerok(gs.pretRefs, gs.prvHp, gs.rvowns), unmarkedp(gs.qrl, gs.ps), ls.lst ∈ gs.orl + gs.qrl, gs.phead ∈ gs.orl, ls.first ∈ gs.orl, gs.vhead ∈ gs.orl from ls.first, ls.rvref ∈ gs.vrvHp, ¬ ls.success, ¬ dups(gs.orl + gs.qrl), gs.vs[gs.vhead].next ≠ null ∧ gs.vs[gs.vs[gs.vhead].next].deqID ≠ None → gs.rvowns(gs.vretRefs(gs.vs[gs.vs[gs.vhead].next].deqID.tid)) = Claimed(gs.vs[gs.vs[gs.vhead].next].deqID.tid, gs.vs[gs.vs[gs.vhead].next].val), gs.orl.last = gs.vhead ∧ (gs.qrl ≠ [] → unmarkedp(gs.qrl.tail, gs.vs)) ∨ gs.orl.butlast ≠ [] ∧ gs.orl.butlast.last = gs.vhead ∧ gs.phead ≠ gs.orl.last ∧ unmarkedp(gs.qrl, gs.vs), gs.vtail = (gs.orl + gs.qrl).last ∨ gs.qrl ≠ [] ∧ gs.vtail = (gs.orl + gs.qrl.butlast).last ∧ gs.vs[gs.qrl.last].deqID = None ∧ gs.vs[(gs.orl + gs.qrl).last].next = null ⊦ (∃ rl. gs.orl + gs.qrl + rl = gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl) ∧ (∃ rl0. gs.orl + rl0 = gstepf(gs, ls, D14, a).orl) ∧ gstepf(gs, ls, D14, a).vtail ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.vtail ∧ gstepf(gs, ls, D14, a).phead ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.phead ∧ gstepf(gs, ls, D14, a).vhead ∈ gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl from gs.vhead ∧ equalrl(gs.orl + gs.qrl, gs.vs, gs.ps, gstepf(gs, ls, D14, a).vs, gstepf(gs, ls, D14, a).ps) ∧ equalowns(gs.vs, gs.ps, gs.owns, tid0, gstepf(gs, ls, D14, a).vs, gstepf(gs, ls, D14, a).ps, gstepf(gs, ls, D14, a).owns) ∧ gs.vretRefs(tid0) = gstepf(gs, ls, D14, a).vretRefs(tid0) ∧ (gs.pretRefs(tid0) = gstepf(gs, ls, D14, a).pretRefs(tid0) ∨ gs.vretRefs(tid0) = gstepf(gs, ls, D14, a).pretRefs(tid0)) ∧ rvownsrely(tid0, gs.rvowns, gstepf(gs, ls, D14, a).rvowns, gs.vrvHp) ∧ rvrely(tid0, gs.rvowns, gs.vretRefs, gs.vrvHp, gstepf(gs, ls, D14, a).vretRefs, gstepf(gs, ls, D14, a).vrvHp) ∧ dom gs.vrvHp ⊆ dom gstepf(gs, ls, D14, a).vrvHp ∧ prvHpRely(gs.vrvHp, gs.prvHp, gstepf(gs, ls, D14, a).prvHp) ∧ noidRely(tid0, gs.orl + gs.qrl, gs.vs, gstepf(gs, ls, D14, a).orl + gstepf(gs, ls, D14, a).qrl, gstepf(gs, ls, D14, a).vs) ∧ nextnottidRely(tid0, gs.vhead, gs.vs, gstepf(gs, ls, D14, a).vhead, gstepf(gs, ls, D14, a).vs) ∧ ownsRely(tid0, gs.owns, gstepf(gs, ls, D14, a).owns) |
ls.nxt = null, gs.pretRefs(ls.tid) = ls.rvref, gs.rvowns(ls.rvref) = Pending(ls.tid), gs.vretRefs(ls.tid) = ls.rvref, gs.vrvHp[ls.rvref] = Empty, dom gs.vrvHp = dom gs.prvHp, gs.orl ≠ [], ls.rvref ≠ null, ls.tid ≠ tid0, allocrv(gs.vretRefs, gs.vrvHp), allocrv(gs.pretRefs, gs.prvHp), listp(gs.orl + gs.qrl, gs.vs, gs.ps, gs.owns), markedp(gs.orl, gs.ps), markedp(gs.orl, gs.vs), nextnottid(ls.tid, gs.vhead, gs.vs), noid(ls.tid, gs.orl + gs.qrl, ls.first, gs.vs), nonullRetRefs(gs.orl + gs.qrl, gs.vs, gs.vretRefs, gs.pretRefs), noowns(ls.tid, gs.owns), rvownerok(gs.vretRefs, gs.vrvHp, gs.rvowns), rvownerok(gs.pretRefs, gs.prvHp, gs.rvowns), unmarkedp(gs.qrl, gs.ps), gs.phead ∈ gs.ps, ls.first ∈ gs.ps, gs.phead ∈ gs.vs, ls.first ∈ gs.vs, gs.phead ∈ gs.orl, ls.first ∈ gs.orl, gs.vhead ∈ gs.orl from ls.first, ls.rvref ∈ gs.vrvHp, ¬ ls.success, ¬ dups(gs.qrl), ¬ dups(gs.orl), ¬ dups(gs.orl + gs.qrl), gs.vs[gs.vhead].next ≠ null ∧ gs.vs[gs.vs[gs.vhead].next].deqID ≠ None → gs.rvowns(gs.vretRefs(gs.vs[gs.vs[gs.vhead].next].deqID.tid)) = Claimed(gs.vs[gs.vs[gs.vhead].next].deqID.tid, gs.vs[gs.vs[gs.vhead].next].val), gs.vtail = (gs.orl + gs.qrl).last ∨ gs.qrl ≠ [] ∧ gs.vtail = (gs.orl + gs.qrl.butlast).last ∧ gs.vs[gs.qrl.last].deqID = None ∧ gs.vs[gs.qrl.last].next = null, ls.lst ∈ gs.orl ∨ ls.lst ∈ gs.qrl, gs.orl.last = gs.vhead ∧ (gs.qrl ≠ [] → unmarkedp(gs.qrl.tail, gs.vs)) ∨ gs.orl.butlast ≠ [] ∧ gs.orl.butlast.last = gs.vhead ∧ gs.phead ≠ gs.orl.last ∧ unmarkedp(gs.qrl, gs.vs) ⊦ gs.vtail ∈ gs.orl + gs.qrl from gs.vtail ∧ gs.vhead ∈ gs.orl + gs.qrl from gs.vhead ∧ prvHpRely(gs.vrvHp, gs.prvHp, gs.prvHp[ls.rvref, Empty])
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] a: ⊦ ¬ dups(x + y) → ¬ dups(x) ∧ ¬ dups(y); (forward) from specification list-dup[reflist] list-elem-in-app11: ⊦ listp(orl + qrl, vs, ps, owns) ∧ node ∈ orl → node ∈ vs; (forward) from specification DMSQ list-elem-in-app12: ⊦ listp(orl + qrl, vs, ps, owns) ∧ node ∈ orl → node ∈ ps; (forward) from specification DMSQ ⊦ ownsRely(tid, owns, owns); (s) ⊦ (gs.prvHp:= vrvHp0).owns = gs.owns; (s) ⊦ gstepf(gs, ls, D14, a) = gs.prvHp:= gs.prvHp[ls.rvref, gs.vrvHp[ls.rvref]]; (s) ⊦ nextnottidRely(tid, vhead, vs, vhead, vs); (s) ⊦ (gs.prvHp:= vrvHp0).vs = gs.vs; (s) ⊦ (gs.prvHp:= vrvHp0).vhead = gs.vhead; (s) ⊦ noidRely(tid, rl, vs, rl, vs); (s) ⊦ (gs.prvHp:= vrvHp0).qrl = gs.qrl; (s) ⊦ (gs.prvHp:= vrvHp0).orl = gs.orl; (s) ⊦ (gs.prvHp:= vrvHp0).prvHp = vrvHp0; (s) ⊦ # s = # s0 → (s ⊆ s0 ↔ s = s0); (s) ⊦ (gs.prvHp:= vrvHp0).vrvHp = gs.vrvHp; (s) ⊦ rvrely(tid, rvowns, vretRefs, vrvHp, vretRefs, vrvHp); (s) ⊦ (gs.prvHp:= vrvHp0).vretRefs = gs.vretRefs; (s) ⊦ rvownsrely(tid, rvowns, rvowns, vrvHp); (s) ⊦ (gs.prvHp:= vrvHp0).rvowns = gs.rvowns; (s) ⊦ (gs.prvHp:= vrvHp0).pretRefs = gs.pretRefs; (s) ⊦ equalowns(vs, ps, owns, tid, vs, ps, owns); (s) ⊦ (gs.prvHp:= vrvHp0).ps = gs.ps; (s) ⊦ equalrl(rl, vs, ps, vs, ps); (s) ⊦ r ∈ rl → r ∈ rl from r; (ss) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) ⊦ r ∈ orl → orl + qrl from r = (orl from r) + qrl; (s) ⊦ (gs.prvHp:= vrvHp0).phead = gs.phead; (s) ⊦ (gs.prvHp:= vrvHp0).vtail = gs.vtail; (s) ⊦ x = x + y ↔ y = []; (s) ⊦ # x = # z → (x + y = z + y0 ↔ x = z ∧ y = y0); (ws) ⊦ y ≠ [] → (x + y).last = y.last; (s) ⊦ pre(gs, ls, D14, a) ↔ a = doDeqEmpty(ls.tid); (s) ⊦ pcstepf(gs, ls, D14, a) = D15; (s)
| ls.nxt = null, gs.pretRefs(ls.tid) = ls.rvref, gs.rvowns(ls.rvref) = Pending(ls.tid), gs.vretRefs(ls.tid) = ls.rvref, gs.vrvHp[ls.rvref] = Empty, dom gs.vrvHp = dom gs.prvHp, gs.orl ≠ [], ls.rvref ≠ null, ls.tid ≠ tid0, allocrv(gs.vretRefs, gs.vrvHp), allocrv(gs.pretRefs, gs.prvHp), listp(gs.orl + gs.qrl, gs.vs, gs.ps, gs.owns), markedp(gs.orl, gs.ps), markedp(gs.orl, gs.vs), nextnottid(ls.tid, gs.vhead, gs.vs), noid(ls.tid, gs.orl + gs.qrl, ls.first, gs.vs), nonullRetRefs(gs.orl + gs.qrl, gs.vs, gs.vretRefs, gs.pretRefs), noowns(ls.tid, gs.owns), rvownerok(gs.vretRefs, gs.vrvHp, gs.rvowns), rvownerok(gs.pretRefs, gs.prvHp, gs.rvowns), unmarkedp(gs.qrl, gs.ps), gs.phead ∈ gs.ps, ls.first ∈ gs.ps, gs.phead ∈ gs.vs, ls.first ∈ gs.vs, gs.phead ∈ gs.orl, ls.first ∈ gs.orl, gs.vhead ∈ gs.orl from ls.first, ls.rvref ∈ gs.vrvHp, ¬ ls.success, ¬ dups(gs.qrl), ¬ dups(gs.orl), ¬ dups(gs.orl + gs.qrl), gs.vs[gs.vhead].next ≠ null ∧ gs.vs[gs.vs[gs.vhead].next].deqID ≠ None → gs.rvowns(gs.vretRefs(gs.vs[gs.vs[gs.vhead].next].deqID.tid)) = Claimed(gs.vs[gs.vs[gs.vhead].next].deqID.tid, gs.vs[gs.vs[gs.vhead].next].val), gs.vtail = (gs.orl + gs.qrl).last ∨ gs.qrl ≠ [] ∧ gs.vtail = (gs.orl + gs.qrl.butlast).last ∧ gs.vs[gs.qrl.last].deqID = None ∧ gs.vs[gs.qrl.last].next = null, ls.lst ∈ gs.orl ∨ ls.lst ∈ gs.qrl, gs.orl.last = gs.vhead ∧ (gs.qrl ≠ [] → unmarkedp(gs.qrl.tail, gs.vs)) ∨ gs.orl.butlast ≠ [] ∧ gs.orl.butlast.last = gs.vhead ∧ gs.phead ≠ gs.orl.last ∧ unmarkedp(gs.qrl, gs.vs) ⊦ gs.vtail ∈ gs.orl + gs.qrl from gs.vtail ∧ gs.vhead ∈ gs.orl + gs.qrl from gs.vhead ∧ prvHpRely(gs.vrvHp, gs.prvHp, gs.prvHp[ls.rvref, Empty]) |
ls.nxt = null, vrvHp[ls.rvref] = Empty, dom vrvHp = dom prvHp, gs = mkgs(ps, vs, phead, vhead, vtail, vretRefs, pretRefs, vrvHp, prvHp, qrl, orl, owns, rvowns), pretRefs(ls.tid) = ls.rvref, rvowns(ls.rvref) = Pending(ls.tid), vretRefs(ls.tid) = ls.rvref, ls.rvref ≠ null, ls.tid ≠ tid0, orl ≠ [], allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(ls.tid, vhead, vs), noid(ls.tid, orl + qrl, ls.first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(ls.tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), ls.rvref ∈ vrvHp, vhead ∈ orl from ls.first, ls.first ∈ orl, phead ∈ orl, ls.first ∈ vs, phead ∈ vs, ls.first ∈ ps, phead ∈ ps, ¬ ls.success, ¬ dups(qrl), ¬ dups(orl), ¬ dups(orl + qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), ls.lst ∈ orl ∨ ls.lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[ls.rvref, Empty])
Used simplifier rules: ⊦ ( ( ( ( ( ( ( ( ( ((ps = gs.ps ∧ vs = gs.vs) ∧ phead = gs.phead) ∧ vhead = gs.vhead) ∧ vtail = gs.vtail) ∧ vretRefs = gs.vretRefs) ∧ pretRefs = gs.pretRefs) ∧ vrvHp = gs.vrvHp) ∧ prvHp = gs.prvHp) ∧ qrl = gs.qrl) ∧ orl = gs.orl) ∧ owns = gs.owns) ∧ rvowns = gs.rvowns ↔ gs = mkgs (ps, vs, phead, vhead, vtail, vretRefs, pretRefs, vrvHp, prvHp, qrl, orl, owns, rvowns); (elim) Used terms: qrl, ps, phead, vrvHp, vretRefs, vhead, vtail, gs, owns, rvowns, orl, prvHp, pretRefs, vs
| ls.nxt = null, vrvHp[ls.rvref] = Empty, dom vrvHp = dom prvHp, gs = mkgs(ps, vs, phead, vhead, vtail, vretRefs, pretRefs, vrvHp, prvHp, qrl, orl, owns, rvowns), pretRefs(ls.tid) = ls.rvref, rvowns(ls.rvref) = Pending(ls.tid), vretRefs(ls.tid) = ls.rvref, ls.rvref ≠ null, ls.tid ≠ tid0, orl ≠ [], allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(ls.tid, vhead, vs), noid(ls.tid, orl + qrl, ls.first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(ls.tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), ls.rvref ∈ vrvHp, vhead ∈ orl from ls.first, ls.first ∈ orl, phead ∈ orl, ls.first ∈ vs, phead ∈ vs, ls.first ∈ ps, phead ∈ ps, ¬ ls.success, ¬ dups(qrl), ¬ dups(orl), ¬ dups(orl + qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), ls.lst ∈ orl ∨ ls.lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[ls.rvref, Empty]) |
ls.nxt = null, vrvHp[ls.rvref] = Empty, dom vrvHp = dom prvHp, pretRefs(ls.tid) = ls.rvref, rvowns(ls.rvref) = Pending(ls.tid), vretRefs(ls.tid) = ls.rvref, ls.rvref ≠ null, ls.tid ≠ tid0, orl ≠ [], allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(ls.tid, vhead, vs), noid(ls.tid, orl + qrl, ls.first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(ls.tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, ls.first ∈ orl, vhead ∈ orl from ls.first, ls.rvref ∈ vrvHp, phead ∈ vs, ls.first ∈ vs, phead ∈ ps, ls.first ∈ ps, ¬ ls.success, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null, ls.lst ∈ orl ∨ ls.lst ∈ qrl, orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[ls.rvref, Empty])
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] a: ⊦ ¬ dups(x + y) → ¬ dups(x) ∧ ¬ dups(y); (forward) from specification list-dup[reflist] list-elem-in-app11: ⊦ listp(orl + qrl, vs, ps, owns) ∧ node ∈ orl → node ∈ vs; (forward) from specification DMSQ list-elem-in-app12: ⊦ listp(orl + qrl, vs, ps, owns) ∧ node ∈ orl → node ∈ ps; (forward) from specification DMSQ
| ls.nxt = null, vrvHp[ls.rvref] = Empty, dom vrvHp = dom prvHp, pretRefs(ls.tid) = ls.rvref, rvowns(ls.rvref) = Pending(ls.tid), vretRefs(ls.tid) = ls.rvref, ls.rvref ≠ null, ls.tid ≠ tid0, orl ≠ [], allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(ls.tid, vhead, vs), noid(ls.tid, orl + qrl, ls.first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(ls.tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, ls.first ∈ orl, vhead ∈ orl from ls.first, ls.rvref ∈ vrvHp, phead ∈ vs, ls.first ∈ vs, phead ∈ ps, ls.first ∈ ps, ¬ ls.success, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null, ls.lst ∈ orl ∨ ls.lst ∈ qrl, orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[ls.rvref, Empty]) |
vrvHp[rvref] = Empty, dom vrvHp = dom prvHp, ls = mkls(tid, value, optval, node, nd, success, lst, nxt, rvref, optval0, first, othertid, addr), nxt = null, pretRefs(tid) = rvref, rvowns(rvref) = Pending(tid), ¬ success, vretRefs(tid) = rvref, orl ≠ [], rvref ≠ null, tid ≠ tid0, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, phead ∈ ps, first ∈ vs, phead ∈ vs, rvref ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[rvref, Empty])
Used simplifier rules: ⊦ ( ( ( ( ( ( ( ( ( ( (tid = ls.tid ∧ value = ls.value) ∧ optval = ls.optval) ∧ node = ls.node) ∧ nd = ls.nd) ∧ (success ↔ ls.success)) ∧ lst = ls.lst) ∧ nxt = ls.nxt) ∧ rvref = ls.rvref) ∧ optval0 = ls.optval0) ∧ first = ls.first) ∧ othertid = ls.othertid) ∧ addr = ls.addr ↔ ls = mkls (tid, value, optval, node, nd, success, lst, nxt, rvref, optval0, first, othertid, addr); (elim) Used terms: value, nxt, optval, node, nd, ls, addr, tid, lst, first, rvref, othertid, success, optval
| vrvHp[rvref] = Empty, dom vrvHp = dom prvHp, ls = mkls(tid, value, optval, node, nd, success, lst, nxt, rvref, optval0, first, othertid, addr), nxt = null, pretRefs(tid) = rvref, rvowns(rvref) = Pending(tid), ¬ success, vretRefs(tid) = rvref, orl ≠ [], rvref ≠ null, tid ≠ tid0, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, phead ∈ ps, first ∈ vs, phead ∈ vs, rvref ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[rvref, Empty]) |
vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null, lst ∈ orl ∨ lst ∈ qrl, orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[vretRefs(tid), Empty])
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] list-elem-in-app11: ⊦ listp(orl + qrl, vs, ps, owns) ∧ node ∈ orl → node ∈ vs; (forward) from specification DMSQ list-elem-in-app12: ⊦ listp(orl + qrl, vs, ps, owns) ∧ node ∈ orl → node ∈ ps; (forward) from specification DMSQ
| vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null, lst ∈ orl ∨ lst ∈ qrl, orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦ vtail ∈ orl + qrl from vtail ∧ vhead ∈ orl + qrl from vhead ∧ prvHpRely(vrvHp, prvHp, prvHp[vretRefs(tid), Empty]) |
vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ vtail ∈ orl + qrl from vtail, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦
vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ vhead ∈ orl + qrl from vhead, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦
vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ prvHpRely(vrvHp, prvHp, prvHp[vretRefs(tid), Empty]), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦
| vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ vtail ∈ orl + qrl from vtail, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ |
vs[qrl.last].deqID = None, vs[qrl.last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + qrl.butlast).last ≠ qrl.last, orl ≠ [], qrl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ (orl + qrl.butlast).last ∈ orl + qrl from (orl + qrl.butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(qrl.tail, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] ⊦ y ≠ [] → (x + y).last = y.last; (s) ⊦ x + y = [] ↔ x = [] ∧ y = []; (as) ⊦ x.last ∈ x ↔ x ≠ []; (s) ⊦ rl.last ∈ rl from r ↔ r ∈ rl; (s)
| vs[qrl.last].deqID = None, vs[qrl.last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + qrl.butlast).last ≠ qrl.last, orl ≠ [], qrl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ (orl + qrl.butlast).last ∈ orl + qrl from (orl + qrl.butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(qrl.tail, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl ⊦ |
vs[qrl.last].deqID = None, vs[qrl.last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), qrl = lst0 + orl0, rvowns(vretRefs(tid)) = Pending(tid), (orl + qrl.butlast).last ≠ qrl.last, orl ≠ [], qrl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ (orl + qrl.butlast).last ∈ orl + qrl from (orl + qrl.butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst ∈ qrl, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦
Used simplifier rules: ⊦ x ≠ [] → (head = x.head ∧ tail = x.tail ↔ x = head + tail); (elim) Used terms: qrl, head, tail
| vs[qrl.last].deqID = None, vs[qrl.last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), qrl = lst0 + orl0, rvowns(vretRefs(tid)) = Pending(tid), (orl + qrl.butlast).last ≠ qrl.last, orl ≠ [], qrl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ (orl + qrl.butlast).last ∈ orl + qrl from (orl + qrl.butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst ∈ qrl, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦ |
vs[(lst0 ' + orl0).last].deqID = None, ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + (lst0 ' + orl0).butlast).last ≠ (lst0 ' + orl0).last, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl0, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl + lst0 ' + orl0 from (orl + (lst0 ' + orl0).butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0 ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] a: ⊦ ¬ dups(x + y) → ¬ dups(x) ∧ ¬ dups(y); (forward) from specification list-dup[reflist] ⊦ a ∈ b ' + x ↔ a = b ∨ a ∈ x; (s) ⊦ a + x = a ' + x; (s) ⊦ unmarkedp(r ', vs) ↔ vs[r].deqID = None; (s) ⊦ unmarkedp(rl + rl0, vs) ↔ unmarkedp(rl, vs) ∧ unmarkedp(rl0, vs); (s) ⊦ dups(a ' + x) ↔ a ∈ x ∨ dups(x); (s) ⊦ dups(x + a ' + y) ↔ a ∈ x ∨ a ∈ y ∨ dups(x + y); (ws) ⊦ a ' + x ≠ []; (s)
| vs[(lst0 ' + orl0).last].deqID = None, ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + (lst0 ' + orl0).butlast).last ≠ (lst0 ' + orl0).last, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl0, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl + lst0 ' + orl0 from (orl + (lst0 ' + orl0).butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0 ⊦ |
⊦ r ∈ rl → r ∈ rl from r
ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + (lst0 ' + orl0).butlast).last ≠ (lst0 ' + orl0).last, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(orl0, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl + lst0 ' + orl0, ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl + lst0 ' + orl0 from (orl + (lst0 ' + orl0).butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs) ⊦
Used terms: (orl + (lst0 ' + orl0).butlast).last, orl + lst0 ' + orl0
| ⊦ r ∈ rl → r ∈ rl from r |
| ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + (lst0 ' + orl0).butlast).last ≠ (lst0 ' + orl0).last, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(orl0, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl + lst0 ' + orl0, ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl + lst0 ' + orl0 from (orl + (lst0 ' + orl0).butlast).last, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs) ⊦ |
vs[(lst0 ' + orl0).last].deqID = None, ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + (lst0 ' + orl0).butlast).last ≠ (lst0 ' + orl0).last, (orl + (lst0 ' + orl0).butlast).last ≠ lst0, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl0, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0 ⊦
Used simplifier rules: ⊦ ¬ a ∈ []; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] ⊦ ¬ r ∈ rl → rl from r = []; (s) ⊦ r0 ≠ r → r0 ' + rl from r = rl from r; (s) ⊦ ¬ r ∈ orl → orl + qrl from r = qrl from r; (s) ⊦ a ∈ b ' + x ↔ a = b ∨ a ∈ x; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s)
| vs[(lst0 ' + orl0).last].deqID = None, ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + (lst0 ' + orl0).butlast).last ≠ (lst0 ' + orl0).last, (orl + (lst0 ' + orl0).butlast).last ≠ lst0, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl0, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl, ¬ (orl + (lst0 ' + orl0).butlast).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0 ⊦ |
⊦ y ≠ [] → (x + y).butlast = x + y.butlast
ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + lst0 ' + orl0.butlast).last ≠ (lst0 ' + orl0).last, (orl + lst0 ' + orl0.butlast).last ≠ lst0, orl ≠ [], orl0 ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(orl0, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + lst0 ' + orl0.butlast).last ∈ orl, ¬ (orl + lst0 ' + orl0.butlast).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs) ⊦
Used simplifier rules: ⊦ a '.last = a; (s) ⊦ unmarkedp([], vs); (s) ⊦ ¬ dups([]); (s) ⊦ ¬ a ∈ []; (s) ⊦ a '.butlast = []; (s) ⊦ x + [] = x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] ⊦ x.last ∈ x ↔ x ≠ []; (s) Used terms: lst0 ', orl0
| ⊦ y ≠ [] → (x + y).butlast = x + y.butlast |
| ps[lst0].deqID = None, vs[(lst0 ' + orl0).last].deqID = None, vs[(lst0 ' + orl0).last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (orl + lst0 ' + orl0.butlast).last ≠ (lst0 ' + orl0).last, (orl + lst0 ' + orl0.butlast).last ≠ lst0, orl ≠ [], orl0 ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(orl0, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (orl + lst0 ' + orl0.butlast).last ∈ orl, ¬ (orl + lst0 ' + orl0.butlast).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs) ⊦ |
ps[lst0].deqID = None, vs[orl0.last].deqID = None, vs[orl0.last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (lst0 ' + orl0.butlast).last ≠ orl0.last, (lst0 ' + orl0.butlast).last ≠ lst0, orl ≠ [], orl0 ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl0, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (lst0 ' + orl0.butlast).last ∈ orl, ¬ (lst0 ' + orl0.butlast).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0 ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] ⊦ (x + a ' + y).last = (a ' + y).last; (s) ⊦ x ≠ [] → (a ' + x).last = x.last; (s)
| ps[lst0].deqID = None, vs[orl0.last].deqID = None, vs[orl0.last].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (lst0 ' + orl0.butlast).last ≠ orl0.last, (lst0 ' + orl0.butlast).last ≠ lst0, orl ≠ [], orl0 ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl0, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (lst0 ' + orl0.butlast).last ∈ orl, ¬ (lst0 ' + orl0.butlast).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0 ⊦ |
vs[phead0].deqID = None, ps[lst0].deqID = None, vs[phead0].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, orl0 = orl1 + phead0 ', pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (lst0 ' + orl1).last ≠ phead0, (lst0 ' + orl1).last ≠ lst0, orl ≠ [], orl0 ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(orl0, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (lst0 ' + orl1).last ∈ orl, ¬ (lst0 ' + orl1).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs) ⊦
Used simplifier rules: x ≠ [] ⊦ a = x.last ∧ y = x.butlast ↔ x = y + a '; (elim) Used terms: orl0, phead0, y
| vs[phead0].deqID = None, ps[lst0].deqID = None, vs[phead0].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, orl0 = orl1 + phead0 ', pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (lst0 ' + orl1).last ≠ phead0, (lst0 ' + orl1).last ≠ lst0, orl ≠ [], orl0 ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + lst0 ' + orl0, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl0, first, vs), nonullRetRefs(orl + lst0 ' + orl0, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(orl0, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + orl0), ¬ dups(orl), ¬ dups(orl0), ¬ lst0 ∈ orl, ¬ lst0 ∈ orl0, ¬ (lst0 ' + orl1).last ∈ orl, ¬ (lst0 ' + orl1).last ∈ orl0, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl0, orl.last = vhead ∧ unmarkedp(orl0, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl0, vs) ⊦ |
ps[lst0].deqID = None, vs[phead0].deqID = None, ps[phead0].deqID = None, vs[phead0].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (lst0 ' + orl1).last ≠ phead0, (lst0 ' + orl1).last ≠ lst0, lst0 ≠ phead0, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl1 + phead0 ', vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl1 + phead0 ', first, vs), nonullRetRefs(orl + lst0 ' + orl1 + phead0 ', vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl1, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl1), ¬ dups(orl), ¬ dups(orl1), ¬ phead0 ∈ orl, ¬ phead0 ∈ orl1, ¬ lst0 ∈ orl, ¬ lst0 ∈ orl1, ¬ (lst0 ' + orl1).last ∈ orl, ¬ (lst0 ' + orl1).last ∈ orl1, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl1, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl1, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl1 ∨ lst = phead0 ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] a: ⊦ ¬ dups(x + y) → ¬ dups(x) ∧ ¬ dups(y); (forward) from specification list-dup[reflist] ⊦ a ∈ b ' ↔ a = b; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) ⊦ unmarkedp(r ', vs) ↔ vs[r].deqID = None; (s) ⊦ unmarkedp(rl + rl0, vs) ↔ unmarkedp(rl, vs) ∧ unmarkedp(rl0, vs); (s) ⊦ ¬ b ∈ x → (dups(x + b ') ↔ dups(x)); (s) ⊦ dups(x + a ') ↔ a ∈ x ∨ dups(x); (ws) ⊦ x + a ' ≠ []; (s)
| ps[lst0].deqID = None, vs[phead0].deqID = None, ps[phead0].deqID = None, vs[phead0].next = null, vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), (lst0 ' + orl1).last ≠ phead0, (lst0 ' + orl1).last ≠ lst0, lst0 ≠ phead0, orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + lst0 ' + orl1 + phead0 ', vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + lst0 ' + orl1 + phead0 ', first, vs), nonullRetRefs(orl + lst0 ' + orl1 + phead0 ', vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(orl1, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + orl1), ¬ dups(orl), ¬ dups(orl1), ¬ phead0 ∈ orl, ¬ phead0 ∈ orl1, ¬ lst0 ∈ orl, ¬ lst0 ∈ orl1, ¬ (lst0 ' + orl1).last ∈ orl, ¬ (lst0 ' + orl1).last ∈ orl1, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ unmarkedp(orl1, vs) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ vs[lst0].deqID = None ∧ unmarkedp(orl1, vs), lst ∈ orl ∨ lst = lst0 ∨ lst ∈ orl1 ∨ lst = phead0 ⊦ |
⊦ y ≠ [] → (x + y).last = y.last
Used simplifier rules: ⊦ x.last ∈ x ↔ x ≠ []; (s) ⊦ x + [] = x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] ⊦ a '.last = a; (s) Used terms: lst0 ', orl1
| ⊦ y ≠ [] → (x + y).last = y.last |
| vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ vhead ∈ orl + qrl from vhead, vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ |
⊦ r ∈ rl → r ∈ rl from r
Used simplifier rules: ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) ⊦ r ∈ rl from r0 → r ∈ rl; (ss) a: ⊦ (x + y) + z = x + y + z; from specification list[reflist] Used terms: vhead, orl + qrl
| ⊦ r ∈ rl → r ∈ rl from r |
| vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), ¬ prvHpRely(vrvHp, prvHp, prvHp[vretRefs(tid), Empty]), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ |
⊦ prvHpRely(vrvHp, prvHp, prvHp0) ↔ (∀ rvref. rvref ∈ prvHp → prvHp0[rvref] = prvHp[rvref] ∨ prvHp0[rvref] = vrvHp[rvref])
vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), ∃ rvref. ¬(rvref ∈ prvHp → prvHp[vretRefs(tid), Empty][rvref] = prvHp[rvref] ∨ prvHp[vretRefs(tid), Empty][rvref] = vrvHp[rvref]), vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null, lst ∈ orl ∨ lst ∈ qrl, orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦
Used terms: vrvHp, prvHp, prvHp[vretRefs(tid), Empty]
| ⊦ prvHpRely(vrvHp, prvHp, prvHp0) ↔ (∀ rvref. rvref ∈ prvHp → prvHp0[rvref] = prvHp[rvref] ∨ prvHp0[rvref] = vrvHp[rvref]) |
| vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(vretRefs, vrvHp), allocrv(pretRefs, prvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, ps), markedp(orl, vs), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(vretRefs, vrvHp, rvowns), rvownerok(pretRefs, prvHp, rvowns), unmarkedp(qrl, ps), phead ∈ orl, first ∈ orl, vhead ∈ orl from first, vretRefs(tid) ∈ vrvHp, phead ∈ vs, phead ∈ ps, first ∈ vs, first ∈ ps, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), ∃ rvref. ¬(rvref ∈ prvHp → prvHp[vretRefs(tid), Empty][rvref] = prvHp[rvref] ∨ prvHp[vretRefs(tid), Empty][rvref] = vrvHp[rvref]), vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null, lst ∈ orl ∨ lst ∈ qrl, orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs) ⊦ |
vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), prvHp[vretRefs(tid), Empty][rvref] ≠ prvHp[rvref], prvHp[vretRefs(tid), Empty][rvref] ≠ vrvHp[rvref], orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), rvref ∈ prvHp, first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦
| vrvHp[vretRefs(tid)] = Empty, dom vrvHp = dom prvHp, pretRefs(tid) = vretRefs(tid), rvowns(vretRefs(tid)) = Pending(tid), prvHp[vretRefs(tid), Empty][rvref] ≠ prvHp[rvref], prvHp[vretRefs(tid), Empty][rvref] ≠ vrvHp[rvref], orl ≠ [], tid ≠ tid0, vretRefs(tid) ≠ null, allocrv(pretRefs, prvHp), allocrv(vretRefs, vrvHp), listp(orl + qrl, vs, ps, owns), markedp(orl, vs), markedp(orl, ps), nextnottid(tid, vhead, vs), noid(tid, orl + qrl, first, vs), nonullRetRefs(orl + qrl, vs, vretRefs, pretRefs), noowns(tid, owns), rvownerok(pretRefs, prvHp, rvowns), rvownerok(vretRefs, vrvHp, rvowns), unmarkedp(qrl, ps), rvref ∈ prvHp, first ∈ ps, first ∈ vs, phead ∈ ps, phead ∈ vs, vretRefs(tid) ∈ vrvHp, vhead ∈ orl from first, first ∈ orl, phead ∈ orl, ¬ dups(orl + qrl), ¬ dups(orl), ¬ dups(qrl), vs[vhead].next ≠ null ∧ vs[vs[vhead].next].deqID ≠ None → rvowns(vretRefs(vs[vs[vhead].next].deqID.tid)) = Claimed(vs[vs[vhead].next].deqID.tid, vs[vs[vhead].next].val), orl.last = vhead ∧ (qrl ≠ [] → unmarkedp(qrl.tail, vs)) ∨ orl.butlast ≠ [] ∧ orl.butlast.last = vhead ∧ phead ≠ orl.last ∧ unmarkedp(qrl, vs), lst ∈ orl ∨ lst ∈ qrl, vtail = (orl + qrl).last ∨ qrl ≠ [] ∧ vtail = (orl + qrl.butlast).last ∧ vs[qrl.last].deqID = None ∧ vs[qrl.last].next = null ⊦ |
⊦ a ≠ b → st[b, d][a] = st[a]
Used simplifier rules: ⊦ a = b → st[b, d][a] = d; (s) Used terms: prvHp, vretRefs(tid), Empty, rvref
| ⊦ a ≠ b → st[b, d][a] = st[a] |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.