[Imprint][Data Privacy Statement][E-Mail]
View long theorem info.
View the proof.
Back to main index.
View the specification.
View theorem base summary,
View theorem base listing,
the used properties by spec,
the dependency list,
the symbol table,
Proof step 1 from proof refine-implies-bwhist (conclusion)
(back to tree)
| C_≤*T_A(cioaut, aioaut) ⊦ ≤BI(hist(cioaut), hist(aioaut)) |
System applied rule normalize
And obtained the following new goals
Rule argument
Additional information
Proof step 2 from proof refine-implies-bwhist (previous step)
(back to tree)
| C_≤*T_A(cioaut, aioaut), ¬ ≤BI(hist(cioaut), hist(aioaut)) ⊦ |
User applied rule apply lemma
And obtained the following new goals
- Proof step 3:
C_≤*T_A(cioaut, aioaut)
⊦ bwsim
(hist(cioaut), hist(aioaut), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → aioaut.start(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. aexec*(aioaut)(aσ, α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
- Proof step 4:
C_≤*T_A(cioaut, aioaut), ¬ ≤BI(hist(cioaut), hist(aioaut)),
bwsim
(hist(cioaut), hist(aioaut), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → aioaut.start(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. aexec*(aioaut)(aσ, α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
spec: <toplevel>, name:refine-implies-bwhist-aux,
seq:C_≤*T_A(cioaut, aioaut)
⊦ bwsim
(hist(cioaut), hist(aioaut),
λ αcs, αas.
aactstream(αas) = cactstream(αcs)
∧ (cactstream(αcs) = [] → aioaut.start(aendstate(αas))),
λ αcs.
∃ cσ, α.
cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas.
∃ aσ, α.
aexec*(aioaut)(aσ, α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^),
subst:[cioaut, aioaut] → [cioaut, aioaut]
Additional information
Used terms: cioaut, aioaut
Proof step 3 from proof refine-implies-bwhist (previous step)
(back to tree)
| C_≤*T_A(cioaut, aioaut)
⊦ bwsim
(hist(cioaut), hist(aioaut), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → aioaut.start(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. aexec*(aioaut)(aσ, α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^) |
Proof step 4 from proof refine-implies-bwhist (previous step)
(back to tree)
| C_≤*T_A(cioaut, aioaut), ¬ ≤BI(hist(cioaut), hist(aioaut)),
bwsim
(hist(cioaut), hist(aioaut), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → aioaut.start(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. aexec*(aioaut)(aσ, α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
Heuristic elimination applied rule apply elim lemma
And obtained the following new goals
- Proof step 5:
aioaut = AIOAut(astartf, astepf), C_≤*T_A(cioaut, aioaut), ¬ ≤BI(hist(cioaut), hist(aioaut)),
bwsim
(hist(cioaut), hist(aioaut), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. aexec*(aioaut)(aσ, α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
spec: IO-Aut-data[histA], name:elim,
seq: ⊦ start = ioaut.start ∧ step = ioaut.step ↔ ioaut = AIOAut(start, step),
subst:[ioaut, start, step] → [aioaut, astartf, astepf]
Additional information
Used simplifier rules:
⊦ start = ioaut.start ∧ step = ioaut.step ↔ ioaut = AIOAut(start, step); (elim)
Used terms: aioaut, astartf, astepf
Proof step 5 from proof refine-implies-bwhist (previous step)
(back to tree)
| aioaut = AIOAut(astartf, astepf), C_≤*T_A(cioaut, aioaut), ¬ ≤BI(hist(cioaut), hist(aioaut)),
bwsim
(hist(cioaut), hist(aioaut), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. aexec*(aioaut)(aσ, α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 6:
C_≤*T_A(cioaut, AIOAut(astartf, astepf)), ¬ ≤BI(hist(cioaut), hist(AIOAut(astartf, astepf))),
bwsim
(hist(cioaut), hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
Additional information
Used simplifier rules:
⊦ aexec(AIOAut(startf, stepf))(σ, β) ↔ afrag(AIOAut(startf, stepf))(σ, β) ∧ startf(σ[0]); (s)
⊦ aexec*(AIOAut(startf, stepf))(σ, β) ↔ aexec(AIOAut(startf, stepf))(σ, β) ∧ finp(β); (s)
Proof step 6 from proof refine-implies-bwhist (previous step)
(back to tree)
| C_≤*T_A(cioaut, AIOAut(astartf, astepf)), ¬ ≤BI(hist(cioaut), hist(AIOAut(astartf, astepf))),
bwsim
(hist(cioaut), hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
User applied rule weakening
And obtained the following new goals
- Proof step 7:
¬ ≤BI(hist(cioaut), hist(AIOAut(astartf, astepf))),
bwsim
(hist(cioaut), hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
poslist: left 1
Additional information
Proof step 7 from proof refine-implies-bwhist (previous step)
(back to tree)
| ¬ ≤BI(hist(cioaut), hist(AIOAut(astartf, astepf))),
bwsim
(hist(cioaut), hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
User applied rule constructor cut
And obtained the following new goals
- Proof step 8:
cioaut = CIOAut(cstartf0, cstepf0), ¬ ≤BI(hist(cioaut), hist(AIOAut(astartf, astepf))),
bwsim
(hist(cioaut), hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
var: cioaut
Additional information
Used simplifier rules:
CIOAutomaton freely generated by CIOAut;;
Proof step 8 from proof refine-implies-bwhist (previous step)
(back to tree)
| cioaut = CIOAut(cstartf0, cstepf0), ¬ ≤BI(hist(cioaut), hist(AIOAut(astartf, astepf))),
bwsim
(hist(cioaut), hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cexec*(cioaut)(cσ, α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 9:
¬ ≤BI(hist(CIOAut(cstartf0, cstepf0)), hist(AIOAut(astartf, astepf))),
bwsim
(hist(CIOAut(cstartf0, cstepf0)), hist(AIOAut(astartf, astepf)),
λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
Additional information
Used simplifier rules:
⊦ cexec(CIOAut(startf, stepf))(σ, β) ↔ cfrag(CIOAut(startf, stepf))(σ, β) ∧ startf(σ[0]); (s)
⊦ cexec*(CIOAut(startf, stepf))(σ, β) ↔ cexec(CIOAut(startf, stepf))(σ, β) ∧ finp(β); (s)
Proof step 9 from proof refine-implies-bwhist (previous step)
(back to tree)
| ¬ ≤BI(hist(CIOAut(cstartf0, cstepf0)), hist(AIOAut(astartf, astepf))),
bwsim
(hist(CIOAut(cstartf0, cstepf0)), hist(AIOAut(astartf, astepf)),
λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 10:
⊦ hist(CIOAut(startf, stepf))
= CHIOAut
(λ αs. cactstream(αs) = [] ∧ startf(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(startf, stepf))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^)
- Proof step 11:
¬
≤BI
(CHIOAut
(λ αs. cactstream(αs) = [] ∧ cstartf0(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf))),
bwsim
(CHIOAut
(λ αs. cactstream(αs) = [] ∧ cstartf0(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
spec: histAut[histC], name:histAut-def,
seq:⊦ hist(CIOAut(startf, stepf))
= CHIOAut
(λ αs. cactstream(αs) = [] ∧ startf(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs))
∧ cmove(CIOAut(startf, stepf))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0))
∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^),
subst:[stepf, startf] → [cstepf0, cstartf0], <all paths>
Additional information
Used terms: cstepf0, cstartf0
Proof step 10 from proof refine-implies-bwhist (previous step)
(back to tree)
| ⊦ hist(CIOAut(startf, stepf))
= CHIOAut
(λ αs. cactstream(αs) = [] ∧ startf(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(startf, stepf))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^) |
A spec-lemma
Proof step 11 from proof refine-implies-bwhist (previous step)
(back to tree)
| ¬
≤BI
(CHIOAut
(λ αs. cactstream(αs) = [] ∧ cstartf0(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf))),
bwsim
(CHIOAut
(λ αs. cactstream(αs) = [] ∧ cstartf0(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 12:
⊦ ≤BI(cioaut, aioaut) ↔ (∃ t, aINV, cINV. bwsim(cioaut, aioaut, t, cINV, aINV))
- Proof step 13:
∀ t, aINV, cINV.
¬
bwsim
(CHIOAut
(λ αcs. cactstream(αcs) = [] ∧ cstartf0(cendstate(αcs)),
λ αcs, a, αcs0.
finp(cactstream(αcs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αcs), ⌜a '⌝ ^, cendstate(αcs0))
∧ cactstream(αcs0) = cactstream(αcs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf)), t, cINV, aINV),
bwsim
(CHIOAut
(λ αs. cactstream(αs) = [] ∧ cstartf0(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦
Rule argument
spec: IObackward-INV[IOrefine-CHIO-AHIO], name:backwardsiminv-def,
seq: ⊦ ≤BI(cioaut, aioaut) ↔ (∃ t, aINV, cINV. bwsim(cioaut, aioaut, t, cINV, aINV)),
subst:[aioaut, cioaut]
→ [hist(AIOAut(astartf, astepf)),
CHIOAut
(λ αcs. cactstream(αcs) = [] ∧ cstartf0(cendstate(αcs)),
λ αcs, a, αcs0.
finp(cactstream(αcs))
∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αcs), ⌜a '⌝ ^, cendstate(αcs0))
∧ cactstream(αcs0) = cactstream(αcs) + ⌜a '⌝ ^)],
<all paths>
Additional information
Used terms: hist(AIOAut(astartf, astepf)), CHIOAut
(λ αcs. cactstream(αcs) = [] ∧ cstartf0(cendstate(αcs)),
λ αcs, a, αcs0.
finp(cactstream(αcs))
∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αcs), ⌜a '⌝ ^, cendstate(αcs0))
∧ cactstream(αcs0) = cactstream(αcs) + ⌜a '⌝ ^)
Proof step 12 from proof refine-implies-bwhist (previous step)
(back to tree)
| ⊦ ≤BI(cioaut, aioaut) ↔ (∃ t, aINV, cINV. bwsim(cioaut, aioaut, t, cINV, aINV)) |
A spec-lemma
Proof step 13 from proof refine-implies-bwhist (previous step)
(back to tree)
| ∀ t, aINV, cINV.
¬
bwsim
(CHIOAut
(λ αcs. cactstream(αcs) = [] ∧ cstartf0(cendstate(αcs)),
λ αcs, a, αcs0.
finp(cactstream(αcs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αcs), ⌜a '⌝ ^, cendstate(αcs0))
∧ cactstream(αcs0) = cactstream(αcs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf)), t, cINV, aINV),
bwsim
(CHIOAut
(λ αs. cactstream(αs) = [] ∧ cstartf0(cendstate(αs)),
λ αs, a, αs0.
finp(cactstream(αs)) ∧ cmove(CIOAut(cstartf0, cstepf0))(cendstate(αs), ⌜a '⌝ ^, cendstate(αs0)) ∧ cactstream(αs0) = cactstream(αs) + ⌜a '⌝ ^),
hist(AIOAut(astartf, astepf)), λ αcs, αas. aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αcs. ∃ cσ, α. cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α) ∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^,
λ αas. ∃ aσ, α. afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α) ∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^)
⊦ |
Heuristic quantifier closing applied rule all left
And closed the goal!
Rule argument
pos: left 1
terms: λ αcs, αas.
aactstream(αas) = cactstream(αcs)
∧ (cactstream(αcs) = [] → astartf(aendstate(αas))),
λ αas.
∃ aσ, α.
afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α)
∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^,
λ αcs.
∃ cσ, α.
cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α)
∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^
Additional information
Used terms: λ αcs, αas.
aactstream(αas) = cactstream(αcs) ∧ (cactstream(αcs) = [] → astartf(aendstate(αas))), λ αas.
∃ aσ, α.
afrag(AIOAut(astartf, astepf))(aσ, α) ∧ astartf(aσ[0]) ∧ finp(α)
∧ aσ.l.last = aendstate(αas) ∧ aactstream(αas) = α ^, λ αcs.
∃ cσ, α.
cfrag(CIOAut(cstartf0, cstepf0))(cσ, α) ∧ cstartf0(cσ[0]) ∧ finp(α)
∧ cσ.l.last = cendstate(αcs) ∧ cactstream(αcs) = α ^
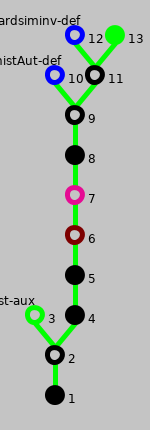
Proof Tree for refine-implies-bwhist
(View conclusion)
The following image shows the proof tree of sequent calculus. The
proved goal is at the bottom. You can click on the nodes to view
additional rules. See here for details on colors in a proof
tree.