[Imprint][Data Privacy Statement][E-Mail]
View long theorem info.
View the proof.
Back to main index.
View the specification.
View theorem base summary,
View theorem base listing,
the used properties by spec,
the dependency list,
the symbol table,
Proof step 1 from proof emptymove-splitfirst (conclusion)
(back to tree)
| move(IOAut(startf, stepf))(s, [], s2), s ≠ s2 ⊦ ∃ s1. stepf(s, τ, s1) ∧ move(IOAut(startf, stepf))(s1, [], s2) |
System applied rule normalize
And obtained the following new goals
- Proof step 2:
s ≠ s2, move(IOAut(startf, stepf))(s, [], s2) ⊦ ∃ s1. stepf(s, τ, s1) ∧ move(IOAut(startf, stepf))(s1, [], s2)
Rule argument
Additional information
| s ≠ s2, move(IOAut(startf, stepf))(s, [], s2) ⊦ ∃ s1. stepf(s, τ, s1) ∧ move(IOAut(startf, stepf))(s1, [], s2) |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 3:
⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β)
- Proof step 4:
s ≠ s2, ∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s = sl[0] ∧ s2 = sl.last ∧ α ^ = []
⊦ ∃ s1. stepf(s, τ, s1) ∧ move(IOAut(startf, stepf))(s1, [], s2)
Rule argument
spec: <toplevel>, name:move,
seq:⊦ move(IOAut(startf, stepf))(s1, β, s2)
↔ (∃ α, sl.
frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β),
subst:[stepf, startf, s2, β, s1] → [stepf, startf, s2, [], s], <all paths>
Additional information
Used terms: s2, [], s, stepf, startf
| ⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β) |
| s ≠ s2, ∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s = sl[0] ∧ s2 = sl.last ∧ α ^ = []
⊦ ∃ s1. stepf(s, τ, s1) ∧ move(IOAut(startf, stepf))(s1, [], s2) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 5:
⌜al⌝ ^ = [], sl[0] ≠ sl.last, frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ ) ⊦ ∃ s1. stepf(sl[0], τ, s1) ∧ move(IOAut(startf, stepf))(s1, [], sl.last)
Rule argument
Additional information
Used simplifier rules:
fragstar: ⊦ frag*(IOAut(startf, stepf))(σ, β) ↔ frag(IOAut(startf, stepf))(σ, β) ∧ finp(β);
⊦ finp(⌜x⌝ ); (s)
stream-fin-forward: ⊦ finp(σ) → (∃ x. ⌜x⌝ = σ); (forward) from specification stream-basic[actionstream]
| ⌜al⌝ ^ = [], sl[0] ≠ sl.last, frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ ) ⊦ ∃ s1. stepf(sl[0], τ, s1) ∧ move(IOAut(startf, stepf))(s1, [], sl.last) |
User applied rule exists right
And obtained the following new goals
- Proof step 6:
⌜al⌝ ^ = [], sl[0] ≠ sl.last, frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ ) ⊦ stepf(sl[0], τ, sl[1]) ∧ move(IOAut(startf, stepf))(sl[1], [], sl.last)
Rule argument
pos: right 1 terms: sl[1] abort: F discard: T computed: F
Additional information
Used terms: sl[1]
| ⌜al⌝ ^ = [], sl[0] ≠ sl.last, frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ ) ⊦ stepf(sl[0], τ, sl[1]) ∧ move(IOAut(startf, stepf))(sl[1], [], sl.last) |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 7:
⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β)
- Proof step 8:
⌜al⌝ ^ = [], sl[0] ≠ sl.last, frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ )
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
spec: <toplevel>, name:move,
seq:⊦ move(IOAut(startf, stepf))(s1, β, s2)
↔ (∃ α, sl.
frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β),
subst:[stepf, startf, s2, β, s1] → [stepf, startf, sl.last, [], sl[1]], <all paths>
Additional information
Used terms: sl.last, [], sl[1], stepf, startf
| ⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β) |
| ⌜al⌝ ^ = [], sl[0] ≠ sl.last, frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ )
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 9:
⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
- Proof step 10:
# ⌜sl⌝ = # ⌜al⌝ + ⌜1⌝ , ⌜al⌝ ^ = [], sl[0] ≠ sl.last, ∀ n. ⌜n⌝ < # ⌜al⌝ → stepf(⌜sl⌝ [n], ⌜al⌝ [n], ⌜sl⌝ [n +1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
spec: <toplevel>, name:frag,
seq:⊦ frag(IOAut(startf, stepf))(σ, β)
↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])),
subst:[β, σ, stepf, startf] → [⌜al⌝ , ⌜sl⌝ , stepf, startf], <all paths>
Additional information
Used terms: ⌜al⌝ , ⌜sl⌝ , stepf, startf
| ⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
Proof step 10 from proof emptymove-splitfirst (previous step)
(back to tree)
| # ⌜sl⌝ = # ⌜al⌝ + ⌜1⌝ , ⌜al⌝ ^ = [], sl[0] ≠ sl.last, ∀ n. ⌜n⌝ < # ⌜al⌝ → stepf(⌜sl⌝ [n], ⌜al⌝ [n], ⌜sl⌝ [n +1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 11:
# al + 1 = # sl, ⌜al⌝ ^ = [], sl[0] ≠ sl.last, ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
Additional information
Used simplifier rules:
fragstar: ⊦ frag*(IOAut(startf, stepf))(σ, β) ↔ frag(IOAut(startf, stepf))(σ, β) ∧ finp(β);
⊦ ⌜x⌝ [n] = x[n]; (s)
⊦ m +1 = m + 1; (s)
⊦ ⌜x⌝ [n] = x[n]; (s)
⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s)
⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf
add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf
⊦ ⌜n⌝ + ⌜m⌝ = ⌜n0⌝ ↔ n + m = n0; (s)
⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
Proof step 11 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, ⌜al⌝ ^ = [], sl[0] ≠ sl.last, ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
User applied rule all left
And obtained the following new goals
- Proof step 12:
# al + 1 = # sl, ⌜al⌝ ^ = [], sl[0] ≠ sl.last, 0 < # al → stepf(sl[0], al[0], sl[0 + 1]),
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
pos: left 4 terms: 0 abort: F discard: F computed: F
Additional information
Used terms: 0
Proof step 12 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, ⌜al⌝ ^ = [], sl[0] ≠ sl.last, 0 < # al → stepf(sl[0], al[0], sl[0 + 1]),
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 13:
# al + 1 = # sl, ⌜al⌝ ^ = [], sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
Additional information
Used simplifier rules:
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
⊦ x ≠ [] → x[0] = hd(x); (s)
⊦ # x = 0 ↔ x = []; (s)
⊦ 0 < m ↔ m ≠ 0; (s)
Proof step 13 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, ⌜al⌝ ^ = [], sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 14:
⊦ α ^ = [] ↔ (∀ n. ⌜n⌝ < # α → α[n] = τ)
- Proof step 15:
# al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]),
∀ n. ⌜n⌝ < # ⌜al⌝ → ⌜al⌝ [n] = τ
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
spec: remtau, name:remtau-empty-equiv,
seq: ⊦ α ^ = [] ↔ (∀ n. ⌜n⌝ < # α → α[n] = τ), subst:[α] → [⌜al⌝ ],
<all paths>
Additional information
Used terms: ⌜al⌝
Proof step 14 from proof emptymove-splitfirst (previous step)
(back to tree)
| ⊦ α ^ = [] ↔ (∀ n. ⌜n⌝ < # α → α[n] = τ) |
A spec-lemma
Proof step 15 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]),
∀ n. ⌜n⌝ < # ⌜al⌝ → ⌜al⌝ [n] = τ
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 16:
# al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]),
∀ n. n < # al → al[n] = τ
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
Additional information
Used simplifier rules:
⊦ ⌜x⌝ [n] = x[n]; (s)
⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s)
⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
Proof step 16 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]),
∀ n. n < # al → al[n] = τ
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
User applied rule all left
And obtained the following new goals
- Proof step 17:
# al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), 0 < # al → al[0] = τ, ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
pos: left 5 terms: 0 abort: F discard: F computed: F
Additional information
Used terms: 0
Proof step 17 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), 0 < # al → al[0] = τ, ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 18:
# al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), al ≠ [] → hd(al) = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ n. n < # al → al[n] = τ
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
Additional information
Used simplifier rules:
⊦ x ≠ [] → x[0] = hd(x); (s)
⊦ # x = 0 ↔ x = []; (s)
⊦ 0 < m ↔ m ≠ 0; (s)
Proof step 18 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [] → stepf(sl[0], hd(al), sl[1]), al ≠ [] → hd(al) = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ n. n < # al → al[n] = τ
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
User applied rule cut formula
And obtained the following new goals
- Proof step 19:
# al + 1 = # sl, al = [], sl[0] ≠ sl.last, al ≠ [] → hd(al) = τ, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
- Proof step 21:
# al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [], al ≠ [] → hd(al) = τ, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
fma: al = []
Additional information
Used formulas: al = []
Proof step 19 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, al = [], sl[0] ≠ sl.last, al ≠ [] → hd(al) = τ, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 20:
1 = # sl, sl[0] ≠ sl.last
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [])
Rule argument
Additional information
Used simplifier rules:
⊦ ¬ n < 0; (s)
⊦ # [] = 0; (s)
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
Proof step 20 from proof emptymove-splitfirst (previous step)
(back to tree)
| 1 = # sl, sl[0] ≠ sl.last
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
User applied rule structural induction
And closed the goal!
Rule argument
indvar: sl
Additional information
Used simplifier rules:
statelist freely generated by [], +;;
⊦ #(a ' + x) = (# x)+1; (s)
⊦ m +1 = m + 1; (s)
⊦ 1 = m + 1 ↔ m = 0; (s)
⊦ # x = 0 ↔ x = []; (s)
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
c: ⊦ m + n = n + m; from specification nat-basic
⊦ (a ' + x)[0] = a; (s)
n ≠ 0 ⊦ (a ' + x)[(* n)] = x[n -1]; (s)
⊦ a + x = a ' + x; (s)
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream]
⊦ a '.last = a; (s)
⊦ # [] = 0; (s)
Proof step 21 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, sl[0] ≠ sl.last, al ≠ [], al ≠ [] → hd(al) = τ, al ≠ [] → stepf(sl[0], hd(al), sl[1]), ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ stepf(sl[0], τ, sl[1]) ∧ (∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 22:
# al + 1 = # sl, hd(al) = τ, sl[0] ≠ sl.last, al ≠ [], stepf(sl[0], τ, sl[1]), ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ ∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []
Rule argument
Additional information
Proof step 22 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, hd(al) = τ, sl[0] ≠ sl.last, al ≠ [], stepf(sl[0], τ, sl[1]), ∀ n. n < # al → al[n] = τ,
∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1])
⊦ ∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [] |
Heuristic elimination applied rule apply elim lemma
And obtained the following new goals
- Proof step 23:
# al + 1 = # sl, a = τ, al = a + al0, sl[0] ≠ sl.last, al ≠ [], stepf(sl[0], τ, sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]),
∀ n. n < # al → al[n] = τ
⊦ ∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []
Rule argument
spec: list-data[actionstream], name:elim-list-c,
seq:x ≠ [] ⊦ a = hd(x) ∧ y = tl(x) ↔ x = a + y, subst:[x, a, y] → [al, a, al0]
Additional information
Used simplifier rules:
x ≠ [] ⊦ a = hd(x) ∧ y = tl(x) ↔ x = a + y; (elim)
Used terms: al, a, y
Proof step 23 from proof emptymove-splitfirst (previous step)
(back to tree)
| # al + 1 = # sl, a = τ, al = a + al0, sl[0] ≠ sl.last, al ≠ [], stepf(sl[0], τ, sl[1]), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]),
∀ n. n < # al → al[n] = τ
⊦ ∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [] |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 24:
2 + # al0 = # sl, sl[0] ≠ sl.last, stepf(sl[0], τ, sl[1]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf(sl[n], (τ ' + al0)[n], sl[n + 1])
⊦ ∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = []
Rule argument
Additional information
Used simplifier rules:
⊦ a + x = a ' + x; (s)
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
⊦ m < n + 1 ↔ ¬ n < m; (s)
a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream]
⊦ m +1 = m + 1; (s)
⊦ #(a ' + x) = (# x)+1; (s)
⊦ a ' + x ≠ []; (s)
Proof step 24 from proof emptymove-splitfirst (previous step)
(back to tree)
| 2 + # al0 = # sl, sl[0] ≠ sl.last, stepf(sl[0], τ, sl[1]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf(sl[n], (τ ' + al0)[n], sl[n + 1])
⊦ ∃ α, sl0. frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ finp(α) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = [] |
User applied rule exists right
And obtained the following new goals
- Proof step 25:
2 + # al0 = # sl, sl[0] ≠ sl.last, stepf(sl[0], τ, sl[1]), ∀ n. ¬ # al0 < n → stepf(sl[n], (τ ' + al0)[n], sl[n + 1]),
∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜tl(sl)⌝ , ⌜al0⌝ ) ∧ finp(⌜al0⌝ ) ∧ sl[1] = tl(sl)[0] ∧ sl.last = tl(sl).last ∧ ⌜al0⌝ ^ = []
Rule argument
pos: right 1 terms: ⌜al0⌝ , tl(sl) abort: F discard: T computed: F
Additional information
Used terms: ⌜al0⌝ , tl(sl)
Proof step 25 from proof emptymove-splitfirst (previous step)
(back to tree)
| 2 + # al0 = # sl, sl[0] ≠ sl.last, stepf(sl[0], τ, sl[1]), ∀ n. ¬ # al0 < n → stepf(sl[n], (τ ' + al0)[n], sl[n + 1]),
∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜tl(sl)⌝ , ⌜al0⌝ ) ∧ finp(⌜al0⌝ ) ∧ sl[1] = tl(sl)[0] ∧ sl.last = tl(sl).last ∧ ⌜al0⌝ ^ = [] |
Heuristic elimination applied rule apply elim lemma
And obtained the following new goals
- Proof step 26:
2 + # al0 = # sl, sl = a + sl0, sl[0] ≠ sl.last, sl ≠ [], stepf(sl[0], τ, sl[1]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf(sl[n], (τ ' + al0)[n], sl[n + 1])
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ finp(⌜al0⌝ ) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ ⌜al0⌝ ^ = []
Rule argument
spec: list-data[IOstatestream], name:elim-list-c,
seq:x ≠ [] ⊦ a = hd(x) ∧ y = tl(x) ↔ x = a + y, subst:[x, a, y] → [sl, a, sl0]
Additional information
Used simplifier rules:
⊦ # [] = 0; (s)
⊦ m + n = 0 ↔ m = 0 ∧ n = 0; (ws)
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
c: ⊦ m + n = n + m; from specification nat-basic
x ≠ [] ⊦ a = hd(x) ∧ y = tl(x) ↔ x = a + y; (elim)
Used terms: sl, a, y
Proof step 26 from proof emptymove-splitfirst (previous step)
(back to tree)
| 2 + # al0 = # sl, sl = a + sl0, sl[0] ≠ sl.last, sl ≠ [], stepf(sl[0], τ, sl[1]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf(sl[n], (τ ' + al0)[n], sl[n + 1])
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ finp(⌜al0⌝ ) ∧ sl[1] = sl0[0] ∧ sl.last = sl0.last ∧ ⌜al0⌝ ^ = [] |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 27:
# sl0 = # al0 + 1, a ≠ (a ' + sl0).last, stepf(a, τ, sl0[0]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n])
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ (a ' + sl0).last = sl0.last ∧ ⌜al0⌝ ^ = []
Rule argument
Additional information
Used simplifier rules:
⊦ a + x = a ' + x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream]
n ≠ 0 ⊦ (a ' + x)[(* n)] = x[n -1]; (s)
⊦ finp(⌜x⌝ ); (s)
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
⊦ (a ' + x)[n + 1] = x[n]; (s)
⊦ (a ' + x)[0] = a; (s)
⊦ a ' + x ≠ []; (s)
n < n0 ⊦ m + (* n) = m0 + (* n0) ↔ m = m0 + (n0 - n); (s)
⊦ m +1 = m + 1; (s)
⊦ #(a ' + x) = (# x)+1; (s)
Proof step 27 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl0 = # al0 + 1, a ≠ (a ' + sl0).last, stepf(a, τ, sl0[0]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n])
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ (a ' + sl0).last = sl0.last ∧ ⌜al0⌝ ^ = [] |
Heuristic nonsplitting cut applied rule cut formula
And obtained the following new goals
- Proof step 28:
# sl0 = # al0 + 1, a ≠ (a ' + sl0).last, sl0 ≠ [], stepf(a, τ, sl0[0]),
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ (a ' + sl0).last = sl0.last ∧ ⌜al0⌝ ^ = []
Rule argument
fma: sl0 = []
Additional information
Used simplifier rules:
⊦ # [] = 0; (s)
⊦ m + n = 0 ↔ m = 0 ∧ n = 0; (ws)
⊦ # x = 0 ↔ x = []; (s)
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
c: ⊦ m + n = n + m; from specification nat-basic
Used formulas: sl0 = []
Proof step 28 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl0 = # al0 + 1, a ≠ (a ' + sl0).last, sl0 ≠ [], stepf(a, τ, sl0[0]),
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ (a ' + sl0).last = sl0.last ∧ ⌜al0⌝ ^ = [] |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 29:
# sl0 = # al0 + 1, a ≠ sl0.last, sl0 ≠ [], stepf(a, τ, hd(sl0)), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n])
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = []
Rule argument
Additional information
Used simplifier rules:
a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream]
⊦ x ≠ [] → (a ' + x).last = x.last; (s)
⊦ x ≠ [] → x[0] = hd(x); (s)
Proof step 29 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl0 = # al0 + 1, a ≠ sl0.last, sl0 ≠ [], stepf(a, τ, hd(sl0)), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n])
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = [] |
Heuristic elimination applied rule apply elim lemma
And obtained the following new goals
- Proof step 30:
# sl0 = # al0 + 1, sl0 = a0 + sl, a ≠ sl0.last, sl0 ≠ [], stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = []
Rule argument
spec: list-data[IOstatestream], name:elim-1,
seq: ⊦ x ≠ [] → (head = hd(x) ∧ tail = tl(x) ↔ x = head + tail),
subst:[x, head, tail] → [sl0, a0, sl]
Additional information
Used simplifier rules:
⊦ x ≠ [] → (head = hd(x) ∧ tail = tl(x) ↔ x = head + tail); (elim)
Used terms: sl0, head, tail
Proof step 30 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl0 = # al0 + 1, sl0 = a0 + sl, a ≠ sl0.last, sl0 ≠ [], stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + sl0)[n], (τ ' + al0)[n], sl0[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜sl0⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = [] |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 31:
# sl = # al0, a ≠ (a0 ' + sl).last, stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = []
Rule argument
Additional information
Used simplifier rules:
a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream]
⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s)
⊦ a + x = a ' + x; (s)
⊦ a ' + x ≠ []; (s)
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
⊦ m + n = m + n0 ↔ n = n0; (s)
⊦ m +1 = m + 1; (s)
⊦ #(a ' + x) = (# x)+1; (s)
Proof step 31 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ (a0 ' + sl).last, stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = [] |
Heuristic weak cut applied rule cut formula
And obtained the following new goals
- Proof step 32:
# sl = # al0, a ≠ (a0 ' + sl).last, sl ≠ [], stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = []
Rule argument
fma: sl = []
Additional information
Used simplifier rules:
frag-one: ⊦ frag(IOAut(startf, stepf))(⌜s '⌝ , []);
⊦ # [] = 0; (s)
⊦ # x = 0 ↔ x = []; (s)
⊦ a '.last = a; (s)
⊦ x + [] = x; (s)
⊦ ⌜[]⌝ = []; (s)
⊦ σ + [] = σ; (s)
append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[IOstatestream]
⊦ (a ' + x)[0] = a; (s)
a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream]
⊦ a '[0] = a; (s)
⊦ # [] = 0; (s)
⊦ 0 < m ↔ m ≠ 0; (s)
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream]
⊦ a '[0] = a; (s)
⊦ ⌜[]⌝ = []; (s)
⊦ [] ^ = []; (s)
Used formulas: sl = []
Proof step 32 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ (a0 ' + sl).last, sl ≠ [], stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = [] |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 33:
# sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = []
Rule argument
Additional information
Used simplifier rules:
a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream]
⊦ x ≠ [] → (a ' + x).last = x.last; (s)
Proof step 33 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ ⌜al0⌝ ^ = [] |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 34:
⊦ α ^ = [] ↔ (∀ n. ⌜n⌝ < # α → α[n] = τ)
- Proof step 35:
# sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]),
∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ (∀ n. ⌜n⌝ < # ⌜al0⌝ → ⌜al0⌝ [n] = τ)
Rule argument
spec: remtau, name:remtau-empty-equiv,
seq: ⊦ α ^ = [] ↔ (∀ n. ⌜n⌝ < # α → α[n] = τ), subst:[α] → [⌜al0⌝ ],
<all paths>
Additional information
Used terms: ⌜al0⌝
Proof step 34 from proof emptymove-splitfirst (previous step)
(back to tree)
| ⊦ α ^ = [] ↔ (∀ n. ⌜n⌝ < # α → α[n] = τ) |
A spec-lemma
Proof step 35 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]),
∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ (∀ n. ⌜n⌝ < # ⌜al0⌝ → ⌜al0⌝ [n] = τ) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 36:
# sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ (n < # al0 → al0[n] = τ)
Rule argument
Additional information
Used simplifier rules:
⊦ ⌜x⌝ [n] = x[n]; (s)
⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s)
⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
Proof step 36 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ) ∧ (n < # al0 → al0[n] = τ) |
User applied rule case distinction
And obtained the following new goals
- Proof step 37:
# sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ¬ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦
- Proof step 41:
# sl = # al0, al0[n] ≠ τ, a ≠ sl.last, sl ≠ [], n < # al0, stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦
Rule argument
pos: right 1
Additional information
Proof step 37 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ¬ frag(IOAut(startf, stepf))(⌜a0 '⌝ + ⌜sl⌝ , ⌜al0⌝ ),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 38:
⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
- Proof step 39:
# sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]),
#(⌜a0 '⌝ + ⌜sl⌝ ) ≠ # ⌜al0⌝ + ⌜1⌝ ∨ (∃ n. ¬(⌜n⌝ < # ⌜al0⌝ → stepf((⌜a0 '⌝ + ⌜sl⌝ )[n], ⌜al0⌝ [n], (⌜a0 '⌝ + ⌜sl⌝ )[n +1])))
⊦
Rule argument
spec: <toplevel>, name:frag,
seq:⊦ frag(IOAut(startf, stepf))(σ, β)
↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])),
subst:[β, σ, stepf, startf] → [⌜al0⌝ , ⌜a0 '⌝ + ⌜sl⌝ , stepf, startf], <all paths>
Additional information
Used terms: ⌜al0⌝ , ⌜a0 '⌝ + ⌜sl⌝ , stepf, startf
Proof step 38 from proof emptymove-splitfirst (previous step)
(back to tree)
| ⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
Proof step 39 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ sl.last, sl ≠ [], stepf(a, τ, a0), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ,
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]),
#(⌜a0 '⌝ + ⌜sl⌝ ) ≠ # ⌜al0⌝ + ⌜1⌝ ∨ (∃ n. ¬(⌜n⌝ < # ⌜al0⌝ → stepf((⌜a0 '⌝ + ⌜sl⌝ )[n], ⌜al0⌝ [n], (⌜a0 '⌝ + ⌜sl⌝ )[n +1])))
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 40:
# sl = # al0, a ≠ sl.last, al0 ≠ [], sl ≠ [], n < # al0, stepf(a, τ, a0), ¬ stepf((a0 ' + sl)[n], al0[n], sl[n]),
∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ, ∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦
Rule argument
Additional information
Used simplifier rules:
⊦ # x = 0 ↔ x = []; (s)
lf-01: ⊦ m < n ∧ n = n0 → m < n0; (forward) from specification nat-basic
f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic
append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[IOstatestream]
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
⊦ ⌜x⌝ [n] = x[n]; (s)
⊦ (⌜a '⌝ + σ)[n + 1] = σ[n]; (s)
⊦ m +1 = m + 1; (s)
⊦ ⌜x⌝ [n] = x[n]; (s)
⊦ (⌜x⌝ + ⌜x0⌝ )[m] = (x + x0)[m]; (s)
⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s)
⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf
add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf
⊦ ⌜n⌝ = ⌜n0⌝ ↔ n = n0; (s)
⊦ n∞ + ⌜0⌝ = n∞; (s)
⊦ m ≤ n → (⌜(* n)⌝ + n∞1 = ⌜(* m)⌝ + n∞2 ↔ ⌜n - m⌝ + n∞1 = n∞2); (s)
⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
⊦ # a ' = 0 +1; (s)
⊦ #(σ + σ1) = # σ + # σ1; (s)
Proof step 40 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, a ≠ sl.last, al0 ≠ [], sl ≠ [], n < # al0, stepf(a, τ, a0), ¬ stepf((a0 ' + sl)[n], al0[n], sl[n]),
∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ, ∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n])
⊦ |
User applied rule all left
And closed the goal!
Rule argument
pos: left 9 terms: n + 1 abort: F discard: T computed: F
Additional information
Used simplifier rules:
⊦ m < n + 1 ↔ ¬ n < m; (s)
⊦ (a ' + x)[n + 1] = x[n]; (s)
a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream]
⊦ (a ' + x)[n + 1] = x[n]; (s)
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream]
Used terms: n + 1
Proof step 41 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, al0[n] ≠ τ, a ≠ sl.last, sl ≠ [], n < # al0, stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 42:
# sl = # al0, al0[n] ≠ τ, a ≠ sl.last, al0 ≠ [], sl ≠ [], n < # al0, stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦
Rule argument
Additional information
Used simplifier rules:
⊦ # x = 0 ↔ x = []; (s)
lf-01: ⊦ m < n ∧ n = n0 → m < n0; (forward) from specification nat-basic
f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic
Proof step 42 from proof emptymove-splitfirst (previous step)
(back to tree)
| # sl = # al0, al0[n] ≠ τ, a ≠ sl.last, al0 ≠ [], sl ≠ [], n < # al0, stepf(a, τ, a0),
∀ n. ¬ # al0 < n → stepf((a ' + a0 ' + sl)[n], (τ ' + al0)[n], (a0 ' + sl)[n]), ∀ n. ¬ # al0 < n → (τ ' + al0)[n] = τ
⊦ |
User applied rule all left
And closed the goal!
Rule argument
pos: left 9 terms: n + 1 abort: F discard: T computed: F
Additional information
Used simplifier rules:
⊦ m < n + 1 ↔ ¬ n < m; (s)
⊦ (a ' + x)[n + 1] = x[n]; (s)
a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic
c: ⊦ m + n = n + m; from specification nat-basic
a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream]
Used terms: n + 1
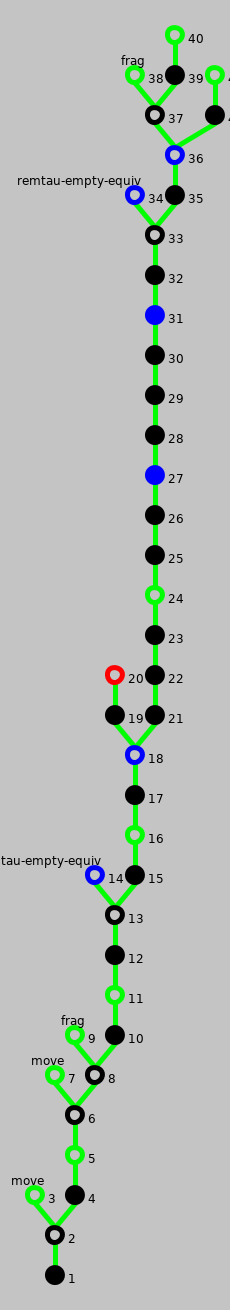
Proof Tree for emptymove-splitfirst
(View conclusion)
The following image shows the proof tree of sequent calculus. The
proved goal is at the bottom. You can click on the nodes to view
additional rules. See here for details on colors in a proof
tree.