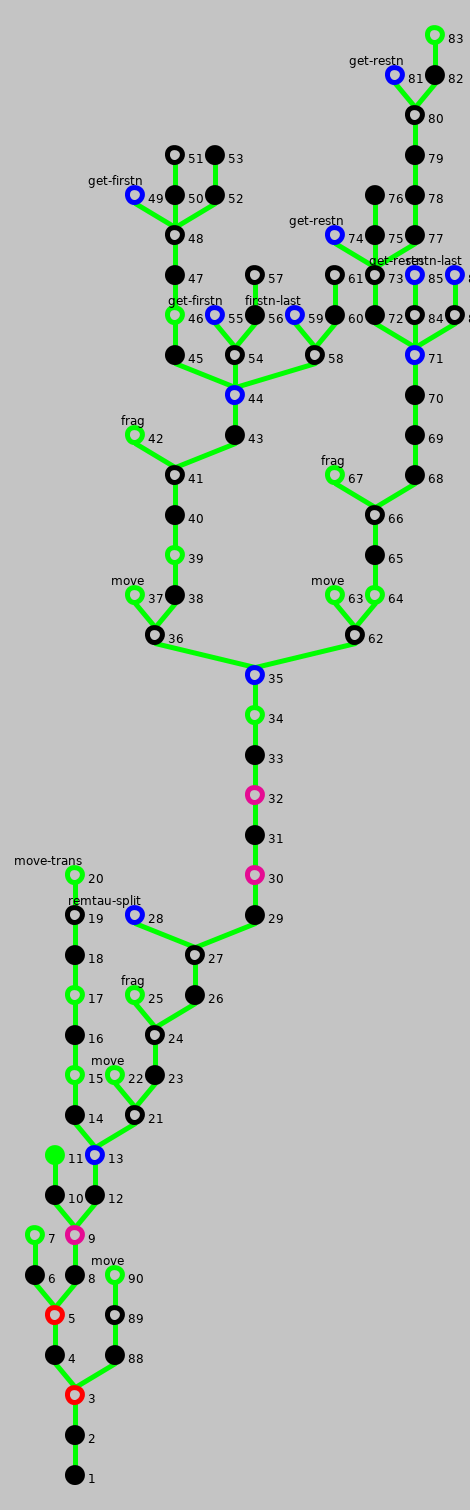
Proof Tree for move-split (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ¬ # α < ⌜n⌝ , move(IOAut(startf, stepf))(s, α, s2) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, α to n, s1) ∧ move(IOAut(startf, stepf))(s1, α from n, s2) |
move(IOAut(startf, stepf))(s, α, s2), ¬ # α < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, α to n, s1) ∧ move(IOAut(startf, stepf))(s1, α from n, s2)
| move(IOAut(startf, stepf))(s, α, s2), ¬ # α < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, α to n, s1) ∧ move(IOAut(startf, stepf))(s1, α from n, s2) |
move(IOAut(startf, stepf))(s, α, s2), ¬ # α < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, α to n, s1) ∧ move(IOAut(startf, stepf))(s1, α from n, s2)
| move(IOAut(startf, stepf))(s, α, s2), ¬ # α < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, α to n, s1) ∧ move(IOAut(startf, stepf))(s1, α from n, s2) |
move(IOAut(startf, stepf))(s, ⌜al⌝ , s2), ¬ # ⌜al⌝ < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜al⌝ to n, s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al⌝ from n, s2)
move(IOAut(startf, stepf))(s, ⌜af⌝ , s2), ¬ # ⌜af⌝ < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜af⌝ to n, s1) ∧ move(IOAut(startf, stepf))(s1, ⌜af⌝ from n, s2)
Used simplifier rules: actionstream freely generated by ⌜ ⌝, ⌜ ⌝;;
| move(IOAut(startf, stepf))(s, ⌜al⌝ , s2), ¬ # ⌜al⌝ < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜al⌝ to n, s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al⌝ from n, s2) |
move(IOAut(startf, stepf))(s, ⌜al⌝ , s2), n ≤ # al ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜al to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al from n⌝ , s2)
Used simplifier rules: ⊦ ⌜x⌝ from n = ⌜x from n⌝ ; (s) ⊦ ⌜x⌝ to n = ⌜x to n⌝ ; (s) ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
| move(IOAut(startf, stepf))(s, ⌜al⌝ , s2), n ≤ # al ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜al to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al from n⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜[]⌝ , s2), n ≤ # [] ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜[] to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜[] from n⌝ , s2)
move(IOAut(startf, stepf))(s, ⌜action + al0⌝ , s2), n ≤ #(action + al0), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action + al0 from n⌝ , s2)
Used simplifier rules: actionlist freely generated by [], +;;
| move(IOAut(startf, stepf))(s, ⌜[]⌝ , s2), n ≤ # [] ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜[] to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜[] from n⌝ , s2) |
move(IOAut(startf, stepf))(s, [], s2) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, [], s1) ∧ move(IOAut(startf, stepf))(s1, [], s2)
Used simplifier rules: ⊦ ⌜[]⌝ = []; (s) ⊦ x from 0 = x; (s) ⊦ x to 0 = []; (s) ⊦ m ≤ 0 ↔ m = 0; (s) ⊦ # [] = 0; (s)
| move(IOAut(startf, stepf))(s, [], s2) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, [], s1) ∧ move(IOAut(startf, stepf))(s1, [], s2) |
Used simplifier rules: move-empty: ⊦ move(IOAut(startf, stepf))(s, [], s); Used terms: s2
| move(IOAut(startf, stepf))(s, ⌜action + al0⌝ , s2), n ≤ #(action + al0), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action + al0 from n⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n ≤ # al0 + 1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action ' + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action ' + al0 from n⌝ , s2)
Used simplifier rules: ⊦ a + x = a ' + x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s) ⊦ m +1 = m + 1; (s) ⊦ #(a ' + x) = (# x)+1; (s)
| move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n ≤ # al0 + 1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action ' + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action ' + al0 from n⌝ , s2) |
n = 0, move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n ≤ # al0 + 1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action ' + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action ' + al0 from n⌝ , s2)
n = n0 +1, move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n ≤ # al0 + 1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action ' + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action ' + al0 from n⌝ , s2)
Used simplifier rules: nat freely generated by 0, +1;;
| n = 0, move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n ≤ # al0 + 1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action ' + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action ' + al0 from n⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, [], s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action '⌝ + ⌜al0⌝ , s2)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s) ⊦ x from 0 = x; (s) ⊦ ⌜[]⌝ = []; (s) ⊦ x to 0 = []; (s) ⊦ 0 ≤ m; (s)
| move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, [], s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action '⌝ + ⌜al0⌝ , s2) |
Used simplifier rules: move-empty: ⊦ move(IOAut(startf, stepf))(s, [], s); Used terms: s
| n = n0 +1, move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n ≤ # al0 + 1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action ' + al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜action ' + al0 from n⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ a ' + x from n + 1 = x from n; (s) ⊦ m +1 = m + 1; (s) ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s) ⊦ a + x = a ' + x; (s) ⊦ a ' + x to n + 1 = a + (x to n); (s) ⊦ m + n ≤ m + n0 ↔ n ≤ n0; (s)
| move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2)
move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2), ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2)
Used formulas: ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2)
| move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2)
| move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), n0 ≤ # al0, move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2) ∧ n0 ≤ # al0 → (∃ s0. move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0) ∧ move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2)
Used terms: startf, stepf, s1, s2, n0
| move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), n0 ≤ # al0, move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2) ∧ n0 ≤ # al0 → (∃ s0. move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0) ∧ move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0), move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2), n0 ≤ # al0 ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2)
| move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0), move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2), n0 ≤ # al0 ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2) |
move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), n0 ≤ # al0 ⊦ move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s0) ∧ move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2)
Used terms: s0
| move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), n0 ≤ # al0 ⊦ move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s0) ∧ move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2) |
move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0), move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2), n0 ≤ # al0, ¬ move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s0) ⊦
| move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1), move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), move(IOAut(startf, stepf))(s1, ⌜al0 to n0⌝ , s0), move(IOAut(startf, stepf))(s0, ⌜al0 from n0⌝ , s2), n0 ≤ # al0, ¬ move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s0) ⊦ |
⊦ move(IOAut(startf, stepf))(s, α1, s1) ∧ move(IOAut(startf, stepf))(s1, α2, s2) → move(IOAut(startf, stepf))(s, α1 + α2, s2)
Used terms: s1, s0, ⌜al0 to n0⌝ , ⌜action '⌝ , s, stepf, startf
| ⊦ move(IOAut(startf, stepf))(s, α1, s1) ∧ move(IOAut(startf, stepf))(s1, α2, s2) → move(IOAut(startf, stepf))(s, α1 + α2, s2) |
| move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0⌝ , s2), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2), ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2) |
⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β)
n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s = sl[0] ∧ s2 = sl.last ∧ α ^ = ⌜action '⌝ + ⌜al0⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2)
Used terms: s2, ⌜action '⌝ + ⌜al0⌝ , s, stepf, startf
| ⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β) |
| n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s = sl[0] ∧ s2 = sl.last ∧ α ^ = ⌜action '⌝ + ⌜al0⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , s2), ∃ s1. move(IOAut(startf, stepf))(s, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , s2) |
⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ ), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last)
Used simplifier rules: fragstar: ⊦ frag*(IOAut(startf, stepf))(σ, β) ↔ frag(IOAut(startf, stepf))(σ, β) ∧ finp(β); ⊦ finp(⌜x⌝ ); (s) stream-fin-forward: ⊦ finp(σ) → (∃ x. ⌜x⌝ = σ); (forward) from specification stream-basic[actionstream]
| ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , frag(IOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ ), n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last) |
⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
# ⌜sl⌝ = # ⌜al⌝ + ⌜1⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. ⌜n⌝ < # ⌜al⌝ → stepf(⌜sl⌝ [n], ⌜al⌝ [n], ⌜sl⌝ [n +1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: ⌜al⌝ , ⌜sl⌝ , stepf, startf
| ⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
| # ⌜sl⌝ = # ⌜al⌝ + ⌜1⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. ⌜n⌝ < # ⌜al⌝ → stepf(⌜sl⌝ [n], ⌜al⌝ [n], ⌜sl⌝ [n +1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
# al + 1 = # sl, ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last)
Used simplifier rules: ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ m +1 = m + 1; (s) ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s) add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf ⊦ ⌜n⌝ + ⌜m⌝ = ⌜n0⌝ ↔ n + m = n0; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
| # al + 1 = # sl, ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last) |
⊦ α ^ = ⌜al⌝ + β2 → (∃ α1, α2. α1 ^ = ⌜al⌝ ∧ α2 ^ = β2 ∧ α1 + α2 = α)
# al + 1 = # sl, ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , n0 ≤ # al0, ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ → (∃ α1, α2. α1 ^ = ⌜action '⌝ ∧ α2 ^ = ⌜al0⌝ ∧ α1 + α2 = ⌜al⌝ ), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: ⌜al⌝ , action ', ⌜al0⌝
| ⊦ α ^ = ⌜al⌝ + β2 → (∃ α1, α2. α1 ^ = ⌜al⌝ ∧ α2 ^ = β2 ∧ α1 + α2 = α) |
| # al + 1 = # sl, ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , n0 ≤ # al0, ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ → (∃ α1, α2. α1 ^ = ⌜action '⌝ ∧ α2 ^ = ⌜al0⌝ ∧ α1 + α2 = ⌜al⌝ ), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
# al + 1 = # sl, α1 + α2 = ⌜al⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , α1 ^ = ⌜action '⌝ , α2 ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last)
| # al + 1 = # sl, α1 + α2 = ⌜al⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , α1 ^ = ⌜action '⌝ , α2 ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last) |
α1 + α2 = ⌜al⌝ , # al + 1 = # sl, α2 ^ = ⌜al0⌝ , α1 ^ = ⌜action '⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , α1 = ⌜al1⌝ , n0 ≤ # al0, ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: actionstream freely generated by ⌜ ⌝, ⌜ ⌝;; ⊦ ⌜nf⌝ + σ = ⌜nf⌝ ; (s) append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[actionstream] ⊦ ⌜x⌝ ≠ ⌜nf⌝ ; (s)
| α1 + α2 = ⌜al⌝ , # al + 1 = # sl, α2 ^ = ⌜al0⌝ , α1 ^ = ⌜action '⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , α1 = ⌜al1⌝ , n0 ≤ # al0, ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
# al + 1 = # sl, ⌜al1⌝ + α2 = ⌜al⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , α2 ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last)
| # al + 1 = # sl, ⌜al1⌝ + α2 = ⌜al⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , α2 ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last) |
⌜al1⌝ + α2 = ⌜al⌝ , # al + 1 = # sl, α2 ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , α2 = ⌜al2⌝ , n0 ≤ # al0, ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: actionstream freely generated by ⌜ ⌝, ⌜ ⌝;; ⊦ ⌜x⌝ ≠ σ + ⌜nf0⌝ ; (s) append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[actionstream]
| ⌜al1⌝ + α2 = ⌜al⌝ , # al + 1 = # sl, α2 ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al⌝ ^ = ⌜action '⌝ + ⌜al0⌝ , α2 = ⌜al2⌝ , n0 ≤ # al0, ∀ n. n < # al → stepf(sl[n], al[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ #(x + y) = # x + # y; (s) append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[actionstream] ⊦ (⌜al⌝ + α2)^ = ⌜al⌝ ^ + α2 ^; (s) ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ ⌜x⌝ + ⌜y⌝ = ⌜z⌝ ↔ x + y = z; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , sl[# al1]) ∧ move(IOAut(startf, stepf))(sl[# al1], ⌜al0⌝ , sl.last)
Used terms: sl[# al1]
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , sl[# al1]) ∧ move(IOAut(startf, stepf))(sl[# al1], ⌜al0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ¬ move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , sl[# al1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ¬ move(IOAut(startf, stepf))(sl[# al1], ⌜al0⌝ , sl.last), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ¬ move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ , sl[# al1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β)
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ α, sl0. ¬(frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[0] = sl0[0] ∧ sl[# al1] = sl0.last ∧ α ^ = ⌜action '⌝ ) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: sl[# al1], ⌜action '⌝ , sl[0], stepf, startf
| ⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β) |
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ α, sl0. ¬(frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[0] = sl0[0] ∧ sl[# al1] = sl0.last ∧ α ^ = ⌜action '⌝ ) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ α, sl0. ¬ frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∨ ¬ finp(α) ∨ sl[0] ≠ sl0[0] ∨ sl[# al1] ≠ sl0.last ∨ α ^ ≠ ⌜action '⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: fragstar: ⊦ frag*(IOAut(startf, stepf))(σ, β) ↔ frag(IOAut(startf, stepf))(σ, β) ∧ finp(β);
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ α, sl0. ¬ frag(IOAut(startf, stepf))(⌜sl0⌝ , α) ∨ ¬ finp(α) ∨ sl[0] ≠ sl0[0] ∨ sl[# al1] ≠ sl0.last ∨ α ^ ≠ ⌜action '⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ¬ frag(IOAut(startf, stepf))(⌜firstn(# al1 + 1, sl)⌝ , ⌜al1⌝ ) ∨ ¬ finp(⌜al1⌝ ) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ∨ ⌜al1⌝ ^ ≠ ⌜action '⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: ⌜al1⌝ , firstn(# al1 + 1, sl)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ¬ frag(IOAut(startf, stepf))(⌜firstn(# al1 + 1, sl)⌝ , ⌜al1⌝ ) ∨ ¬ finp(⌜al1⌝ ) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ∨ ⌜al1⌝ ^ ≠ ⌜action '⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ¬ frag(IOAut(startf, stepf))(⌜firstn(# al1 + 1, sl)⌝ , ⌜al1⌝ ) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ finp(⌜x⌝ ); (s)
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ¬ frag(IOAut(startf, stepf))(⌜firstn(# al1 + 1, sl)⌝ , ⌜al1⌝ ) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ¬ ( # ⌜firstn(# al1 + 1, sl)⌝ = # ⌜al1⌝ + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # ⌜al1⌝ → stepf(⌜firstn(# al1 + 1, sl)⌝ [n], ⌜al1⌝ [n], ⌜firstn(# al1 + 1, sl)⌝ [n +1]))) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: ⌜al1⌝ , ⌜firstn(# al1 + 1, sl)⌝ , stepf, startf
| ⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ¬ ( # ⌜firstn(# al1 + 1, sl)⌝ = # ⌜al1⌝ + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # ⌜al1⌝ → stepf(⌜firstn(# al1 + 1, sl)⌝ [n], ⌜al1⌝ [n], ⌜firstn(# al1 + 1, sl)⌝ [n +1]))) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ¬(n < # al1 → stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1])) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ m +1 = m + 1; (s) ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s) add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf ⊦ ⌜n⌝ = ⌜n0⌝ ↔ n = n0; (s) ⊦ n∞ + ⌜0⌝ = n∞; (s) ⊦ m ≤ n → (⌜(* n)⌝ + n∞1 = ⌜(* m)⌝ + n∞2 ↔ ⌜n - m⌝ + n∞1 = n∞2); (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ ⌜m + n⌝ = ⌜m⌝ + ⌜n⌝ ; (s) ⊦ # firstn(n, x) = n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ¬(n < # al1 → stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1])) ∨ sl[0] ≠ firstn(# al1 + 1, sl)[0] ∨ sl[# al1] ≠ firstn(# al1 + 1, sl).last ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n < # al1, n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[0] ≠ firstn(# al1 + 1, sl)[0], n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[# al1] ≠ firstn(# al1 + 1, sl).last, n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n < # al1, n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], n < # al1, n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ # x = 0 ↔ x = []; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], n < # al1, n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al1 ≠ [], n < # al1, n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: n
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al1 ≠ [], n < # al1, n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], n < # al1 + # al2, n < # al1, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ m < n → n ≠ 0; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ ¬ m + n < m; (s) fle-01: ⊦ m ≤ n ∧ n < n0 → m < n0; (forward) from specification nat ⊦ m < n ↔ ¬ n ≤ m; (ss) a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ n < # x → (x + y)[n] = x[n]; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], n < # al1 + # al2, n < # al1, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ n < m ∧ m ≤ # x → firstn(m, x)[n] = x[n]
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al1 ≠ [], n < # al1, n < # al1 + # al2, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), n < # al1 + 1 ∧ # al1 + 1 ≤ # sl
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al1 ≠ [], n < # al1, n < # al1 + # al2, n < # al1 + 1, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, # al1 + 1 ≤ # sl, ¬ stepf(sl[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: n, sl, # al1 + 1
| ⊦ n < m ∧ m ≤ # x → firstn(m, x)[n] = x[n] |
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al1 ≠ [], n < # al1, n < # al1 + # al2, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), n < # al1 + 1 ∧ # al1 + 1 ≤ # sl |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], n < # al1 + # al2, n < # al1, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, # sl ≤ # al1, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ m < n ↔ ¬ n ≤ m; (ss) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ m < n → ¬ n < m; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], n < # al1 + # al2, n < # al1, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, # sl ≤ # al1, ¬ stepf(firstn(# al1 + 1, sl)[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
Used simplifier rules: ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ ¬ m + n < m; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al1 ≠ [], n < # al1, n < # al1 + # al2, n < # al1 + 1, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, # al1 + 1 ≤ # sl, ¬ stepf(sl[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], sl ≠ [], n < # al1 + # al2, n < # al1, # al1 < # sl, n < # sl, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, ¬ stepf(sl[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(hd(sl), ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m < n → ¬ n < m; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) lf-01: ⊦ m < n ∧ n = n0 → m < n0; (forward) from specification nat-basic ⊦ x ≠ [] → x[0] = hd(x); (s) ⊦ m = m0 + n0 ∧ n < n0 → m0 + n < m; (s) ⊦ m +1 = m + 1; (s) ⊦ ¬ m + n < m; (s) ⊦ # x = 0 ↔ x = []; (s) trans: ⊦ n < n0 ∧ n0 < n1 → n < n1; (forward) from specification nat-basic lf: ⊦ m < n ∧ n < n0 → m +1 < n0; (forward) from specification nat-basic f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ m + 1 ≤ n ↔ m < n; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al1 ≠ [], sl ≠ [], n < # al1 + # al2, n < # al1, # al1 < # sl, n < # sl, stepf(sl[n], al1[n], sl[n + 1]), n0 ≤ # al0, ¬ stepf(sl[n], al1[n], firstn(# al1 + 1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(hd(sl), ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
Used simplifier rules: ⊦ m + n = m + n0 ↔ n = n0; (s) ⊦ a ' + x ≠ []; (s) ⊦ #(a ' + x) = (# x)+1; (s) ⊦ m +1 = m + 1; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) ⊦ firstn(n + 1, a ' + x) = a + firstn(n, x); (s) ⊦ a + x = a ' + x; (s) ⊦ (a ' + x)[n + 1] = x[n]; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream] ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ n < m ∧ m ≤ # x → firstn(m, x)[n] = x[n]; (s) x ≠ [] ⊦ a = hd(x) ∧ y = tl(x) ↔ x = a + y; (elim) Used terms: sl, a, y
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[0] ≠ firstn(# al1 + 1, sl)[0], n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ n < m ∧ m ≤ # x → firstn(m, x)[n] = x[n]
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , sl[0] ≠ firstn(# al1 + 1, sl)[0], n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), 0 < # al1 + 1 ∧ # al1 + 1 ≤ # sl
Used terms: 0, sl, # al1 + 1
| ⊦ n < m ∧ m ≤ # x → firstn(m, x)[n] = x[n] |
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , sl[0] ≠ firstn(# al1 + 1, sl)[0], n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), 0 < # al1 + 1 ∧ # al1 + 1 ≤ # sl |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[0] ≠ firstn(# al1 + 1, sl)[0], n0 ≤ # al0, # sl ≤ # al1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ m < n ↔ ¬ n ≤ m; (ss) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ m + 1 ≠ 0; (s) ⊦ 0 < m ↔ m ≠ 0; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[0] ≠ firstn(# al1 + 1, sl)[0], n0 ≤ # al0, # sl ≤ # al1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
Used simplifier rules: ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ ¬ m + n < m; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[# al1] ≠ firstn(# al1 + 1, sl).last, n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ m ≠ 0 ∧ m ≤ # x → firstn(m, x).last = x[m -1]
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , sl[# al1] ≠ firstn(# al1 + 1, sl).last, n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), # al1 + 1 ≠ 0 ∧ # al1 + 1 ≤ # sl
Used simplifier rules: ⊦ m + 1 ≠ 0; (s) ⊦ (m + 1)-1 = m; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: sl, # al1 + 1
| ⊦ m ≠ 0 ∧ m ≤ # x → firstn(m, x).last = x[m -1] |
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , sl[# al1] ≠ firstn(# al1 + 1, sl).last, n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), # al1 + 1 ≠ 0 ∧ # al1 + 1 ≤ # sl |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[# al1] ≠ firstn(# al1 + 1, sl).last, n0 ≤ # al0, # sl ≤ # al1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ m < n ↔ ¬ n ≤ m; (ss) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ m + 1 ≠ 0; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[# al1] ≠ firstn(# al1 + 1, sl).last, n0 ≤ # al0, # sl ≤ # al1, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
Used simplifier rules: ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ ¬ m + n < m; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ¬ move(IOAut(startf, stepf))(sl[# al1], ⌜al0⌝ , sl.last), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β)
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ α, sl0. ¬(frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[# al1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = ⌜al0⌝ ) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: sl.last, ⌜al0⌝ , sl[# al1], stepf, startf
| ⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β) |
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ α, sl0. ¬(frag*(IOAut(startf, stepf))(⌜sl0⌝ , α) ∧ sl[# al1] = sl0[0] ∧ sl.last = sl0.last ∧ α ^ = ⌜al0⌝ ) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), frag*(IOAut(startf, stepf))(⌜restn(# al1, sl)⌝ , ⌜al2⌝ ) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last ∧ ⌜al2⌝ ^ = ⌜al0⌝
Used terms: ⌜al2⌝ , restn(# al1, sl)
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), frag*(IOAut(startf, stepf))(⌜restn(# al1, sl)⌝ , ⌜al2⌝ ) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last ∧ ⌜al2⌝ ^ = ⌜al0⌝ |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), frag(IOAut(startf, stepf))(⌜restn(# al1, sl)⌝ , ⌜al2⌝ ) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last
Used simplifier rules: fragstar: ⊦ frag*(IOAut(startf, stepf))(σ, β) ↔ frag(IOAut(startf, stepf))(σ, β) ∧ finp(β); ⊦ finp(⌜x⌝ ); (s)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), frag(IOAut(startf, stepf))(⌜restn(# al1, sl)⌝ , ⌜al2⌝ ) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last |
⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ( # ⌜restn(# al1, sl)⌝ = # ⌜al2⌝ + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # ⌜al2⌝ → stepf(⌜restn(# al1, sl)⌝ [n], ⌜al2⌝ [n], ⌜restn(# al1, sl)⌝ [n +1]))) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last
Used terms: ⌜al2⌝ , ⌜restn(# al1, sl)⌝ , stepf, startf
| ⊦ frag(IOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), ( # ⌜restn(# al1, sl)⌝ = # ⌜al2⌝ + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # ⌜al2⌝ → stepf(⌜restn(# al1, sl)⌝ [n], ⌜al2⌝ [n], ⌜restn(# al1, sl)⌝ [n +1]))) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), # al2 + 1 = # sl - # al1 ∧ (n < # al2 → stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1])) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last
Used simplifier rules: ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ m +1 = m + 1; (s) ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s) add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf ⊦ ⌜n⌝ + ⌜m⌝ = ⌜n0⌝ ↔ n + m = n0; (s) n ≤ # x ⊦ # restn(n, x) = # x - n; (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ ¬ m + n < m; (s) ⊦ # x = 0 ↔ x = []; (s) lf-02: ⊦ m < n ∧ m = n0 → n0 < n; (forward) from specification nat-basic f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ m ≤ n ↔ ¬ n < m; (ss) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), # al2 + 1 = # sl - # al1 ∧ (n < # al2 → stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1])) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last |
# sl = n1 + # al1, (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, # al1 ≤ # sl, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), # al2 + 1 = n1 ∧ (n < # al2 → stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1])) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last
Used simplifier rules: ⊦ m ≤ n ↔ ¬ n < m; (ss) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic lf-02: ⊦ m < n ∧ m = n0 → n0 < n; (forward) from specification nat-basic ⊦ # x = 0 ↔ x = []; (s) ⊦ ¬ m + n < m; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic n ≤ m ⊦ n0 = m - n ↔ m = n0 + n; (elim) Used terms: # sl, # al1, n1
| # sl = n1 + # al1, (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, # al1 ≤ # sl, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), # al2 + 1 = n1 ∧ (n < # al2 → stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1])) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, # al1 ≤ # sl, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), (n < # al2 → stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1])) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic eqs: ⊦ m = n + n0 ∧ m = n + n1 → n0 = n1; (forward) from specification nat-basic
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , n0 ≤ # al0, # al1 ≤ # sl, ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last), (n < # al2 → stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1])) ∧ sl[# al1] = restn(# al1, sl)[0] ∧ sl.last = restn(# al1, sl).last |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n < # al2, # al1 ≤ # sl, n0 ≤ # al0, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[# al1] ≠ restn(# al1, sl)[0], # al1 ≤ # sl, n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl.last ≠ restn(# al1, sl).last, # al1 ≤ # sl, n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , n < # al2, # al1 ≤ # sl, n0 ≤ # al0, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al2 ≠ [], n < # al2, # al1 ≤ # sl, n0 ≤ # al0, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ # x = 0 ↔ x = []; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al2 ≠ [], n < # al2, # al1 ≤ # sl, n0 ≤ # al0, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ m + n < # x → restn(n, x)[m] = x[m + n]
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n0 ≤ # al0, # al1 ≤ # sl, ¬ n + # al1 < # sl, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n + # al1 < # sl, n0 ≤ # al0, # al1 ≤ # sl, ¬ stepf(sl[n + # al1], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used terms: n, sl, # al1
| ⊦ m + n < # x → restn(n, x)[m] = x[m + n] |
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n0 ≤ # al0, # al1 ≤ # sl, ¬ n + # al1 < # sl, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, # sl ≤ n + # al1, n0 ≤ # al0, # al1 ≤ # sl, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m ≤ m + n; (s) let: ⊦ n ≤ n0 ∧ n0 ≤ n1 → n ≤ n1; (forward) from specification nat ⊦ m < n ↔ ¬ n ≤ m; (ss)
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, # sl ≤ n + # al1, n0 ≤ # al0, # al1 ≤ # sl, ¬ stepf(restn(# al1, sl)[n], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
Used simplifier rules: ⊦ #(x + y) = # x + # y; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream] ⊦ m + n = m + n0 ↔ n = n0; (s) ⊦ m ≤ m + n; (s) ⊦ m + n ≤ m + n0 ↔ n ≤ n0; (s) fle-01: ⊦ m ≤ n ∧ n < n0 → m < n0; (forward) from specification nat lf-02: ⊦ m < n ∧ m = n0 → n0 < n; (forward) from specification nat-basic ⊦ ¬ m + n < m; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ n ≤ # x → (y = firstn(n, x) ∧ z = restn(n, x) ↔ x = y + z ∧ # y = n); (elim) Used terms: sl, # al1, y, z
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n + # al1 < # sl, n0 ≤ # al0, # al1 ≤ # sl, ¬ stepf(sl[n + # al1], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], sl ≠ [], n < # al2, n + # al1 < # sl, n0 ≤ # al0, # al1 ≤ # sl, ¬ stepf(sl[n + # al1], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(hd(sl), ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: ⊦ x ≠ [] → x[0] = hd(x); (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m < n → ¬ n < m; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) ⊦ m + n < m + n0 ↔ n < n0; (s) ⊦ # x = 0 ↔ x = []; (s) lf-01: ⊦ m < n ∧ n = n0 → m < n0; (forward) from specification nat-basic f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic
| (# al1 + # al2) + 1 = # sl, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], sl ≠ [], n < # al2, n + # al1 < # sl, n0 ≤ # al0, # al1 ≤ # sl, ¬ stepf(sl[n + # al1], al2[n], restn(# al1, sl)[n + 1]), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(hd(sl), ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
(# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl = a + sl0, al2 ≠ [], sl ≠ [], n + # al1 < # sl, n < # al2, # al1 ≤ # sl, n0 ≤ # al0, ¬ stepf(sl[n + # al1], al2[n], restn(# al1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last)
Used simplifier rules: x ≠ [] ⊦ a = hd(x) ∧ y = tl(x) ↔ x = a + y; (elim) Used terms: sl, a, y
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl = a + sl0, al2 ≠ [], sl ≠ [], n + # al1 < # sl, n < # al2, # al1 ≤ # sl, n0 ≤ # al0, ¬ stepf(sl[n + # al1], al2[n], restn(# al1, sl)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
# al1 + # al2 = # sl0, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n0 ≤ # al0, # al1 ≤ # sl0 + 1, ¬ stepf((a ' + sl0)[n + # al1], al2[n], restn(# al1, a ' + sl0)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n1. n1 < # sl0 → stepf((a ' + sl0)[n1], (al1 + al2)[n1], sl0[n1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , (a ' + sl0).last)
Used simplifier rules: ⊦ a + x = a ' + x; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream] c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ (a ' + x)[n + 1] = x[n]; (s) ⊦ m = m0 + n0 ∧ n < n0 → ¬ m < m0 + n; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) ⊦ m +1 = m + 1; (s) ⊦ #(a ' + x) = (# x)+1; (s) ⊦ a ' + x ≠ []; (s) ⊦ m + n = m + n0 ↔ n = n0; (s)
| # al1 + # al2 = # sl0, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n0 ≤ # al0, # al1 ≤ # sl0 + 1, ¬ stepf((a ' + sl0)[n + # al1], al2[n], restn(# al1, a ' + sl0)[n + 1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n1. n1 < # sl0 → stepf((a ' + sl0)[n1], (al1 + al2)[n1], sl0[n1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , (a ' + sl0).last) |
⊦ m + n < # x → restn(n, x)[m] = x[m + n]
# al1 + # al2 = # sl0, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al2 ≠ [], n < # al2, (n + 1) + # al1 < #(a ' + sl0), # al1 ≤ # sl0 + 1, n0 ≤ # al0, ¬ stepf((a ' + sl0)[n + # al1], al2[n], (a ' + sl0)[(n + 1) + # al1]), ∀ n1. n1 < # sl0 → stepf((a ' + sl0)[n1], (al1 + al2)[n1], sl0[n1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , (a ' + sl0).last)
Used simplifier rules: ⊦ #(a ' + x) = (# x)+1; (s) ⊦ m +1 = m + 1; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream] ⊦ m + n < m + n0 ↔ n < n0; (s) ⊦ m = m0 + n0 ∧ n < n0 → m0 + n < m; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: n + 1, a ' + sl0, # al1
| ⊦ m + n < # x → restn(n, x)[m] = x[m + n] |
| # al1 + # al2 = # sl0, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , al2 ≠ [], n < # al2, (n + 1) + # al1 < #(a ' + sl0), # al1 ≤ # sl0 + 1, n0 ≤ # al0, ¬ stepf((a ' + sl0)[n + # al1], al2[n], (a ' + sl0)[(n + 1) + # al1]), ∀ n1. n1 < # sl0 → stepf((a ' + sl0)[n1], (al1 + al2)[n1], sl0[n1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , (a ' + sl0).last) |
# al1 + # al2 = # sl0, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n0 ≤ # al0, # al1 ≤ # sl0 + 1, ¬ stepf((a ' + sl0)[n + # al1], al2[n], sl0[n + # al1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n1. n1 < # sl0 → stepf((a ' + sl0)[n1], (al1 + al2)[n1], sl0[n1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , (a ' + sl0).last)
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[IOstatestream] c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ (a ' + x)[n + 1] = x[n]; (s) ⊦ m = m0 + n0 ∧ n < n0 → m0 + n < m; (s) ⊦ m + n < m + n0 ↔ n < n0; (s) ⊦ m +1 = m + 1; (s) ⊦ #(a ' + x) = (# x)+1; (s)
| # al1 + # al2 = # sl0, ⌜al1⌝ ^ = ⌜action '⌝ , ⌜al2⌝ ^ = ⌜al0⌝ , al2 ≠ [], n < # al2, n0 ≤ # al0, # al1 ≤ # sl0 + 1, ¬ stepf((a ' + sl0)[n + # al1], al2[n], sl0[n + # al1]), ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n1. n1 < # sl0 → stepf((a ' + sl0)[n1], (al1 + al2)[n1], sl0[n1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(a, ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , (a ' + sl0).last) |
Used simplifier rules: ⊦ m = m0 + n0 ∧ n < n0 → m0 + n < m; (s) ⊦ (x + y)[n + # x] = y[n]; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] Used terms: n + # al1
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl[# al1] ≠ restn(# al1, sl)[0], # al1 ≤ # sl, n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ m + n < # x → restn(n, x)[m] = x[m + n]
Used simplifier rules: ⊦ n + 0 = n; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ m ≤ n → (n ≤ m ↔ m = n); (s) ⊦ m = m0 + 1 + n → m ≠ n; (s) Used terms: 0, sl, # al1
| ⊦ m + n < # x → restn(n, x)[m] = x[m + n] |
| (# al1 + # al2) + 1 = # sl, ⌜al2⌝ ^ = ⌜al0⌝ , ⌜al1⌝ ^ = ⌜action '⌝ , sl.last ≠ restn(# al1, sl).last, # al1 ≤ # sl, n0 ≤ # al0, ∀ startf, stepf, s, s2, n. move(IOAut(startf, stepf))(s, ⌜al0⌝ , s2) ∧ n ≤ # al0 → (∃ s1. move(IOAut(startf, stepf))(s, ⌜al0 to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n⌝ , s2)), ∀ n. n < # al1 + # al2 → stepf(sl[n], (al1 + al2)[n], sl[n + 1]) ⊦ ∃ s1. move(IOAut(startf, stepf))(sl[0], ⌜action '⌝ + ⌜al0 to n0⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜al0 from n0⌝ , sl.last) |
⊦ n < # x → restn(n, x).last = x.last
Used simplifier rules: ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ m ≤ n → (n ≤ m ↔ m = n); (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ m = m0 + 1 + n → m ≠ n; (s) Used terms: sl, # al1
| ⊦ n < # x → restn(n, x).last = x.last |
| move(IOAut(startf, stepf))(s, ⌜af⌝ , s2), ¬ # ⌜af⌝ < ⌜n⌝ ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜af⌝ to n, s1) ∧ move(IOAut(startf, stepf))(s1, ⌜af⌝ from n, s2) |
move(IOAut(startf, stepf))(s, ⌜af⌝ , s2) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜af to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜af from n⌝ , s2)
Used simplifier rules: ⊦ ⌜nf⌝ from n = ⌜nf from n⌝ ; (s) ⊦ ⌜nf⌝ to n = ⌜nf to n⌝ ; (s) ⊦ ¬ ∞ < n∞; (s) ⊦ # ⌜nf⌝ = ∞; (s)
| move(IOAut(startf, stepf))(s, ⌜af⌝ , s2) ⊦ ∃ s1. move(IOAut(startf, stepf))(s, ⌜af to n⌝ , s1) ∧ move(IOAut(startf, stepf))(s1, ⌜af from n⌝ , s2) |
⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β)
Used simplifier rules: fragstar: ⊦ frag*(IOAut(startf, stepf))(σ, β) ↔ frag(IOAut(startf, stepf))(σ, β) ∧ finp(β); stream-fin-forward: ⊦ finp(σ) → (∃ x. ⌜x⌝ = σ); (forward) from specification stream-basic[actionstream] ⊦ ⌜al⌝ ^ ≠ ⌜af⌝ ; (s) Used terms: s2, ⌜af⌝ , s, stepf, startf
| ⊦ move(IOAut(startf, stepf))(s1, β, s2) ↔ (∃ α, sl. frag*(IOAut(startf, stepf))(⌜sl⌝ , α) ∧ s1 = sl[0] ∧ s2 = sl.last ∧ α ^ = β) |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.