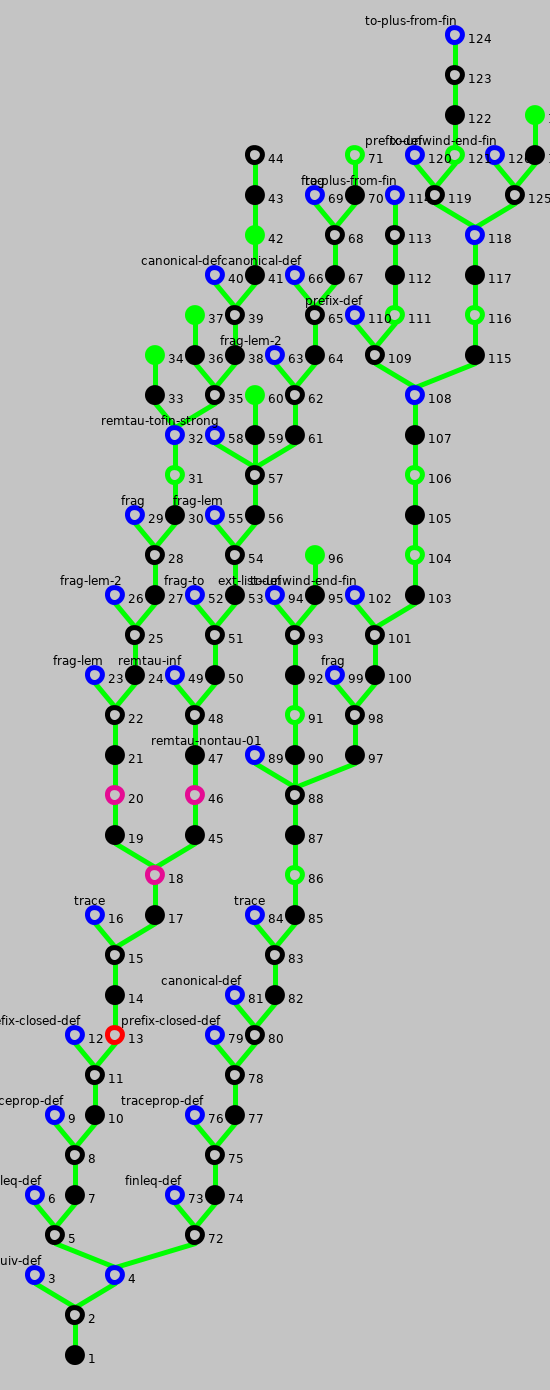
Proof Tree for lemma-2-8-2 (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| traceprop(tP) ⊦ albeh(can(tP)) ≡*T tP |
traceprop(tP), ¬ albeh(can(tP)) ≡*T tP ⊦
| traceprop(tP), ¬ albeh(can(tP)) ≡*T tP ⊦ |
⊦ tP ≡*T tQ ↔ tP ≤*T tQ ∧ tQ ≤*T tP
traceprop(tP), ¬ albeh(can(tP)) ≤*T tP ∨ ¬ tP ≤*T albeh(can(tP)) ⊦
Used terms: tP, albeh(can(tP))
| ⊦ tP ≡*T tQ ↔ tP ≤*T tQ ∧ tQ ≤*T tP |
| traceprop(tP), ¬ albeh(can(tP)) ≤*T tP ∨ ¬ tP ≤*T albeh(can(tP)) ⊦ |
traceprop(tP), ¬ albeh(can(tP)) ≤*T tP ⊦
traceprop(tP), ¬ tP ≤*T albeh(can(tP)) ⊦
| traceprop(tP), ¬ albeh(can(tP)) ≤*T tP ⊦ |
⊦ tP ≤*T tQ ↔ (∀ α. finp(α) ∧ tP(α) → tQ(α))
traceprop(tP), ∃ α. ¬(finp(α) ∧ albeh(can(tP))(α) → tP(α)) ⊦
Used terms: tP, albeh(can(tP))
| ⊦ tP ≤*T tQ ↔ (∀ α. finp(α) ∧ tP(α) → tQ(α)) |
| traceprop(tP), ∃ α. ¬(finp(α) ∧ albeh(can(tP))(α) → tP(α)) ⊦ |
albeh(can(tP))(⌜al⌝ ), traceprop(tP), ¬ tP(⌜al⌝ ) ⊦
Used simplifier rules: ⊦ finp(⌜x⌝ ); (s) stream-fin-forward: ⊦ finp(σ) → (∃ x. ⌜x⌝ = σ); (forward) from specification stream-basic[actionstream]
| albeh(can(tP))(⌜al⌝ ), traceprop(tP), ¬ tP(⌜al⌝ ) ⊦ |
⊦ traceprop(tP) ↔ (∀ α. tP(α) → ext(α)) ∧ (∃ α. tP(α)) ∧ prefix-closed(tP)
albeh(can(tP))(⌜al⌝ ), prefix-closed(tP), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∃ α. tP(α) ⊦
Used terms: tP
| ⊦ traceprop(tP) ↔ (∀ α. tP(α) → ext(α)) ∧ (∃ α. tP(α)) ∧ prefix-closed(tP) |
| albeh(can(tP))(⌜al⌝ ), prefix-closed(tP), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∃ α. tP(α) ⊦ |
albeh(can(tP))(⌜al⌝ ), prefix-closed(tP), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α) ⊦
| albeh(can(tP))(⌜al⌝ ), prefix-closed(tP), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α) ⊦ |
⊦ prefix-closed(tP) ↔ (∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2))
albeh(can(tP))(⌜al⌝ ), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used terms: tP
| ⊦ prefix-closed(tP) ↔ (∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2)) |
| albeh(can(tP))(⌜al⌝ ), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), albeh(can(tP))(⌜al⌝ ), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ALIOAutomaton freely generated by ALIOAut;;
| ALIOAut(alstartf, alstepf) = can(tP), albeh(can(tP))(⌜al⌝ ), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), altrace(ALIOAut(alstartf, alstepf))(⌜al⌝ ), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ⊦ albeh(ALIOAut(startf, stepf))(α) ↔ altrace(ALIOAut(startf, stepf))(α); (s)
| ALIOAut(alstartf, alstepf) = can(tP), altrace(ALIOAut(alstartf, alstepf))(⌜al⌝ ), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
⊦ altrace(ALIOAut(startf, stepf))(α) ↔ (∃ σ, β. α = β ^ ∧ alexec(ALIOAut(startf, stepf))(σ, β))
ALIOAut(alstartf, alstepf) = can(tP), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∃ alσ, β. ⌜al⌝ = β ^ ∧ alexec(ALIOAut(alstartf, alstepf))(alσ, β) ⊦
Used terms: ⌜al⌝ , alstepf, alstartf
| ⊦ altrace(ALIOAut(startf, stepf))(α) ↔ (∃ σ, β. α = β ^ ∧ alexec(ALIOAut(startf, stepf))(σ, β)) |
| ALIOAut(alstartf, alstepf) = can(tP), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∃ alσ, β. ⌜al⌝ = β ^ ∧ alexec(ALIOAut(alstartf, alstepf))(alσ, β) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = α0 ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, α0), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ⊦ alexec(ALIOAut(startf, stepf))(σ, β) ↔ alfrag(ALIOAut(startf, stepf))(σ, β) ∧ startf(σ[0]); (s)
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = α0 ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, α0), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), α0 = ⌜al0⌝ , ⌜al⌝ = α0 ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, α0), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
ALIOAut(alstartf, alstepf) = can(tP), α0 = ⌜af⌝ , ⌜al⌝ = α0 ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, α0), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: actionstream freely generated by ⌜ ⌝, ⌜ ⌝;;
| ALIOAut(alstartf, alstepf) = can(tP), α0 = ⌜al0⌝ , ⌜al⌝ = α0 ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, α0), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜al0⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜al0⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), alσ = ⌜alli⌝ , ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜al0⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: actionliststream freely generated by ⌜ ⌝, ⌜ ⌝;; ⊦ ⌜nf⌝ [n] = nf(n); (s) ⊦ ¬ alfrag(ALIOAut(startf, stepf))(⌜sf⌝ , ⌜al⌝ ); (s)
| ALIOAut(alstartf, alstepf) = can(tP), alσ = ⌜alli⌝ , ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜al0⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ⊦ ⌜x⌝ [n] = x[n]; (s)
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ), n < # alli ⊦ alli[n] = alli[0] + (al to n)
ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + (al0 to # al0), ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: ⊦ alfrag(ALIOAut(startf, stepf))(⌜sl⌝ , ⌜al⌝ ) → (# al < # sl ↔ true); (ss) Used terms: tP, alli, al0, # al0
| alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ), n < # alli ⊦ alli[n] = alli[0] + (al to n) |
| ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + (al0 to # al0), ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ⊦ x to # x = x; (s)
| ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ) ⊦ ⌜al⌝ ^ = ⌜al⌝
ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used terms: tP, alli, al0
| alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ) ⊦ ⌜al⌝ ^ = ⌜al⌝ |
| ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , ⌜al⌝ = ⌜al0⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ⊦ ⌜x⌝ = ⌜x0⌝ ↔ x = x0; (s)
| ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alfrag(ALIOAut(alstartf, alstepf))(⌜alli⌝ , ⌜al0⌝ ), alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
⊦ alfrag(ALIOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
# ⌜alli⌝ = # ⌜al0⌝ + ⌜1⌝ , ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ n. ⌜n⌝ < # ⌜al0⌝ → alstepf(⌜alli⌝ [n], ⌜al0⌝ [n], ⌜alli⌝ [n +1]) ⊦
Used terms: ⌜al0⌝ , ⌜alli⌝ , alstepf, alstartf
| ⊦ alfrag(ALIOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
| # ⌜alli⌝ = # ⌜al0⌝ + ⌜1⌝ , ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ n. ⌜n⌝ < # ⌜al0⌝ → alstepf(⌜alli⌝ [n], ⌜al0⌝ [n], ⌜alli⌝ [n +1]) ⊦ |
# al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ n. n < # al0 → alstepf(alli[n], al0[n], alli[n + 1]) ⊦
Used simplifier rules: ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ m +1 = m + 1; (s) ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s) add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf ⊦ ⌜n⌝ + ⌜m⌝ = ⌜n0⌝ ↔ n + m = n0; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
| # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ n. n < # al0 → alstepf(alli[n], al0[n], alli[n + 1]) ⊦ |
# al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), # al0 - 1 < # al0 → alstepf(alli[# al0 - 1], al0[# al0 - 1], alli[(# al0 - 1) + 1]), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used terms: # al0 - 1
| # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ tP(⌜al0⌝ ), # al0 - 1 < # al0 → alstepf(alli[# al0 - 1], al0[# al0 - 1], alli[(# al0 - 1) + 1]), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
# al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ # al0 - 1 < # al0, ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
# al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), alstepf(alli[# al0 - 1], al0[# al0 - 1], alli[(# al0 - 1) + 1]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
| # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), tP(α), ¬ # al0 - 1 < # al0, ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), 1 = # alli, alstartf(alli[0]), tP(α), ¬ tP([]), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: ⊦ ⌜[]⌝ = []; (s) ⊦ 0 ≤ m; (s) ⊦ # [] = 0; (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ x + [] = x; (s) ⊦ [] ^ = []; (s) ⊦ # x = 0 ↔ x = []; (s) leprf: ⊦ m ≤ m - 1 → m = 0; (forward) from specification nat ⊦ m < n ↔ ¬ n ≤ m; (ss)
| ALIOAut(alstartf, alstepf) = can(tP), 1 = # alli, alstartf(alli[0]), tP(α), ¬ tP([]), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
Used simplifier rules: ⊦ [] ≤ σ; (s) Used terms: α, []
| # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), alstepf(alli[# al0 - 1], al0[# al0 - 1], alli[(# al0 - 1) + 1]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
# al0 = 0, # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), alstepf(alli[# al0 - 1], al0[# al0 - 1], alli[(# al0 - 1) + 1]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
# al0 = n0 + 1, # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , # al0 ≠ 0, alstartf(alli[0]), alstepf(alli[n0], al0[n0], alli[n0 + 1]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: n ≠ 0 ⊦ m = n - 1 ↔ n = m + 1; (elim) Used terms: # al0, m
| # al0 = 0, # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , alstartf(alli[0]), alstepf(alli[# al0 - 1], al0[# al0 - 1], alli[(# al0 - 1) + 1]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), 1 = # alli, alstartf(alli[0]), alstepf(alli[0 - 1], [][0 - 1], alli[(0 - 1) + 1]), tP(α), ¬ tP([]), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: ⊦ ⌜[]⌝ = []; (s) ⊦ # [] = 0; (s) ⊦ [] ^ = []; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ x + [] = x; (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ # x = 0 ↔ x = []; (s)
| ALIOAut(alstartf, alstepf) = can(tP), 1 = # alli, alstartf(alli[0]), alstepf(alli[0 - 1], [][0 - 1], alli[(0 - 1) + 1]), tP(α), ¬ tP([]), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
Used simplifier rules: ⊦ [] ≤ σ; (s) Used terms: α, []
| # al0 = n0 + 1, # al0 + 1 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[# al0] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , # al0 ≠ 0, alstartf(alli[0]), alstepf(alli[n0], al0[n0], alli[n0 + 1]), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
# al0 = n0 + 1, 2 + n0 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[n0 + 1] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , al0 ≠ [], alstartf(alli[0]), alstepf(alli[n0], al0[n0], alli[0] + al0), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ # x = 0 ↔ x = []; (s)
| # al0 = n0 + 1, 2 + n0 = # alli, ALIOAut(alstartf, alstepf) = can(tP), alli[n0 + 1] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , al0 ≠ [], alstartf(alli[0]), alstepf(alli[n0], al0[n0], alli[0] + al0), tP(α), ¬ tP(⌜al0⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
⊦ can(tP) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ ))
# al0 = n0 + 1, 2 + n0 = # alli, ALIOAut(alstartf, alstepf) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )), alli[n0 + 1] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , al0 ≠ [], alstartf(alli[0]), alstepf(alli[n0], al0[n0], alli[0] + al0), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used terms: tP
| ⊦ can(tP) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )) |
| # al0 = n0 + 1, 2 + n0 = # alli, ALIOAut(alstartf, alstepf) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )), alli[n0 + 1] = alli[0] + al0, ⌜al0⌝ ^ = ⌜al0⌝ , al0 ≠ [], alstartf(alli[0]), alstepf(alli[n0], al0[n0], alli[0] + al0), tP(α), ¬ tP(⌜al0⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
# alli[n0 + 1] = n0 + 1, 2 + n0 = # alli, alli[n0 + 1] = alli[n0] + alli[n0 + 1][n0] ', alli[0] = [], ⌜alli[n0 + 1]⌝ ^ = ⌜alli[n0 + 1]⌝ , alli[n0 + 1] ≠ [], tP(⌜alli[n0]⌝ ), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ), tP(α), alli[n0 + 1][n0] ∈ alli[n0 + 1], ¬ tP(⌜alli[n0 + 1]⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] in-15: ⊦ x + a ' = y → a ∈ y; (forward) from specification list[actionstream] ⊦ [] + x = x; (s) n < # al ⊦ α ^ = ⌜al⌝ → (al[n] = τ ↔ false); (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ ¬ n < n; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) ⊦ ALIOAut(startf, stepf) = ALIOAut(startf0, stepf0) ↔ startf = startf0 ∧ stepf = stepf0; (ws) ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s)
| # alli[n0 + 1] = n0 + 1, 2 + n0 = # alli, alli[n0 + 1] = alli[n0] + alli[n0 + 1][n0] ', alli[0] = [], ⌜alli[n0 + 1]⌝ ^ = ⌜alli[n0 + 1]⌝ , alli[n0 + 1] ≠ [], tP(⌜alli[n0]⌝ ), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ), tP(α), alli[n0 + 1][n0] ∈ alli[n0 + 1], ¬ tP(⌜alli[n0 + 1]⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
# alli[n0 + 1] = n0 + 1, 2 + n0 = # alli, alli[0] = [], alli[n0 + 1] = alli[n0] + alli[n0 + 1][n0] ', ⌜alli[n0 + 1]⌝ ^ = ⌜alli[n0 + 1]⌝ , alli[n0 + 1] ≠ [], tP(α), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ), tP(⌜alli[n0]⌝ ), alli[n0 + 1][n0] ∈ alli[n0 + 1], ¬ tP(⌜alli[n0 + 1]⌝ ), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ) ∧ ⌜alli[n0] + alli[n0 + 1][n0] '⌝ ≤ ⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ → tP(⌜alli[n0] + alli[n0 + 1][n0] '⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used terms: ⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ , ⌜alli[n0] + alli[n0 + 1][n0] '⌝
| # alli[n0 + 1] = n0 + 1, 2 + n0 = # alli, alli[0] = [], alli[n0 + 1] = alli[n0] + alli[n0 + 1][n0] ', ⌜alli[n0 + 1]⌝ ^ = ⌜alli[n0 + 1]⌝ , alli[n0 + 1] ≠ [], tP(α), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ), tP(⌜alli[n0]⌝ ), alli[n0 + 1][n0] ∈ alli[n0 + 1], ¬ tP(⌜alli[n0 + 1]⌝ ), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ) ∧ ⌜alli[n0] + alli[n0 + 1][n0] '⌝ ≤ ⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ → tP(⌜alli[n0] + alli[n0 + 1][n0] '⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
# alli[n0 + 1] = n0 + 1, 2 + n0 = # alli, alli[n0 + 1] = alli[n0] + alli[n0 + 1][n0] ', alli[0] = [], ⌜alli[n0 + 1]⌝ ^ = ⌜alli[n0 + 1]⌝ , alli[n0 + 1] ≠ [], tP(⌜alli[n0]⌝ ), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ), tP(α), alli[n0 + 1][n0] ∈ alli[n0 + 1], ¬ tP(⌜alli[n0 + 1]⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s) append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[actionstream] ⊦ σ ≤ σ; (s) ⊦ ⌜x⌝ + σ1 ≤ ⌜x⌝ + σ2 ↔ σ1 ≤ σ2; (s)
| # alli[n0 + 1] = n0 + 1, 2 + n0 = # alli, alli[n0 + 1] = alli[n0] + alli[n0 + 1][n0] ', alli[0] = [], ⌜alli[n0 + 1]⌝ ^ = ⌜alli[n0 + 1]⌝ , alli[n0 + 1] ≠ [], tP(⌜alli[n0]⌝ ), tP(⌜alli[n0]⌝ + ⌜alli[n0 + 1][n0] '⌝ ), tP(α), alli[n0 + 1][n0] ∈ alli[n0 + 1], ¬ tP(⌜alli[n0 + 1]⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
Used simplifier rules: ⊦ (⌜al⌝ + α2)^ = ⌜al⌝ ^ + α2 ^; (s) append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[actionstream] ⊦ #(x + y) = # x + # y; (s) ⊦ # a ' = 0 +1; (s) ⊦ m + n = m + n0 ↔ n = n0; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ x + a ' ≠ []; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) ⊦ a ∈ b ' ↔ a = b; (s) ⊦ n = # x → (x + a ')[n] = a; (s) ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream]
| ALIOAut(alstartf, alstepf) = can(tP), α0 = ⌜af⌝ , ⌜al⌝ = α0 ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, α0), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜af⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜af⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), alσ = ⌜f_n->actionlist⌝ , ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜af⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: actionliststream freely generated by ⌜ ⌝, ⌜ ⌝;; ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ ¬ alfrag(ALIOAut(startf, stepf))(⌜sl⌝ , ⌜af⌝ ); (s)
| ALIOAut(alstartf, alstepf) = can(tP), alσ = ⌜f_n->actionlist⌝ , ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(alσ, ⌜af⌝ ), alstartf(alσ[0]), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ⊦ ⌜nf⌝ [n] = nf(n); (s)
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
⊦ finp(⌜af⌝ ^) ↔ (∃ n. ∀ m. n ≤ m → af(m) = τ)
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), finp(⌜af⌝ ^) ↔ (∃ n. ∀ m. n ≤ m → af(m) = τ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used terms: af
| ⊦ finp(⌜af⌝ ^) ↔ (∃ n. ∀ m. n ≤ m → af(m) = τ) |
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), finp(⌜af⌝ ^) ↔ (∃ n. ∀ m. n ≤ m → af(m) = τ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦
Used simplifier rules: ⊦ finp(⌜x⌝ ); (s)
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦ |
⊦ alfrag(ALIOAut(startf, stepf))(σ, α) ∧ ¬ # α < ⌜n⌝ → alfrag*(ALIOAut(startf, stepf))(σ to n + 1, α to n)
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ) ∧ ¬ # ⌜af⌝ < ⌜n⌝ → alfrag*(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ to n + 1, ⌜af⌝ to n), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used terms: alstartf, alstepf, ⌜f_n->actionlist⌝ , ⌜af⌝ , n
| ⊦ alfrag(ALIOAut(startf, stepf))(σ, α) ∧ ¬ # α < ⌜n⌝ → alfrag*(ALIOAut(startf, stepf))(σ to n + 1, α to n) |
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ) ∧ ¬ # ⌜af⌝ < ⌜n⌝ → alfrag*(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ to n + 1, ⌜af⌝ to n), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦
Used simplifier rules: ⊦ finp(⌜nf to n⌝ ); (s) ⊦ alfrag*(ALIOAut(startf, stepf))(σ, β) ↔ alfrag(ALIOAut(startf, stepf))(σ, β) ∧ finp(β); (s) ⊦ ⌜nf⌝ to n = ⌜nf to n⌝ ; (s) ⊦ ⌜nf⌝ to n = ⌜nf to n⌝ ; (s) ⊦ ¬ ∞ < n∞; (s) ⊦ # ⌜nf⌝ = ∞; (s)
| ALIOAut(alstartf, alstepf) = can(tP), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦ |
alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ), n < # alli ⊦ alli[n] = alli[0] + (al to n)
ALIOAut(alstartf, alstepf) = can(tP), (f_n->actionlist to n + 1)[n] = (f_n->actionlist to n + 1)[0] + ((af to n) to n), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: ⊦ #(nf to n) = n; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) ⊦ ¬ n < n; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: tP, f_n->actionlist to n + 1, af to n, n
| alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ), n < # alli ⊦ alli[n] = alli[0] + (al to n) |
| ALIOAut(alstartf, alstepf) = can(tP), (f_n->actionlist to n + 1)[n] = (f_n->actionlist to n + 1)[0] + ((af to n) to n), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦
Used simplifier rules: ⊦ (nf to n) to n = nf to n; (s) m < n ⊦ (nf to n)[m] = nf(m); (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m + 1 ≠ 0; (s) ⊦ 0 < m ↔ m ≠ 0; (s) ⊦ ¬ n < n; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s)
| ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦ |
¬ # β < ⌜n⌝ , ∀ m. n ≤ m ∧ ⌜m⌝ < # β → β[m] = τ ⊦ β ^ = (β to n)^
ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ ¬ # ⌜af⌝ < ⌜n⌝ ∧ (∀ m. n ≤ m ∧ ⌜m⌝ < # ⌜af⌝ → ⌜af⌝ [m] = τ)
ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = (⌜af⌝ to n)^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ # ⌜af⌝ < ⌜n⌝ , ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ m. n ≤ m ∧ ⌜m⌝ < # ⌜af⌝ → ⌜af⌝ [m] = τ ⊦
Used terms: ⌜af⌝ , n
| ¬ # β < ⌜n⌝ , ∀ m. n ≤ m ∧ ⌜m⌝ < # β → β[m] = τ ⊦ β ^ = (β to n)^ |
| ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ ¬ # ⌜af⌝ < ⌜n⌝ ∧ (∀ m. n ≤ m ∧ ⌜m⌝ < # ⌜af⌝ → ⌜af⌝ [m] = τ) |
ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af⌝ ^, af(n0) ≠ τ, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), n ≤ n0, ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦
Used simplifier rules: ⊦ ⌜nf⌝ [n] = nf(n); (s) ⊦ ⌜m⌝ < ∞; (s) ⊦ # ⌜nf⌝ = ∞; (s) ⊦ ¬ ∞ < n∞; (s)
| ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af⌝ ^, af(n0) ≠ τ, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), n ≤ n0, ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦ |
Used terms: n0
| ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = (⌜af⌝ to n)^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ # ⌜af⌝ < ⌜n⌝ , ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ m. n ≤ m ∧ ⌜m⌝ < # ⌜af⌝ → ⌜af⌝ [m] = τ ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af to n⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦
Used simplifier rules: ⊦ ⌜nf⌝ [n] = nf(n); (s) ⊦ ⌜m⌝ < ∞; (s) ⊦ # ⌜nf⌝ = ∞; (s) ⊦ ¬ ∞ < n∞; (s) ⊦ ⌜nf⌝ to n = ⌜nf to n⌝ ; (s)
| ALIOAut(alstartf, alstepf) = can(tP), f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af to n⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦ |
alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ) ⊦ ⌜al⌝ ^ = ⌜al⌝
ALIOAut(alstartf, alstepf) = can(tP), ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af to n⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used terms: tP, f_n->actionlist to n + 1, af to n
| alfrag(can(tP))(⌜alli⌝ , ⌜al⌝ ) ⊦ ⌜al⌝ ^ = ⌜al⌝ |
| ALIOAut(alstartf, alstepf) = can(tP), ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = f_n->actionlist(0) + (af to n), ⌜al⌝ = ⌜af to n⌝ ^, alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜al⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
ALIOAut(alstartf, alstepf) = can(tP), ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = f_n->actionlist(0) + (af to n), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜af to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦
Used simplifier rules: ⊦ ⌜x⌝ = ⌜x0⌝ ↔ x = x0; (s)
| ALIOAut(alstartf, alstepf) = can(tP), ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = f_n->actionlist(0) + (af to n), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜af to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦ |
⊦ can(tP) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ ))
ALIOAut(alstartf, alstepf) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )), ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = f_n->actionlist(0) + (af to n), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜af to n⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used terms: tP
| ⊦ can(tP) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )) |
| ALIOAut(alstartf, alstepf) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )), ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = f_n->actionlist(0) + (af to n), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), alfrag(ALIOAut(alstartf, alstepf))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alstartf(f_n->actionlist(0)), tP(α), ¬ tP(⌜af to n⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(0) = [], f_n->actionlist(n) = af to n, alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), tP(α), ¬ tP(⌜af to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ [] + x = x; (s) ⊦ ALIOAut(startf, stepf) = ALIOAut(startf0, stepf0) ↔ startf = startf0 ∧ stepf = stepf0; (ws) ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s)
| ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(0) = [], f_n->actionlist(n) = af to n, alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist⌝ , ⌜af⌝ ), alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), tP(α), ¬ tP(⌜af to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ ⊦ |
⊦ alfrag(ALIOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
# ⌜f_n->actionlist⌝ = # ⌜af⌝ + ⌜1⌝ , ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = af to n, f_n->actionlist(0) = [], alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), tP(α), ¬ tP(⌜af to n⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ n. ⌜n⌝ < # ⌜af⌝ → ⌜f_n->actionlist⌝ [n +1] = ⌜f_n->actionlist⌝ [n] + ⌜af⌝ [n] ' ∧ ⌜af⌝ [n] ≠ τ ∧ tP(⌜⌜f_n->actionlist⌝ [n]⌝ ) ∧ tP(⌜⌜f_n->actionlist⌝ [n]⌝ + ⌜⌜af⌝ [n] '⌝ ) ⊦
Used terms: ⌜af⌝ , ⌜f_n->actionlist⌝ , λ al, a, al0. al0 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ ), λ al. al = []
| ⊦ alfrag(ALIOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
| # ⌜f_n->actionlist⌝ = # ⌜af⌝ + ⌜1⌝ , ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(n) = af to n, f_n->actionlist(0) = [], alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), tP(α), ¬ tP(⌜af to n⌝ ), ∀ m. n ≤ m → af(m) = τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ n. ⌜n⌝ < # ⌜af⌝ → ⌜f_n->actionlist⌝ [n +1] = ⌜f_n->actionlist⌝ [n] + ⌜af⌝ [n] ' ∧ ⌜af⌝ [n] ≠ τ ∧ tP(⌜⌜f_n->actionlist⌝ [n]⌝ ) ∧ tP(⌜⌜f_n->actionlist⌝ [n]⌝ + ⌜⌜af⌝ [n] '⌝ ) ⊦ |
⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(0) = [], f_n->actionlist(n) = af to n, alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), tP(α), ¬ tP(⌜af to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ, ∀ n0. f_n->actionlist(n0 + 1) = f_n->actionlist(n0) + af(n0) ' ∧ af(n0) ≠ τ ∧ tP(⌜f_n->actionlist(n0)⌝ ) ∧ tP(⌜f_n->actionlist(n0)⌝ + ⌜af(n0) '⌝ ) ⊦
Used simplifier rules: ⊦ ⌜nf⌝ [n] = nf(n); (s) ⊦ ⌜nf⌝ [n] = nf(n); (s) ⊦ m +1 = m + 1; (s) ⊦ ⌜m⌝ < ∞; (s) ⊦ # ⌜nf⌝ = ∞; (s) add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf ⊦ ⌜m⌝ + ∞ = ∞; (s) ⊦ # ⌜nf⌝ = ∞; (s)
| ⌜af to n⌝ ^ = ⌜af to n⌝ , f_n->actionlist(0) = [], f_n->actionlist(n) = af to n, alfrag(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al⌝ + ⌜a '⌝ )))(⌜f_n->actionlist to n + 1⌝ , ⌜af to n⌝ ), tP(α), ¬ tP(⌜af to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. n ≤ m → af(m) = τ, ∀ n0. f_n->actionlist(n0 + 1) = f_n->actionlist(n0) + af(n0) ' ∧ af(n0) ≠ τ ∧ tP(⌜f_n->actionlist(n0)⌝ ) ∧ tP(⌜f_n->actionlist(n0)⌝ + ⌜af(n0) '⌝ ) ⊦ |
Used simplifier rules: in-15: ⊦ x + a ' = y → a ∈ y; (forward) from specification list[actionstream] a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] Used terms: n
| traceprop(tP), ¬ tP ≤*T albeh(can(tP)) ⊦ |
⊦ tP ≤*T tQ ↔ (∀ α. finp(α) ∧ tP(α) → tQ(α))
traceprop(tP), ∃ α. ¬(finp(α) ∧ tP(α) → albeh(can(tP))(α)) ⊦
Used terms: albeh(can(tP)), tP
| ⊦ tP ≤*T tQ ↔ (∀ α. finp(α) ∧ tP(α) → tQ(α)) |
| traceprop(tP), ∃ α. ¬(finp(α) ∧ tP(α) → albeh(can(tP))(α)) ⊦ |
tP(⌜al⌝ ), traceprop(tP), ¬ albeh(can(tP))(⌜al⌝ ) ⊦
Used simplifier rules: ⊦ finp(⌜x⌝ ); (s) stream-fin-forward: ⊦ finp(σ) → (∃ x. ⌜x⌝ = σ); (forward) from specification stream-basic[actionstream]
| tP(⌜al⌝ ), traceprop(tP), ¬ albeh(can(tP))(⌜al⌝ ) ⊦ |
⊦ traceprop(tP) ↔ (∀ α. tP(α) → ext(α)) ∧ (∃ α. tP(α)) ∧ prefix-closed(tP)
prefix-closed(tP), tP(⌜al⌝ ), ¬ albeh(can(tP))(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∃ α. tP(α) ⊦
Used terms: tP
| ⊦ traceprop(tP) ↔ (∀ α. tP(α) → ext(α)) ∧ (∃ α. tP(α)) ∧ prefix-closed(tP) |
| prefix-closed(tP), tP(⌜al⌝ ), ¬ albeh(can(tP))(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∃ α. tP(α) ⊦ |
prefix-closed(tP), tP(α), tP(⌜al⌝ ), ¬ albeh(can(tP))(⌜al⌝ ), ∀ α. tP(α) → ext(α) ⊦
| prefix-closed(tP), tP(α), tP(⌜al⌝ ), ¬ albeh(can(tP))(⌜al⌝ ), ∀ α. tP(α) → ext(α) ⊦ |
⊦ prefix-closed(tP) ↔ (∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2))
tP(⌜al⌝ ), tP(α), ¬ albeh(can(tP))(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used terms: tP
| ⊦ prefix-closed(tP) ↔ (∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2)) |
| tP(⌜al⌝ ), tP(α), ¬ albeh(can(tP))(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
⊦ can(tP) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ ))
tP(α), tP(⌜al⌝ ), ¬ albeh(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )))(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used terms: tP
| ⊦ can(tP) = ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )) |
| tP(α), tP(⌜al⌝ ), ¬ albeh(ALIOAut(λ al. al = [], λ al, a, al1. al1 = al + a ' ∧ a ≠ τ ∧ tP(⌜al⌝ ) ∧ tP(⌜al1⌝ )))(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
tP(⌜al⌝ ), tP(α), ¬ altrace(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: ⊦ albeh(ALIOAut(startf, stepf))(α) ↔ altrace(ALIOAut(startf, stepf))(α); (s) a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s)
| tP(⌜al⌝ ), tP(α), ¬ altrace(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
⊦ altrace(ALIOAut(startf, stepf))(α) ↔ (∃ σ, β. α = β ^ ∧ alexec(ALIOAut(startf, stepf))(σ, β))
tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ alσ, β. ¬(⌜al⌝ = β ^ ∧ alexec(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(alσ, β)) ⊦
Used terms: ⌜al⌝ , λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ ), λ al. al = []
| ⊦ altrace(ALIOAut(startf, stepf))(α) ↔ (∃ σ, β. α = β ^ ∧ alexec(ALIOAut(startf, stepf))(σ, β)) |
| tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ alσ, β. ¬(⌜al⌝ = β ^ ∧ alexec(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(alσ, β)) ⊦ |
tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ alσ, β. ⌜al⌝ ≠ β ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(alσ, β) ∨ alσ[0] ≠ [] ⊦
Used simplifier rules: ⊦ alexec(ALIOAut(startf, stepf))(σ, β) ↔ alfrag(ALIOAut(startf, stepf))(σ, β) ∧ startf(σ[0]); (s)
| tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ alσ, β. ⌜al⌝ ≠ β ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(alσ, β) ∨ alσ[0] ≠ [] ⊦ |
tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ⌜al⌝ ≠ ⌜al⌝ ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜λ m. al to m⌝ to # al + 1, ⌜al⌝ ) ∨ (⌜λ m. al to m⌝ to # al + 1)[0] ≠ [] ⊦
Used terms: ⌜λ m. al to m⌝ to # al + 1, ⌜al⌝
| tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ⌜al⌝ ≠ ⌜al⌝ ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜λ m. al to m⌝ to # al + 1, ⌜al⌝ ) ∨ (⌜λ m. al to m⌝ to # al + 1)[0] ≠ [] ⊦ |
tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ⌜al⌝ ≠ ⌜al⌝ ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ) ⊦
Used simplifier rules: ⊦ x to 0 = []; (s) m < n ⊦ (nf to n)[m] = nf(m); (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m + 1 ≠ 0; (s) ⊦ 0 < m ↔ m ≠ 0; (s) ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ ⌜nf⌝ to n = ⌜nf to n⌝ ; (s)
| tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ⌜al⌝ ≠ ⌜al⌝ ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ) ⊦ |
∀ m. ⌜m⌝ < # α → α[m] ≠ τ ⊦ α ^ = α
tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ⌜al⌝ ≠ ⌜al⌝ ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ) ⊦ ∀ m. ⌜m⌝ < # ⌜al⌝ → ⌜al⌝ [m] ≠ τ
tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ m. ⌜m⌝ < # ⌜al⌝ → ⌜al⌝ [m] ≠ τ, ⌜al⌝ ≠ ⌜al⌝ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ) ⊦
Used terms: ⌜al⌝
| ∀ m. ⌜m⌝ < # α → α[m] ≠ τ ⊦ α ^ = α |
| tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ⌜al⌝ ≠ ⌜al⌝ ^ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ) ⊦ ∀ m. ⌜m⌝ < # ⌜al⌝ → ⌜al⌝ [m] ≠ τ |
al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦
Used simplifier rules: n < # al ⊦ α ^ = ⌜al⌝ → (al[n] = τ ↔ false); (s) ⊦ # x = 0 ↔ x = []; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s) ⊦ ⌜x⌝ [n] = x[n]; (s)
| al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ |
al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(⌜al⌝ ), tP(α), tP(⌜al⌝ ) → ext(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used terms: ⌜al⌝
| al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(⌜al⌝ ), tP(α), tP(⌜al⌝ ) → ext(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦
Used simplifier rules: ⊦ ext(⌜al⌝ ) ↔ ext(al); (s)
| al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2) ⊦ |
⊦ ext(al) ↔ (∀ n. n < # al → ext(al[n]))
al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(⌜al⌝ ), tP(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ n. n < # al → ext(al[n]) ⊦
Used terms: al
| ⊦ ext(al) ↔ (∀ n. n < # al → ext(al[n])) |
| al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(⌜al⌝ ), tP(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ n. n < # al → ext(al[n]) ⊦ |
al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ n. n < # al → al[n] ≠ τ ⊦
Used simplifier rules: ⊦ ext(a) ↔ a ≠ τ; (s)
| al[m] = τ, al ≠ [], ⌜al⌝ ≠ ⌜al⌝ ^, m < # al, tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ n. n < # al → al[n] ≠ τ ⊦ |
Used terms: m
| tP(α), tP(⌜al⌝ ), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ m. ⌜m⌝ < # ⌜al⌝ → ⌜al⌝ [m] ≠ τ, ⌜al⌝ ≠ ⌜al⌝ ∨ ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ) ⊦ |
tP(⌜al⌝ ), tP(α), ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦
Used simplifier rules: ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s)
| tP(⌜al⌝ ), tP(α), ¬ alfrag(ALIOAut(λ al. al = [], λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ )))(⌜(λ m. al to m) to # al + 1⌝ , ⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ |
⊦ alfrag(ALIOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1]))
tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), # ⌜(λ m. al to m) to # al + 1⌝ ≠ # ⌜al⌝ + ⌜1⌝ ∨ (∃ n. ¬ ( ⌜n⌝ < # ⌜al⌝ → ⌜(λ m. al to m) to # al + 1⌝ [n +1] = ⌜(λ m. al to m) to # al + 1⌝ [n] + ⌜al⌝ [n] ' ∧ ⌜al⌝ [n] ≠ τ ∧ tP(⌜⌜(λ m. al to m) to # al + 1⌝ [n]⌝ ) ∧ tP(⌜⌜(λ m. al to m) to # al + 1⌝ [n]⌝ + ⌜⌜al⌝ [n] '⌝ ))) ⊦
Used terms: ⌜al⌝ , ⌜(λ m. al to m) to # al + 1⌝ , λ al0, a, al1. al1 = al0 + a ' ∧ a ≠ τ ∧ tP(⌜al0⌝ ) ∧ tP(⌜al0⌝ + ⌜a '⌝ ), λ al. al = []
| ⊦ alfrag(ALIOAut(startf, stepf))(σ, β) ↔ # σ = # β + ⌜1⌝ ∧ (∀ n. ⌜n⌝ < # β → stepf(σ[n], β[n], σ[n +1])) |
| tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), # ⌜(λ m. al to m) to # al + 1⌝ ≠ # ⌜al⌝ + ⌜1⌝ ∨ (∃ n. ¬ ( ⌜n⌝ < # ⌜al⌝ → ⌜(λ m. al to m) to # al + 1⌝ [n +1] = ⌜(λ m. al to m) to # al + 1⌝ [n] + ⌜al⌝ [n] ' ∧ ⌜al⌝ [n] ≠ τ ∧ tP(⌜⌜(λ m. al to m) to # al + 1⌝ [n]⌝ ) ∧ tP(⌜⌜(λ m. al to m) to # al + 1⌝ [n]⌝ + ⌜⌜al⌝ [n] '⌝ ))) ⊦ |
al ≠ [], n < # al, tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al to n + 1 = (al to n) + al[n] ' ∧ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used simplifier rules: ⊦ # x = 0 ↔ x = []; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ ⌜x⌝ [n] = x[n]; (s) m < n ⊦ (nf to n)[m] = nf(m); (s) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m < n → ¬ n < m; (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) ⊦ ⌜x⌝ [n] = x[n]; (s) ⊦ m < n → (n ≤ m ↔ false); (s) ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ m + n < m + n0 ↔ n < n0; (s) ⊦ m +1 = m + 1; (s) ⊦ ⌜m⌝ < ⌜n⌝ ↔ m < n; (s) ⊦ # ⌜x⌝ = ⌜# x⌝ ; (s) add-comm: ⊦ n∞1 + n∞2 = n∞2 + n∞1; from specification nat-inf add-assoc: ⊦ (n∞ + n∞1) + n∞2 = n∞ + n∞1 + n∞2; from specification nat-inf ⊦ ⌜n⌝ = ⌜n0⌝ ↔ n = n0; (s) ⊦ n∞ + ⌜0⌝ = n∞; (s) ⊦ m ≤ n → (⌜(* n)⌝ + n∞1 = ⌜(* m)⌝ + n∞2 ↔ ⌜n - m⌝ + n∞1 = n∞2); (s) ⊦ ⌜m + n⌝ = ⌜m⌝ + ⌜n⌝ ; (s) ⊦ # ⌜nf to n⌝ = ⌜n⌝ ; (s)
| al ≠ [], n < # al, tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al to n + 1 = (al to n) + al[n] ' ∧ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
m < # x ⊦ x to m + 1 = (x to m) + x[m] '
al ≠ [], n < # al, tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ (al to n) + al[n] ' = (al to n) + al[n] ' ∧ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: n, al
| m < # x ⊦ x to m + 1 = (x to m) + x[m] ' |
| al ≠ [], n < # al, tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ (al to n) + al[n] ' = (al to n) + al[n] ' ∧ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
| al ≠ [], n < # al, tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, tP(⌜al⌝ ), tP(α), tP(⌜al⌝ ) → ext(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: ⌜al⌝
| al ≠ [], n < # al, tP(⌜al⌝ ), tP(α), tP(⌜al⌝ ) → ext(⌜al⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used simplifier rules: ⊦ ext(⌜al⌝ ) ↔ ext(al); (s)
| al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al⌝ ) ∧ ⌜al to n⌝ ≤ ⌜al⌝ → tP(⌜al to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: ⌜al⌝ , ⌜al to n⌝
| al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al⌝ ) ∧ ⌜al to n⌝ ≤ ⌜al⌝ → tP(⌜al to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ⌜al to n⌝ ≤ ⌜al⌝ → tP(⌜al to n⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
| al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ⌜al to n⌝ ≤ ⌜al⌝ → tP(⌜al to n⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), ¬ ⌜al to n⌝ ≤ ⌜al⌝ , ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
| al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), ¬ ⌜al to n⌝ ≤ ⌜al⌝ , ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
⊦ σ1 ≤ σ2 ↔ (∃ σ. σ1 + σ = σ2)
al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ α. ⌜al to n⌝ + α ≠ ⌜al⌝ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: ⌜al⌝ , ⌜al to n⌝
| ⊦ σ1 ≤ σ2 ↔ (∃ σ. σ1 + σ = σ2) |
| al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α), ∀ α. ⌜al to n⌝ + α ≠ ⌜al⌝ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
⌜al to n⌝ + ⌜al from n⌝ ≠ ⌜al⌝ , al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: ⌜al from n⌝
| ⌜al to n⌝ + ⌜al from n⌝ ≠ ⌜al⌝ , al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
(al to n) + (al from n) ≠ al, al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used simplifier rules: append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[actionstream] ⊦ ⌜x⌝ + ⌜y⌝ = ⌜z⌝ ↔ x + y = z; (s)
| (al to n) + (al from n) ≠ al, al ≠ [], n < # al, ext(al), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
⊦ n ≤ # x → (x to n) + (x from n) = x
Used simplifier rules: ⊦ m < n → m ≤ n; (s) Used terms: n, al
| ⊦ n ≤ # x → (x to n) + (x from n) = x |
| al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), ∀ α. tP(α) → ext(α), ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ ) ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
| al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α1, α2. tP(α1) ∧ α2 ≤ α1 → tP(α2), ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), tP(⌜al⌝ ) ∧ ⌜al to n + 1⌝ ≤ ⌜al⌝ → tP(⌜al to n + 1⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: ⌜al⌝ , ⌜al to n + 1⌝
| al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), tP(⌜al⌝ ) ∧ ⌜al to n + 1⌝ ≤ ⌜al⌝ → tP(⌜al to n + 1⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ⌜al to n + 1⌝ ≤ ⌜al⌝ → tP(⌜al to n + 1⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
| al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ⌜al to n + 1⌝ ≤ ⌜al⌝ → tP(⌜al to n + 1⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), ¬ ⌜al to n + 1⌝ ≤ ⌜al⌝ , ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), tP(⌜al to n + 1⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
| al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), ¬ ⌜al to n + 1⌝ ≤ ⌜al⌝ , ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
⊦ σ1 ≤ σ2 ↔ (∃ σ. σ1 + σ = σ2)
al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α), ∀ α. ⌜al to n + 1⌝ + α ≠ ⌜al⌝ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: ⌜al⌝ , ⌜al to n + 1⌝
| ⊦ σ1 ≤ σ2 ↔ (∃ σ. σ1 + σ = σ2) |
| al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α), ∀ α. ⌜al to n + 1⌝ + α ≠ ⌜al⌝ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
⌜al to n + 1⌝ + ⌜al from n + 1⌝ ≠ ⌜al⌝ , al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: ⌜al from n + 1⌝
| ⌜al to n + 1⌝ + ⌜al from n + 1⌝ ≠ ⌜al⌝ , al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
(al to n + 1) + (al from n + 1) ≠ al, al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used simplifier rules: append-assoc: ⊦ (σ + σ1) + σ2 = σ + σ1 + σ2; from specification stream[actionstream] ⊦ ⌜x⌝ + ⌜y⌝ = ⌜z⌝ ↔ x + y = z; (s)
| (al to n + 1) + (al from n + 1) ≠ al, al ≠ [], n < # al, ext(al), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
⊦ n ≤ # x → (x to n) + (x from n) = x
Used simplifier rules: ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ m < n → (n ≤ m ↔ false); (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: n + 1, al
| ⊦ n ≤ # x → (x to n) + (x from n) = x |
| al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), tP(⌜al to n + 1⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
m < # x ⊦ x to m + 1 = (x to m) + x[m] '
al ≠ [], n < # al, ext(al), tP(⌜(al to n) + al[n] '⌝ ), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ )
Used terms: n, al
| m < # x ⊦ x to m + 1 = (x to m) + x[m] ' |
| al ≠ [], n < # al, ext(al), tP(⌜(al to n) + al[n] '⌝ ), tP(⌜al to n⌝ ), tP(α), tP(⌜al⌝ ), ∀ m. m < # al → al[m] ≠ τ, ∀ α. tP(α) → ext(α) ⊦ al[n] ≠ τ ∧ tP(⌜al to n⌝ + ⌜al[n] '⌝ ) |
al[n] = τ, al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), tP(⌜al to n⌝ + ⌜τ '⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[actionstream] ⊦ ⌜x + y⌝ = ⌜x⌝ + ⌜y⌝ ; (s)
| al[n] = τ, al ≠ [], n < # al, ext(al), tP(⌜al⌝ ), tP(α), tP(⌜al to n⌝ ), tP(⌜al to n⌝ + ⌜τ '⌝ ), ∀ α. tP(α) → ext(α), ∀ m. m < # al → al[m] ≠ τ ⊦ |
Used terms: n
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.