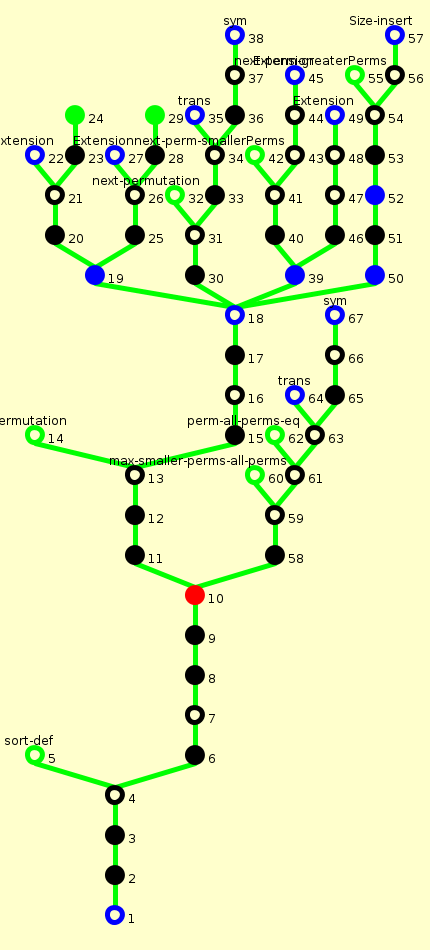
Proof Tree for permut-correct (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ar0 = ar ⊦ ⟨permut#(; ar, listofar)⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)) |
ar0 = ar ⊦ ⟨listofar := []; sort#(; ar); let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))
Used simplifier rules: permut: ⊦ ;
| ar0 = ar ⊦ ⟨listofar := []; sort#(; ar); let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)) |
ar0 = ar, listofar = [] ⊦ ⟨sort#(; ar); let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))
| ar0 = ar, listofar = [] ⊦ ⟨sort#(; ar); let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)) |
ar0 = ar, listofar = [] ⊦ ⟨sort#(; ar); let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))
Used simplifier rules: ⊦ x + a = x + a '; (s)
| ar0 = ar, listofar = [] ⊦ ⟨sort#(; ar); let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)) |
ar0 = ar ⊦ ⟨sort#(; ar)⟩ (ordered≤(ar) ∧ perm(ar0, ar))
ar = ar, ar0 = ar, ar3 = ar, listofar = [] ⊦ [sort#(; ar) ] (( ordered≤(ar) ∧ perm(ar3, ar) → ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))) ; default :: true )
| ar0 = ar ⊦ ⟨sort#(; ar)⟩ (ordered≤(ar) ∧ perm(ar0, ar)) |
| ar = ar, ar0 = ar, ar3 = ar, listofar = [] ⊦ [sort#(; ar) ] (( ordered≤(ar) ∧ perm(ar3, ar) → ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))) ; default :: true ) |
ar0 = ar, listofar = [] ⊦ [sort#(; ar) ] (( ordered≤(ar) ∧ perm(ar0, ar) → ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))) ; default :: true )
| ar0 = ar, listofar = [] ⊦ [sort#(; ar) ] (( ordered≤(ar) ∧ perm(ar0, ar) → ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))) ; default :: true ) |
ar0 = ar, listofar = [] ⊦ ∀ ar. ordered≤(ar) ∧ perm(ar0, ar) → ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))
| ar0 = ar, listofar = [] ⊦ ∀ ar. ordered≤(ar) ∧ perm(ar0, ar) → ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar, ar`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar);listofar.toSet = smallerPerms(ar) ++ ar) ∧ (¬ hasNext → max(ar)) wfbound # greaterPerms(ar) + (hasNext ⊃ 1;0) */; listofar := listofar + ar '; next#(; ar; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)) |
listofar = [], ordered≤(ar1), perm(ar0, ar1) ⊦ ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar1, ar1`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1)) wfbound # greaterPerms(ar1) + (hasNext ⊃ 1;0) */; listofar := listofar + ar1 '; next#(; ar1; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))
| listofar = [], ordered≤(ar1), perm(ar0, ar1) ⊦ ⟨let hasNext = true in while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar1, ar1`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1)) wfbound # greaterPerms(ar1) + (hasNext ⊃ 1;0) */; listofar := listofar + ar1 '; next#(; ar1; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)) |
hasNext ↔ true, listofar = [], ordered≤(ar1), perm(ar0, ar1) ⊦ ⟨while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar1, ar1`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1)) wfbound # greaterPerms(ar1) + (hasNext ⊃ 1;0) */; listofar := listofar + ar1 '; next#(; ar1; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0))
| hasNext ↔ true, listofar = [], ordered≤(ar1), perm(ar0, ar1) ⊦ ⟨while hasNext do {/* invariant ¬ dups(listofar) ∧ perm(ar1, ar1`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1)) wfbound # greaterPerms(ar1) + (hasNext ⊃ 1;0) */; listofar := listofar + ar1 '; next#(; ar1; hasNext)}⟩ (¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)) |
hasNext1 ↔ true, hasNext ↔ hasNext0, ar1 = ar, hasNext, listofar0 = [], ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar), ¬ hasNext → max(ar1), (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ⊦ ⟨listofar := listofar + ar1 '; next#(; ar1; hasNext)⟩ ( ( ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1))) ∧ # greaterPerms(ar1) + (hasNext ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0))
hasNext1 ↔ true, ¬ hasNext, listofar0 = [], ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar), ¬ hasNext → max(ar1), (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ⊦ ¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0)
Used simplifier rules: ordered-arraylist-base0: ⊦ ordered≤([]); nil-toSet: ⊦ [].toSet = ∅; ordered-smallerPerms: ⊦ ordered≤(ar) → smallerPerms(ar) = ∅; <; (wellfounded) ⊦ ¬ dups([]); (s) ⊦ perm(x, x); (s) Used formulas: ¬ dups(listofar) ∧ perm(ar1, ar1`) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1)), # greaterPerms(ar1) + (hasNext ⊃ 1;0) = # greaterPerms(ar1) + (hasNext ⊃ 1;0)
| hasNext1 ↔ true, hasNext ↔ hasNext0, ar1 = ar, hasNext, listofar0 = [], ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar), ¬ hasNext → max(ar1), (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ⊦ ⟨listofar := listofar + ar1 '; next#(; ar1; hasNext)⟩ ( ( ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1))) ∧ # greaterPerms(ar1) + (hasNext ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)) |
hasNext ↔ hasNext0, hasNext1 ↔ true, ar1 = ar, hasNext, listofar = listofar1 + ar1 ', listofar0 = [], ordered≤(listofar1), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ hasNext → max(ar1), (hasNext ⊃ listofar1.toSet = smallerPerms(ar1);listofar1.toSet = smallerPerms(ar1) ++ ar1) ⊦ ⟨next#(; ar1; hasNext)⟩ ( ( ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1))) ∧ # greaterPerms(ar1) + (hasNext ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0))
| hasNext ↔ hasNext0, hasNext1 ↔ true, ar1 = ar, hasNext, listofar = listofar1 + ar1 ', listofar0 = [], ordered≤(listofar1), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ hasNext → max(ar1), (hasNext ⊃ listofar1.toSet = smallerPerms(ar1);listofar1.toSet = smallerPerms(ar1) ++ ar1) ⊦ ⟨next#(; ar1; hasNext)⟩ ( ( ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext → max(ar1))) ∧ # greaterPerms(ar1) + (hasNext ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)) |
listofar1.toSet = smallerPerms(ar), ar1 = ar, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦ ⟨next#(; ar1; hasNext1)⟩ ( ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0))
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification list[list-of-natarray] ⊦ a ∈ b ' ↔ a = b; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) in-15: ⊦ x + a ' = y → a ∈ y; (forward) from specification list[list-of-natarray]
| listofar1.toSet = smallerPerms(ar), ar1 = ar, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦ ⟨next#(; ar1; hasNext1)⟩ ( ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)) |
ar = ar0 ⊦ ⟨next#(; ar; hasNext)⟩ (hasNext ⊃ nextperm(ar0, ar);ar = ar0 ∧ max(ar))
listofar1.toSet = smallerPerms(ar), ar1 = ar, ar1 = ar1, ar5 = ar1, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ [next#(; ar1; hasNext1) ] (( (hasNext1 ⊃ nextperm(ar5, ar1);ar1 = ar5 ∧ max(ar1)) → ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)) ; default :: true )
| ar = ar0 ⊦ ⟨next#(; ar; hasNext)⟩ (hasNext ⊃ nextperm(ar0, ar);ar = ar0 ∧ max(ar)) |
| listofar1.toSet = smallerPerms(ar), ar1 = ar, ar1 = ar1, ar5 = ar1, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ [next#(; ar1; hasNext1) ] (( (hasNext1 ⊃ nextperm(ar5, ar1);ar1 = ar5 ∧ max(ar1)) → ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)) ; default :: true ) |
listofar1.toSet = smallerPerms(ar), ar1 = ar, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ [next#(; ar1; hasNext1) ] (( (hasNext1 ⊃ nextperm(ar, ar1);ar1 = ar ∧ max(ar)) → ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)) ; default :: true )
| listofar1.toSet = smallerPerms(ar), ar1 = ar, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ [next#(; ar1; hasNext1) ] (( (hasNext1 ⊃ nextperm(ar, ar1);ar1 = ar ∧ max(ar)) → ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)) ; default :: true ) |
listofar1.toSet = smallerPerms(ar), ar1 = ar, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦ ∀ ar1, hasNext1. (hasNext1 ⊃ nextperm(ar, ar1);ar1 = ar ∧ max(ar)) → ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0)
| listofar1.toSet = smallerPerms(ar), ar1 = ar, hasNext0, hasNext1, listofar = listofar1 + ar ', ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦ ∀ ar1, hasNext1. (hasNext1 ⊃ nextperm(ar, ar1);ar1 = ar ∧ max(ar)) → ¬ dups(listofar) ∧ perm(ar1, ar2) ∧ ordered≤(listofar) ∧ (hasNext1 ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ∧ (¬ hasNext1 → max(ar1)) ∧ # greaterPerms(ar1) + (hasNext1 ⊃ 1;0) < # greaterPerms(ar) + (hasNext0 ⊃ 1;0) |
listofar1.toSet = smallerPerms(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ ¬ ar ∈ listofar1 ∧ perm(ar3, ar2) ∧ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3) ∧ (¬ hasNext → max(ar3)) ∧ ¬ # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0)
Used simplifier rules: ordered-append: ⊦ ordered≤(arx) ∧ arx.toSet = smallerPerms(ar) → ordered≤(arx + ar '); c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m < n + 1 ↔ ¬ n < m; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[list-of-natarray] ⊦ dups(x + a ') ↔ a ∈ x ∨ dups(x); (ws)
| listofar1.toSet = smallerPerms(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ ¬ ar ∈ listofar1 ∧ perm(ar3, ar2) ∧ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3) ∧ (¬ hasNext → max(ar3)) ∧ ¬ # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0) |
listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦
listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ perm(ar3, ar2), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦
listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3)
listofar1.toSet = smallerPerms(ar), # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦
| listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ |
listofar1.toSet = smallerPerms(ar), hasNext, nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦
listofar1.toSet = smallerPerms(ar), ar3 = ar, ¬ hasNext, max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦
| listofar1.toSet = smallerPerms(ar), hasNext, nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦ |
listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦
| listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦ |
⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2)
nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1.toSet ↔ a ∈ smallerPerms(ar) ⊦
Used terms: listofar1.toSet, smallerPerms(ar)
| ⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2) |
| nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1.toSet ↔ a ∈ smallerPerms(ar) ⊦ |
nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1 ↔ ar ≠ a ∧ perm(ar, a) ∧ a ≤ ar ⊦
Used simplifier rules: toSet: ⊦ ar ∈ arx.toSet ↔ ar ∈ arx; smaller-perms: ⊦ ar0 ∈ smallerPerms(ar) ↔ ar ≠ ar0 ∧ perm(ar, ar0) ∧ ar0 ≤ ar;
| nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1 ↔ ar ≠ a ∧ perm(ar, a) ∧ a ≤ ar ⊦ |
Used terms: ar
| listofar1.toSet = smallerPerms(ar), ar3 = ar, ¬ hasNext, max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦ |
listofar1.toSet = smallerPerms(ar), max(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦
| listofar1.toSet = smallerPerms(ar), max(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1) ⊦ |
⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2)
max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1.toSet ↔ a ∈ smallerPerms(ar) ⊦
Used terms: listofar1.toSet, smallerPerms(ar)
| ⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2) |
| max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1.toSet ↔ a ∈ smallerPerms(ar) ⊦ |
max(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1 ↔ ar ≠ a ∧ perm(ar, a) ∧ a ≤ ar ⊦
Used simplifier rules: toSet: ⊦ ar ∈ arx.toSet ↔ ar ∈ arx; smaller-perms: ⊦ ar0 ∈ smallerPerms(ar) ↔ ar ≠ ar0 ∧ perm(ar, ar0) ∧ ar0 ≤ ar;
| max(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ar ∈ listofar1, ¬ dups(listofar1), ∀ a. a ∈ listofar1 ↔ ar ≠ a ∧ perm(ar, a) ∧ a ≤ ar ⊦ |
Used terms: ar
| listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ perm(ar3, ar2), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ |
listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ perm(ar3, ar2) ⊦
Used simplifier rules: ⊦ perm(x, y) ∧ ¬ perm(x0, y) → x ≠ x0; (s)
| listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ perm(ar3, ar2) ⊦ |
⊦ nextperm(ar1, ar2) ↔ perm(ar1, ar2) ∧ ar1 ≠ ar2 ∧ ar1 ≤ ar2 ∧ (∀ ar3. perm(ar1, ar3) ∧ ar3 ≠ ar1 ∧ ar3 ≠ ar2 → ¬(ar1 ≤ ar3 ∧ ar3 ≤ ar2))
listofar1.toSet = smallerPerms(ar), ar ≠ ar3, ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), perm(ar, ar3), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ∀ ar0. perm(ar, ar0) ∧ ar0 ≠ ar ∧ ar0 ≠ ar3 → ¬(ar ≤ ar0 ∧ ar0 ≤ ar3) ⊦
Used terms: ar, ar3
| ⊦ nextperm(ar1, ar2) ↔ perm(ar1, ar2) ∧ ar1 ≠ ar2 ∧ ar1 ≤ ar2 ∧ (∀ ar3. perm(ar1, ar3) ∧ ar3 ≠ ar1 ∧ ar3 ≠ ar2 → ¬(ar1 ≤ ar3 ∧ ar3 ≤ ar2)) |
| listofar1.toSet = smallerPerms(ar), ar ≠ ar3, ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), perm(ar, ar3), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ∀ ar0. perm(ar, ar0) ∧ ar0 ≠ ar ∧ ar0 ≠ ar3 → ¬(ar ≤ ar0 ∧ ar0 ≤ ar3) ⊦ |
listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar3), perm(ar, ar2), perm(ar0, ar2), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ∀ ar1. perm(ar, ar1) ∧ ar1 ≠ ar ∧ ar1 ≠ ar3 → ¬ ar ≤ ar1 ∨ ¬ ar1 ≤ ar3 ⊦
Used simplifier rules: ⊦ perm(x, y) ∧ ¬ perm(x0, y) → x ≠ x0; (s)
| listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar3), perm(ar, ar2), perm(ar0, ar2), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ∀ ar1. perm(ar, ar1) ∧ ar1 ≠ ar ∧ ar1 ≠ ar3 → ¬ ar ≤ ar1 ∨ ¬ ar1 ≤ ar3 ⊦ |
⊦ perm(x, y) ∧ perm(y, z) → perm(x, z)
listofar1.toSet = smallerPerms(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), perm(ar, ar3), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ∀ ar1. perm(ar, ar1) ∧ ar1 ≠ ar ∧ ar1 ≠ ar3 → ¬ ar ≤ ar1 ∨ ¬ ar1 ≤ ar3 ⊦ perm(ar3, ar) ∧ perm(ar, ar2)
Used terms: ar, ar3, ar2
| ⊦ perm(x, y) ∧ perm(y, z) → perm(x, z) |
| listofar1.toSet = smallerPerms(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), perm(ar, ar3), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ∀ ar1. perm(ar, ar1) ∧ ar1 ≠ ar ∧ ar1 ≠ ar3 → ¬ ar ≤ ar1 ∨ ¬ ar1 ≤ ar3 ⊦ perm(ar3, ar) ∧ perm(ar, ar2) |
listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar3), perm(ar, ar2), perm(ar0, ar2), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ¬ perm(ar3, ar), ∀ ar1. perm(ar, ar1) ∧ ar1 ≠ ar ∧ ar1 ≠ ar3 → ¬ ar ≤ ar1 ∨ ¬ ar1 ≤ ar3 ⊦
| listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar3), perm(ar, ar2), perm(ar0, ar2), ar ≤ ar3, ¬ dups(listofar1), ¬ perm(ar3, ar2), ¬ perm(ar3, ar), ∀ ar1. perm(ar, ar1) ∧ ar1 ≠ ar ∧ ar1 ≠ ar3 → ¬ ar ≤ ar1 ∨ ¬ ar1 ≤ ar3 ⊦ |
⊦ perm(x, y) ↔ perm(y, x)
Used terms: ar3, ar
| ⊦ perm(x, y) ↔ perm(y, x) |
| listofar1.toSet = smallerPerms(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3) |
listofar1.toSet = smallerPerms(ar), hasNext, nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3)
listofar1.toSet = smallerPerms(ar), ar3 = ar, ¬ hasNext, max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3)
| listofar1.toSet = smallerPerms(ar), hasNext, nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3) |
listofar1.toSet = smallerPerms(ar), (listofar1 + ar ').toSet ≠ smallerPerms(ar3), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦
| listofar1.toSet = smallerPerms(ar), (listofar1 + ar ').toSet ≠ smallerPerms(ar3), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦ |
⊦ nextperm(ar1, ar2) → smallerPerms(ar2) = smallerPerms(ar1) ++ ar1
listofar1.toSet = smallerPerms(ar), (listofar1 + ar ').toSet ≠ smallerPerms(ar) ++ ar, nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦
Used terms: ar, ar3
| ⊦ nextperm(ar1, ar2) → smallerPerms(ar2) = smallerPerms(ar1) ++ ar1 |
| listofar1.toSet = smallerPerms(ar), (listofar1 + ar ').toSet ≠ smallerPerms(ar) ++ ar, nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ |
(listofar1 + ar ').toSet ≠ listofar1.toSet ++ ar, nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦
| (listofar1 + ar ').toSet ≠ listofar1.toSet ++ ar, nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦ |
⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2)
Used simplifier rules: toSet: ⊦ ar ∈ arx.toSet ↔ ar ∈ arx; ⊦ a ∈ s ++ b ↔ a = b ∨ a ∈ s; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) ⊦ a ∈ b ' ↔ a = b; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[list-of-natarray] Used terms: (listofar1 + ar ').toSet, listofar1.toSet ++ ar
| ⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2) |
| listofar1.toSet = smallerPerms(ar), ar3 = ar, ¬ hasNext, max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ (hasNext ⊃ (listofar1 + ar ').toSet = smallerPerms(ar3);(listofar1 + ar ').toSet = smallerPerms(ar3) ++ ar3) |
listofar1.toSet = smallerPerms(ar), (listofar1 + ar ').toSet ≠ smallerPerms(ar) ++ ar, max(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦
| listofar1.toSet = smallerPerms(ar), (listofar1 + ar ').toSet ≠ smallerPerms(ar) ++ ar, max(ar), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1) ⊦ |
(listofar1 + ar ').toSet ≠ listofar1.toSet ++ ar, max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦
| (listofar1 + ar ').toSet ≠ listofar1.toSet ++ ar, max(ar), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1) ⊦ |
⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2)
Used simplifier rules: toSet: ⊦ ar ∈ arx.toSet ↔ ar ∈ arx; ⊦ a ∈ s ++ b ↔ a = b ∨ a ∈ s; (s) ⊦ a ∈ x + y ↔ a ∈ x ∨ a ∈ y; (s) ⊦ a ∈ b ' ↔ a = b; (s) a: ⊦ (x + y) + z = x + y + z; from specification list[list-of-natarray] Used terms: (listofar1 + ar ').toSet, listofar1.toSet ++ ar
| ⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2) |
| listofar1.toSet = smallerPerms(ar), # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ |
listofar1.toSet = smallerPerms(ar), # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦
Used simplifier rules: f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ n + 0 = n; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ ¬ a < a; (s) Used formulas: nextperm(ar, ar3)
| listofar1.toSet = smallerPerms(ar), # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1), (hasNext ⊃ nextperm(ar, ar3);ar3 = ar ∧ max(ar)) ⊦ |
listofar1.toSet = smallerPerms(ar), # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1), ¬ hasNext → ar3 = ar ∧ max(ar) ⊦
Used simplifier rules: ⊦ m < n → n ≠ 0; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic
| listofar1.toSet = smallerPerms(ar), # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), ¬ dups(listofar1), ¬ hasNext → ar3 = ar ∧ max(ar) ⊦ |
listofar1.toSet = smallerPerms(ar), hasNext, # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ hasNext → ar3 = ar ∧ max(ar) ⊦
Used simplifier rules: ⊦ n + 0 = n; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ m < n → n ≠ 0; (s) ⊦ ¬ a < a; (s) Used formulas: ¬ hasNext
| listofar1.toSet = smallerPerms(ar), hasNext, # greaterPerms(ar) < # greaterPerms(ar3) + (hasNext ⊃ 1;0), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), ¬ dups(listofar1), ¬ hasNext → ar3 = ar ∧ max(ar) ⊦ |
listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), # greaterPerms(ar) ≤ # greaterPerms(ar3), ¬ dups(listofar1) ⊦
Used simplifier rules: ⊦ m < n ↔ ¬ n ≤ m; (ss) c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m < n + 1 ↔ ¬ n < m; (s)
| listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(ar2), ordered≤(listofar1), perm(ar0, ar2), perm(ar, ar2), # greaterPerms(ar) ≤ # greaterPerms(ar3), ¬ dups(listofar1) ⊦ |
⊦ nextperm(ar1, ar2) → greaterPerms(ar1) = greaterPerms(ar2) ++ ar2
listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), #(greaterPerms(ar3) ++ ar3) ≤ # greaterPerms(ar3), ¬ dups(listofar1) ⊦
Used terms: ar3, ar
| ⊦ nextperm(ar1, ar2) → greaterPerms(ar1) = greaterPerms(ar2) ++ ar2 |
| listofar1.toSet = smallerPerms(ar), nextperm(ar, ar3), ordered≤(listofar1), ordered≤(ar2), perm(ar, ar2), perm(ar0, ar2), #(greaterPerms(ar3) ++ ar3) ≤ # greaterPerms(ar3), ¬ dups(listofar1) ⊦ |
⊦ ¬ a ∈ s → #(s ++ a) = # s + 1
Used simplifier rules: greater-perms: ⊦ ar0 ∈ greaterPerms(ar) ↔ ar ≠ ar0 ∧ perm(ar, ar0) ∧ ar ≤ ar0; ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ ¬ a < a; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic ⊦ a ∈ s → s ++ a = s; (s) ⊦ m ≤ m; (s) Used terms: greaterPerms(ar3), ar3
| ⊦ ¬ a ∈ s → #(s ++ a) = # s + 1 |
| hasNext1 ↔ true, ¬ hasNext, listofar0 = [], ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar), ¬ hasNext → max(ar1), (hasNext ⊃ listofar.toSet = smallerPerms(ar1);listofar.toSet = smallerPerms(ar1) ++ ar1) ⊦ ¬ dups(listofar) ∧ ordered≤(listofar) ∧ listofar.toSet = allPerms(ar0) |
listofar.toSet = smallerPerms(ar1) ++ ar1, smallerPerms(ar1) ++ ar1 ≠ allPerms(ar0), max(ar1), ordered≤(listofar), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar) ⊦
| listofar.toSet = smallerPerms(ar1) ++ ar1, smallerPerms(ar1) ++ ar1 ≠ allPerms(ar0), max(ar1), ordered≤(listofar), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar) ⊦ |
⊦ max(ar) → smallerPerms(ar) ++ ar = allPerms(ar)
listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar) ⊦
Used terms: ar1
| ⊦ max(ar) → smallerPerms(ar) ++ ar = allPerms(ar) |
| listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar) ⊦ |
⊦ perm(ar0, ar1) → allPerms(ar0) = allPerms(ar1)
listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(listofar), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar), ¬ perm(ar0, ar1) ⊦
Used terms: ar1, ar0
| ⊦ perm(ar0, ar1) → allPerms(ar0) = allPerms(ar1) |
| listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(listofar), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar), ¬ perm(ar0, ar1) ⊦ |
⊦ perm(x, y) ∧ perm(y, z) → perm(x, z)
listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar), ¬ perm(ar0, ar1) ⊦ perm(ar0, ar2) ∧ perm(ar2, ar1)
Used terms: ar2, ar0, ar1
| ⊦ perm(x, y) ∧ perm(y, z) → perm(x, z) |
| listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(ar2), ordered≤(listofar), perm(ar0, ar2), perm(ar1, ar2), ¬ dups(listofar), ¬ perm(ar0, ar1) ⊦ perm(ar0, ar2) ∧ perm(ar2, ar1) |
listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(listofar), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar), ¬ perm(ar0, ar1), ¬ perm(ar2, ar1) ⊦
| listofar.toSet = allPerms(ar1), allPerms(ar1) ≠ allPerms(ar0), max(ar1), ordered≤(listofar), ordered≤(ar2), perm(ar1, ar2), perm(ar0, ar2), ¬ dups(listofar), ¬ perm(ar0, ar1), ¬ perm(ar2, ar1) ⊦ |
⊦ perm(x, y) ↔ perm(y, x)
Used terms: ar2, ar1
| ⊦ perm(x, y) ↔ perm(y, x) |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.