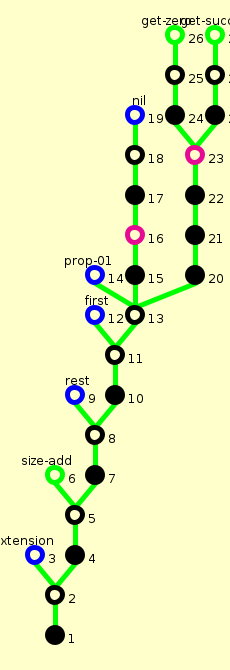
Proof Tree for case-list (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ x = [] ∨ x = x.first + x.rest |
x ≠ [], x ≠ x.first + x.rest ⊦
| x ≠ [], x ≠ x.first + x.rest ⊦ |
⊦ ar1 = ar2 ↔ # ar1 = # ar2 ∧ (∀ n. n < # ar1 → ar1[n] = ar2[n])
x ≠ [], # x ≠ #(x.first + x.rest) ∨ (∃ n. ¬(n < # x → x[n] = (x.first + x.rest)[n])) ⊦
Used terms: x, x.first + x.rest
| ⊦ ar1 = ar2 ↔ # ar1 = # ar2 ∧ (∀ n. n < # ar1 → ar1[n] = ar2[n]) |
| x ≠ [], # x ≠ #(x.first + x.rest) ∨ (∃ n. ¬(n < # x → x[n] = (x.first + x.rest)[n])) ⊦ |
x ≠ [], # x ≠ #(x.first + x.rest) ∨ ¬(n < # x → x[n] = (x.first + x.rest)[n]) ⊦
| x ≠ [], # x ≠ #(x.first + x.rest) ∨ ¬(n < # x → x[n] = (x.first + x.rest)[n]) ⊦ |
⊦ #(a + x) = (# x)+1
x ≠ [], # x ≠ (# x.rest)+1 ∨ ¬(n < # x → x[n] = (x.first + x.rest)[n]) ⊦
Used terms: x.first, x.rest
| x ≠ [], # x ≠ (# x.rest)+1 ∨ ¬(n < # x → x[n] = (x.first + x.rest)[n]) ⊦ |
x ≠ [], # x ≠ # x.rest + 1 ∨ ¬(n < # x → x[n] = (x.first + x.rest)[n]) ⊦
Used simplifier rules: ⊦ m +1 = m + 1; (s)
| x ≠ [], # x ≠ # x.rest + 1 ∨ ¬(n < # x → x[n] = (x.first + x.rest)[n]) ⊦ |
⊦ ar.rest = subarray(ar, 1, # ar - 1)
x ≠ [], # x ≠ # subarray(x, 1, # x - 1) + 1 ∨ ¬(n < # x → x[n] = (x.first + subarray(x, 1, # x - 1))[n]) ⊦
Used terms: x
| ⊦ ar.rest = subarray(ar, 1, # ar - 1) |
| x ≠ [], # x ≠ # subarray(x, 1, # x - 1) + 1 ∨ ¬(n < # x → x[n] = (x.first + subarray(x, 1, # x - 1))[n]) ⊦ |
x ≠ [], # x ≠ (# x - 1) + 1 ∨ ¬(n < # x → x[n] = (x.first + subarray(x, 1, # x - 1))[n]) ⊦
Used simplifier rules: ⊦ # subarray(ar, m, n) = n; (s)
| x ≠ [], # x ≠ (# x - 1) + 1 ∨ ¬(n < # x → x[n] = (x.first + subarray(x, 1, # x - 1))[n]) ⊦ |
⊦ ar.first = ar[0]
x ≠ [], # x ≠ (# x - 1) + 1 ∨ ¬(n < # x → x[n] = (x[0] + subarray(x, 1, # x - 1))[n]) ⊦
Used terms: x
| x ≠ [], # x ≠ (# x - 1) + 1 ∨ ¬(n < # x → x[n] = (x[0] + subarray(x, 1, # x - 1))[n]) ⊦ |
n ≤ m ⊦ (m - n) + n = m
x ≠ [], ¬ 1 ≤ # x, # x ≠ (# x - 1) + 1 ∨ ¬(n < # x → x[n] = (x[0] + subarray(x, 1, # x - 1))[n]) ⊦
x ≠ [], 1 ≤ # x, # x ≠ # x ∨ ¬(n < # x → x[n] = (x[0] + subarray(x, 1, # x - 1))[n]) ⊦
Used terms: # x, 1
| n ≤ m ⊦ (m - n) + n = m |
| x ≠ [], ¬ 1 ≤ # x, # x ≠ (# x - 1) + 1 ∨ ¬(n < # x → x[n] = (x[0] + subarray(x, 1, # x - 1))[n]) ⊦ |
# x = 0, x ≠ [] ⊦
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m + 1 ≠ 0; (s) ⊦ m < 1 ↔ m = 0; (s) ⊦ m ≤ n ↔ ¬ n < m; (ss)
| # x = 0, x ≠ [] ⊦ |
# x = 0, x = mkarray(n), x ≠ [] ⊦
Used simplifier rules: array('a) generated by mkarray, [ := ];; ⊦ # ar[n := a] = # ar; (s) ⊦ ar[n := a] = ar ↔ ¬ n < # ar ∨ ar[n] = a; (s) ⊦ m < n → n ≠ 0; (s)
| # x = 0, x = mkarray(n), x ≠ [] ⊦ |
mkarray(0) ≠ [] ⊦
Used simplifier rules: ⊦ # mkarray(n) = n; (s)
| mkarray(0) ≠ [] ⊦ |
⊦ [] = mkarray(0)
Used terms:
| x ≠ [], 1 ≤ # x, # x ≠ # x ∨ ¬(n < # x → x[n] = (x[0] + subarray(x, 1, # x - 1))[n]) ⊦ |
x[n] ≠ (x[0] + subarray(x, 1, # x - 1))[n], x ≠ [], n < # x, 1 ≤ # x ⊦
Used simplifier rules: ⊦ m < n → n ≠ 0; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic
| x[n] ≠ (x[0] + subarray(x, 1, # x - 1))[n], x ≠ [], n < # x, 1 ≤ # x ⊦ |
# x = n0 + 1, # x ≠ 0, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n < # x, 1 ≤ # x ⊦
Used simplifier rules: ⊦ m < n → n ≠ 0; (s) n ≠ 0 ⊦ m = n - 1 ↔ n = m + 1; (elim) Used terms: # x, m
| # x = n0 + 1, # x ≠ 0, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n < # x, 1 ≤ # x ⊦ |
# x = n0 + 1, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n ≤ n0 ⊦
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m ≤ n → (n < m ↔ false); (s) ⊦ m < n + 1 ↔ ¬ n < m; (s) ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ m ≤ m + n; (s) ⊦ m + 1 ≠ 0; (s) lf-01: ⊦ m < n ∧ n = n0 → m < n0; (forward) from specification nat-basic f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic ⊦ m < n → n ≠ 0; (s)
| # x = n0 + 1, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n ≤ n0 ⊦ |
# x = n0 + 1, n = 0, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n ≤ n0 ⊦
# x = n0 + 1, n = n1 +1, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n ≤ n0 ⊦
Used simplifier rules: nat freely generated by 0, +1;;
| # x = n0 + 1, n = 0, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n ≤ n0 ⊦ |
# x = n0 + 1, x[0] ≠ (x[0] + subarray(x, 1, n0))[0], x ≠ [] ⊦
Used simplifier rules: ⊦ 0 ≤ m; (s)
| # x = n0 + 1, x[0] ≠ (x[0] + subarray(x, 1, n0))[0], x ≠ [] ⊦ |
⊦ (a + x)[0] = a
Used terms: x[0], subarray(x, 1, n0)
| # x = n0 + 1, n = n1 +1, x[n] ≠ (x[0] + subarray(x, 1, n0))[n], x ≠ [], n ≤ n0 ⊦ |
# x = n0 + 1, x[n1 + 1] ≠ (x[0] + subarray(x, 1, n0))[n1 + 1], x ≠ [], n1 < n0 ⊦
Used simplifier rules: ⊦ m < n → n ≠ 0; (s) f: ⊦ m < n → n ≠ 0; (forward) from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m + 1 ≤ n ↔ m < n; (s) ⊦ m +1 = m + 1; (s)
| # x = n0 + 1, x[n1 + 1] ≠ (x[0] + subarray(x, 1, n0))[n1 + 1], x ≠ [], n1 < n0 ⊦ |
⊦ (a + x)[n + 1] = x[n]
Used simplifier rules: ⊦ n0 < n → subarray(ar, m, n)[n0] = ar[m + n0]; (s) c: ⊦ m + n = n + m; from specification nat-basic Used terms: x[0], subarray(x, 1, n0), n1
| ⊦ (a + x)[n + 1] = x[n] |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.