[Imprint][Data Privacy Statement][E-Mail]
View long theorem info.
View the proof.
Back to main index.
View the specification.
View theorem base summary,
View theorem base listing,
the used properties by spec,
the dependency list,
the symbol table,
Proof step 1 from proof longest-common-prefix (conclusion)
(back to tree)
| ⊦ ∃ z, x0, y0. x = z + x0 ∧ y = z + y0 ∧ (x0 ≠ [] ∧ y0 ≠ [] → x0.head ≠ y0.head) |
Heuristic structural induction applied rule structural induction
And obtained the following new goals
- Proof step 2:
⊦ ∃ z, x0, y0. x = z + x0 ∧ [] = z + y0 ∧ (x0 ≠ [] ∧ y0 ≠ [] → x0.head ≠ y0.head)
- Proof step 3:
∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
term: y
Additional information
Used simplifier rules:
list('a) freely generated by [], +;;
Proof step 2 from proof longest-common-prefix (previous step)
(back to tree)
| ⊦ ∃ z, x0, y0. x = z + x0 ∧ [] = z + y0 ∧ (x0 ≠ [] ∧ y0 ≠ [] → x0.head ≠ y0.head) |
User applied rule exists right
And closed the goal!
Rule argument
pos: right 1 terms: [], x, [] abort: F discard: T computed: F
Additional information
Used simplifier rules:
Nil: ⊦ [] + x = x;
a: ⊦ (x + y) + z = x + y + z;
Used terms: [], x, []
Proof step 3 from proof longest-common-prefix (previous step)
(back to tree)
| ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 4:
∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
Additional information
Used simplifier rules:
c: ⊦ a + x = a ' + x;
Proof step 4 from proof longest-common-prefix (previous step)
(back to tree)
| ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
User applied rule constructor cut
And obtained the following new goals
- Proof step 5:
x = [], ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
- Proof step 7:
x = a0 + x1, ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
var: x
Additional information
Used simplifier rules:
list('a) freely generated by [], +;;
Proof step 5 from proof longest-common-prefix (previous step)
(back to tree)
| x = [], ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 6:
∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. [] = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
Additional information
Proof step 6 from proof longest-common-prefix (previous step)
(back to tree)
| ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. [] = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
User applied rule exists right
And closed the goal!
Rule argument
pos: right 1 terms: [], [], a + y0 abort: F discard: T computed: F
Additional information
Used simplifier rules:
c: ⊦ a + x = a ' + x;
Nil: ⊦ [] + x = x;
app-01: ⊦ x + y = x + z ↔ y = z;
a: ⊦ (x + y) + z = x + y + z;
Used terms: [], [], a + y0
Proof step 7 from proof longest-common-prefix (previous step)
(back to tree)
| x = a0 + x1, ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. x = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 8:
∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
Additional information
Used simplifier rules:
c: ⊦ a + x = a ' + x;
Proof step 8 from proof longest-common-prefix (previous step)
(back to tree)
| ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
User applied rule cut formula
And obtained the following new goals
- Proof step 9:
a = a0, ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
- Proof step 13:
a ≠ a0, ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
fma: a = a0
Additional information
Used formulas: a = a0
Proof step 9 from proof longest-common-prefix (previous step)
(back to tree)
| a = a0, ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 10:
∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a0 ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
Additional information
Proof step 10 from proof longest-common-prefix (previous step)
(back to tree)
| ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a0 ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
User applied rule all left
And obtained the following new goals
- Proof step 11:
∃ z, x0, y1. x1 = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a0 ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
Rule argument
pos: left 1 terms: x1 abort: F discard: T computed: F
Additional information
Used terms: x1
Proof step 11 from proof longest-common-prefix (previous step)
(back to tree)
| ∃ z, x0, y1. x1 = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a0 ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
Rule argument
Additional information
Proof step 12 from proof longest-common-prefix (previous step)
(back to tree)
| x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head ⊦ ∃ z0, x, y. a0 ' + z + x0 = z0 + x ∧ a0 ' + z + y1 = z0 + y ∧ (x ≠ [] ∧ y ≠ [] → x.head ≠ y.head) |
User applied rule exists right
And closed the goal!
Rule argument
pos: right 1 terms: a0 ' + z, x0, y1 abort: F discard: F computed: T
Additional information
Used simplifier rules:
a: ⊦ (x + y) + z = x + y + z;
Used terms: a0 ' + z, x0, y1
Proof step 13 from proof longest-common-prefix (previous step)
(back to tree)
| a ≠ a0, ∀ x. ∃ z, x0, y1. x = z + x0 ∧ y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head)
⊦ ∃ z, x0, y1. a0 ' + x1 = z + x0 ∧ a ' + y0 = z + y1 ∧ (x0 ≠ [] ∧ y1 ≠ [] → x0.head ≠ y1.head) |
User applied rule exists right
And closed the goal!
Rule argument
pos: right 1 terms: [], a0 ' + x1, a ' + y0 abort: F discard: F computed: F
Additional information
Used simplifier rules:
Nil: ⊦ [] + x = x;
app-01: ⊦ x + y = x + z ↔ y = z;
e-01: ⊦ a ' + x ≠ [];
c-08: ⊦ (a ' + x).head = a;
a: ⊦ (x + y) + z = x + y + z;
Used terms: [], a0 ' + x1, a ' + y0
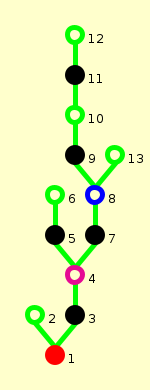
Proof Tree for longest-common-prefix
(View conclusion)
The following image shows the proof tree of sequent calculus. The
proved goal is at the bottom. You can click on the nodes to view
additional rules. See here for details on colors in a proof
tree.