[Imprint][Data Privacy Statement][E-Mail]
View long theorem info.
View the proof.
Back to main index.
View the specification.
View theorem base summary,
View theorem base listing,
the used properties by spec,
the dependency list,
the symbol table,
Proof step 1 from proof add-preserves-reachable-rev (conclusion)
(back to tree)
| ⊦ h[r1].nxt = h[r2].nxt ∧ r0 ≠ r2 ∧ ce.nxt = r2 ∧ ¬ reachable(r, r0, h) ∧ ¬ reachable(r, r2, h) ∧ r2 ≠ null ∧ r2 ∈ h ∧ reachable(r, r1, h)
→ (reachable(r, r0, h[r1 := ce]) ↔ false) |
System applied rule normalize
And obtained the following new goals
- Proof step 2:
h[r1].nxt = h[r2].nxt, ce.nxt = r2, ¬(reachable(r, r0, h[r1 := ce]) ↔ false), r0 ≠ r2, r2 ≠ null, reachable(r, r1, h), r2 ∈ h, ¬ reachable(r, r2, h),
¬ reachable(r, r0, h)
⊦
Rule argument
Additional information
Proof step 2 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[r2].nxt, ce.nxt = r2, ¬(reachable(r, r0, h[r1 := ce]) ↔ false), r0 ≠ r2, r2 ≠ null, reachable(r, r1, h), r2 ∈ h, ¬ reachable(r, r2, h),
¬ reachable(r, r0, h)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 3:
h[r1].nxt = h[ce.nxt].nxt, ce.nxt ≠ null, r0 ≠ ce.nxt, reachable(r, r1, h), reachable(r, r0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h, r0 ∈ h[r1 := ce],
¬ reachable(r, ce.nxt, h), ¬ reachable(r, r0, h)
⊦
Rule argument
Additional information
Used simplifier rules:
reach-alloc: ⊦ reachable(r, r1, h) → r1 ∈ h;
Proof step 3 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, ce.nxt ≠ null, r0 ≠ ce.nxt, reachable(r, r1, h), reachable(r, r0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h, r0 ∈ h[r1 := ce],
¬ reachable(r, ce.nxt, h), ¬ reachable(r, r0, h)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 4:
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
- Proof step 5:
h[r1].nxt = h[ce.nxt].nxt, ce.nxt ≠ null, r0 ≠ ce.nxt, reachable(r, r1, h), r0 ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r, ce.nxt, h),
¬ reachable(r, r0, h), ∃ x. path(r ' + x, h[r1 := ce]) ∧ (r ' + x).last = r0
⊦
Rule argument
spec: <toplevel>, name:reachable-def,
seq: ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0),
subst:[h, r0, r] → [h[r1 := ce], r0, r], <all paths>
Additional information
Used terms: h[r1 := ce], r0, r
Proof step 4 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
Proof step 5 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, ce.nxt ≠ null, r0 ≠ ce.nxt, reachable(r, r1, h), r0 ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r, ce.nxt, h),
¬ reachable(r, r0, h), ∃ x. path(r ' + x, h[r1 := ce]) ∧ (r ' + x).last = r0
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 6:
h[r1].nxt = h[ce.nxt].nxt, (r ' + x).last ≠ ce.nxt, ce.nxt ≠ null, path(r ' + x, h[r1 := ce]), reachable(r, r1, h), ce.nxt ∈ h, r1 ∈ h,
(r ' + x).last ∈ h[r1 := ce], ¬ reachable(r, ce.nxt, h), ¬ reachable(r, (r ' + x).last, h)
⊦
Rule argument
Additional information
Proof step 6 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (r ' + x).last ≠ ce.nxt, ce.nxt ≠ null, path(r ' + x, h[r1 := ce]), reachable(r, r1, h), ce.nxt ∈ h, r1 ∈ h,
(r ' + x).last ∈ h[r1 := ce], ¬ reachable(r, ce.nxt, h), ¬ reachable(r, (r ' + x).last, h)
⊦ |
User applied rule structural induction
And obtained the following new goals
- Proof step 7:
h[r1].nxt = h[ce.nxt].nxt, (r ' + (r0 + x0)).last ≠ ce.nxt, ce.nxt ≠ null, path(r ' + (r0 + x0), h[r1 := ce]), reachable(r, r1, h),
(r ' + (r0 + x0)).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r, ce.nxt, h), ¬ reachable(r, (r ' + (r0 + x0)).last, h),
∀ h, r1, ce, r.
¬
( h[r1].nxt = h[ce.nxt].nxt ∧ (r ' + x0).last ≠ ce.nxt ∧ ce.nxt ≠ null ∧ path(r ' + x0, h[r1 := ce]) ∧ reachable(r, r1, h) ∧ ce.nxt ∈ h ∧ r1 ∈ h
∧ (r ' + x0).last ∈ h[r1 := ce] ∧ ¬ reachable(r, ce.nxt, h) ∧ ¬ reachable(r, (r ' + x0).last, h))
⊦
Rule argument
indvar: x
Additional information
Used simplifier rules:
path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null;
self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h;
list('a) freely generated by [], +;;
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a '.last = a; (s)
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
Proof step 7 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (r ' + (r0 + x0)).last ≠ ce.nxt, ce.nxt ≠ null, path(r ' + (r0 + x0), h[r1 := ce]), reachable(r, r1, h),
(r ' + (r0 + x0)).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r, ce.nxt, h), ¬ reachable(r, (r ' + (r0 + x0)).last, h),
∀ h, r1, ce, r.
¬
( h[r1].nxt = h[ce.nxt].nxt ∧ (r ' + x0).last ≠ ce.nxt ∧ ce.nxt ≠ null ∧ path(r ' + x0, h[r1 := ce]) ∧ reachable(r, r1, h) ∧ ce.nxt ∈ h ∧ r1 ∈ h
∧ (r ' + x0).last ∈ h[r1 := ce] ∧ ¬ reachable(r, ce.nxt, h) ∧ ¬ reachable(r, (r ' + x0).last, h))
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 8:
h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), r ∈ h[r1 := ce], ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (r3 ' + x0).last = ce0.nxt ∨ ce0.nxt = null ∨ ¬ path(r3 ' + x0, h0[r2 := ce0]) ∨ ¬ reachable(r3, r2, h0)
∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ ¬ (r3 ' + x0).last ∈ h0[r2 := ce0] ∨ reachable(r3, ce0.nxt, h0) ∨ reachable(r3, (r3 ' + x0).last, h0)
⊦
Rule argument
Additional information
Used simplifier rules:
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ (b ' + a ' + x).last = (a ' + x).last; (s)
⊦ a + x = a ' + x; (s)
Proof step 8 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), r ∈ h[r1 := ce], ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (r3 ' + x0).last = ce0.nxt ∨ ce0.nxt = null ∨ ¬ path(r3 ' + x0, h0[r2 := ce0]) ∨ ¬ reachable(r3, r2, h0)
∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ ¬ (r3 ' + x0).last ∈ h0[r2 := ce0] ∨ reachable(r3, ce0.nxt, h0) ∨ reachable(r3, (r3 ' + x0).last, h0)
⊦ |
User applied rule all left
And obtained the following new goals
- Proof step 9:
h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), ce.nxt ∈ h, r1 ∈ h, ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce], r ∈ h[r1 := ce],
¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
h[r1].nxt ≠ h[ce.nxt].nxt ∨ ((h[r1 := ce])[r].nxt ' + x0).last = ce.nxt ∨ ce.nxt = null ∨ ¬ path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce])
∨ ¬ reachable((h[r1 := ce])[r].nxt, r1, h) ∨ ¬ ce.nxt ∈ h ∨ ¬ r1 ∈ h ∨ ¬ ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce]
∨ reachable((h[r1 := ce])[r].nxt, ce.nxt, h) ∨ reachable((h[r1 := ce])[r].nxt, ((h[r1 := ce])[r].nxt ' + x0).last, h)
⊦
Rule argument
pos: left 13 terms: h, r1, ce, (h[r1 := ce])[r].nxt abort: F discard: T computed: T
Additional information
Used terms: h, r1, ce, (h[r1 := ce])[r].nxt
Proof step 9 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), ce.nxt ∈ h, r1 ∈ h, ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce], r ∈ h[r1 := ce],
¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
h[r1].nxt ≠ h[ce.nxt].nxt ∨ ((h[r1 := ce])[r].nxt ' + x0).last = ce.nxt ∨ ce.nxt = null ∨ ¬ path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce])
∨ ¬ reachable((h[r1 := ce])[r].nxt, r1, h) ∨ ¬ ce.nxt ∈ h ∨ ¬ r1 ∈ h ∨ ¬ ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce]
∨ reachable((h[r1 := ce])[r].nxt, ce.nxt, h) ∨ reachable((h[r1 := ce])[r].nxt, ((h[r1 := ce])[r].nxt ' + x0).last, h)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 10:
h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), r ∈ h[r1 := ce], ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
¬ reachable((h[r1 := ce])[r].nxt, r1, h) ∨ reachable((h[r1 := ce])[r].nxt, ce.nxt, h)
∨ reachable((h[r1 := ce])[r].nxt, ((h[r1 := ce])[r].nxt ' + x0).last, h)
⊦
Rule argument
Additional information
Proof step 10 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), r ∈ h[r1 := ce], ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
¬ reachable((h[r1 := ce])[r].nxt, r1, h) ∨ reachable((h[r1 := ce])[r].nxt, ce.nxt, h)
∨ reachable((h[r1 := ce])[r].nxt, ((h[r1 := ce])[r].nxt ' + x0).last, h)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 11:
⊦ a ≠ b → (st[b := d])[a] = st[a]
- Proof step 12:
h[r1].nxt = h[ce.nxt].nxt, r = r1, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null,
path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h), ce.nxt ∈ h, r1 ∈ h, ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce],
r ∈ h[r1 := ce], ¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
¬ reachable((h[r1 := ce])[r].nxt, r1, h) ∨ reachable((h[r1 := ce])[r].nxt, ce.nxt, h)
∨ reachable((h[r1 := ce])[r].nxt, ((h[r1 := ce])[r].nxt ' + x0).last, h)
⊦
- Proof step 59:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h),
ce.nxt ∈ h, r1 ∈ h, (h[r].nxt ' + x0).last ∈ h[r1 := ce], r ∈ h[r1 := ce], ¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
¬ reachable(h[r].nxt, r1, h) ∨ reachable(h[r].nxt, ce.nxt, h) ∨ reachable(h[r].nxt, (h[r].nxt ' + x0).last, h)
⊦
Rule argument
spec: polystore, name:At-other, seq: ⊦ a ≠ b → (st[b := d])[a] = st[a],
subst:[a, d, b, st] → [r, ce, r1, h]; ['a, 'b] → [Ref, cell], <all paths>
Additional information
Used terms: r, ce, r1, h
Proof step 11 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ a ≠ b → (st[b := d])[a] = st[a] |
A spec-lemma
Proof step 12 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, r = r1, ((h[r1 := ce])[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null,
path((h[r1 := ce])[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h), ce.nxt ∈ h, r1 ∈ h, ((h[r1 := ce])[r].nxt ' + x0).last ∈ h[r1 := ce],
r ∈ h[r1 := ce], ¬ reachable(r, ((h[r1 := ce])[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
¬ reachable((h[r1 := ce])[r].nxt, r1, h) ∨ reachable((h[r1 := ce])[r].nxt, ce.nxt, h)
∨ reachable((h[r1 := ce])[r].nxt, ((h[r1 := ce])[r].nxt ' + x0).last, h)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 13:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦
Rule argument
Additional information
Used simplifier rules:
self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h;
⊦ (st[a := d])[a] = d; (s)
⊦ a ∈ st[a := d]; (s)
Proof step 13 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ |
User applied rule cut formula
And obtained the following new goals
- Proof step 14:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h),
∃ r. reachable(r1, h[r].nxt, h) ∧ path(r ' + x0, h[r1 := ce]) ∧ ¬ reachable(r1, (r ' + x0).last, h)
⊦
- Proof step 43:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ ∃ r. reachable(r1, h[r].nxt, h) ∧ path(r ' + x0, h[r1 := ce]) ∧ ¬ reachable(r1, (r ' + x0).last, h)
Rule argument
fma: ∃ r.
reachable(r1, h[r].nxt, h) ∧ path(r ' + x0, h[r1 := ce])
∧ ¬ reachable(r1, (r ' + x0).last, h)
Additional information
Used formulas: ∃ r.
reachable(r1, h[r].nxt, h) ∧ path(r ' + x0, h[r1 := ce])
∧ ¬ reachable(r1, (r ' + x0).last, h)
Proof step 14 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h),
∃ r. reachable(r1, h[r].nxt, h) ∧ path(r ' + x0, h[r1 := ce]) ∧ ¬ reachable(r1, (r ' + x0).last, h)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 15:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(r ' + x0, h[r1 := ce]), path(ce.nxt ' + x0, h[r1 := ce]),
reachable(r1, h[r].nxt, h), (ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ¬ reachable(r1, ce.nxt, h),
¬ reachable(r1, (ce.nxt ' + x0).last, h), ¬ reachable(r1, (r ' + x0).last, h)
⊦
Rule argument
Additional information
Used simplifier rules:
reach-alloc: ⊦ reachable(r, r1, h) → r1 ∈ h;
Proof step 15 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(r ' + x0, h[r1 := ce]), path(ce.nxt ' + x0, h[r1 := ce]),
reachable(r1, h[r].nxt, h), (ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ¬ reachable(r1, ce.nxt, h),
¬ reachable(r1, (ce.nxt ' + x0).last, h), ¬ reachable(r1, (r ' + x0).last, h)
⊦ |
User applied rule weakening
And obtained the following new goals
- Proof step 16:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(r ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h),
ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h), ¬ reachable(r1, (r ' + x0).last, h)
⊦
Rule argument
poslist: left 6, left 8, left 11
Additional information
Proof step 16 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(r ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h),
ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h), ¬ reachable(r1, (r ' + x0).last, h)
⊦ |
User applied rule structural induction
And obtained the following new goals
- Proof step 17:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + (r0 + x)).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(r ' + (r0 + x), h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + (r0 + x)).last, h),
¬ reachable(r1, (r ' + (r0 + x)).last, h),
∀ h, r1, ce, r.
¬
( h[r1].nxt = h[ce.nxt].nxt ∧ (ce.nxt ' + x).last ≠ ce.nxt ∧ ce.nxt ≠ null ∧ r1 ≠ null ∧ path(r ' + x, h[r1 := ce]) ∧ reachable(r1, h[r].nxt, h)
∧ ce.nxt ∈ h ∧ r1 ∈ h ∧ ¬ reachable(r1, ce.nxt, h) ∧ ¬ reachable(r1, (ce.nxt ' + x).last, h) ∧ ¬ reachable(r1, (r ' + x).last, h))
⊦
Rule argument
indvar: x0
Additional information
Used simplifier rules:
list('a) freely generated by [], +;;
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a '.last = a; (s)
Proof step 17 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + (r0 + x)).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(r ' + (r0 + x), h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + (r0 + x)).last, h),
¬ reachable(r1, (r ' + (r0 + x)).last, h),
∀ h, r1, ce, r.
¬
( h[r1].nxt = h[ce.nxt].nxt ∧ (ce.nxt ' + x).last ≠ ce.nxt ∧ ce.nxt ≠ null ∧ r1 ≠ null ∧ path(r ' + x, h[r1 := ce]) ∧ reachable(r1, h[r].nxt, h)
∧ ce.nxt ∈ h ∧ r1 ∈ h ∧ ¬ reachable(r1, ce.nxt, h) ∧ ¬ reachable(r1, (ce.nxt ' + x).last, h) ∧ ¬ reachable(r1, (r ' + x).last, h))
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 18:
h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, r1 ≠ null,
path((h[r1 := ce])[r].nxt ' + x, h[r1 := ce]), reachable(r1, h[r].nxt, h), r ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r1, ((h[r1 := ce])[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦
Rule argument
Additional information
Used simplifier rules:
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ (b ' + a ' + x).last = (a ' + x).last; (s)
⊦ a + x = a ' + x; (s)
Proof step 18 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, r1 ≠ null,
path((h[r1 := ce])[r].nxt ' + x, h[r1 := ce]), reachable(r1, h[r].nxt, h), r ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r1, ((h[r1 := ce])[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 19:
⊦ a ≠ b → (st[b := d])[a] = st[a]
- Proof step 20:
h[r1].nxt = h[ce.nxt].nxt, r = r1, ((h[r1 := ce])[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, r1 ≠ null,
path((h[r1 := ce])[r].nxt ' + x, h[r1 := ce]), reachable(r1, h[r].nxt, h), ce.nxt ∈ h, r1 ∈ h, r ∈ h[r1 := ce],
¬ reachable(r1, ((h[r1 := ce])[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦
- Proof step 22:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), ce.nxt ∈ h, r1 ∈ h, r ∈ h[r1 := ce], ¬ reachable(r1, (h[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦
Rule argument
spec: polystore, name:At-other, seq: ⊦ a ≠ b → (st[b := d])[a] = st[a],
subst:[a, d, b, st] → [r, ce, r1, h]; ['a, 'b] → [Ref, cell], <all paths>
Additional information
Used terms: r, ce, r1, h
Proof step 19 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ a ≠ b → (st[b := d])[a] = st[a] |
A spec-lemma
Proof step 20 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, r = r1, ((h[r1 := ce])[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ null, r1 ≠ null,
path((h[r1 := ce])[r].nxt ' + x, h[r1 := ce]), reachable(r1, h[r].nxt, h), ce.nxt ∈ h, r1 ∈ h, r ∈ h[r1 := ce],
¬ reachable(r1, ((h[r1 := ce])[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 21:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x, h[r1 := ce]), reachable(r1, h[r1].nxt, h),
r1 ∈ h, ce.nxt ∈ h, h[r1].nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x).last, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦
Rule argument
Additional information
Used simplifier rules:
reach-alloc: ⊦ reachable(r, r1, h) → r1 ∈ h;
⊦ (st[a := d])[a] = d; (s)
⊦ a ∈ st[a := d]; (s)
Proof step 21 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x, h[r1 := ce]), reachable(r1, h[r1].nxt, h),
r1 ∈ h, ce.nxt ∈ h, h[r1].nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x).last, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦ |
User applied rule all left
And closed the goal!
Rule argument
pos: left 12 terms: h, r1, ce, ce.nxt abort: F discard: T computed: T
Additional information
Used simplifier rules:
reachnext: ⊦ reachable(r0, h[r0].nxt, h) ↔ r0 ≠ null ∧ r0 ∈ h ∧ h[r0].nxt ∈ h ∧ h[r0].nxt ≠ null;
Used terms: h, r1, ce, ce.nxt
Proof step 22 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), ce.nxt ∈ h, r1 ∈ h, r ∈ h[r1 := ce], ¬ reachable(r1, (h[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 23:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(r1, (h[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦
Rule argument
Additional information
Used simplifier rules:
⊦ a ≠ b → (a ∈ st[b := d] ↔ a ∈ st); (s)
Proof step 23 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(r1, (h[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦ |
Heuristic weak cut applied rule cut formula
And obtained the following new goals
- Proof step 24:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, (h[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦
Rule argument
fma: x = []
Additional information
Used simplifier rules:
path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null;
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a '.last = a; (s)
Used formulas: x = []
Proof step 24 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, (h[r].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ (ce0.nxt ' + x).last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0])
∨ ¬ reachable(r2, h0[r3].nxt, h0) ∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, (ce0.nxt ' + x).last, h0)
∨ reachable(r2, (r3 ' + x).last, h0)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 25:
h[r1].nxt = h[ce.nxt].nxt, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ x.last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0]) ∨ ¬ reachable(r2, h0[r3].nxt, h0)
∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, x.last, h0)
⊦
Rule argument
Additional information
Used simplifier rules:
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ x ≠ [] → (a ' + x).last = x.last; (s)
Proof step 25 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h),
∀ h0, r2, ce0, r3.
h0[r2].nxt ≠ h0[ce0.nxt].nxt ∨ x.last = ce0.nxt ∨ ce0.nxt = null ∨ r2 = null ∨ ¬ path(r3 ' + x, h0[r2 := ce0]) ∨ ¬ reachable(r2, h0[r3].nxt, h0)
∨ ¬ ce0.nxt ∈ h0 ∨ ¬ r2 ∈ h0 ∨ reachable(r2, ce0.nxt, h0) ∨ reachable(r2, x.last, h0)
⊦ |
User applied rule all left
And obtained the following new goals
- Proof step 26:
h[r1].nxt = h[ce.nxt].nxt, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h),
h[r1].nxt ≠ h[ce.nxt].nxt ∨ x.last = ce.nxt ∨ ce.nxt = null ∨ r1 = null ∨ ¬ path(h[r].nxt ' + x, h[r1 := ce]) ∨ ¬ reachable(r1, h[h[r].nxt].nxt, h)
∨ ¬ ce.nxt ∈ h ∨ ¬ r1 ∈ h ∨ reachable(r1, ce.nxt, h) ∨ reachable(r1, x.last, h)
⊦
Rule argument
pos: left 15 terms: h, r1, ce, h[r].nxt abort: F discard: T computed: T
Additional information
Used terms: h, r1, ce, h[r].nxt
Proof step 26 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h),
h[r1].nxt ≠ h[ce.nxt].nxt ∨ x.last = ce.nxt ∨ ce.nxt = null ∨ r1 = null ∨ ¬ path(h[r].nxt ' + x, h[r1 := ce]) ∨ ¬ reachable(r1, h[h[r].nxt].nxt, h)
∨ ¬ ce.nxt ∈ h ∨ ¬ r1 ∈ h ∨ reachable(r1, ce.nxt, h) ∨ reachable(r1, x.last, h)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 27:
h[r1].nxt = h[ce.nxt].nxt, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h
Rule argument
Additional information
Used simplifier rules:
reach-reachnext: ⊦ reachable(r, r1, h)
→ (reachable(r, h[r1].nxt, h) ↔ ¬(h[r1].nxt = null ∨ ¬ h[r1].nxt ∈ h));
Proof step 27 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h |
User applied rule constructor cut
And obtained the following new goals
- Proof step 28:
h[r1].nxt = h[ce.nxt].nxt, x = r0 + x0, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h
Rule argument
var: x
Additional information
Used simplifier rules:
list('a) freely generated by [], +;;
Proof step 28 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, x = r0 + x0, x.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, r1 ≠ null, x ≠ [], path(h[r].nxt ' + x, h[r1 := ce]),
reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, x.last, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 29:
h[r1].nxt = h[ce.nxt].nxt, (h[r1 := ce])[h[r].nxt].nxt ' + x0 ≠ [], ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ null, ce.nxt ≠ null,
r ≠ null, r ≠ r1, r1 ≠ null, path((h[r1 := ce])[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), h[r].nxt ∈ h[r1 := ce], r ∈ h,
ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h
Rule argument
Additional information
Used simplifier rules:
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
⊦ a + x = a ' + x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
Proof step 29 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r1 := ce])[h[r].nxt].nxt ' + x0 ≠ [], ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ null, ce.nxt ≠ null,
r ≠ null, r ≠ r1, r1 ≠ null, path((h[r1 := ce])[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), h[r].nxt ∈ h[r1 := ce], r ∈ h,
ce.nxt ∈ h, r1 ∈ h, ¬ reachable(r1, ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 30:
⊦ a ≠ b → (st[b := d])[a] = st[a]
- Proof step 31:
h[r].nxt = r1, h[r1].nxt = h[ce.nxt].nxt, (h[r1 := ce])[h[r].nxt].nxt ' + x0 ≠ [], ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ null,
ce.nxt ≠ null, r ≠ null, r ≠ r1, r1 ≠ null, path((h[r1 := ce])[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h,
r ∈ h, h[r].nxt ∈ h[r1 := ce], ¬ reachable(r1, ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h
- Proof step 41:
h[r1].nxt = h[ce.nxt].nxt, h[h[r].nxt].nxt ' + x0 ≠ [], (h[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ r1, h[r].nxt ≠ null, ce.nxt ≠ null,
r ≠ null, r ≠ r1, r1 ≠ null, path(h[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, h[r].nxt ∈ h[r1 := ce],
¬ reachable(r1, (h[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h
Rule argument
spec: polystore, name:At-other, seq: ⊦ a ≠ b → (st[b := d])[a] = st[a],
subst:[a, d, b, st] → [h[r].nxt, ce, r1, h]; ['a, 'b] → [Ref, cell], <all paths>
Additional information
Used terms: h[r].nxt, ce, r1, h
Proof step 30 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ a ≠ b → (st[b := d])[a] = st[a] |
A spec-lemma
Proof step 31 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r].nxt = r1, h[r1].nxt = h[ce.nxt].nxt, (h[r1 := ce])[h[r].nxt].nxt ' + x0 ≠ [], ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ null,
ce.nxt ≠ null, r ≠ null, r ≠ r1, r1 ≠ null, path((h[r1 := ce])[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h,
r ∈ h, h[r].nxt ∈ h[r1 := ce], ¬ reachable(r1, ((h[r1 := ce])[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 32:
h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + x0 ≠ [], (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, h[r].nxt ≠ null, r ≠ null, r ≠ h[r].nxt,
path(ce.nxt ' + x0, h[h[r].nxt := ce]), r ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ¬ reachable(h[r].nxt, ce.nxt, h),
¬ reachable(h[r].nxt, (ce.nxt ' + x0).last, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h
Rule argument
Additional information
Used simplifier rules:
self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h;
⊦ (st[a := d])[a] = d; (s)
⊦ a ∈ st[a := d]; (s)
Proof step 32 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + x0 ≠ [], (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, h[r].nxt ≠ null, r ≠ null, r ≠ h[r].nxt,
path(ce.nxt ' + x0, h[h[r].nxt := ce]), r ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ¬ reachable(h[r].nxt, ce.nxt, h),
¬ reachable(h[r].nxt, (ce.nxt ' + x0).last, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h |
User applied rule constructor cut
And obtained the following new goals
- Proof step 33:
h[h[r].nxt].nxt = h[ce.nxt].nxt, x0 = r0 + x, ce.nxt ' + x0 ≠ [], (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, h[r].nxt ≠ null, r ≠ null,
r ≠ h[r].nxt, path(ce.nxt ' + x0, h[h[r].nxt := ce]), h[r].nxt ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(h[r].nxt, ce.nxt, h),
¬ reachable(h[r].nxt, (ce.nxt ' + x0).last, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h
Rule argument
var: x0
Additional information
Used simplifier rules:
list('a) freely generated by [], +;;
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a '.last = a; (s)
Proof step 33 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[h[r].nxt].nxt = h[ce.nxt].nxt, x0 = r0 + x, ce.nxt ' + x0 ≠ [], (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, h[r].nxt ≠ null, r ≠ null,
r ≠ h[r].nxt, path(ce.nxt ' + x0, h[h[r].nxt := ce]), h[r].nxt ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(h[r].nxt, ce.nxt, h),
¬ reachable(h[r].nxt, (ce.nxt ' + x0).last, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 34:
h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + x ≠ [], ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt,
h[r].nxt ≠ null, ce.nxt ≠ null, r ≠ h[r].nxt, r ≠ null, path((h[h[r].nxt := ce])[ce.nxt].nxt ' + x, h[h[r].nxt := ce]), ce.nxt ∈ h[h[r].nxt := ce],
h[r].nxt ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h
Rule argument
Additional information
Used simplifier rules:
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ (b ' + a ' + x).last = (a ' + x).last; (s)
⊦ a + x = a ' + x; (s)
Proof step 34 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + x ≠ [], ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt,
h[r].nxt ≠ null, ce.nxt ≠ null, r ≠ h[r].nxt, r ≠ null, path((h[h[r].nxt := ce])[ce.nxt].nxt ' + x, h[h[r].nxt := ce]), ce.nxt ∈ h[h[r].nxt := ce],
h[r].nxt ∈ h, ce.nxt ∈ h, r ∈ h, ¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h |
User applied rule constructor cut
And obtained the following new goals
- Proof step 35:
h[h[r].nxt].nxt = h[ce.nxt].nxt, x = [], ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + x ≠ [], ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt,
h[r].nxt ≠ null, ce.nxt ≠ null, r ≠ h[r].nxt, r ≠ null, path((h[h[r].nxt := ce])[ce.nxt].nxt ' + x, h[h[r].nxt := ce]), r ∈ h, ce.nxt ∈ h,
h[r].nxt ∈ h, ce.nxt ∈ h[h[r].nxt := ce], ¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h
- Proof step 38:
h[h[r].nxt].nxt = h[ce.nxt].nxt, x = r0 + x1, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + x ≠ [],
((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt, h[r].nxt ≠ null, ce.nxt ≠ null, r ≠ h[r].nxt, r ≠ null,
path((h[h[r].nxt := ce])[ce.nxt].nxt ' + x, h[h[r].nxt := ce]), r ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ce.nxt ∈ h[h[r].nxt := ce],
¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h
Rule argument
var: x
Additional information
Used simplifier rules:
list('a) freely generated by [], +;;
Proof step 35 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[h[r].nxt].nxt = h[ce.nxt].nxt, x = [], ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + x ≠ [], ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt,
h[r].nxt ≠ null, ce.nxt ≠ null, r ≠ h[r].nxt, r ≠ null, path((h[h[r].nxt := ce])[ce.nxt].nxt ' + x, h[h[r].nxt := ce]), r ∈ h, ce.nxt ∈ h,
h[r].nxt ∈ h, ce.nxt ∈ h[h[r].nxt := ce], ¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 36:
h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' ≠ [], h[r].nxt ≠ null, ce.nxt ≠ null,
(h[h[r].nxt := ce])[ce.nxt].nxt ≠ ce.nxt, (h[h[r].nxt := ce])[ce.nxt].nxt ≠ null, r ≠ h[r].nxt, r ≠ null, ce.nxt ∈ h[h[r].nxt := ce], h[r].nxt ∈ h,
ce.nxt ∈ h, r ∈ h, (h[h[r].nxt := ce])[ce.nxt].nxt ∈ h[h[r].nxt := ce], ¬ reachable(h[r].nxt, ce.nxt, h),
¬ reachable(h[r].nxt, (h[h[r].nxt := ce])[ce.nxt].nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h
Rule argument
Additional information
Used simplifier rules:
path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null;
⊦ a '.last = a; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ x + [] = x; (s)
Proof step 36 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' ≠ [], h[r].nxt ≠ null, ce.nxt ≠ null,
(h[h[r].nxt := ce])[ce.nxt].nxt ≠ ce.nxt, (h[h[r].nxt := ce])[ce.nxt].nxt ≠ null, r ≠ h[r].nxt, r ≠ null, ce.nxt ∈ h[h[r].nxt := ce], h[r].nxt ∈ h,
ce.nxt ∈ h, r ∈ h, (h[h[r].nxt := ce])[ce.nxt].nxt ∈ h[h[r].nxt := ce], ¬ reachable(h[r].nxt, ce.nxt, h),
¬ reachable(h[r].nxt, (h[h[r].nxt := ce])[ce.nxt].nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h |
User applied rule apply rewrite lemma
And obtained the following new goals
Rule argument
spec: polystore, name:At-other, seq: ⊦ a ≠ b → (st[b := d])[a] = st[a],
subst:[a, d, b, st] → [ce.nxt, ce, h[r].nxt, h]; ['a, 'b] → [Ref, cell], <all paths>
Additional information
Used simplifier rules:
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
⊦ a = b → (st[b := d])[a] = d; (s)
Used terms: ce.nxt, ce, h[r].nxt, h
Proof step 37 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ a ≠ b → (st[b := d])[a] = st[a] |
A spec-lemma
Proof step 38 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[h[r].nxt].nxt = h[ce.nxt].nxt, x = r0 + x1, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + x ≠ [],
((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt, h[r].nxt ≠ null, ce.nxt ≠ null, r ≠ h[r].nxt, r ≠ null,
path((h[h[r].nxt := ce])[ce.nxt].nxt ' + x, h[h[r].nxt := ce]), r ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ce.nxt ∈ h[h[r].nxt := ce],
¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 39:
h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + (h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1 ≠ [],
((h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1).last ≠ ce.nxt, (h[h[r].nxt := ce])[ce.nxt].nxt ≠ null, ce.nxt ≠ null,
h[r].nxt ≠ null, r ≠ null, r ≠ h[r].nxt, path((h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1, h[h[r].nxt := ce]),
(h[h[r].nxt := ce])[ce.nxt].nxt ∈ h[h[r].nxt := ce], r ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ce.nxt ∈ h[h[r].nxt := ce],
¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h
Rule argument
Additional information
Used simplifier rules:
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ (b ' + a ' + x).last = (a ' + x).last; (s)
⊦ a + x = a ' + x; (s)
Proof step 39 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[h[r].nxt].nxt = h[ce.nxt].nxt, ce.nxt ' + (h[h[r].nxt := ce])[ce.nxt].nxt ' + (h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1 ≠ [],
((h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1).last ≠ ce.nxt, (h[h[r].nxt := ce])[ce.nxt].nxt ≠ null, ce.nxt ≠ null,
h[r].nxt ≠ null, r ≠ null, r ≠ h[r].nxt, path((h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1, h[h[r].nxt := ce]),
(h[h[r].nxt := ce])[ce.nxt].nxt ∈ h[h[r].nxt := ce], r ∈ h, ce.nxt ∈ h, h[r].nxt ∈ h, ce.nxt ∈ h[h[r].nxt := ce],
¬ reachable(h[r].nxt, ((h[h[r].nxt := ce])[(h[h[r].nxt := ce])[ce.nxt].nxt].nxt ' + x1).last, h), ¬ reachable(h[r].nxt, ce.nxt, h)
⊦ h[ce.nxt].nxt ≠ null ∧ h[ce.nxt].nxt ∈ h |
User applied rule apply rewrite lemma
And obtained the following new goals
Rule argument
spec: polystore, name:At-other, seq: ⊦ a ≠ b → (st[b := d])[a] = st[a],
subst:[a, d, b, st] → [ce.nxt, ce, h[r].nxt, h]; ['a, 'b] → [Ref, cell], <all paths>
Additional information
Used simplifier rules:
self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h;
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
⊦ a = b → (st[b := d])[a] = d; (s)
⊦ a ∈ st[a := d]; (s)
Used terms: ce.nxt, ce, h[r].nxt, h
Proof step 40 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ a ≠ b → (st[b := d])[a] = st[a] |
A spec-lemma
Proof step 41 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, h[h[r].nxt].nxt ' + x0 ≠ [], (h[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ r1, h[r].nxt ≠ null, ce.nxt ≠ null,
r ≠ null, r ≠ r1, r1 ≠ null, path(h[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), r1 ∈ h, ce.nxt ∈ h, r ∈ h, h[r].nxt ∈ h[r1 := ce],
¬ reachable(r1, (h[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 42:
h[r1].nxt = h[ce.nxt].nxt, h[h[r].nxt].nxt ' + x0 ≠ [], (h[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ r1, h[r].nxt ≠ null, ce.nxt ≠ null,
r ≠ null, r ≠ r1, r1 ≠ null, path(h[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, h[r].nxt ∈ h,
¬ reachable(r1, (h[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h
Rule argument
Additional information
Used simplifier rules:
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
Proof step 42 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, h[h[r].nxt].nxt ' + x0 ≠ [], (h[h[r].nxt].nxt ' + x0).last ≠ ce.nxt, h[r].nxt ≠ r1, h[r].nxt ≠ null, ce.nxt ≠ null,
r ≠ null, r ≠ r1, r1 ≠ null, path(h[h[r].nxt].nxt ' + x0, h[r1 := ce]), reachable(r1, h[r].nxt, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, h[r].nxt ∈ h,
¬ reachable(r1, (h[h[r].nxt].nxt ' + x0).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[h[r].nxt].nxt ≠ null ∧ h[h[r].nxt].nxt ∈ h |
User applied rule constructor cut
And closed the goal!
Rule argument
var: x0
Additional information
Used simplifier rules:
path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null;
reach-reachnext: ⊦ reachable(r, r1, h)
→ (reachable(r, h[r1].nxt, h) ↔ ¬(h[r1].nxt = null ∨ ¬ h[r1].nxt ∈ h));
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
list('a) freely generated by [], +;;
⊦ a + x = a ' + x; (s)
⊦ (b ' + a ' + x).last = (a ' + x).last; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
⊦ a = b → (st[b := d])[a] = d; (s)
⊦ x + [] = x; (s)
⊦ a '.last = a; (s)
Proof step 43 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ ∃ r. reachable(r1, h[r].nxt, h) ∧ path(r ' + x0, h[r1 := ce]) ∧ ¬ reachable(r1, (r ' + x0).last, h) |
User applied rule exists right
And obtained the following new goals
- Proof step 44:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ reachable(r1, h[ce.nxt].nxt, h) ∧ path(ce.nxt ' + x0, h[r1 := ce]) ∧ ¬ reachable(r1, (ce.nxt ' + x0).last, h)
Rule argument
pos: right 1 terms: ce.nxt abort: F discard: T computed: T
Additional information
Used terms: ce.nxt
Proof step 44 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ reachable(r1, h[ce.nxt].nxt, h) ∧ path(ce.nxt ' + x0, h[r1 := ce]) ∧ ¬ reachable(r1, (ce.nxt ' + x0).last, h) |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 45:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h), ¬ reachable(r1, h[r1].nxt, h)
⊦
Rule argument
Additional information
Proof step 45 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h), ¬ reachable(r1, h[r1].nxt, h)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 46:
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
- Proof step 47:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h),
∀ x. ¬(path(r1 ' + x, h) ∧ (r1 ' + x).last = h[r1].nxt)
⊦
Rule argument
spec: <toplevel>, name:reachable-def,
seq: ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0),
subst:[h, r0, r] → [h, h[r1].nxt, r1], <all paths>
Additional information
Used terms: h, h[r1].nxt, r1
Proof step 46 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
Proof step 47 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h),
∀ x. ¬(path(r1 ' + x, h) ∧ (r1 ' + x).last = h[r1].nxt)
⊦ |
User applied rule all left
And obtained the following new goals
- Proof step 48:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ path(r1 ' + h[r1].nxt ', h) ∧ (r1 ' + h[r1].nxt ').last = h[r1].nxt
Rule argument
pos: left 11 terms: h[r1].nxt ' abort: F discard: T computed: F
Additional information
Used terms: h[r1].nxt '
Proof step 48 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ path(r1 ' + h[r1].nxt ', h) ∧ (r1 ' + h[r1].nxt ').last = h[r1].nxt |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 49:
h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null
Rule argument
Additional information
Used simplifier rules:
path-two: ⊦ path(r ' + r0 ', h) ↔ r ∈ h ∧ r0 ∈ h ∧ r ≠ null ∧ r0 ≠ null ∧ h[r].nxt = r0;
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ (x + a ').last = a; (s)
Proof step 49 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]),
(ce.nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null |
User applied rule constructor cut
And obtained the following new goals
- Proof step 50:
h[r1].nxt = h[ce.nxt].nxt, x0 = r + x, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null
Rule argument
var: x0
Additional information
Used simplifier rules:
list('a) freely generated by [], +;;
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a '.last = a; (s)
Proof step 50 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, x0 = r + x, (ce.nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null, path(ce.nxt ' + x0, h[r1 := ce]), ce.nxt ∈ h, r1 ∈ h,
(ce.nxt ' + x0).last ∈ h[r1 := ce], ¬ reachable(r1, ce.nxt, h), ¬ reachable(r1, (ce.nxt ' + x0).last, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 51:
h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null,
path((h[r1 := ce])[ce.nxt].nxt ' + x, h[r1 := ce]), ce.nxt ∈ h[r1 := ce], ce.nxt ∈ h, r1 ∈ h, ((h[r1 := ce])[ce.nxt].nxt ' + x).last ∈ h[r1 := ce],
¬ reachable(r1, ((h[r1 := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null
Rule argument
Additional information
Used simplifier rules:
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ (b ' + a ' + x).last = (a ' + x).last; (s)
⊦ a + x = a ' + x; (s)
Proof step 51 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, ((h[r1 := ce])[ce.nxt].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ null, r1 ≠ null,
path((h[r1 := ce])[ce.nxt].nxt ' + x, h[r1 := ce]), ce.nxt ∈ h[r1 := ce], ce.nxt ∈ h, r1 ∈ h, ((h[r1 := ce])[ce.nxt].nxt ' + x).last ∈ h[r1 := ce],
¬ reachable(r1, ((h[r1 := ce])[ce.nxt].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 52:
⊦ a ≠ b → (st[b := d])[a] = st[a]
- Proof step 53:
h[r1].nxt = h[ce.nxt].nxt, (h[ce.nxt].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[ce.nxt].nxt ' + x, h[r1 := ce]),
(h[ce.nxt].nxt ' + x).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ce.nxt ∈ h[r1 := ce], ¬ reachable(r1, (h[ce.nxt].nxt ' + x).last, h),
¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null
Rule argument
spec: polystore, name:At-other, seq: ⊦ a ≠ b → (st[b := d])[a] = st[a],
subst:[a, d, b, st] → [ce.nxt, ce, r1, h]; ['a, 'b] → [Ref, cell], <all paths>
Additional information
Used simplifier rules:
self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h;
⊦ a ∈ st[a := d]; (s)
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
⊦ (st[a := d])[a] = d; (s)
Used terms: ce.nxt, ce, r1, h
Proof step 52 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ a ≠ b → (st[b := d])[a] = st[a] |
A spec-lemma
Proof step 53 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[ce.nxt].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[ce.nxt].nxt ' + x, h[r1 := ce]),
(h[ce.nxt].nxt ' + x).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ce.nxt ∈ h[r1 := ce], ¬ reachable(r1, (h[ce.nxt].nxt ' + x).last, h),
¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 54:
h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), r1 ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], ce.nxt ∈ h, ¬ reachable(r1, (h[r1].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null
Rule argument
Additional information
Used simplifier rules:
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
Proof step 54 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), r1 ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], ce.nxt ∈ h, ¬ reachable(r1, (h[r1].nxt ' + x).last, h), ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 55:
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
- Proof step 56:
h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), ce.nxt ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ∀ x0. ¬(path(r1 ' + x0, h) ∧ (r1 ' + x0).last = (h[r1].nxt ' + x).last)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null
Rule argument
spec: <toplevel>, name:reachable-def,
seq: ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0),
subst:[h, r0, r] → [h, (h[r1].nxt ' + x).last, r1], <all paths>
Additional information
Used terms: h, (h[r1].nxt ' + x).last, r1
Proof step 55 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
Proof step 56 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), ce.nxt ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], r1 ∈ h, ¬ reachable(r1, ce.nxt, h), ∀ x0. ¬(path(r1 ' + x0, h) ∧ (r1 ' + x0).last = (h[r1].nxt ' + x).last)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null |
User applied rule all left
And obtained the following new goals
- Proof step 57:
h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), r1 ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null, path(r1 ' + h[r1].nxt ', h) ∧ (r1 ' + h[r1].nxt ').last = (h[r1].nxt ' + x).last
Rule argument
pos: left 11 terms: h[r1].nxt ' abort: F discard: T computed: F
Additional information
Used terms: h[r1].nxt '
Proof step 57 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), r1 ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], ce.nxt ∈ h, ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null, path(r1 ' + h[r1].nxt ', h) ∧ (r1 ' + h[r1].nxt ').last = (h[r1].nxt ' + x).last |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 58:
h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), ce.nxt ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], r1 ∈ h, ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null
Rule argument
Additional information
Used simplifier rules:
path-two: ⊦ path(r ' + r0 ', h) ↔ r ∈ h ∧ r0 ∈ h ∧ r ≠ null ∧ r0 ≠ null ∧ h[r].nxt = r0;
a: ⊦ (x + y) + z = x + y + z; from specification polylist
Proof step 58 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r1].nxt ' + x).last ≠ ce.nxt, ce.nxt ≠ r1, ce.nxt ≠ null, r1 ≠ null, path(h[r1].nxt ' + x, h[r1 := ce]), ce.nxt ∈ h,
(h[r1].nxt ' + x).last ∈ h[r1 := ce], r1 ∈ h, ¬ reachable(r1, ce.nxt, h)
⊦ h[r1].nxt ∈ h ∧ h[r1].nxt ≠ null |
User applied rule constructor cut
And closed the goal!
Rule argument
var: x
Additional information
Used simplifier rules:
path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null;
path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h);
list('a) freely generated by [], +;;
⊦ (b ' + a ' + x).last = (a ' + x).last; (s)
⊦ a + x = a ' + x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
⊦ a = b → (st[b := d])[a] = d; (s)
⊦ a '.last = a; (s)
⊦ x + [] = x; (s)
Proof step 59 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h),
ce.nxt ∈ h, r1 ∈ h, (h[r].nxt ' + x0).last ∈ h[r1 := ce], r ∈ h[r1 := ce], ¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h),
¬ reachable(h[r].nxt, r1, h) ∨ reachable(h[r].nxt, ce.nxt, h) ∨ reachable(h[r].nxt, (h[r].nxt ' + x0).last, h)
⊦ |
User applied rule case distinction
And obtained the following new goals
- Proof step 60:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h),
reachable(h[r].nxt, ce.nxt, h), r ∈ h[r1 := ce], (h[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r, (h[r].nxt ' + x0).last, h),
¬ reachable(r, ce.nxt, h)
⊦
- Proof step 65:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h),
reachable(h[r].nxt, (h[r].nxt ' + x0).last, h), r ∈ h[r1 := ce], (h[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h)
⊦
Rule argument
pos: left 14
Additional information
Used simplifier rules:
fromnext-reachable: ⊦ reachable(r, r0, h) ∧ r ≠ r0 → (reachable(h[r].nxt, r0, h) ↔ true);
⊦ a ≠ b → (a ∈ st[b := d] ↔ a ∈ st); (s)
Proof step 60 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h),
reachable(h[r].nxt, ce.nxt, h), r ∈ h[r1 := ce], (h[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h, ¬ reachable(r, (h[r].nxt ' + x0).last, h),
¬ reachable(r, ce.nxt, h)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 61:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]),
reachable(h[r].nxt, ce.nxt, h), reachable(r, r1, h), r1 ∈ h, (h[r].nxt ' + x0).last ∈ h[r1 := ce], r ∈ h, ce.nxt ∈ h,
¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h)
⊦
Rule argument
Additional information
Used simplifier rules:
reach-alloc: ⊦ reachable(r, r1, h) → r1 ∈ h;
⊦ a ≠ b → (a ∈ st[b := d] ↔ a ∈ st); (s)
Proof step 61 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]),
reachable(h[r].nxt, ce.nxt, h), reachable(r, r1, h), r1 ∈ h, (h[r].nxt ' + x0).last ∈ h[r1 := ce], r ∈ h, ce.nxt ∈ h,
¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h)
⊦ |
Heuristic weak cut applied rule cut formula
And obtained the following new goals
- Proof step 62:
h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, x0 ≠ [], path(h[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), reachable(h[r].nxt, ce.nxt, h), ce.nxt ∈ h, r ∈ h, (h[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h,
¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h)
⊦
Rule argument
fma: x0 = []
Additional information
Used simplifier rules:
path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null;
reachnext: ⊦ reachable(r0, h[r0].nxt, h) ↔ r0 ≠ null ∧ r0 ∈ h ∧ h[r0].nxt ∈ h ∧ h[r0].nxt ≠ null;
startnotinH-notreachable: ⊦ ¬ r ∈ h → (reachable(r, r0, h) ↔ false);
⊦ x + [] = x; (s)
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ a '.last = a; (s)
Used formulas: x0 = []
Proof step 62 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, x0 ≠ [], path(h[r].nxt ' + x0, h[r1 := ce]),
reachable(r, r1, h), reachable(h[r].nxt, ce.nxt, h), ce.nxt ∈ h, r ∈ h, (h[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h,
¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h)
⊦ |
Heuristic simplifier applied rule simplifier
And obtained the following new goals
- Proof step 63:
h[r1].nxt = h[ce.nxt].nxt, x0.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, x0 ≠ [], path(h[r].nxt ' + x0, h[r1 := ce]),
reachable(h[r].nxt, ce.nxt, h), reachable(r, r1, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, x0.last ∈ h[r1 := ce], ¬ reachable(r, ce.nxt, h),
¬ reachable(r, x0.last, h)
⊦
Rule argument
Additional information
Used simplifier rules:
a: ⊦ (x + y) + z = x + y + z; from specification polylist
⊦ x ≠ [] → (a ' + x).last = x.last; (s)
Proof step 63 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, x0.last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, x0 ≠ [], path(h[r].nxt ' + x0, h[r1 := ce]),
reachable(h[r].nxt, ce.nxt, h), reachable(r, r1, h), r ∈ h, ce.nxt ∈ h, r1 ∈ h, x0.last ∈ h[r1 := ce], ¬ reachable(r, ce.nxt, h),
¬ reachable(r, x0.last, h)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 64:
⊦ reachable(h[r].nxt, r0, h) ∧ r ≠ r0 ∧ r ≠ null ∧ r ∈ h → (reachable(r, r0, h) ↔ true)
Rule argument
spec: <toplevel>, name:fromnext-reachable-rev,
seq:⊦ reachable(h[r].nxt, r0, h) ∧ r ≠ r0 ∧ r ≠ null ∧ r ∈ h
→ (reachable(r, r0, h) ↔ true),
subst:[h, r0, r] → [h, ce.nxt, r], <all paths>
Additional information
Used simplifier rules:
self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h;
Used terms: h, ce.nxt, r
Proof step 64 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ reachable(h[r].nxt, r0, h) ∧ r ≠ r0 ∧ r ≠ null ∧ r ∈ h → (reachable(r, r0, h) ↔ true) |
Proof step 65 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| h[r1].nxt = h[ce.nxt].nxt, (h[r].nxt ' + x0).last ≠ ce.nxt, ce.nxt ≠ null, r ≠ r1, r ≠ null, path(h[r].nxt ' + x0, h[r1 := ce]), reachable(r, r1, h),
reachable(h[r].nxt, (h[r].nxt ' + x0).last, h), r ∈ h[r1 := ce], (h[r].nxt ' + x0).last ∈ h[r1 := ce], r1 ∈ h, ce.nxt ∈ h,
¬ reachable(r, (h[r].nxt ' + x0).last, h), ¬ reachable(r, ce.nxt, h)
⊦ |
User applied rule apply rewrite lemma
And obtained the following new goals
- Proof step 66:
⊦ reachable(h[r].nxt, r0, h) ∧ r ≠ r0 ∧ r ≠ null ∧ r ∈ h → (reachable(r, r0, h) ↔ true)
Rule argument
spec: <toplevel>, name:fromnext-reachable-rev,
seq:⊦ reachable(h[r].nxt, r0, h) ∧ r ≠ r0 ∧ r ≠ null ∧ r ∈ h
→ (reachable(r, r0, h) ↔ true),
subst:[h, r0, r] → [h, (h[r].nxt ' + x0).last, r], <all paths>
Additional information
Used simplifier rules:
reach-alloc: ⊦ reachable(r, r1, h) → r1 ∈ h;
self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h;
⊦ a ∈ st[b := d] ↔ a = b ∨ a ∈ st; (ws)
Used terms: h, (h[r].nxt ' + x0).last, r
Proof step 66 from proof add-preserves-reachable-rev (previous step)
(back to tree)
| ⊦ reachable(h[r].nxt, r0, h) ∧ r ≠ r0 ∧ r ≠ null ∧ r ∈ h → (reachable(r, r0, h) ↔ true) |
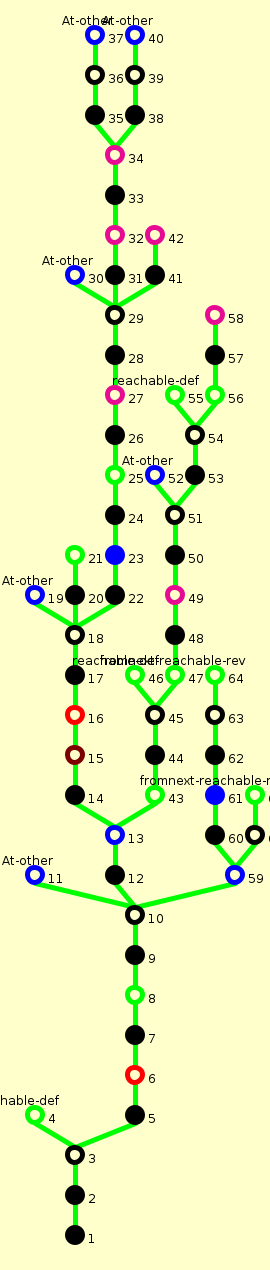
Proof Tree for add-preserves-reachable-rev
(View conclusion)
The following image shows the proof tree of sequent calculus. The
proved goal is at the bottom. You can click on the nodes to view
additional rules. See here for details on colors in a proof
tree.