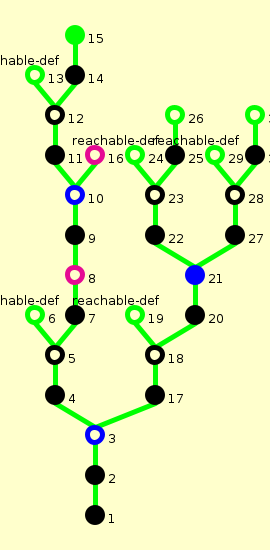
Proof Tree for frommodified (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ r ≠ null ∧ ce.nxt ≠ r → (reachable(r, r0, h[r := ce]) ↔ r = r0 ∨ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])) |
ce.nxt ≠ r, ¬(reachable(r, r0, h[r := ce]) ↔ r = r0 ∨ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])), r ≠ null ⊦
| ce.nxt ≠ r, ¬(reachable(r, r0, h[r := ce]) ↔ r = r0 ∨ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])), r ≠ null ⊦ |
ce.nxt ≠ r, ¬(reachable(r, r0, h[r := ce]) ↔ r = r0 ∨ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])), r ≠ null ⊦
| ce.nxt ≠ r, ¬(reachable(r, r0, h[r := ce]) ↔ r = r0 ∨ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])), r ≠ null ⊦ |
ce.nxt ≠ r, r ≠ r0, r ≠ null, reachable(r, r0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])
ce.nxt ≠ r, r ≠ null, ¬ reachable(r, r0, h[r := ce]), r = r0 ∨ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce]) ⊦
| ce.nxt ≠ r, r ≠ r0, r ≠ null, reachable(r, r0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce]) |
ce.nxt ≠ r, r ≠ r0, r ≠ null, reachable(r, r0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])
| ce.nxt ≠ r, r ≠ r0, r ≠ null, reachable(r, r0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce]) |
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
ce.nxt ≠ r, r ≠ r0, r ≠ null, ∃ x. path(r ' + x, h[r := ce]) ∧ (r ' + x).last = r0 ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce])
Used terms: h[r := ce], r0, r
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
| ce.nxt ≠ r, r ≠ r0, r ≠ null, ∃ x. path(r ' + x, h[r := ce]) ∧ (r ' + x).last = r0 ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce]) |
ce.nxt ≠ r, r ≠ (r ' + x).last, r ≠ null, path(r ' + x, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (r ' + x).last, h[r := ce])
| ce.nxt ≠ r, r ≠ (r ' + x).last, r ≠ null, path(r ' + x, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (r ' + x).last, h[r := ce]) |
x = r0 + x0, ce.nxt ≠ r, r ≠ (r ' + x).last, r ≠ null, path(r ' + x, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (r ' + x).last, h[r := ce])
Used simplifier rules: list('a) freely generated by [], +;; ⊦ x + [] = x; (s) a: ⊦ (x + y) + z = x + y + z; from specification polylist ⊦ a '.last = a; (s)
| x = r0 + x0, ce.nxt ≠ r, r ≠ (r ' + x).last, r ≠ null, path(r ' + x, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (r ' + x).last, h[r := ce]) |
ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce])
Used simplifier rules: path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h); a: ⊦ (x + y) + z = x + y + z; from specification polylist ⊦ (b ' + a ' + x).last = (a ' + x).last; (s) ⊦ a + x = a ' + x; (s) ⊦ (st[a := d])[a] = d; (s) ⊦ a ∈ st[a := d]; (s)
| ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce]) |
ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce])
ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce]), ce.nxt ≠ null ∧ ce.nxt ∈ h
Used formulas: ce.nxt ≠ null ∧ ce.nxt ∈ h
| ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce]) |
ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h, ¬ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce]) ⊦
| ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h, ¬ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce]) ⊦ |
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h, ∀ x. ¬(path(ce.nxt ' + x, h[r := ce]) ∧ (ce.nxt ' + x).last = (ce.nxt ' + x0).last) ⊦
Used terms: h[r := ce], (ce.nxt ' + x0).last, ce.nxt
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
| ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h, ∀ x. ¬(path(ce.nxt ' + x, h[r := ce]) ∧ (ce.nxt ' + x).last = (ce.nxt ' + x0).last) ⊦ |
ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h, ∀ x. ¬ path(ce.nxt ' + x, h[r := ce]) ∨ (ce.nxt ' + x).last ≠ (ce.nxt ' + x0).last ⊦
| ce.nxt ≠ null, ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]), ce.nxt ∈ h, ∀ x. ¬ path(ce.nxt ' + x, h[r := ce]) ∨ (ce.nxt ' + x).last ≠ (ce.nxt ' + x0).last ⊦ |
Used terms: x0
| ce.nxt ≠ r, r ≠ (ce.nxt ' + x0).last, r ≠ null, path(ce.nxt ' + x0, h[r := ce]) ⊦ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, (ce.nxt ' + x0).last, h[r := ce]), ce.nxt ≠ null ∧ ce.nxt ∈ h |
Used simplifier rules: path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null; path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h); list('a) freely generated by [], +;; ⊦ a ≠ b → (a ∈ st[b := d] ↔ a ∈ st); (s) ⊦ a ≠ b → (st[b := d])[a] = st[a]; (s) ⊦ a + x = a ' + x; (s) ⊦ (b ' + a ' + x).last = (a ' + x).last; (s) a: ⊦ (x + y) + z = x + y + z; from specification polylist ⊦ x + [] = x; (s) ⊦ a '.last = a; (s)
| ce.nxt ≠ r, r ≠ null, ¬ reachable(r, r0, h[r := ce]), r = r0 ∨ ce.nxt ≠ null ∧ ce.nxt ∈ h ∧ reachable(ce.nxt, r0, h[r := ce]) ⊦ |
ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ r0, reachable(ce.nxt, r0, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, r0, h[r := ce]) ⊦
Used simplifier rules: self-reachable: ⊦ reachable(r, r, h) ↔ r ≠ null ∧ r ∈ h; ⊦ a ∈ st[a := d]; (s)
| ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ r0, reachable(ce.nxt, r0, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, r0, h[r := ce]) ⊦ |
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ r0, ce.nxt ∈ h, ¬ reachable(r, r0, h[r := ce]), ∃ x. path(ce.nxt ' + x, h[r := ce]) ∧ (ce.nxt ' + x).last = r0 ⊦
Used terms: h[r := ce], r0, ce.nxt
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
| ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ r0, ce.nxt ∈ h, ¬ reachable(r, r0, h[r := ce]), ∃ x. path(ce.nxt ' + x, h[r := ce]) ∧ (ce.nxt ' + x).last = r0 ⊦ |
ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ (ce.nxt ' + x).last, path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, (ce.nxt ' + x).last, h[r := ce]) ⊦
| ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ (ce.nxt ' + x).last, path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, (ce.nxt ' + x).last, h[r := ce]) ⊦ |
x = [], ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ (ce.nxt ' + x).last, path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, (ce.nxt ' + x).last, h[r := ce]) ⊦
ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ (ce.nxt ' + x).last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, (ce.nxt ' + x).last, h[r := ce]) ⊦
Used formulas: x = []
| x = [], ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ (ce.nxt ' + x).last, path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, (ce.nxt ' + x).last, h[r := ce]) ⊦ |
ce.nxt ≠ null, r ≠ null, r ≠ ce.nxt, ce.nxt ∈ h, ¬ reachable(r, ce.nxt, h[r := ce]) ⊦
Used simplifier rules: path-one: ⊦ path(r ', h) ↔ r ∈ h ∧ r ≠ null; ⊦ a '.last = a; (s) a: ⊦ (x + y) + z = x + y + z; from specification polylist ⊦ x + [] = x; (s) ⊦ a ≠ b → (a ∈ st[b := d] ↔ a ∈ st); (s)
| ce.nxt ≠ null, r ≠ null, r ≠ ce.nxt, ce.nxt ∈ h, ¬ reachable(r, ce.nxt, h[r := ce]) ⊦ |
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
ce.nxt ≠ null, r ≠ null, r ≠ ce.nxt, ce.nxt ∈ h, ∀ x. ¬(path(r ' + x, h[r := ce]) ∧ (r ' + x).last = ce.nxt) ⊦
Used terms: h[r := ce], ce.nxt, r
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
| ce.nxt ≠ null, r ≠ null, r ≠ ce.nxt, ce.nxt ∈ h, ∀ x. ¬(path(r ' + x, h[r := ce]) ∧ (r ' + x).last = ce.nxt) ⊦ |
ce.nxt ≠ null, r ≠ null, r ≠ ce.nxt, ce.nxt ∈ h, ∀ x. ¬ path(r ' + x, h[r := ce]) ∨ (r ' + x).last ≠ ce.nxt ⊦
| ce.nxt ≠ null, r ≠ null, r ≠ ce.nxt, ce.nxt ∈ h, ∀ x. ¬ path(r ' + x, h[r := ce]) ∨ (r ' + x).last ≠ ce.nxt ⊦ |
Used simplifier rules: path-two: ⊦ path(r ' + r0 ', h) ↔ r ∈ h ∧ r0 ∈ h ∧ r ≠ null ∧ r0 ≠ null ∧ h[r].nxt = r0; ⊦ a ∈ st[a := d]; (s) ⊦ a ≠ b → (a ∈ st[b := d] ↔ a ∈ st); (s) ⊦ (st[a := d])[a] = d; (s) ⊦ (x + a ').last = a; (s) a: ⊦ (x + y) + z = x + y + z; from specification polylist Used terms: ce.nxt '
| ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ (ce.nxt ' + x).last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, (ce.nxt ' + x).last, h[r := ce]) ⊦ |
ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ x.last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, x.last, h[r := ce]) ⊦
Used simplifier rules: a: ⊦ (x + y) + z = x + y + z; from specification polylist ⊦ x ≠ [] → (a ' + x).last = x.last; (s)
| ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ x.last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ¬ reachable(r, x.last, h[r := ce]) ⊦ |
⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0)
ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ x.last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ∀ x0. ¬(path(r ' + x0, h[r := ce]) ∧ (r ' + x0).last = x.last) ⊦
Used terms: h[r := ce], x.last, r
| ⊦ reachable(r, r0, h) ↔ (∃ x. path(r ' + x, h) ∧ (r ' + x).last = r0) |
| ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ x.last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ∀ x0. ¬(path(r ' + x0, h[r := ce]) ∧ (r ' + x0).last = x.last) ⊦ |
ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ x.last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ∀ x0. ¬ path(r ' + x0, h[r := ce]) ∨ (r ' + x0).last ≠ x.last ⊦
| ce.nxt ≠ r, ce.nxt ≠ null, r ≠ null, r ≠ x.last, x ≠ [], path(ce.nxt ' + x, h[r := ce]), ce.nxt ∈ h, ∀ x0. ¬ path(r ' + x0, h[r := ce]) ∨ (r ' + x0).last ≠ x.last ⊦ |
Used simplifier rules: path-cons: ⊦ path(r ' + r0 ' + x, h) ↔ r ∈ h ∧ r ≠ null ∧ h[r].nxt = r0 ∧ path(r0 ' + x, h); ⊦ a ∈ st[a := d]; (s) ⊦ (st[a := d])[a] = d; (s) ⊦ a + x = a ' + x; (s) ⊦ y ≠ [] → (a ' + x + y).last = y.last; (s) a: ⊦ (x + y) + z = x + y + z; from specification polylist Used terms: ce.nxt + x
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.