Proof Tree for merge-owned (View conclusion)
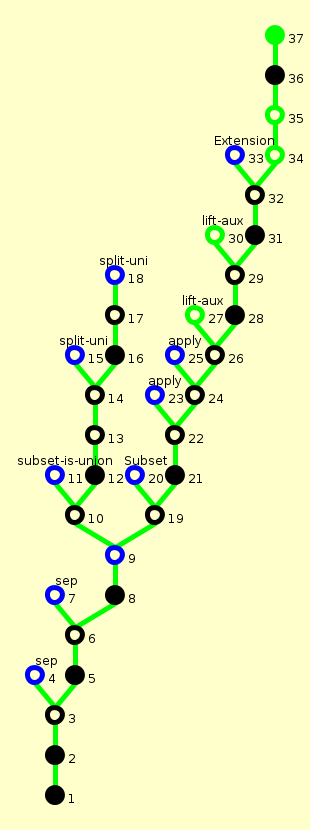
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ (a[hP] * hR)[rs, f, g] ∧ (a0[hP0] * hR0)[rs, f, g] ∧ a0 ≠ a → (a[hP] * a0[hP0] * true)[rs, f, g] |
a0 ≠ a, (a[hP] * hR)[rs, f, g], (a0[hP0] * hR0)[rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs, f, g] ⊦
| a0 ≠ a, (a[hP] * hR)[rs, f, g], (a0[hP0] * hR0)[rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs, f, g] ⊦ |
a0 ≠ a, (a0[hP0] * hR0)[rs, f, g], (a[hP] * hR)[rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs, f, g] ⊦
| a0 ≠ a, (a0[hP0] * hR0)[rs, f, g], (a[hP] * hR)[rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs, f, g] ⊦ |
⊦ (hR0 * hR1)[rs, f, g] ↔ (∃ rs0, rs1. rs0 ∪ rs1 = rs ∧ rs0 ∩ rs1 = ∅ ∧ hR0[rs0, f, g] ∧ hR1[rs1, f, g])
a0 ≠ a, (a0[hP0] * hR0)[rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs, f, g], ∃ rs0, rs1. rs0 ∪ rs1 = rs ∧ rs0 ∩ rs1 = ∅ ∧ a[hP][rs0, f, g] ∧ hR[rs1, f, g] ⊦
Used terms: rs, hR, g, a[hP], f
| ⊦ (hR0 * hR1)[rs, f, g] ↔ (∃ rs0, rs1. rs0 ∪ rs1 = rs ∧ rs0 ∩ rs1 = ∅ ∧ hR0[rs0, f, g] ∧ hR1[rs1, f, g]) |
| a0 ≠ a, (a0[hP0] * hR0)[rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs, f, g], ∃ rs0, rs1. rs0 ∪ rs1 = rs ∧ rs0 ∩ rs1 = ∅ ∧ a[hP][rs0, f, g] ∧ hR[rs1, f, g] ⊦ |
rs0 ∩ rs1 = ∅, a0 ≠ a, a[hP][rs0, f, g], hR[rs1, f, g], (a0[hP0] * hR0)[rs0 ∪ rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g] ⊦
| rs0 ∩ rs1 = ∅, a0 ≠ a, a[hP][rs0, f, g], hR[rs1, f, g], (a0[hP0] * hR0)[rs0 ∪ rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g] ⊦ |
⊦ (hR0 * hR1)[rs, f, g] ↔ (∃ rs0, rs1. rs0 ∪ rs1 = rs ∧ rs0 ∩ rs1 = ∅ ∧ hR0[rs0, f, g] ∧ hR1[rs1, f, g])
rs0 ∩ rs1 = ∅, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ∃ rs2, rs3. rs2 ∪ rs3 = rs0 ∪ rs1 ∧ rs2 ∩ rs3 = ∅ ∧ a0[hP0][rs2, f, g] ∧ hR0[rs3, f, g] ⊦
Used terms: rs0 ∪ rs1, hR0, g, a0[hP0], f
| ⊦ (hR0 * hR1)[rs, f, g] ↔ (∃ rs0, rs1. rs0 ∪ rs1 = rs ∧ rs0 ∩ rs1 = ∅ ∧ hR0[rs0, f, g] ∧ hR1[rs1, f, g]) |
| rs0 ∩ rs1 = ∅, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ∃ rs2, rs3. rs2 ∪ rs3 = rs0 ∪ rs1 ∧ rs2 ∩ rs3 = ∅ ∧ a0[hP0][rs2, f, g] ∧ hR0[rs3, f, g] ⊦ |
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g] ⊦
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g] ⊦ |
rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], rs2 ⊆ rs1, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g] ⊦
rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ rs2 ⊆ rs1 ⊦
Used formulas: rs2 ⊆ rs1
| rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], rs2 ⊆ rs1, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g] ⊦ |
⊦ s ⊆ s0 ↔ (∃ s1. s ∪ s1 = s0 ∧ s ∩ s1 = ∅)
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ∃ s1. rs2 ∪ s1 = rs1 ∧ rs2 ∩ s1 = ∅ ⊦
Used terms: rs1, rs2
| ⊦ s ⊆ s0 ↔ (∃ s1. s ∪ s1 = s0 ∧ s ∩ s1 = ∅) |
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ∃ s1. rs2 ∪ s1 = rs1 ∧ rs2 ∩ s1 = ∅ ⊦ |
rs2 ∩ rs3 = ∅, rs2 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs0 ∩ rs = ∅, rs2 ∪ rs3 = rs0 ∪ rs2 ∪ rs, a0 ≠ a, hR[rs2 ∪ rs, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], ¬ (a[hP] * a0[hP0] * true)[rs2 ∪ rs3, f, g] ⊦
Used simplifier rules: int-c: ⊦ s ∩ s0 = s0 ∩ s; from specification set-union[refset] int-a: ⊦ (s ∩ s0) ∩ s1 = s ∩ s0 ∩ s1; from specification set-union[refset] unc: ⊦ s ∪ s0 = s0 ∪ s; from specification set-union[refset] una: ⊦ (s ∪ s0) ∪ s1 = s ∪ s0 ∪ s1; from specification set-union[refset] ⊦ s ∩ (s0 ∪ s1) = ∅ ↔ s ∩ s0 = ∅ ∧ s ∩ s1 = ∅; (ws)
| rs2 ∩ rs3 = ∅, rs2 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs0 ∩ rs = ∅, rs2 ∪ rs3 = rs0 ∪ rs2 ∪ rs, a0 ≠ a, hR[rs2 ∪ rs, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], ¬ (a[hP] * a0[hP0] * true)[rs2 ∪ rs3, f, g] ⊦ |
rs0 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs2 ∩ rs = ∅, rs2 ∩ rs3 = ∅, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs2 ∪ rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs2 ∪ rs, f, g] ⊦
| rs0 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs2 ∩ rs = ∅, rs2 ∩ rs3 = ∅, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs2 ∪ rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs2 ∪ rs, f, g] ⊦ |
⊦ hR0[rs0, f, g] ∧ hR1[rs1, f, g] ∧ rs0 ∩ rs1 = ∅ → (hR0 * hR1)[rs0 ∪ rs1, f, g]
rs2 ∩ rs3 = ∅, rs2 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs0 ∩ rs = ∅, a0 ≠ a, hR[rs2 ∪ rs, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs2 ∪ rs, f, g] ⊦ a[hP][rs0, f, g] ∧ (a0[hP0] * true)[rs2 ∪ rs, f, g] ∧ rs0 ∩ (rs2 ∪ rs) = ∅
Used terms: rs0, a0[hP0] * true, g, a[hP], f, rs2 ∪ rs
| ⊦ hR0[rs0, f, g] ∧ hR1[rs1, f, g] ∧ rs0 ∩ rs1 = ∅ → (hR0 * hR1)[rs0 ∪ rs1, f, g] |
| rs2 ∩ rs3 = ∅, rs2 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs0 ∩ rs = ∅, a0 ≠ a, hR[rs2 ∪ rs, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs2 ∪ rs, f, g] ⊦ a[hP][rs0, f, g] ∧ (a0[hP0] * true)[rs2 ∪ rs, f, g] ∧ rs0 ∩ (rs2 ∪ rs) = ∅ |
rs0 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs2 ∩ rs = ∅, rs2 ∩ rs3 = ∅, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs2 ∪ rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs2 ∪ rs, f, g], ¬ (a0[hP0] * true)[rs2 ∪ rs, f, g] ⊦
Used simplifier rules: int-c: ⊦ s ∩ s0 = s0 ∩ s; from specification set-union[refset] int-a: ⊦ (s ∩ s0) ∩ s1 = s ∩ s0 ∩ s1; from specification set-union[refset] unc: ⊦ s ∪ s0 = s0 ∪ s; from specification set-union[refset] una: ⊦ (s ∪ s0) ∪ s1 = s ∪ s0 ∪ s1; from specification set-union[refset] ⊦ s ∩ (s0 ∪ s1) = ∅ ↔ s ∩ s0 = ∅ ∧ s ∩ s1 = ∅; (ws)
| rs0 ∩ rs = ∅, rs0 ∩ rs2 = ∅, rs2 ∩ rs = ∅, rs2 ∩ rs3 = ∅, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs2 ∪ rs, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs2 ∪ rs, f, g], ¬ (a0[hP0] * true)[rs2 ∪ rs, f, g] ⊦ |
⊦ hR0[rs0, f, g] ∧ hR1[rs1, f, g] ∧ rs0 ∩ rs1 = ∅ → (hR0 * hR1)[rs0 ∪ rs1, f, g]
Used simplifier rules: ⊦ true[rs, f, g]; (s) Used terms: rs2, true, g, a0[hP0], f, rs
| ⊦ hR0[rs0, f, g] ∧ hR1[rs1, f, g] ∧ rs0 ∩ rs1 = ∅ → (hR0 * hR1)[rs0 ∪ rs1, f, g] |
| rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ rs2 ⊆ rs1 ⊦ |
⊦ s1 ⊆ s2 ↔ (∀ a. a ∈ s1 → a ∈ s2)
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ∃ r. ¬(r ∈ rs2 → r ∈ rs1) ⊦
Used terms: rs1, rs2
| ⊦ s1 ⊆ s2 ↔ (∀ a. a ∈ s1 → a ∈ s2) |
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP][rs0, f, g], hR[rs1, f, g], ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ∃ r. ¬(r ∈ rs2 → r ∈ rs1) ⊦ |
rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1 ⊦
| rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP][rs0, f, g], hR0[rs3, f, g], a0[hP0][rs2, f, g], r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1 ⊦ |
⊦ hR[rs, f, g] ↔ hR(mk(rs, f, g))
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP](mk(rs0, f, g)), hR[rs1, f, g], r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1 ⊦
Used terms: g, f, rs0, a[hP]
| ⊦ hR[rs, f, g] ↔ hR(mk(rs, f, g)) |
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, a0[hP0][rs2, f, g], hR0[rs3, f, g], a[hP](mk(rs0, f, g)), hR[rs1, f, g], r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1 ⊦ |
⊦ hR[rs, f, g] ↔ hR(mk(rs, f, g))
rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP](mk(rs0, f, g)), hR0[rs3, f, g], a0[hP0](mk(rs2, f, g)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1 ⊦
Used terms: g, f, rs2, a0[hP0]
| ⊦ hR[rs, f, g] ↔ hR(mk(rs, f, g)) |
| rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP](mk(rs0, f, g)), hR0[rs3, f, g], a0[hP0](mk(rs2, f, g)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1 ⊦ |
⊦ a[hP](mk(rs, f, g)) ↔ hP(mk(rs, f)) ∧ (∀ r. r ∈ rs → g(r) = a)
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR0[rs3, f, g], a[hP](mk(rs0, f, g)), hR[rs1, f, g], hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0 ⊦
Used terms: a0, hP0, rs2, g, f
| ⊦ a[hP](mk(rs, f, g)) ↔ hP(mk(rs, f)) ∧ (∀ r. r ∈ rs → g(r) = a) |
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR0[rs3, f, g], a[hP](mk(rs0, f, g)), hR[rs1, f, g], hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0 ⊦ |
rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP](mk(rs0, f, g)), hR0[rs3, f, g], hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0 ⊦
| rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], a[hP](mk(rs0, f, g)), hR0[rs3, f, g], hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0 ⊦ |
⊦ a[hP](mk(rs, f, g)) ↔ hP(mk(rs, f)) ∧ (∀ r. r ∈ rs → g(r) = a)
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs0 → g(r) = a ⊦
Used terms: a, hP, rs0, g, f
| ⊦ a[hP](mk(rs, f, g)) ↔ hP(mk(rs, f)) ∧ (∀ r. r ∈ rs → g(r) = a) |
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs0 → g(r) = a ⊦ |
rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], hR0[rs3, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 → g(r) = a0 ⊦
| rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, rs2 ∪ rs3 = rs0 ∪ rs1, a0 ≠ a, hR[rs1, f, g], hR0[rs3, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 → g(r) = a0 ⊦ |
⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2)
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, a0 ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1 ⊦
Used terms: rs0 ∪ rs1, rs2 ∪ rs3
| ⊦ s1 = s2 ↔ (∀ a. a ∈ s1 ↔ a ∈ s2) |
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, a0 ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, ∀ r. r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1 ⊦ |
rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, a0 ≠ a, hR[rs1, f, g], hR0[rs3, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 → g(r) = a0 ⊦
Used terms: r
| rs0 ∩ rs1 = ∅, rs2 ∩ rs3 = ∅, a0 ≠ a, hR[rs1, f, g], hR0[rs3, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 → g(r) = a0 ⊦ |
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, a0 ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, r ∈ rs0 → g(r) = a, r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1 ⊦
Used terms: r
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, a0 ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * a0[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs1, r ∈ rs0 → g(r) = a, r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs2 → g(r) = a0, ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1 ⊦ |
rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, g(r) ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * g(r)[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs0, ¬ r ∈ rs1, ∀ r0. r0 ∈ rs2 → g(r0) = g(r), ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1 ⊦
| rs2 ∩ rs3 = ∅, rs0 ∩ rs1 = ∅, g(r) ≠ a, hR0[rs3, f, g], hR[rs1, f, g], hP(mk(rs0, f)), hP0(mk(rs2, f)), r ∈ rs2, ¬ (a[hP] * g(r)[hP0] * true)[rs0 ∪ rs1, f, g], ¬ r ∈ rs0, ¬ r ∈ rs1, ∀ r0. r0 ∈ rs2 → g(r0) = g(r), ∀ r. r ∈ rs0 → g(r) = a, ∀ r. r ∈ rs2 ∪ rs3 ↔ r ∈ rs0 ∪ rs1 ⊦ |
Used simplifier rules: ⊦ ¬ a ∈ s → (a ∈ s ∪ s0 ↔ a ∈ s0); (s) ⊦ a ∈ s ∪ s0 ↔ ¬(¬ a ∈ s ∧ ¬ a ∈ s0); (ss) una: ⊦ (s ∪ s0) ∪ s1 = s ∪ s0 ∪ s1; from specification set-union[refset] unc: ⊦ s ∪ s0 = s0 ∪ s; from specification set-union[refset] Used terms: r
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.