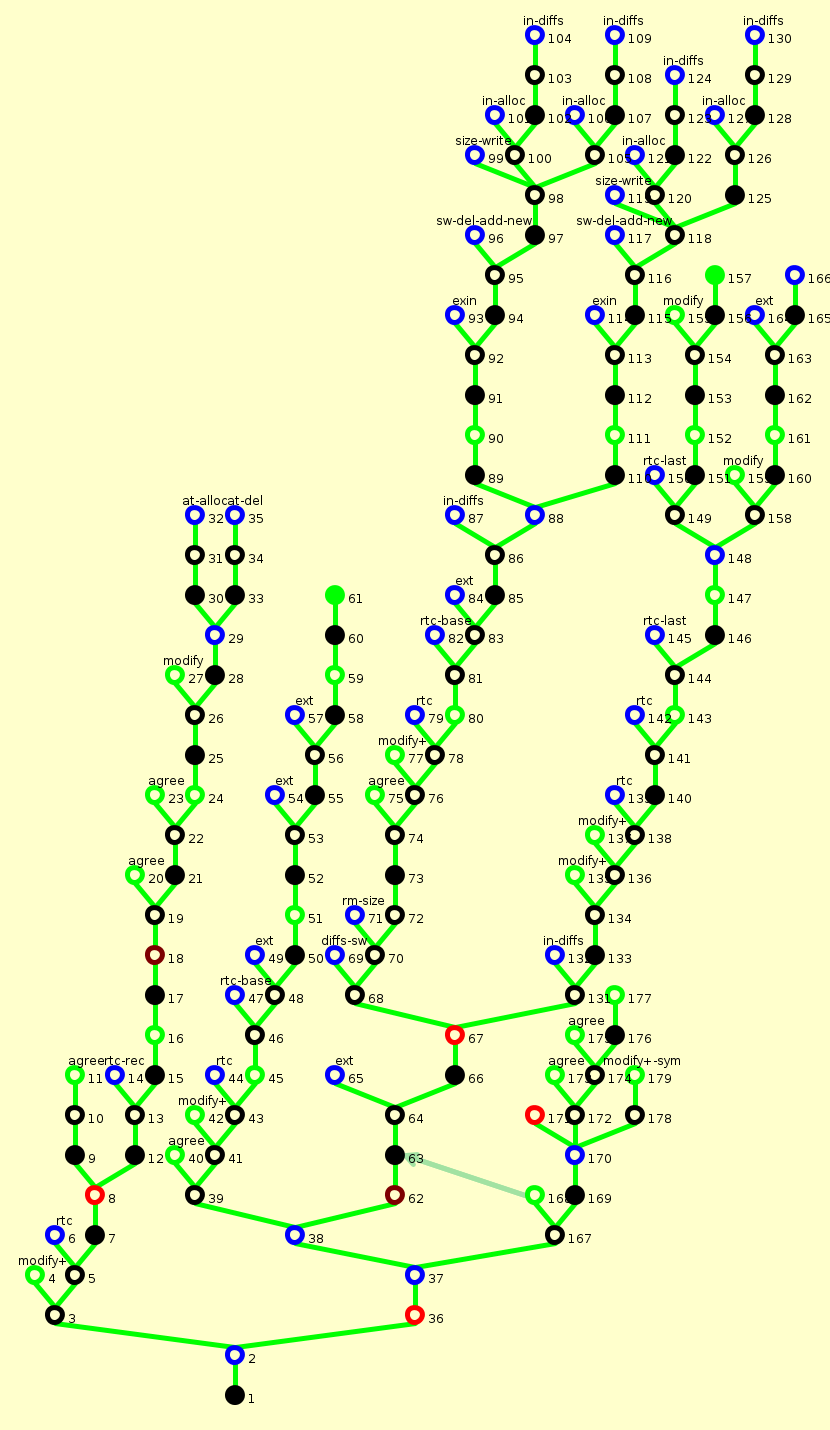
Proof Tree for modify-agree (View conclusion)
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.
| ⊦ modify*(rs)(h0, h1) ↔ ((h0 ≡ h1))(rs) |
¬(modify*(rs)(h0, h1) ↔ ((h0 ≡ h1))(rs)) ⊦
| ¬(modify*(rs)(h0, h1) ↔ ((h0 ≡ h1))(rs)) ⊦ |
modify*(rs)(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦
((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1) ⊦
| modify*(rs)(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦ |
⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1)
modify(rs) ^*(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦
Used terms: h1, h0, rs
| ⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1) |
| modify(rs) ^*(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦ |
⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b))
¬ ((h0 ≡ h1))(rs), ∃ n. rtc(n, modify(rs))(h0, h1) ⊦
Used terms: h1, h0, modify(rs)
| ⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b)) |
| ¬ ((h0 ≡ h1))(rs), ∃ n. rtc(n, modify(rs))(h0, h1) ⊦ |
rtc(n, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦
| rtc(n, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦ |
rtc(0, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦
rtc(n0 +1, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs), ∀ rs, h0, h1. ¬(rtc(n0, modify(rs))(h0, h1) ∧ ¬ ((h0 ≡ h1))(rs)) ⊦
Used simplifier rules: nat freely generated by 0, +1;;
| rtc(0, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs) ⊦ |
¬ ((h1 ≡ h1))(rs) ⊦
Used simplifier rules: ⊦ rtc(0, pelem)(a, b) ↔ a = b; (s)
| ¬ ((h1 ≡ h1))(rs) ⊦ |
⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
Used terms: rs, h1, h1
| ⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| rtc(n0 +1, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs), ∀ rs, h0, h1. ¬(rtc(n0, modify(rs))(h0, h1) ∧ ¬ ((h0 ≡ h1))(rs)) ⊦ |
rtc(n0 + 1, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs), ∀ rs0, h, h2. ¬ rtc(n0, modify(rs0))(h, h2) ∨ ((h ≡ h2))(rs0) ⊦
Used simplifier rules: ⊦ m +1 = m + 1; (s)
| rtc(n0 + 1, modify(rs))(h0, h1), ¬ ((h0 ≡ h1))(rs), ∀ rs0, h, h2. ¬ rtc(n0, modify(rs0))(h, h2) ∨ ((h ≡ h2))(rs0) ⊦ |
⊦ rtc(n + 1, pelem)(a, b) ↔ (∃ c. pelem(a, c) ∧ rtc(n, pelem)(c, b))
¬ ((h0 ≡ h1))(rs), ∀ rs0, h, h2. ¬ rtc(n0, modify(rs0))(h, h2) ∨ ((h ≡ h2))(rs0), ∃ c. modify(rs)(h0, c) ∧ rtc(n0, modify(rs))(c, h1) ⊦
Used terms: h1, h0, modify(rs), n0
| ⊦ rtc(n + 1, pelem)(a, b) ↔ (∃ c. pelem(a, c) ∧ rtc(n, pelem)(c, b)) |
| ¬ ((h0 ≡ h1))(rs), ∀ rs0, h, h2. ¬ rtc(n0, modify(rs0))(h, h2) ∨ ((h ≡ h2))(rs0), ∃ c. modify(rs)(h0, c) ∧ rtc(n0, modify(rs))(c, h1) ⊦ |
modify(rs)(h0, h), rtc(n0, modify(rs))(h, h1), ¬ ((h0 ≡ h1))(rs), ∀ rs0, h, h2. ¬ rtc(n0, modify(rs0))(h, h2) ∨ ((h ≡ h2))(rs0) ⊦
| modify(rs)(h0, h), rtc(n0, modify(rs))(h, h1), ¬ ((h0 ≡ h1))(rs), ∀ rs0, h, h2. ¬ rtc(n0, modify(rs0))(h, h2) ∨ ((h ≡ h2))(rs0) ⊦ |
modify(rs)(h0, h), rtc(n0, modify(rs))(h, h1), ¬ ((h0 ≡ h1))(rs), ¬ rtc(n0, modify(rs))(h, h1) ∨ ((h ≡ h1))(rs) ⊦
Used terms: rs, h, h1
| modify(rs)(h0, h), rtc(n0, modify(rs))(h, h1), ¬ ((h0 ≡ h1))(rs), ¬ rtc(n0, modify(rs))(h, h1) ∨ ((h ≡ h1))(rs) ⊦ |
modify(rs)(h0, h), rtc(n0, modify(rs))(h, h1), ((h ≡ h1))(rs), ¬ ((h0 ≡ h1))(rs) ⊦
| modify(rs)(h0, h), rtc(n0, modify(rs))(h, h1), ((h ≡ h1))(rs), ¬ ((h0 ≡ h1))(rs) ⊦ |
modify(rs)(h0, h), ((h ≡ h1))(rs), ¬ ((h0 ≡ h1))(rs) ⊦
| modify(rs)(h0, h), ((h ≡ h1))(rs), ¬ ((h0 ≡ h1))(rs) ⊦ |
⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
modify(rs)(h0, h), ((h ≡ h1))(rs), ∃ r. ¬(r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) ⊦
Used terms: rs, h1, h0
| ⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| modify(rs)(h0, h), ((h ≡ h1))(rs), ∃ r. ¬(r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) ⊦ |
modify(rs)(h0, h), r ∈ rs, ((h ≡ h1))(rs) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
| modify(rs)(h0, h), r ∈ rs, ((h ≡ h1))(rs) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
modify(rs)(h0, h), r ∈ rs, ∀ r. r ∈ rs → (r ∈ h ↔ r ∈ h1) ∧ (r ∈ h → h[r] = h1[r]) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used terms: rs, h1, h
| ⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| modify(rs)(h0, h), r ∈ rs, ∀ r. r ∈ rs → (r ∈ h ↔ r ∈ h1) ∧ (r ∈ h → h[r] = h1[r]) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
modify(rs)(h0, h), r ∈ rs, r ∈ rs → (r ∈ h ↔ r ∈ h1) ∧ (r ∈ h → h[r] = h1[r]) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used terms: r
| modify(rs)(h0, h), r ∈ rs, r ∈ rs → (r ∈ h ↔ r ∈ h1) ∧ (r ∈ h → h[r] = h1[r]) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
r ∈ h ↔ r ∈ h1, modify(rs)(h0, h), r ∈ rs, r ∈ h1 → h[r] = h1[r] ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
| r ∈ h ↔ r ∈ h1, modify(rs)(h0, h), r ∈ rs, r ∈ h1 → h[r] = h1[r] ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
⊦ modify(rs)(h0, h1) ↔ (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h1 = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0 -- r)
r ∈ h ↔ r ∈ h1, r ∈ rs, r ∈ h1 → h[r] = h1[r], (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h = h0 -- r) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used terms: h, h0, rs
| ⊦ modify(rs)(h0, h1) ↔ (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h1 = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0 -- r) |
| r ∈ h ↔ r ∈ h1, r ∈ rs, r ∈ h1 → h[r] = h1[r], (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h = h0 -- r) ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
r ∈ h ↔ r ∈ h1, r ∈ rs, r ∈ h1 → h[r] = h1[r], ¬ r0 ∈ rs ∧ r0 ≠ null ∧ ¬ r0 ∈ h0 ∧ h = h0 ++ r0 ∨ ¬ r1 ∈ rs ∧ r1 ∈ h0 ∧ h = h0[r1, o] ∨ ¬ r2 ∈ rs ∧ r2 ∈ h0 ∧ h = h0 -- r2 ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
| r ∈ h ↔ r ∈ h1, r ∈ rs, r ∈ h1 → h[r] = h1[r], ¬ r0 ∈ rs ∧ r0 ≠ null ∧ ¬ r0 ∈ h0 ∧ h = h0 ++ r0 ∨ ¬ r1 ∈ rs ∧ r1 ∈ h0 ∧ h = h0[r1, o] ∨ ¬ r2 ∈ rs ∧ r2 ∈ h0 ∧ h = h0 -- r2 ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
r ∈ h ↔ r ∈ h1, h = h0 ++ r0, r0 ≠ null, r ∈ rs, ¬ r0 ∈ h0, ¬ r0 ∈ rs, r ∈ h1 → h[r] = h1[r] ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
r ∈ h ↔ r ∈ h1, h = h0 -- r2, r ∈ rs, r2 ∈ h0, ¬ r2 ∈ rs, r ∈ h1 → h[r] = h1[r] ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used simplifier rules: ⊦ r ∈ h[r0, o] ↔ r ∈ h; (s) ⊦ h[r0, o][r] = (r = r0 ∧ r0 ∈ h ⊃ o;h[r]); (s)
| r ∈ h ↔ r ∈ h1, h = h0 ++ r0, r0 ≠ null, r ∈ rs, ¬ r0 ∈ h0, ¬ r0 ∈ rs, r ∈ h1 → h[r] = h1[r] ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
(h0 ++ r0)[r] = h1[r], h0[r] ≠ h1[r], r0 ≠ null, r ∈ rs, r ∈ h0, r ∈ h1, ¬ r0 ∈ h0, ¬ r0 ∈ rs ⊦
Used simplifier rules: r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h; (s)
| (h0 ++ r0)[r] = h1[r], h0[r] ≠ h1[r], r0 ≠ null, r ∈ rs, r ∈ h0, r ∈ h1, ¬ r0 ∈ h0, ¬ r0 ∈ rs ⊦ |
r ∈ h, r0 ≠ null, ¬ r0 ∈ h ⊦ r ≠ r0 → (h ++ r0)[r] = h[r]
Used terms: r, r0, h0
| r ∈ h, r0 ≠ null, ¬ r0 ∈ h ⊦ r ≠ r0 → (h ++ r0)[r] = h[r] |
| r ∈ h ↔ r ∈ h1, h = h0 -- r2, r ∈ rs, r2 ∈ h0, ¬ r2 ∈ rs, r ∈ h1 → h[r] = h1[r] ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
(h0 -- r2)[r] = h1[r], h0[r] ≠ h1[r], r2 ∈ h0, r ∈ rs, r ∈ h0, r ∈ h1, ¬ r2 ∈ rs ⊦
Used simplifier rules: ⊦ r ∈ h -- r0 ↔ r ≠ r0 ∧ r ∈ h; (s)
| (h0 -- r2)[r] = h1[r], h0[r] ≠ h1[r], r2 ∈ h0, r ∈ rs, r ∈ h0, r ∈ h1, ¬ r2 ∈ rs ⊦ |
r ∈ h ⊦ r ≠ r0 → (h -- r0)[r] = h[r]
Used terms: r, r2, h0
| r ∈ h ⊦ r ≠ r0 → (h -- r0)[r] = h[r] |
| ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1) ⊦ |
((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: <; (wellfounded) Used terms: #(h0 \ rs) + #(h1 \ rs)
| ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h0 \ rs = ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used formulas: h0 \ rs = ∅
| h0 \ rs = ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h0 \ rs = ∅, h1 \ rs = ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
h0 \ rs = ∅, h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used formulas: h1 \ rs = ∅
| h0 \ rs = ∅, h1 \ rs = ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
h1 \ rs = ∅, h0 \ rs = ∅, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h0, h1, rs
| ⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| h1 \ rs = ∅, h0 \ rs = ∅, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1)
h0 \ rs = ∅, h1 \ rs = ∅, ¬ modify(rs) ^*(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: rs, h0, h1
| ⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1) |
| h0 \ rs = ∅, h1 \ rs = ∅, ¬ modify(rs) ^*(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b))
h1 \ rs = ∅, h0 \ rs = ∅, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ n. ¬ rtc(n, modify(rs))(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: modify(rs), h0, h1
| ⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b)) |
| h1 \ rs = ∅, h0 \ rs = ∅, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ n. ¬ rtc(n, modify(rs))(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h0 \ rs = ∅, h1 \ rs = ∅, ¬ rtc(0, modify(rs))(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: 0
| h0 \ rs = ∅, h1 \ rs = ∅, ¬ rtc(0, modify(rs))(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ rtc(0, pelem)(a, b) ↔ a = b
h1 \ rs = ∅, h0 \ rs = ∅, h0 ≠ h1, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: modify(rs), h0, h1
| ⊦ rtc(0, pelem)(a, b) ↔ a = b |
| h1 \ rs = ∅, h0 \ rs = ∅, h0 ≠ h1, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
h0 \ rs = ∅, h1 \ rs = ∅, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ r. ¬((r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h0, h1
| ⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| h0 \ rs = ∅, h1 \ rs = ∅, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ r. ¬((r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h1 \ rs = ∅, h0 \ rs = ∅, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
| h1 \ rs = ∅, h0 \ rs = ∅, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
h0 \ rs = ∅, h1 \ rs = ∅, r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used terms: r
| h0 \ rs = ∅, h1 \ rs = ∅, r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
h1 \ rs = ∅, h0 \ rs = ∅, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
| h1 \ rs = ∅, h0 \ rs = ∅, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
h0 \ rs = ∅, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r. (r ∈ h1 \ rs ↔ r ∈ ∅) ∧ (r ∈ h1 \ rs → (h1 \ rs)[r] = ∅[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used terms: h1 \ rs, ∅
| ⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| h0 \ rs = ∅, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r. (r ∈ h1 \ rs ↔ r ∈ ∅) ∧ (r ∈ h1 \ rs → (h1 \ rs)[r] = ∅[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
h0 \ rs = ∅, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used simplifier rules: ⊦ ¬ r ∈ ∅; (s)
| h0 \ rs = ∅, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
¬ r ∈ rs, ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r. (r ∈ h0 \ rs ↔ r ∈ ∅) ∧ (r ∈ h0 \ rs → (h0 \ rs)[r] = ∅[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used terms: h0 \ rs, ∅
| ⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| ¬ r ∈ rs, ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r. (r ∈ h0 \ rs ↔ r ∈ ∅) ∧ (r ∈ h0 \ rs → (h0 \ rs)[r] = ∅[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ r0. ¬ r0 ∈ h0 \ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used simplifier rules: ⊦ ¬ r ∈ ∅; (s)
| ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ r0. ¬ r0 ∈ h0 \ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
¬ r ∈ h0 \ rs, ¬ r ∈ rs, ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])
Used terms: r
| ¬ r ∈ h0 \ rs, ¬ r ∈ rs, ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]) |
r ∈ h1, ¬ r ∈ rs, ¬ r ∈ h0, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs; (ss)
| r ∈ h1, ¬ r ∈ rs, ¬ r ∈ h0, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ r0. ¬ r0 ∈ h1 \ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < # ∅ + # ∅ → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
Used simplifier rules: ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs; (ss) Used terms: r
| h0 \ rs = ∅, h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∃ r. ¬((r ∈ h1 \ rs ↔ r ∈ ∅) ∧ (r ∈ h1 \ rs → (h1 \ rs)[r] = ∅[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h1 \ rs, ∅
| ⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∃ r. ¬((r ∈ h1 \ rs ↔ r ∈ ∅) ∧ (r ∈ h1 \ rs → (h1 \ rs)[r] = ∅[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ ¬ r ∈ ∅; (s)
| r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + #((h1 -- r) \ rs) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ ((h0 ≡ (h1 -- r)))(rs) ∧ ¬ modify*(rs)(h0, h1 -- r)
Used terms: h0, rs, h1 -- r
| r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + #((h1 -- r) \ rs) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ (h -- r) \ rs = (h \ rs) -- r
r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + #((h1 \ rs) -- r) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h1, r, rs
| ⊦ (h -- r) \ rs = (h \ rs) -- r |
| r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + #((h1 \ rs) -- r) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ r ∈ h → #(h -- r) = # h - 1
r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + (#(h1 \ rs) - 1) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h1 \ rs, r
| ⊦ r ∈ h → #(h -- r) = # h - 1 |
| r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + (#(h1 \ rs) - 1) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + (#(h1 \ rs) - 1) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ m + n < m + n0 ↔ n < n0; (s) ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ m = n + 1 → ¬ m ≤ n; (s) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic n ≠ 0 ⊦ m = n - 1 ↔ n = m + 1; (elim) Used terms: #(h1 \ rs), m
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ #(h0 \ rs) + (#(h1 \ rs) - 1) < #(h0 \ rs) + #(h1 \ rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ 0 ≤ m; (s) leprf: ⊦ m ≤ m - 1 → m = 0; (forward) from specification nat c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ m < n ↔ ¬ n ≤ m; (ss) ⊦ m + n < m + n0 ↔ n < n0; (s)
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
#(h1 \ rs) = 0, r ∈ h1 \ rs, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h0, h1, rs
| ⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1)
#(h1 \ rs) = 0, r ∈ h1 \ rs, ¬ modify(rs) ^*(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: rs, h0, h1
| ⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1) |
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ¬ modify(rs) ^*(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b))
#(h1 \ rs) = 0, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ n. ¬ rtc(n, modify(rs))(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: modify(rs), h0, h1
| ⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b)) |
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ n. ¬ rtc(n, modify(rs))(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, r ∈ h1 \ rs, ¬ rtc(0, modify(rs))(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: 0
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ¬ rtc(0, modify(rs))(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ rtc(0, pelem)(a, b) ↔ a = b
#(h1 \ rs) = 0, h0 ≠ h1, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: modify(rs), h0, h1
| ⊦ rtc(0, pelem)(a, b) ↔ a = b |
| #(h1 \ rs) = 0, h0 ≠ h1, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
#(h1 \ rs) = 0, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ r. ¬((r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h0, h1
| ⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ r. ¬((r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0])
| #(h1 \ rs) = 0, r ∈ h1 \ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]) |
⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs
#(h1 \ rs) = 0, r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0])
Used terms: r, h1, rs
| ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs |
| #(h1 \ rs) = 0, r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]) |
#(h1 \ rs) = 0, r0 ∈ h0 ↔ r0 ∈ h1, r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0])
#(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0])
Used formulas: r0 ∈ h0 ↔ r0 ∈ h1
| #(h1 \ rs) = 0, r0 ∈ h0 ↔ r0 ∈ h1, r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]) |
#(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r ∈ h1, r0 ∈ h0, r0 ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| #(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r ∈ h1, r0 ∈ h0, r0 ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r0 ∈ h1, r0 ∈ h0, r ∈ h1, ¬ r ∈ rs, r0 ∈ rs → (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: r0
| #(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r0 ∈ h1, r0 ∈ h0, r ∈ h1, ¬ r ∈ rs, r0 ∈ rs → (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r ∈ h1, r0 ∈ h0, r0 ∈ h1, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| #(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r ∈ h1, r0 ∈ h0, r0 ∈ h1, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ r ≠ null → (r ∈ h ↔ (∃ h0, o. h = (h0 ++ r)[r, o] ∧ ¬ r ∈ h0))
#(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r0 ≠ null, r0 ∈ h0, r ∈ h1, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ h0, o. h1 = (h0 ++ r0)[r0, o] ∧ ¬ r0 ∈ h0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ ¬ null ∈ h; (s) Used terms: r0, h1
| ⊦ r ≠ null → (r ∈ h ↔ (∃ h0, o. h = (h0 ++ r)[r, o] ∧ ¬ r ∈ h0)) |
| #(h1 \ rs) = 0, h0[r0] ≠ h1[r0], r0 ≠ null, r0 ∈ h0, r ∈ h1, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ h0, o. h1 = (h0 ++ r0)[r0, o] ∧ ¬ r0 ∈ h0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#((h ++ r0)[r0, o] \ rs) = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ h[r0, o][r] = (r = r0 ∧ r0 ∈ h ⊃ o;h[r]); (s) r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h; (s) ⊦ r ∈ h → r ≠ null; (s) ⊦ r ∈ h[r0, o] ↔ r ∈ h; (s)
| #((h ++ r0)[r0, o] \ rs) = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
¬ r ∈ h, r ≠ null ⊦ ¬ r ∈ rs → (h ++ r)[r, o] \ rs = ((h \ rs) ++ r)[r, o]
# ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ≠ null, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s) Used terms: h, r0, o, rs
| ¬ r ∈ h, r ≠ null ⊦ ¬ r ∈ rs → (h ++ r)[r, o] \ rs = ((h \ rs) ++ r)[r, o] |
| # ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ≠ null, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
# ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s)
| # ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r ∈ h ⊦ # h[r, o] = # h
# ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
#((h \ rs) ++ r0) = 0, h0[r0] ≠ o, r0 ∈ h0, r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: (h \ rs) ++ r0, r0, o
| r ∈ h ⊦ # h[r, o] = # h |
| # ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h
# ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r0 ≠ null ∧ ¬ r0 ∈ h \ rs
Used terms: r0, h \ rs, r0
| r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h |
| # ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, ¬ r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r0 ≠ null ∧ ¬ r0 ∈ h \ rs |
# ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, r0 ∈ h \ rs, ¬ r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s)
| # ((h \ rs) ++ r0)[r0, o] = 0, h0[r0] ≠ o, r0 ∈ h0, r0 ∈ h \ rs, ¬ r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs
Used terms: r0, h, rs
| ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs |
| #((h \ rs) ++ r0) = 0, h0[r0] ≠ o, r0 ∈ h0, r0 ∈ (h \ rs) ++ r0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h
#((h \ rs) ++ r0) = 0, h0[r0] ≠ o, r0 ∈ (h \ rs) ++ r0, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r0 ≠ null ∧ ¬ r0 ∈ h \ rs
Used simplifier rules: ¬ r ∈ h, r ≠ null ⊦ #(h ++ r) = # h + 1; (s) ⊦ m + n = 0 ↔ m = 0 ∧ n = 0; (ws) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: r0, h \ rs, r0
| r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h |
| #((h \ rs) ++ r0) = 0, h0[r0] ≠ o, r0 ∈ (h \ rs) ++ r0, r0 ∈ h0, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r0 ≠ null ∧ ¬ r0 ∈ h \ rs |
#((h \ rs) ++ r0) = 0, h0[r0] ≠ o, r0 ∈ h0, r0 ∈ (h \ rs) ++ r0, r0 ∈ h \ rs, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s)
| #((h \ rs) ++ r0) = 0, h0[r0] ≠ o, r0 ∈ h0, r0 ∈ (h \ rs) ++ r0, r0 ∈ h \ rs, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r0 ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r0)[r1]), r = r0 ∨ r ∈ h, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs
Used terms: r0, h, rs
| ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs |
| #(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]) |
#(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| #(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, r0 ∈ rs → (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: r0
| #(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, r0 ∈ rs → (r0 ∈ h0 ↔ r0 ∈ h1) ∧ (r0 ∈ h0 → h0[r0] = h1[r0]), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| #(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ∈ h1, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ r ≠ null → (r ∈ h ↔ (∃ h0, o. h = (h0 ++ r)[r, o] ∧ ¬ r ∈ h0))
#(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ≠ null, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ h0, o. h1 = (h0 ++ r)[r, o] ∧ ¬ r ∈ h0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ ¬ null ∈ h; (s) Used terms: r, h1
| ⊦ r ≠ null → (r ∈ h ↔ (∃ h0, o. h = (h0 ++ r)[r, o] ∧ ¬ r ∈ h0)) |
| #(h1 \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 ∈ h1), r ≠ null, ¬ r ∈ rs, ¬ r0 ∈ rs, ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ h0, o. h1 = (h0 ++ r)[r, o] ∧ ¬ r ∈ h0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#((h ++ r)[r, o] \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ h[r0, o][r] = (r = r0 ∧ r0 ∈ h ⊃ o;h[r]); (s) r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h; (s) ⊦ r ∈ h[r0, o] ↔ r ∈ h; (s)
| #((h ++ r)[r, o] \ rs) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
¬ r ∈ h, r ≠ null ⊦ ¬ r ∈ rs → (h ++ r)[r, o] \ rs = ((h \ rs) ++ r)[r, o]
# ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h, r, o, rs
| ¬ r ∈ h, r ≠ null ⊦ ¬ r ∈ rs → (h ++ r)[r, o] \ rs = ((h \ rs) ++ r)[r, o] |
| # ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r ∈ h ⊦ # h[r, o] = # h
# ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
#((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: (h \ rs) ++ r, r, o
| r ∈ h ⊦ # h[r, o] = # h |
| # ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h
# ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r ≠ null ∧ ¬ r ∈ h \ rs
Used terms: r, h \ rs, r
| r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h |
| # ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, ¬ r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r ≠ null ∧ ¬ r ∈ h \ rs |
# ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ h \ rs, ¬ r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s)
| # ((h \ rs) ++ r)[r, o] = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ h \ rs, ¬ r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs
Used terms: r, h, rs
| ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs |
| #((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ≠ null, r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
#((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s)
| #((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h
#((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r ≠ null ∧ ¬ r ∈ h \ rs
Used simplifier rules: ¬ r ∈ h, r ≠ null ⊦ #(h ++ r) = # h + 1; (s) ⊦ m + n = 0 ↔ m = 0 ∧ n = 0; (ws) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: r, h \ rs, r
| r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h |
| #((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ (h \ rs) ++ r, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ r ≠ null ∧ ¬ r ∈ h \ rs |
#((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ (h \ rs) ++ r, r ∈ h \ rs, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s)
| #((h \ rs) ++ r) = 0, ¬(r0 ∈ h0 ↔ r0 = r ∨ r0 ∈ h), r ∈ (h \ rs) ++ r, r ∈ h \ rs, ¬ r ∈ rs, ¬ r0 ∈ rs, ¬ r ∈ h, ∀ r1. r1 ∈ rs → (r1 ∈ h0 ↔ r1 ∈ h) ∧ (r1 ∈ h0 → h0[r1] = (h ++ r)[r1]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + 0 → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs
Used terms: r, h, rs
| ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs |
| r ∈ h1 \ rs, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ ((h0 ≡ (h1 -- r)))(rs) ∧ ¬ modify*(rs)(h0, h1 -- r) |
⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs
r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ ((h0 ≡ (h1 -- r)))(rs) ∧ ¬ modify*(rs)(h0, h1 -- r)
Used terms: r, h1, rs
| ⊦ r ∈ h \ rs ↔ r ∈ h ∧ ¬ r ∈ rs |
| r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ ((h0 ≡ (h1 -- r)))(rs) ∧ ¬ modify*(rs)(h0, h1 -- r) |
modify*(rs)(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: agree-rm-01: ⊦ ¬ r ∈ rs → (((h ≡ (h0 -- r)))(rs) ↔ ((h ≡ h0))(rs));
| modify*(rs)(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1)
modify(rs) ^*(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: rs, h0, h1 -- r
| ⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1) |
| modify(rs) ^*(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1)
modify(rs) ^*(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs) ^*(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: rs, h0, h1
| ⊦ modify*(rs)(h0, h1) ↔ modify(rs) ^*(h0, h1) |
| modify(rs) ^*(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs) ^*(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b))
r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs) ^*(h0, h1), ¬ r ∈ rs, ∃ n. rtc(n, modify(rs))(h0, h1 -- r), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: modify(rs), h0, h1 -- r
| ⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b)) |
| r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs) ^*(h0, h1), ¬ r ∈ rs, ∃ n. rtc(n, modify(rs))(h0, h1 -- r), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs) ^*(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs) ^*(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b))
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ n. ¬ rtc(n, modify(rs))(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: modify(rs), h0, h1
| ⊦ pelem ^*(a, b) ↔ (∃ n. rtc(n, pelem)(a, b)) |
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ n. ¬ rtc(n, modify(rs))(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ rtc(n + 2, modify(rs))(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: n + 2
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ rtc(n + 2, modify(rs))(h0, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ n ≠ 0 → (rtc(n, pelem)(a, b) ↔ (∃ c. rtc(n - 1, pelem)(a, c) ∧ pelem(c, b)))
n + 2 ≠ 0, rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬(rtc(n + 2 - 1, modify(rs))(h0, c) ∧ modify(rs)(c, h1)), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ m + n = 0 ↔ m = 0 ∧ n = 0; (ws) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: n + 2, modify(rs), h0, h1
| ⊦ n ≠ 0 → (rtc(n, pelem)(a, b) ↔ (∃ c. rtc(n - 1, pelem)(a, c) ∧ pelem(c, b))) |
| n + 2 ≠ 0, rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬(rtc(n + 2 - 1, modify(rs))(h0, c) ∧ modify(rs)(c, h1)), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬ rtc(1 + n, modify(rs))(h0, c) ∨ ¬ modify(rs)(c, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ n ≤ m → m + n0 - n = (m - n) + n0; (s) n < n0 ⊦ (* n) ≠ m0 + (* n0); (s)
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬ rtc(1 + n, modify(rs))(h0, c) ∨ ¬ modify(rs)(c, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ¬ rtc(1 + n, modify(rs))(h0, (h1 -- r) ++ r) ∨ ¬ modify(rs)((h1 -- r) ++ r, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: (h1 -- r) ++ r
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ¬ rtc(1 + n, modify(rs))(h0, (h1 -- r) ++ r) ∨ ¬ modify(rs)((h1 -- r) ++ r, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ rtc(1 + n, modify(rs))(h0, (h1 -- r) ++ r), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs)((h1 -- r) ++ r, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ rtc(1 + n, modify(rs))(h0, (h1 -- r) ++ r), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ n ≠ 0 → (rtc(n, pelem)(a, b) ↔ (∃ c. rtc(n - 1, pelem)(a, c) ∧ pelem(c, b)))
1 + n ≠ 0, rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬(rtc(1 + n - 1, modify(rs))(h0, c) ∧ modify(rs)(c, (h1 -- r) ++ r)), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ m + n = 0 ↔ m = 0 ∧ n = 0; (ws) a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic c: ⊦ m + n = n + m; from specification nat-basic Used terms: 1 + n, modify(rs), h0, (h1 -- r) ++ r
| ⊦ n ≠ 0 → (rtc(n, pelem)(a, b) ↔ (∃ c. rtc(n - 1, pelem)(a, c) ∧ pelem(c, b))) |
| 1 + n ≠ 0, rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬(rtc(1 + n - 1, modify(rs))(h0, c) ∧ modify(rs)(c, (h1 -- r) ++ r)), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬ rtc(n, modify(rs))(h0, c) ∨ ¬ modify(rs)(c, (h1 -- r) ++ r), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic a: ⊦ (m + n0) + n1 = m + n0 + n1; from specification nat-basic ⊦ n + 0 = n; (s) ⊦ n ≤ m → m + n0 - n = (m - n) + n0; (s) ⊦ m + 1 ≠ 0; (s)
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ c. ¬ rtc(n, modify(rs))(h0, c) ∨ ¬ modify(rs)(c, (h1 -- r) ++ r), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ¬ rtc(n, modify(rs))(h0, h1 -- r) ∨ ¬ modify(rs)(h1 -- r, (h1 -- r) ++ r), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h1 -- r
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ¬ rtc(n, modify(rs))(h0, h1 -- r) ∨ ¬ modify(rs)(h1 -- r, (h1 -- r) ++ r), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs)(h1 -- r, (h1 -- r) ++ r), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs)(h1 -- r, (h1 -- r) ++ r), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ modify(rs)(h0, h1) ↔ (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h1 = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0 -- r)
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ≠ null ∧ ¬ r0 ∈ h1 -- r ∧ (h1 -- r) ++ r = (h1 -- r) ++ r0), ∀ r0, o. ¬(¬ r0 ∈ rs ∧ r0 ∈ h1 -- r ∧ (h1 -- r) ++ r = (h1 -- r)[r0, o]), ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ∈ h1 -- r ∧ (h1 -- r) ++ r = h1 -- r -- r0), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: rs, h1 -- r, (h1 -- r) ++ r
| ⊦ modify(rs)(h0, h1) ↔ (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h1 = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0 -- r) |
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ≠ null ∧ ¬ r0 ∈ h1 -- r ∧ (h1 -- r) ++ r = (h1 -- r) ++ r0), ∀ r0, o. ¬(¬ r0 ∈ rs ∧ r0 ∈ h1 -- r ∧ (h1 -- r) ++ r = (h1 -- r)[r0, o]), ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ∈ h1 -- r ∧ (h1 -- r) ++ r = h1 -- r -- r0), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ≠ r ∧ r0 ∈ h1 ∨ (h1 -- r) ++ r ≠ (h1 -- r) ++ r0, ∀ r0. r0 ∈ rs ∨ r0 = r ∨ ¬ r0 ∈ h1 ∨ (h1 -- r) ++ r ≠ h1 -- r -- r0, ∀ r0, o. r0 ∈ rs ∨ r0 = r ∨ ¬ r0 ∈ h1 ∨ (h1 -- r) ++ r ≠ (h1 -- r)[r0, o], ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h -- r0 ↔ r ≠ r0 ∧ r ∈ h; (s)
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ≠ r ∧ r0 ∈ h1 ∨ (h1 -- r) ++ r ≠ (h1 -- r) ++ r0, ∀ r0. r0 ∈ rs ∨ r0 = r ∨ ¬ r0 ∈ h1 ∨ (h1 -- r) ++ r ≠ h1 -- r -- r0, ∀ r0, o. r0 ∈ rs ∨ r0 = r ∨ ¬ r0 ∈ h1 ∨ (h1 -- r) ++ r ≠ (h1 -- r)[r0, o], ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
Used simplifier rules: ⊦ r ∈ h → r ≠ null; (s) Used terms: r
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ modify(rs)((h1 -- r) ++ r, h1), ¬ r ∈ rs, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ modify(rs)(h0, h1) ↔ (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h1 = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0 -- r)
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ≠ null ∧ ¬ r0 ∈ (h1 -- r) ++ r ∧ h1 = (h1 -- r) ++ r ++ r0), ∀ r0, o. ¬(¬ r0 ∈ rs ∧ r0 ∈ (h1 -- r) ++ r ∧ h1 = ((h1 -- r) ++ r)[r0, o]), ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ∈ (h1 -- r) ++ r ∧ h1 = ((h1 -- r) ++ r) -- r0), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: rs, (h1 -- r) ++ r, h1
| ⊦ modify(rs)(h0, h1) ↔ (∃ r. ¬ r ∈ rs ∧ r ≠ null ∧ ¬ r ∈ h0 ∧ h1 = h0 ++ r) ∨ (∃ r, o. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0[r, o]) ∨ (∃ r. ¬ r ∈ rs ∧ r ∈ h0 ∧ h1 = h0 -- r) |
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ≠ null ∧ ¬ r0 ∈ (h1 -- r) ++ r ∧ h1 = (h1 -- r) ++ r ++ r0), ∀ r0, o. ¬(¬ r0 ∈ rs ∧ r0 ∈ (h1 -- r) ++ r ∧ h1 = ((h1 -- r) ++ r)[r0, o]), ∀ r0. ¬(¬ r0 ∈ rs ∧ r0 ∈ (h1 -- r) ++ r ∧ h1 = ((h1 -- r) ++ r) -- r0), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∀ r0, o. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r)[r0, o], ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: ⊦ r ∈ h -- r0 ↔ r ≠ r0 ∧ r ∈ h; (s) r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h; (s) ⊦ r ∈ h → r ≠ null; (s)
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∀ r0, o. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r)[r0, o], ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, r ∈ rs ∨ ¬ r ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r)[r, h1[r]], ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: r, h1[r]
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, r ∈ rs ∨ ¬ r ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r)[r, h1[r]], ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h1 ≠ ((h1 -- r) ++ r)[r, h1[r]], rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| h1 ≠ ((h1 -- r) ++ r)[r, h1[r]], rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∃ r0. ¬((r0 ∈ h1 ↔ r0 ∈ ((h1 -- r) ++ r)[r, h1[r]]) ∧ (r0 ∈ h1 → h1[r0] = ((h1 -- r) ++ r)[r, h1[r]][r0])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h1, ((h1 -- r) ++ r)[r, h1[r]]
| ⊦ h0 = h1 ↔ (∀ r. (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∃ r0. ¬((r0 ∈ h1 ↔ r0 ∈ ((h1 -- r) ++ r)[r, h1[r]]) ∧ (r0 ∈ h1 → h1[r0] = ((h1 -- r) ++ r)[r, h1[r]][r0])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h1[r0] ≠ (r0 = r ⊃ h1[r];h1[r0]), rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, r0 ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used simplifier rules: r ∈ h ⊦ r ≠ r0 → (h -- r0)[r] = h[r]; (s) r ∈ h, r0 ≠ null, ¬ r0 ∈ h ⊦ r ≠ r0 → (h ++ r0)[r] = h[r]; (s) ⊦ r ∈ h -- r0 ↔ r ≠ r0 ∧ r ∈ h; (s) ⊦ r ∈ h → r ≠ null; (s) r0 ≠ null, ¬ r0 ∈ h ⊦ r ∈ h ++ r0 ↔ r = r0 ∨ r ∈ h; (s) ⊦ h[r0, o][r] = (r = r0 ∧ r0 ∈ h ⊃ o;h[r]); (s) ⊦ r ∈ h[r0, o] ↔ r ∈ h; (s)
| h1[r0] ≠ (r0 = r ⊃ h1[r];h1[r0]), rtc(n, modify(rs))(h0, h1 -- r), r ∈ h1, r0 ∈ h1, ((h0 ≡ h1))(rs), ¬ r ∈ rs, ∀ r0. r0 ∈ rs ∨ ¬ r0 ∈ h1 ∨ h1 ≠ ((h1 -- r) ++ r) -- r0, ∀ r0. r0 ∈ rs ∨ r0 = null ∨ r0 ∈ h1 ∨ h1 ≠ (h1 -- r) ++ r ++ r0, ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
| h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h1 \ rs) + #(h0 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false) ∧ ((h1 ≡ h0))(rs) ∧ ¬ modify*(rs)(h1, h0)
| h1 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
| h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h1 \ rs) + #(h0 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false) ∧ ((h1 ≡ h0))(rs) ∧ ¬ modify*(rs)(h1, h0) |
h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (#(h \ rs0) + #(h2 \ rs0) < #(h1 \ rs) + #(h0 \ rs) → ¬ ((h ≡ h2))(rs0) ∨ modify*(rs0)(h, h2)) ∧ ((h1 ≡ h0))(rs) ∧ ¬ modify*(rs)(h1, h0)
| h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (#(h \ rs0) + #(h2 \ rs0) < #(h1 \ rs) + #(h0 \ rs) → ¬ ((h ≡ h2))(rs0) ∨ modify*(rs0)(h, h2)) ∧ ((h1 ≡ h0))(rs) ∧ ¬ modify*(rs)(h1, h0) |
h0 \ rs ≠ ∅, #(h \ rs0) + #(h2 \ rs0) < #(h1 \ rs) + #(h0 \ rs), ((h ≡ h2))(rs0), ((h0 ≡ h1))(rs), ¬ modify*(rs0)(h, h2), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ ((h1 ≡ h0))(rs), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
h0 \ rs ≠ ∅, modify*(rs)(h1, h0), ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
| h0 \ rs ≠ ∅, #(h \ rs0) + #(h2 \ rs0) < #(h1 \ rs) + #(h0 \ rs), ((h ≡ h2))(rs0), ((h0 ≡ h1))(rs), ¬ modify*(rs0)(h, h2), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
Used simplifier rules: c: ⊦ m + n = n + m; from specification nat-basic Used terms: h, rs0, h2
| h0 \ rs ≠ ∅, ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ¬ ((h1 ≡ h0))(rs), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
h0 \ rs ≠ ∅, ¬ modify*(rs)(h0, h1), ¬ ((h1 ≡ h0))(rs), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h0, h1, rs
| ⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| h0 \ rs ≠ ∅, ¬ modify*(rs)(h0, h1), ¬ ((h1 ≡ h0))(rs), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]))
h0 \ rs ≠ ∅, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ r. ¬(r ∈ rs → (r ∈ h1 ↔ r ∈ h0) ∧ (r ∈ h1 → h1[r] = h0[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦
Used terms: h1, h0, rs
| ⊦ ((h0 ≡ h1))(rs) ↔ (∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r])) |
| h0 \ rs ≠ ∅, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∃ r. ¬(r ∈ rs → (r ∈ h1 ↔ r ∈ h0) ∧ (r ∈ h1 → h1[r] = h0[r])), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
# rs ≠ 0, h0 \ rs ≠ ∅, rs ≠ ∅, r ∈ rs, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h1 ↔ r ∈ h0) ∧ (r ∈ h1 → h1[r] = h0[r])
Used simplifier rules: size-zero-01: ⊦ s ≠ ∅ → # s ≠ 0; (forward) from specification set-basic[refset] ne-01: ⊦ a ∈ s → s ≠ ∅; (forward) from specification set-basic[refset]
| # rs ≠ 0, h0 \ rs ≠ ∅, rs ≠ ∅, r ∈ rs, ¬ modify*(rs)(h0, h1), ∀ r. r ∈ rs → (r ∈ h0 ↔ r ∈ h1) ∧ (r ∈ h0 → h0[r] = h1[r]), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ (r ∈ h1 ↔ r ∈ h0) ∧ (r ∈ h1 → h1[r] = h0[r]) |
Used terms: r
| h0 \ rs ≠ ∅, modify*(rs)(h1, h0), ((h0 ≡ h1))(rs), ¬ modify*(rs)(h0, h1), ∀ h, rs0, h2. #(h \ rs0) + #(h2 \ rs0) < #(h0 \ rs) + #(h1 \ rs) → ((h ≡ h2))(rs0) ∧ ¬ modify*(rs0)(h, h2) → false ⊦ |
⊦ modify*(rs)(h0, h1) ↔ modify*(rs)(h1, h0)
Used terms: rs, h0, h1
| ⊦ modify*(rs)(h0, h1) ↔ modify*(rs)(h1, h0) |
The following image shows the proof tree of sequent calculus. The proved goal is at the bottom. You can click on the nodes to view additional rules. See here for details on colors in a proof tree.